cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · bleepingcomputer.com

CISA Sets June 28 Deadline to Address Cisco and PTC Vulnerabilities

CISA set a June 28 deadline for federal agencies to patch or stop using products affected by CVE-2026-20230 and CVE-2026-12569. Cisco's SSRF flaw is being exploited to write arbitrary text files; PTC's is a critical deserialization-based RCE.
Jun 26, 2026
Vulnerability & Exploit · securityweek.com

Amazon Q Developer Flaw Could Enable Cloud Credential Theft via Malicious Repositories

Wiz disclosed that Amazon Q Developer could run commands from workspace configuration files without permission, exposing cloud credentials when developers opened malicious repositories. AWS patched CVE-2026-12957 and a related symlink issue, CVE-2026-12958.

Jun 26, 2026
Vulnerability & Exploit · wiz.io

Amazon Q VS Code Vulnerability Enabled Code Execution and Cloud Credential Theft

CVE-2026-12957 let malicious workspace MCP configurations execute commands through Amazon Q for VS Code, potentially exposing developer credentials. AWS fixed the issue in language server version 1.65.0.

Jun 26, 2026
Vulnerability & Exploit · zscaler.com

Critical Splunk Enterprise Flaw Enables Unauthenticated Remote Code Execution

CVE-2026-20253 is a critical, unauthenticated Splunk Enterprise flaw that can enable remote code execution through its PostgreSQL sidecar recovery endpoint. Splunk reported active exploitation, and CISA added it to the KEV catalog.

Jun 26, 2026
Vulnerability & Exploit · securityweek.com

Researchers Observe CVE-2025-67038 Exploitation Against Lantronix EDS5000 Honeypot

Forescout observed CVE-2025-67038 exploitation against a Lantronix EDS5000 honeypot after a patch was released. The unauthenticated flaw enables root-level command injection; researchers say the activity may indicate patch reverse-engineering.

Jun 25, 2026
Vulnerability & Exploit · securityweek.com

curl Update Patches 18 Vulnerabilities, Including 25-Year-Old Potential Authentication Bypass

A curl update fixes 18 vulnerabilities, including CVE-2026-8932, a 25-year-old flaw that could allow authentication bypass in libcurl applications. No successful in-the-wild exploitation has been publicly reported.

Jun 25, 2026
Vulnerability & Exploit · securityweek.com

Chrome 149 Update Fixes 18 Vulnerabilities

Google’s Chrome 149 update fixes 18 vulnerabilities, including four critical and 14 high-severity flaws. Google did not report exploitation in the wild.

Jun 25, 2026
Vulnerability & Exploit · thehackernews.com

CISA Flags Active Exploitation of Lantronix EDS5000 and UniFi OS Flaws

CISA says CVE-2025-67038 is being actively exploited in Lantronix EDS5000 devices, and confirms active exploitation of three UniFi OS flaws. The issues can enable privileged command execution, root access, and lateral movement.

Jun 24, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns of Active Exploitation of Ubiquiti and Lantronix Flaws

CISA warns that four flaws affecting Ubiquiti UniFi OS and Lantronix EDS5000 are being actively exploited. Patches are available; researchers demonstrated that the three UniFi OS flaws can be chained for remote code execution.

Jun 24, 2026
Vulnerability & Exploit · securityweek.com

CISA Warns of Exploitation of Critical Ubiquiti UniFi OS Flaws

CISA added three critical Ubiquiti UniFi OS flaws to its KEV catalog. BishopFox analyzed how the flaws enable an authentication bypass and command injection; users reported rogue administrator accounts, while Ubiquiti released patches in version 5.0.8.

Jun 24, 2026
Vulnerability & Exploit · securityweek.com

Defused Reports Exploitation of Cisco Unified CM Flaw; Cisco Has Not Confirmed Attacks

Defused reports exploitation of patched Cisco Unified CM flaw CVE-2026-20230, but Cisco says it is not aware of malicious use. The flaw requires WebDialer to be enabled; Cisco urges customers to upgrade.

Jun 24, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Unified CM Flaw CVE-2026-20230 Exploited in Attacks

Defused reports active exploitation of Cisco Unified CM’s CVE-2026-20230 SSRF flaw, with activity appearing to be reconnaissance. Cisco issued security updates; SSD Secure published technical details and a proof of concept.

Jun 24, 2026
Vulnerability & Exploit · securityweek.com

Dify Flaws Could Expose Data Across AI Application Tenants

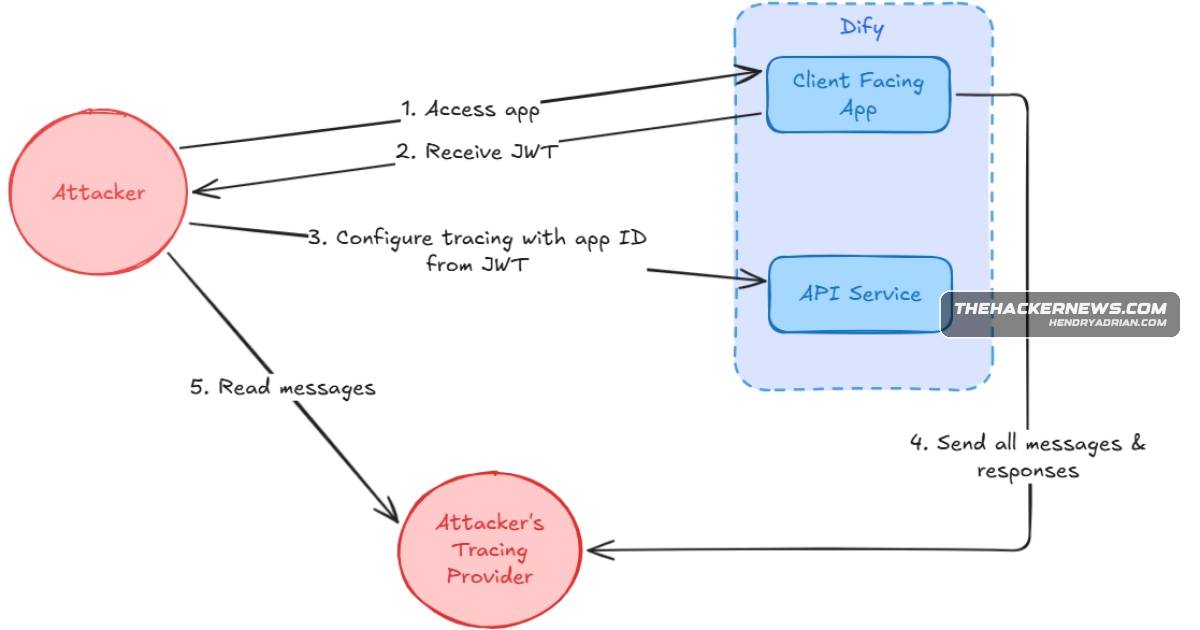
Zafran Security reports four Dify vulnerabilities that could expose chats, files, and internal API access across tenants. Dify 1.14.2 includes fixes; users are advised to update and apply a WAF rule for CVE-2026-41948.

Jun 23, 2026
Vulnerability & Exploit · securityweek.com

Samsung Patched CVE-2026-20971 Kernel Flaw Affecting Galaxy Devices

Researchers say CVE-2026-20971 is a KNOX kernel use-after-free affecting multiple Samsung device generations. Samsung patched it in January 2026; its advisory says local exploitation requires user interaction.

Jun 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

FFmpeg Fixes PixelSmash Flaw That Can Enable RCE in Jellyfin

JFrog disclosed PixelSmash (CVE-2026-8461), a high-severity heap out-of-bounds write in FFmpeg’s MagicYUV decoder. Crafted video can cause DoS and, under conditions including disabled or bypassed ASLR, RCE; FFmpeg 8.1.2 fixes it.

Jun 23, 2026
Vulnerability & Exploit · thehackernews.com

DifyTap Flaws Could Expose Cross-Tenant AI Chats and Files; One Fix Pending

Researchers say four Dify flaws could expose AI chats, internal APIs, and files across tenants. Dify 1.14.2 fixes most issues; a fix for CVE-2026-41948 is pending.

Jun 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

Microsoft Fixes AutoGen Studio Flaw That Could Enable Host Command Execution

Microsoft says the AutoJack vulnerability chain could let a malicious webpage trick an AutoGen Studio agent into running commands on its host. The flaw was fixed before PyPI release; developers who built from GitHub during a brief window were exposed.

Jun 22, 2026
Vulnerability & Exploit · thehackernews.com

Squidbleed Bug Can Leak Cleartext HTTP Requests from Squid Proxy Users

Squidbleed (CVE-2026-47729), a heap over-read in Squid’s FTP listing parser, can expose other users’ cleartext HTTP requests to a client already authorized to use the same proxy. Fixes include a parser guard or disabling FTP; no in-the-wild exploitation was reported.

Jun 22, 2026
Vulnerability & Exploit · securityweek.com

Squidbleed Flaw Can Expose Users’ HTTP Data Through Squid Proxy

Calif researchers disclosed Squidbleed (CVE-2026-47729), a Squid FTP parser memory leak that may expose prior users’ HTTP request data. The article says Squid 7.6 includes a patch and disabling FTP can mitigate the risk.

Jun 22, 2026
Vulnerability & Exploit · securityweek.com

Attackers Exploit Gravity SMTP Flaw to Expose WordPress System Data

Attackers have exploited CVE-2026-4020 in Gravity SMTP for WordPress since early May, exposing system details and configured API credentials through an unauthenticated REST endpoint. Defiant reports over 17 million blocked attempts; update to 2.1.5 and rotate affected-­

Jun 22, 2026
Vulnerability & Exploit · netspi.com

Microsoft Fixed Entra Conditional Access Bypass via Nested App Authentication

NetSPI found that certain Nested App Authentication flows could bypass Entra Conditional Access when issuing Microsoft Graph tokens. The exploit required an Azure Portal refresh token; Microsoft has since fixed the issue.

Jun 22, 2026
Vulnerability & Exploit · thehackernews.com

Attackers Exploit Gravity SMTP Flaw to Expose API Keys

CVE-2026-4020 lets unauthenticated attackers retrieve sensitive data from Gravity SMTP’s REST API. Wordfence reports more than 17 million blocked exploit attempts and advises updating to version 2.1.5 and rotating exposed credentials.

Jun 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

Hackers Exploit Gravity SMTP WordPress Plugin Flaw Exposing Credentials

Attackers are exploiting CVE-2026-4020 in Gravity SMTP, exposing sensitive data through an unauthenticated REST API endpoint. Wordfence reports blocking over 17 million attempts; a separate Avada Builder flaw has been patched.

Jun 19, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited Splunk Flaw

CISA says attackers are exploiting CVE-2026-20253, an unauthenticated Splunk Enterprise flaw, and ordered federal agencies to patch. Splunk recommends upgrading; disabling the PostgreSQL sidecar is a mitigation with stated service impacts.

Jun 19, 2026
PreviousPage 44 of 65 Next
© 2026 cyber.hendryadrian.com