
Bad Epoll Linux Kernel Flaw Can Give Local Users Root on Linux and Android
Summary
Bad Epoll (CVE-2026-46242) is a Linux kernel use-after-free that can let local users gain root on Linux systems and some Android devices. An exploit reportedly succeeded about 99% in tests; an upstream fix is available.
Key points
- Bad Epoll is a Linux kernel use-after-free flaw that can allow a local user to escalate privileges to root.
- The article says kernels 6.4 and newer are affected unless patched; some older 6.1-based kernels, including some Android phones, are not affected.
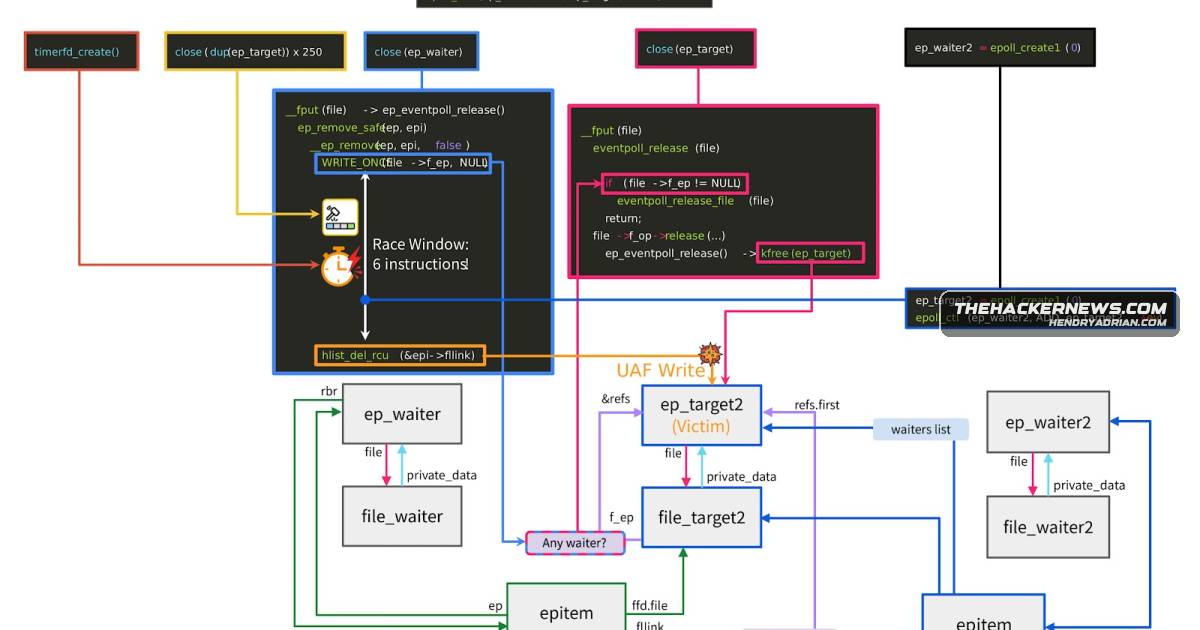
- Researcher Jaeyoung Chung reportedly widened a roughly six-instruction race window; the exploit reached root about 99% of the time on tested systems.
- Chung says the flaw can be triggered from inside Chrome's renderer sandbox; epoll cannot be disabled as a workaround.
- Apply upstream commit a6dc643c6931 or a vendor backport. The article reports no known real-world exploitation and describes the working code as a kernelCTF proof of concept.
- Bad Epoll is distinct from CVE-2026-43074, another flaw in the same epoll code area that Anthropic's Mythos AI reportedly found.
Article Details
- Vulnerability Types
- Use-after-free
- Race condition
- Severity
- Local privilege escalation to root; Chung reports about 99% exploit success on tested systems.
- Affected Versions
- Linux kernel 6.4 and newer, unless already fixed
- Exploitation Status
- not_reported
- Exploit Availability
- public_poc
- Patch Status
- available
MITRE ATT&CK
CVE
CVE-2026-43074The bug is especially notable because it was found after Anthropic’s Mythos AI missed it in the same epoll code area where it had found CVE-2026-43074.CVE-2026-46242Bad Epoll (CVE-2026-46242) is a Linux kernel use-after-free flaw that can let a local user gain root on affected Linux desktops, servers, and Android devices, with a fix already available.
People
Vendors
Products
AndroidBad Epoll (CVE-2026-46242) is a Linux kernel use-after-free flaw that can let a local user gain root on affected Linux desktops, servers, and Android devices, with a fix already available.Google ChromeTwo things make it more dangerous: by his account, it can be triggered from inside Chrome’s renderer sandbox, which blocks almost every other kernel bug, and it can reach Android, which most Linux privilege bugs cannot.Linux kernelBad Epoll (CVE-2026-46242) is a Linux kernel use-after-free flaw that can let a local user gain root on affected Linux desktops, servers, and Android devices, with a fix already available.MythosThe bug is especially notable because it was found after Anthropic’s Mythos AI missed it in the same epoll code area where it had found CVE-2026-43074.