
Adobe ColdFusion CVE-2026-48282 Enables Unauthenticated File Writes and Potential RCE
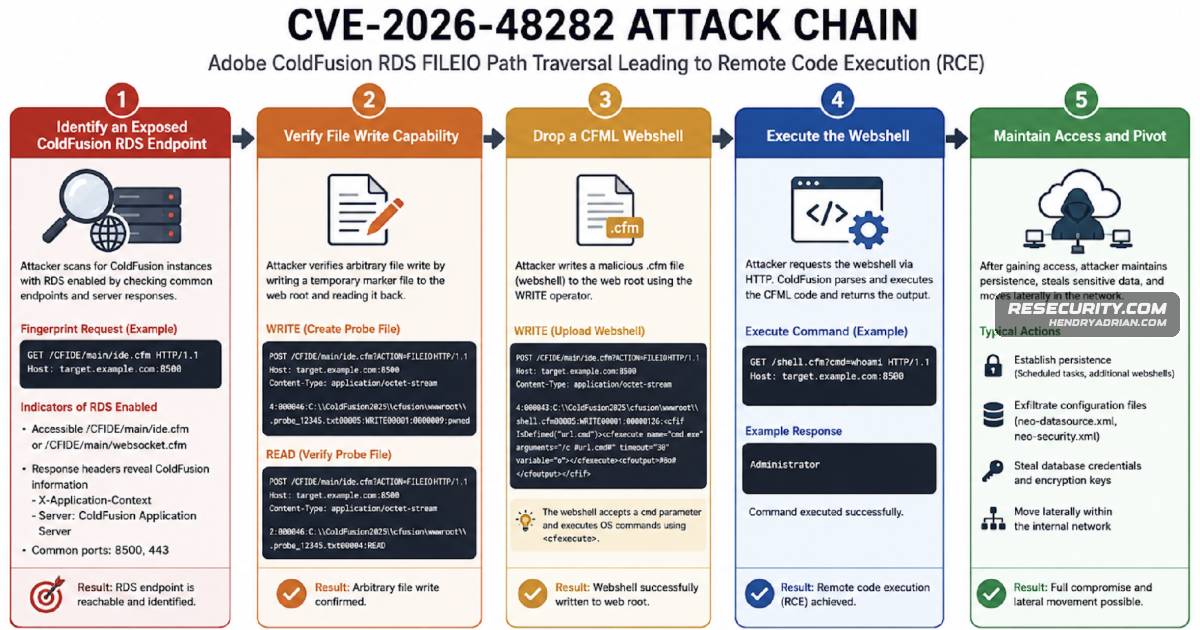
Summary
Resecurity reports active exploitation of CVE-2026-48282, a ColdFusion RDS FILEIO path-traversal flaw enabling unauthenticated arbitrary file writes and potential RCE. CISA added it to KEV; Adobe fixed it in ColdFusion 2025 Update 10 and 2023 Update 21.
Key points
- Resecurity says CVE-2026-48282 is being exploited; CISA added the vulnerability to its Known Exploited Vulnerabilities Catalog.
- The flaw is in ColdFusion’s RDS FILEIO handler, which accepts user-controlled paths without adequate canonicalization or directory-boundary validation.
- The article describes unauthenticated file reads and writes through crafted HTTP requests; writing executable files to the web root may enable remote code execution, depending on configuration and service-account privileges.
- ColdFusion 2025 Update 9 and earlier and ColdFusion 2023 Update 20 and earlier are listed as affected; Adobe’s fixes are Update 10 and Update 21, respectively.
- The article recommends applying the updates, disabling RDS if unnecessary or restricting it to trusted hosts, and checking for suspicious files and FILEIO requests.
Article Details
- Vulnerability Types
- Path traversal
- Unauthenticated arbitrary file write
- Remote code execution
- Severity
- Critical (CVSS v3.1 score 10.0)
- Affected Versions
- Adobe ColdFusion 2025 Update 9 and earlier
- Adobe ColdFusion 2023 Update 20 and earlier
- Exploitation Status
- active
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Disable RDS unless required; if enabled, restrict access to trusted administrator hosts or internal networks.
- Block external access to ColdFusion administrative endpoints, including /CFIDE/main/ide.cfm and /CFIDE/main/websocket.cfm.
MITRE ATT&CK
T1005 · Data from Local SystemThe article describes using the FILEIO READ operation to access local files, including ColdFusion configuration files and an example Windows file.T1059 · Command and Scripting InterpreterThe example webshell uses the CFML cfexecute tag to run operating-system commands supplied through a cmd parameter.T1190 · Exploit Public-Facing ApplicationThe article describes attackers scanning for exposed ColdFusion RDS endpoints and sending crafted HTTP requests to exploit the FILEIO path traversal vulnerability.T1505.003 · Web ShellThe described attack writes a .cfm webshell into the ColdFusion web root and accesses it through the web server.