
Unpatched Argo CD Flaw Could Enable Code Execution and Kubernetes Cluster Takeover
Summary
Synacktiv says an unpatched Argo CD repo-server flaw lets unauthenticated requests execute attacker-controlled scripts if its internal gRPC port is reachable, potentially enabling cluster takeover via Redis cache poisoning. No fix is available; network isolation is the
Key points
- Synacktiv reports that unauthenticated requests to repo-server’s internal gRPC service can execute commands when the service is reachable.
- The exploit sets kustomize’s --helm-command option to run an attacker-controlled script from a Git repository.
- Synacktiv demonstrated the issue on Argo CD v2.13.3 and reports no patched release; it did not provide a complete list of affected versions.
- In a Helm-based installation with network policies disabled, a compromised pod could reach repo-server and trigger the flaw.
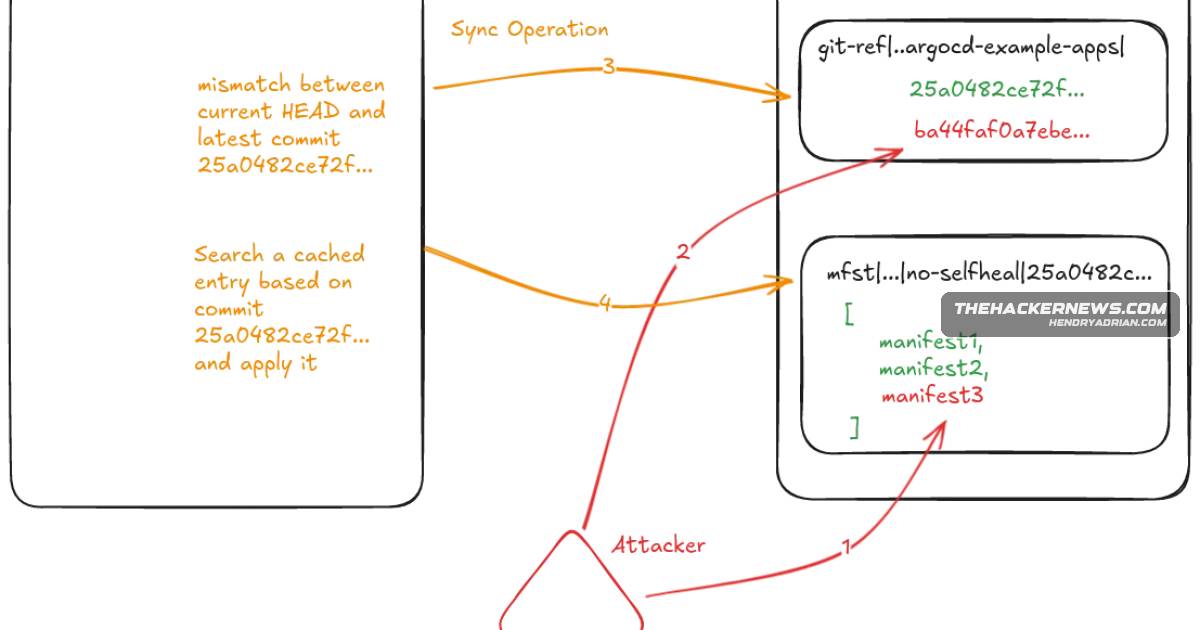
- Synacktiv used repo-server access to read the Redis password, poison Argo CD’s deployment cache, and cause a later automatic sync to deploy an attacker-supplied workload.
- There is no patch; administrators are advised to enable network policies restricting access to repo-server and Redis.
Article Details
- Vulnerability Types
- Unauthenticated command execution
- Redis deployment-cache poisoning
- Affected Versions
- Argo CD v2.13.3 (demonstrated vulnerable; full affected-version range not disclosed)
- Exploitation Status
- not_reported
- Exploit Availability
- claimed_or_private
- Patch Status
- unavailable
- Workarounds
- Enable Kubernetes network policies so only Argo CD components can reach the repo-server and Redis ports.
MITRE ATT&CK
T1059 · Command and Scripting InterpreterThe crafted request sets kustomize’s helm-command option to an attacker-controlled script, which kustomize executes instead of Helm.T1105 · Ingress Tool TransferThe script executed through kustomize is pulled from an attacker-controlled Git repository.T1210 · Exploitation of Remote ServicesAn attacker able to reach the internal repo-server gRPC service can send a crafted request that triggers command execution.T1565.001 · Stored Data ManipulationAfter reading the Redis password from the repo-server environment, Synacktiv’s demonstrated attack poisons deployment data stored in Argo CD’s Redis cache.
CVE
Products
Argo CDSynacktiv disclosed an unpatched Argo CD repo-server flaw that can let an unauthenticated attacker execute code and potentially take over a Kubernetes cluster if the internal port is reachable.KubernetesSynacktiv disclosed an unpatched Argo CD repo-server flaw that can let an unauthenticated attacker execute code and potentially take over a Kubernetes cluster if the internal port is reachable.RedisThe issue affects common Helm-based deployments with network policies disabled, and defenders are urged to isolate repo-server and Redis immediately.