
CISA Adds Actively Exploited SharePoint RCE Flaw to KEV Catalog
Summary
CISA added SharePoint Server flaw CVE-2026-45659 to its KEV catalog after finding active exploitation. Microsoft fixed it in May 2026; FCEB agencies are advised to patch by July 4.
Key points
- CVE-2026-45659 is a high-severity remote code execution flaw caused by deserialization of untrusted data.
- An authenticated attacker with at least Site Member permissions can exploit it over the network without elevated privileges.
- Microsoft fixed the flaw in May 2026 for SharePoint Server 2016, 2019, and Subscription Edition.
- CISA added the vulnerability to its KEV catalog based on evidence of active exploitation; the article says the exploitation method and actors are unknown.
- FCEB agencies are advised to apply the fixes by July 4, 2026.
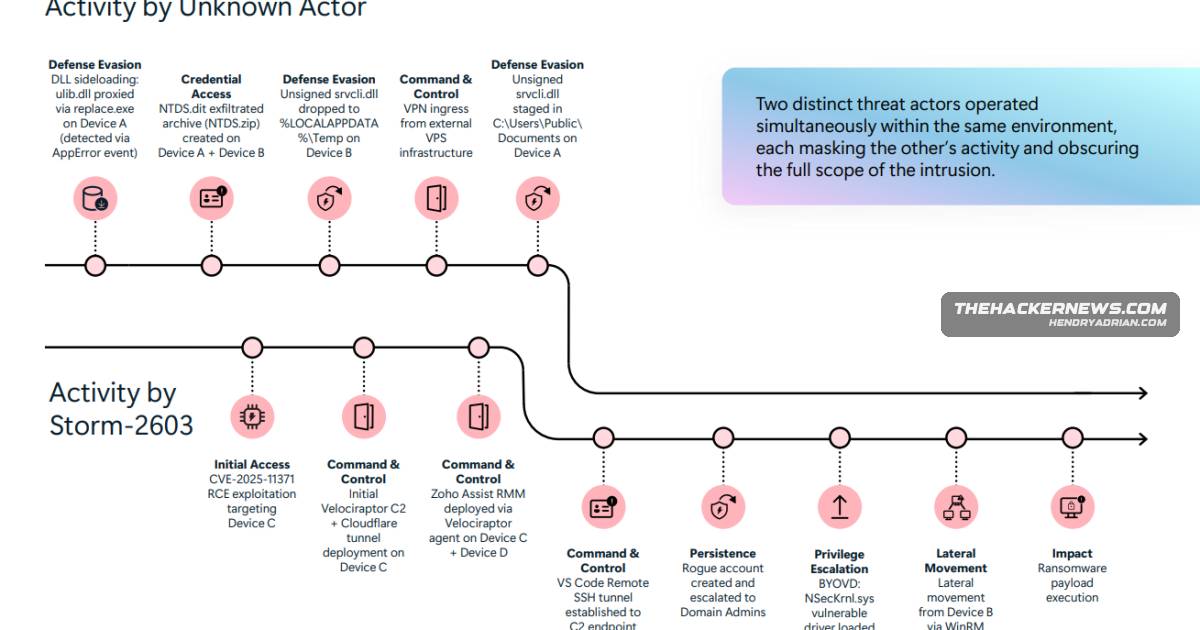
- Separately, Microsoft described overlapping activity involving Storm-2603, Warlock ransomware, and an unrelated actor; its investigation linked another initial-access attempt to CVE-2025-11371 in Gladinet Triofox.
Article Details
- Vulnerability Types
- Deserialization of untrusted data leading to remote code execution
- Severity
- High (CVSS 8.8)
- Affected Versions
- SharePoint Server Subscription Edition
- SharePoint Server 2019
- SharePoint Enterprise Server 2016
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1021.004 · SSHThe attackers established remote access using SSH connections configured through Visual Studio Code.T1136.001 · Local AccountThe attack created new local administrator accounts.T1136.002 · Domain AccountThe attack created new domain administrator accounts.T1219 · Remote Access ToolsMicrosoft reported Zoho Assist among the remote access channels established by the attackers.T1562.001 · Disable or Modify ToolsA vulnerable driver was used to tamper with endpoint security protections and reduce the attackers’ visibility.T1572 · Protocol TunnelingMicrosoft reported Cloudflare tunneling among the remote access channels established by the attackers.T1574.002 · DLL Side-LoadingMicrosoft reported that a second, unrelated threat actor used DLL side-loading.
CVE
CVE-2025-11371Gladinet · CentreStack and TrioFoxEvidence points to it being CVE-2025-11371 (CVSS score: 9.1), a critical flaw impacting Gladinet Triofox.CVE-2026-45659Microsoft · Microsoft SharePoint Enterprise Server 2016; Microsoft · Microsoft SharePoint Server 2019; +1 moreCISA added CVE-2026-45659, a high-severity Microsoft SharePoint Server remote code execution flaw, to its Known Exploited Vulnerabilities catalog after finding evidence of active exploitation.
Threat Actors
Malware
Vendors
Cloudflarewith trusted administrative behavior, as well as established multiple remote access channels through Cloudflare tunneling, Zoho Assist, and Secure Shell (SSH) connections configured through Visual Studio Code.GladinetEvidence points to it being CVE-2025-11371 (CVSS score: 9.1), a critical flaw impacting Gladinet Triofox.MicrosoftCISA added CVE-2026-45659, a high-severity Microsoft SharePoint Server remote code execution flaw, to its Known Exploited Vulnerabilities catalog after finding evidence of active exploitation.Zohobehavior, as well as established multiple remote access channels through Cloudflare tunneling, Zoho Assist, and Secure Shell (SSH) connections configured through Visual Studio Code.
Products
Gladinet TriofoxEvidence points to it being CVE-2025-11371 (CVSS score: 9.1), a critical flaw impacting Gladinet Triofox.Microsoft SharePoint ServerCISA added CVE-2026-45659, a high-severity Microsoft SharePoint Server remote code execution flaw, to its Known Exploited Vulnerabilities catalog after finding evidence of active exploitation.VSCodethrough Cloudflare tunneling, Zoho Assist, and Secure Shell (SSH) connections configured through Visual Studio Code.Zoho Assistbehavior, as well as established multiple remote access channels through Cloudflare tunneling, Zoho Assist, and Secure Shell (SSH) connections configured through Visual Studio Code.