
Metabase Zero-Day SQL Injection Enables Unauthenticated Admin Access
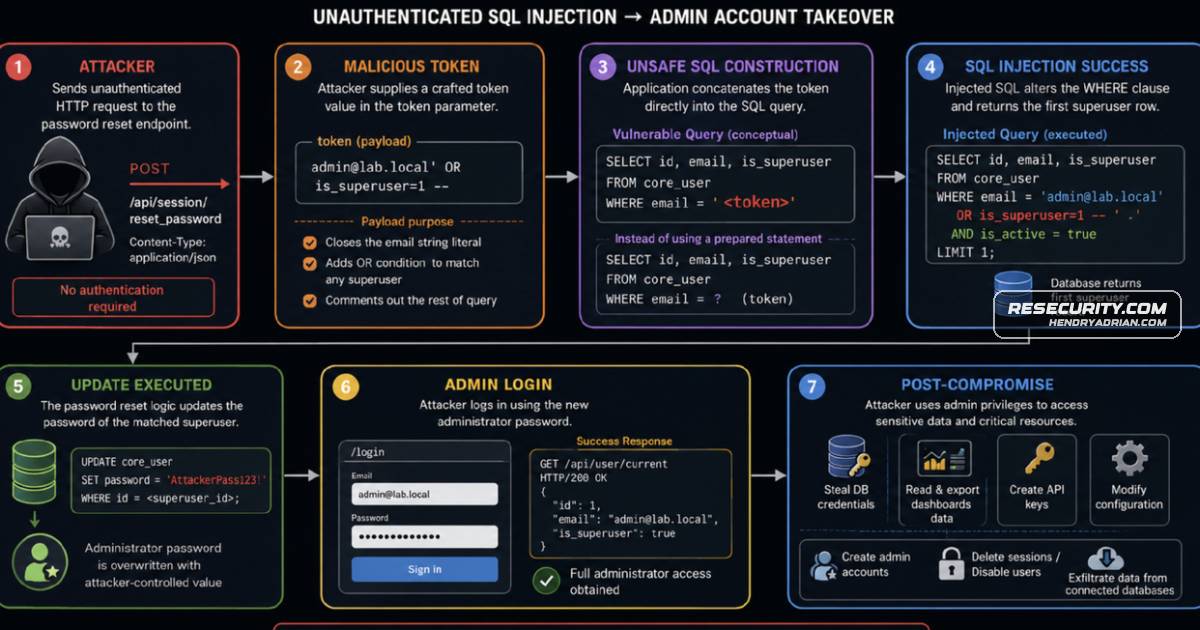
Summary
Metabase says attackers exploited GHSA-vwf4-m7j8-wcjf, an unauthenticated SQL injection in password reset that can grant admin access. Self-hosted versions need patching; Framework reported unauthorized access to customer information.
Key points
- The flaw affects the unauthenticated /api/session/reset_password endpoint: attacker-controlled user-id input can be compiled as raw SQL through HoneySQL.
- The article says exploitation was active before public disclosure; Metabase Cloud was patched, while self-hosted deployments in release trains v1.58–v1.63 are affected.
- Patched versions listed are 58.24, 59.21, 60.17, 61.11, 62.9, and 63.5.
- Successful exploitation can enable administrator access, expose stored data-source credentials, and allow creation of persistent accounts or API keys.
- Framework reported unauthorized access to customer information including names, email addresses, phone numbers, physical addresses, and login IP addresses.
- Until patched, the article recommends blocking the reset endpoint and reviewing administrator accounts, API keys, sessions, database credentials, and warehouse logs.
Article Details
- Vulnerability Types
- Unauthenticated SQL injection
- Insufficient type validation of user-id input
- Severity
- Critical (CVSS v3.1: 10.0)
- Affected Versions
- Metabase v1.58 release train: ≥58.0 and <58.23
- Metabase v1.59 release train: ≥59.0 and <59.20
- Metabase v1.60 release train: ≥60.0 and <60.16
- Metabase v1.61 release train: ≥61.0 and <61.10
- Metabase v1.62 release train: ≥62.0 and <62.8
- Metabase v1.63 release train: ≥63.0 and <63.3
- Exploitation Status
- active
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Until patched, block /api/session/reset_password at the reverse proxy or WAF.
MITRE ATT&CK
T1078 · Valid AccountsAfter changing the administrator password through the exploit, the attacker authenticates as that Metabase administrator.T1098 · Account ManipulationThe described exploit overwrites the selected administrator account's password to enable persistent access.T1136.001 · Local AccountThe article describes creating additional Metabase administrator accounts to maintain access.T1190 · Exploit Public-Facing ApplicationAn unauthenticated attacker exploits SQL injection in Metabase's publicly accessible password-reset endpoint.
Vendors
Products
MetabaseMetabase has disclosed a maximum-severity, unauthenticated SQL injection vulnerability that is being actively exploited in the wild as a zero-day.Metabase CloudAvailable in both Open Source (OSS) and Enterprise (EE) editions, as well as the fully managed Metabase Cloud service, the platform allows users to build interactive dashboards, generate reports, and perform ad hoc