
Interrupt Injection Can Bypass Linux Spectre v2 Defenses on AMD CPUs
Summary
Researchers demonstrated INTERRUPT INJECTION can exploit interrupt timing gaps in Linux Spectre v2 defenses to leak kernel memory on AMD Zen 2 with local unprivileged execution. AMD lists Zen 1–4 as affected; a Linux fix is available. Intel end-to-end leakage was not
Key points
- The technique uses precisely timed interrupts to reopen a branch-predictor training window after Spectre v2 defenses have run.
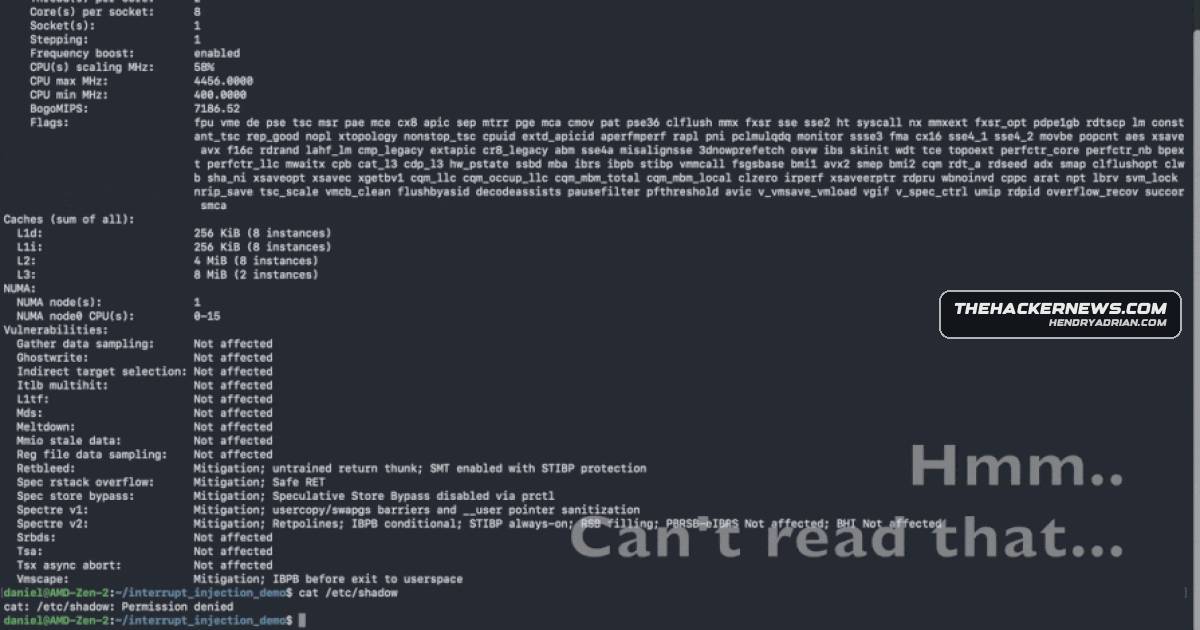
- On AMD Zen 2 with Linux 6.14 and default Spectre v2 mitigations enabled, the researchers demonstrated kernel-memory leakage using local, unprivileged code execution.
- In five of ten attempts, the researchers located and read /etc/shadow, which contains system password hashes.
- AMD bulletin AMD-SB-7061 lists Zen 1 through Zen 4 processors as affected; an end-to-end leak was demonstrated on Zen 2, while AMD's bulletin says Zen 3 and Zen 4 were suggested but not demonstrated.
- A Linux kernel fix, “Make Safe-RET robust against interrupt injection,” is available; AMD's bulletin does not identify the commit or a kernel release.
- On Intel Arrow Lake and Cascade Lake Refresh, the researchers observed kernel mispredictions but did not demonstrate an end-to-end leak; they say a usable disclosure gadget would also be needed.
- The researchers presented the work at Black Hat USA; Intel said mitigation was not required and referred to existing guidance.
Article Details
- Vulnerability Types
- Interrupt-timing race in branch predictor sanitization
- Speculative execution information disclosure
- Affected Versions
- AMD Zen 1 through Zen 4 processors
- Exploitation Status
- reported
- Exploit Availability
- none_reported
- Patch Status
- available
MITRE ATT&CK
CVE
People
Borislav PetkovAMD engineer who wrote the Linux kernel commit fixing Safe RET against interrupt injection.Daniël TrujilloMIT CSAIL researcher who co-discovered and demonstrated INTERRUPT INJECTION.David KaplanAMD engineer who co-developed the Linux kernel commit fixing Safe RET against interrupt injection.Mengjia YanMIT CSAIL researcher who co-discovered and demonstrated INTERRUPT INJECTION.
Vendors
Products
Linux kernelThey demonstrated arbitrary kernel memory disclosure on AMD Zen 2 and showed the issue affects AMD’s Safe RET mitigation on Zen 1 through Zen 4, with a Linux kernel fix already available.Safe RETThey demonstrated arbitrary kernel memory disclosure on AMD Zen 2 and showed the issue affects AMD’s Safe RET mitigation on Zen 1 through Zen 4, with a Linux kernel fix already available.