
ConnectWise Issues Temporary Mitigation for Unpatched ScreenConnect Flaw
Summary
A newly discovered ScreenConnect file-transfer flaw affects cloud and on-premises deployments. ConnectWise advises disabling TransferFiles permissions while it prepares a patch; the flaw has no CVE ID yet.
Key points
- ConnectWise identified an issue affecting file transfers in ScreenConnect Remote Access Support and Access sessions.
- The vulnerability affects both cloud-hosted and on-premises deployments and has not yet received a CVE ID.
- Administrators can temporarily mitigate the issue by disabling TransferFiles permissions, or TransferFilesInSession for legacy roles, across session groups.
- ConnectWise plans to release a permanent fix later this week.
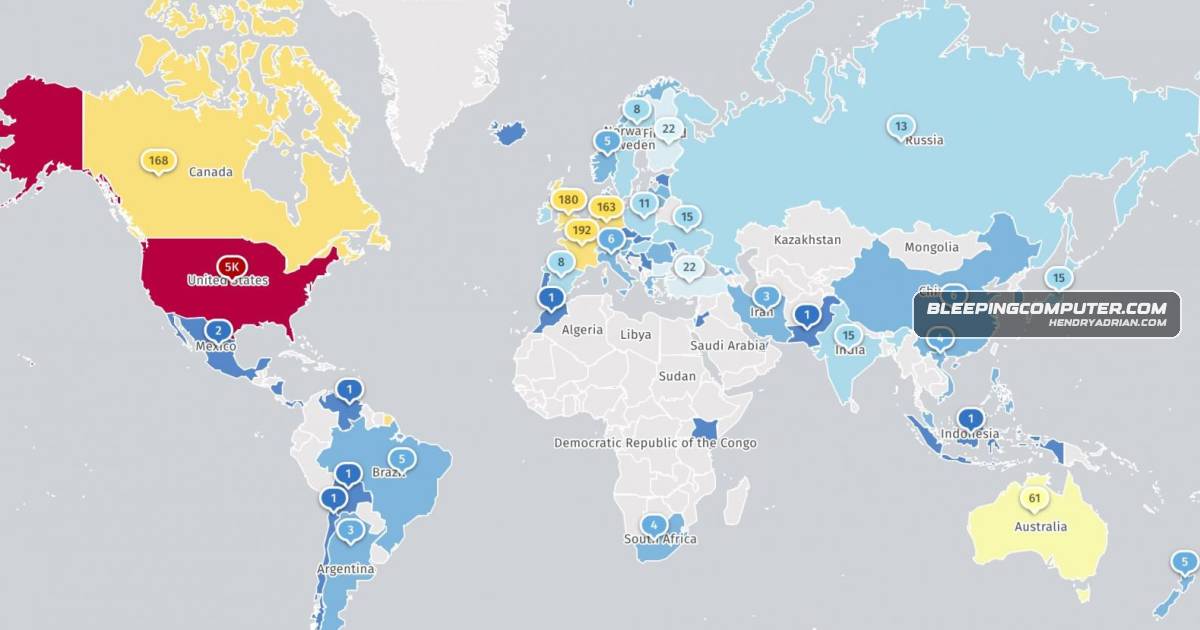
- Shadowserver tracks nearly 6,000 exposed ScreenConnect instances, but the article says it is unknown how many are honeypots or already secured.
- Previous ScreenConnect vulnerabilities have been exploited by ransomware groups and state-backed actors; that history does not establish exploitation of this newly reported flaw.
Article Details
- Vulnerability Types
- File transfer behavior vulnerability
- Severity
- Unknown
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- unavailable
- Workarounds
- Deselect the TransferFiles permission (or TransferFilesInSession for legacy) for each session group across all user roles.
CVE
Threat Actors
Vendors
Products
ConnectWise ScreenConnectConnectWise has issued temporary mitigations for a newly discovered ScreenConnect Remote Access vulnerability that affects both cloud and on-premises deployments and will be patched later this week.ScreenConnectConnectWise has issued temporary mitigations for a newly discovered ScreenConnect Remote Access vulnerability that affects both cloud and on-premises deployments and will be patched later this week.