
N-able patches critical N-central RCE; exploitation remains unconfirmed
Summary
N-able released N-central 2026.3 HF4 for unauthenticated RCE CVE-2026-86218. The company says exploitation is unconfirmed; Huntress flagged possible zero-day activity, and Shadowserver tracks nearly 1,500 exposed servers.
Key points
- CVE-2026-86218 is a low-complexity, unauthenticated remote code execution flaw affecting exposed, unpatched N-central systems.
- N-able released N-central 2026.3 Hotfix 4 and urged on-premises customers to install it immediately; HF3 remains vulnerable.
- N-able said it has no confirmation that CVE-2026-86218 was exploited in production.
- Huntress flagged the flaw as a potential zero-day but could not determine whether it was used in a customer incident because server logs had rotated.
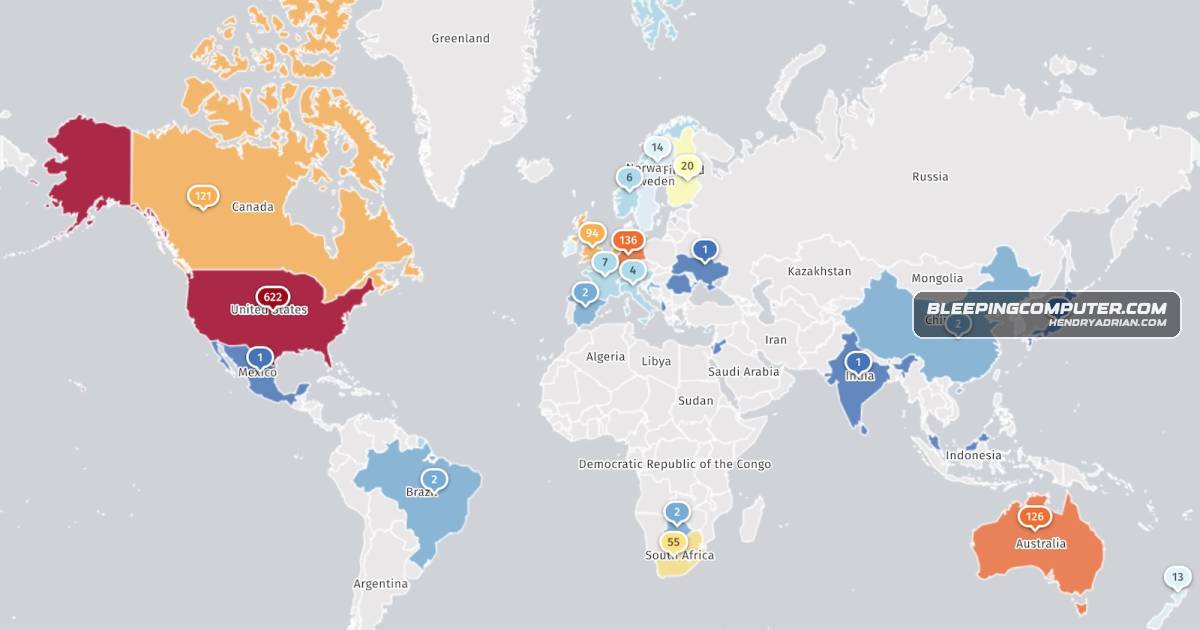
- Shadowserver tracks nearly 1,500 internet-exposed N-central servers, most in the United States and Europe.
- The hotfix also addresses CVE-2026-86206 and CVE-2026-86207, which Huntress said could enable authentication bypass and full platform access.
Article Details
- Vulnerability Types
- Remote code execution
- Authentication bypass
- Severity
- Maximum severity
- Affected Versions
- N-central 2026.3 HF3 (vulnerable)
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- On-premises customers should upgrade to N-central 2026.3 HF4.
MITRE ATT&CK
CVE
CVE-2025-8875One year ago, N-able released security updates for two N-central vulnerabilities (CVE-2025-8875 and CVE-2025-8876) that attackers were exploiting in the wild.CVE-2025-8876One year ago, N-able released security updates for two N-central vulnerabilities (CVE-2025-8875 and CVE-2025-8876) that attackers were exploiting in the wild.CVE-2026-86206Two additional flaws, CVE-2026-86206 and CVE-2026-86207, were also fixed.CVE-2026-86207Two additional flaws, CVE-2026-86206 and CVE-2026-86207, were also fixed.CVE-2026-86218N-able has issued an emergency hotfix for CVE-2026-86218, a maximum-severity RCE flaw in its N-central RMM platform that could let unauthenticated attackers run malicious code on exposed systems.