
Over 36,000 Internet-Exposed Plex Servers Remain Unpatched Against Security Flaws
Summary
Plex says multiple flaws affect Media Server v1.43.2 and earlier and urges users to upgrade. Shadowserver reports more than 36,000 exposed instances remain unpatched; the flaws have no CVE IDs yet.
Key points
- The flaws affect Plex Media Server v1.43.2 and earlier; Plex has not yet provided further details or CVE IDs.
- Plex recommends upgrading Media Server to 1.43.3 and Plex Desktop to 1.115.0.
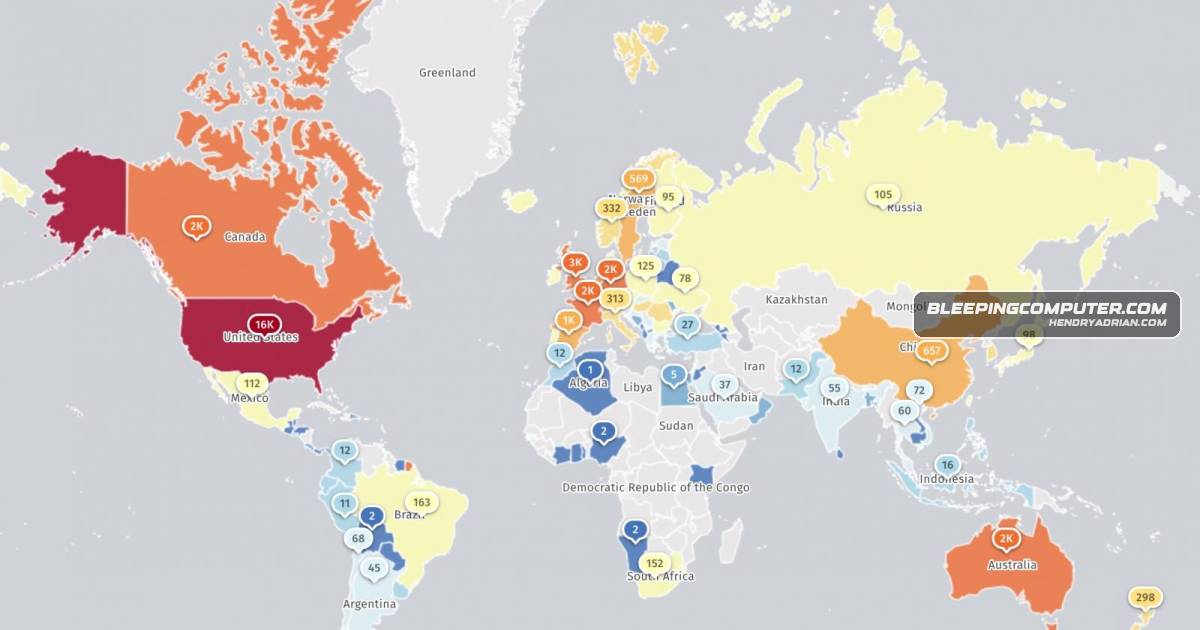
- Shadowserver reported more than 36,000 internet-exposed, unpatched Plex Media Server instances and said it is scanning daily.
- Plex warned users to update before attackers reverse-engineer the fixes and develop exploits.
- The article also cites earlier Plex flaws CVE-2025-34158 and CVE-2020-5741; it says CISA flagged CVE-2020-5741 as actively exploited.
Article Details
- Affected Versions
- Plex Media Server v1.43.2 and earlier
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- available
CVE
Vendors
Products
Plex DesktopUsers are urged to upgrade to Plex Media Server 1.43.3 and Plex Desktop 1.115.0 before attackers reverse-engineer the fixes and exploit the vulnerabilities.Plex Media ServerPlex has warned that more than 36,000 internet-exposed Plex Media Server instances remain unpatched against multiple security flaws affecting Plex Media Server v1.43.2 and earlier.