cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · bleepingcomputer.com

Attackers Exploit Vite Flaw to Steal AWS and Azure Secrets

F5 observed more than 800 attacks and about 32,000 events targeting exposed Vite servers through CVE-2026-39364, with attempts to access cloud credentials and other secrets. Developers should update Vite, restrict access, and rotate exposed secrets.

Sep 14, 2026
Vulnerability & Exploit · rapid7.com

Critical GitLab Path Traversal Vulnerability Actively Exploited; Emergency Patching Urged

CVE-2026-85706, a critical unauthenticated path traversal flaw in self-managed GitLab CE/EE, is being exploited in the wild. GitLab has released fixes, and organizations are urged to patch immediately and check for compromise.

Sep 14, 2026
Vulnerability & Exploit · securityweek.com

Three JFrog Artifactory Flaws Exploited to Deploy Backdoors

Wiz reports attackers exploited three JFrog Artifactory flaws to gain access, escalate privileges, and deploy backdoors. Organizations are urged to update self-managed deployments to patched versions.

Sep 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns of Active Exploitation of Critical GitLab Vulnerability

CISA says attackers are exploiting GitLab flaw CVE-2026-85706, which can expose credentials and other sensitive data. GitLab released fixes, and CISA urges organizations to patch and check for probing.

Sep 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

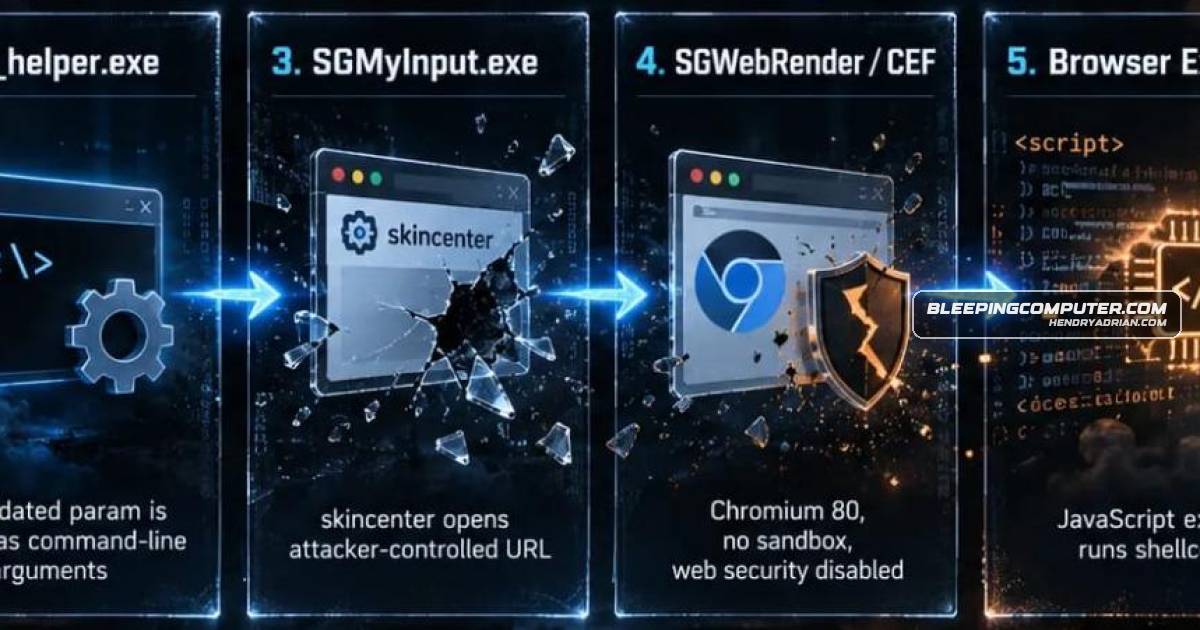
Hackers Exploit Sogou Input Method Flaw to Install GrayRabbit Backdoor

Gen Digital reports that UNC3569 exploited CVE-2026-51990 in Sogou Input Method for Windows to install GrayRabbit via a crafted link. Tencent patched the flaw in version 16.3.0.3498, though the browser remains outdated and unsandboxed.

Sep 13, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Five Actively Exploited Artifactory, ScreenConnect and RouterOS Flaws to KEV

CISA added five actively exploited flaws in Artifactory, ScreenConnect and RouterOS to its KEV catalog. Reports describe privilege escalation, backdoor deployment and device takeover; agencies face September patch deadlines.

Sep 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

Dutch NCSC warns of imminent exploitation of two critical Check Point VPN flaws

The Dutch NCSC expects attacks on two critical Check Point VPN flaws soon. Affected organizations should install fixes and restrict Site-to-Site VPN access to trusted IP addresses.

Sep 12, 2026
Vulnerability & Exploit · cyberscoop.com

GitLab Patches Two Critical Flaws as Internet Probing Is Reported

GitLab patched two critical flaws, including an unauthenticated path traversal that could expose files on self-managed servers. WatchTowr Labs reported probing, and CISA added both vulnerabilities to its KEV list.

Sep 11, 2026
Vulnerability & Exploit · thehackernews.com

GitLab Patches Critical File-Read Flaw After Reports of In-the-Wild Probes

GitLab patched CVE-2026-85706, a CVSS 10.0 path traversal flaw that could let unauthenticated attackers read files. watchTowr reported in-the-wild probes; GitLab also fixed a critical EE deserialization flaw.

Sep 11, 2026
Vulnerability & Exploit · bleepingcomputer.com

GitLab Patches Critical Path Traversal Flaw After Probing Begins

GitLab patched CVE-2026-85706, a maximum-severity path traversal flaw that could expose arbitrary data under certain conditions. watchTowr reported probing of exposed, unpatched servers; GitLab also fixed CVE-2026-87719.

Sep 11, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Chain JFrog Artifactory Flaws to Deploy Rust Backdoor

Wiz reports attackers chained three JFrog Artifactory flaws to gain admin access, steal data, and deploy a Rust backdoor. Administrators should upgrade to fixed versions and investigate exposed instances.

Sep 11, 2026
Vulnerability & Exploit · securityweek.com

GitLab Path Traversal Exploitation Attempts Observed One Day After Disclosure

WatchTowr reports in-the-wild probes targeting GitLab CVE-2026-85706 one day after disclosure. The unauthenticated path traversal can expose arbitrary server files; affected self-hosted instances should upgrade to patched releases.

Sep 11, 2026
Vulnerability & Exploit · thehackernews.com

Check Point Patches Two Critical VPN Certificate Flaws That Could Enable Unauthenticated RCE

Check Point patched two CVSS 9.8 VPN certificate flaws that could enable unauthenticated remote code execution on affected Security Gateway and Security Management systems. The company reports no known exploitation and is distributing fixes through Live Patch and Jumbo

Sep 11, 2026
Vulnerability & Exploit · resecurity.com

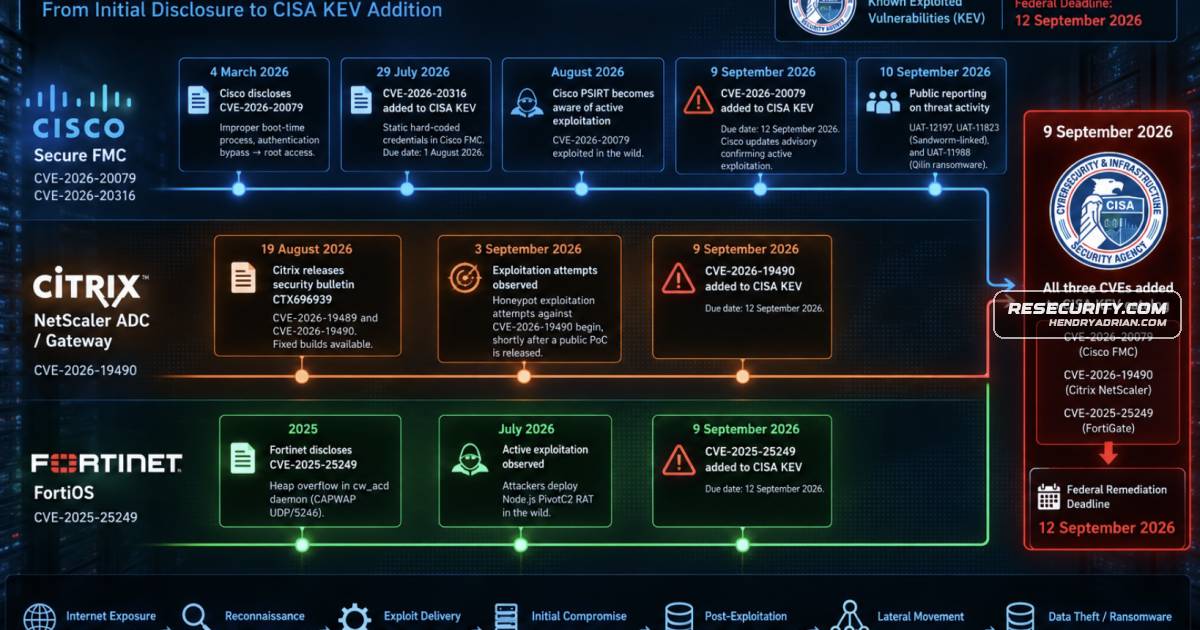
CISA Adds Three Cisco, Citrix and Fortinet Flaws to KEV After Exploitation Reports

CISA added three actively exploited Cisco, Citrix and Fortinet vulnerabilities to its KEV catalog on Sept. 9, 2026, with a Sept. 12 federal remediation deadline. The article details affected builds, exploit paths and mitigations.

Sep 11, 2026
Vulnerability & Exploit · fieldeffect.com

Check Point Patches Two Critical VPN Certificate-Processing Vulnerabilities

Check Point disclosed and began patching two CVSS 9.8 flaws in VPN certificate processing affecting Quantum Security Gateway, Security Management Server, and Spark Firewall products. The flaws may allow code execution under specific conditions.

Sep 11, 2026
Vulnerability & Exploit · fieldeffect.com

GitLab Patches Critical File-Access Flaw as Internet-Wide Probing Begins

GitLab patched critical unauthenticated path traversal flaw CVE-2026-85706 in self-managed CE and EE; researchers reported internet-wide probing beginning September 11. Exposed files may include credentials and tokens.

Sep 11, 2026
Vulnerability & Exploit · wiz.io

Attackers Exploit Three JFrog Artifactory Vulnerabilities to Gain Admin Access and Deploy Backdoors

Wiz reports active exploitation of three Artifactory flaws to bypass authentication and gain administrator access. Attackers have deployed persistent accounts, malicious Groovy plugins, and Rust backdoors; affected instances should be patched and investigated for signs,

Sep 10, 2026
Vulnerability & Exploit · helpnetsecurity.com

Cisco FMC Vulnerabilities CVE-2026-20079 and CVE-2026-20316 Exploited in Attacks

Cisco Talos reports three intrusion clusters exploiting two Cisco FMC flaws for unauthorized access, credential theft, reconnaissance and ransomware deployment. Cisco urges customers to apply hotfixes or block internet access to the management interface.

Sep 10, 2026
Vulnerability & Exploit · securityonline.info

ChatGPT Flaw Let Attackers Extract Data From Other Users’ Sessions

Check Point Research found that a shared internal Artifactory service could let hidden instructions in shared chats or custom GPTs relay data from a victim’s ChatGPT session. OpenAI decommissioned the service; no in-the-wild exploitation is confirmed.

Sep 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

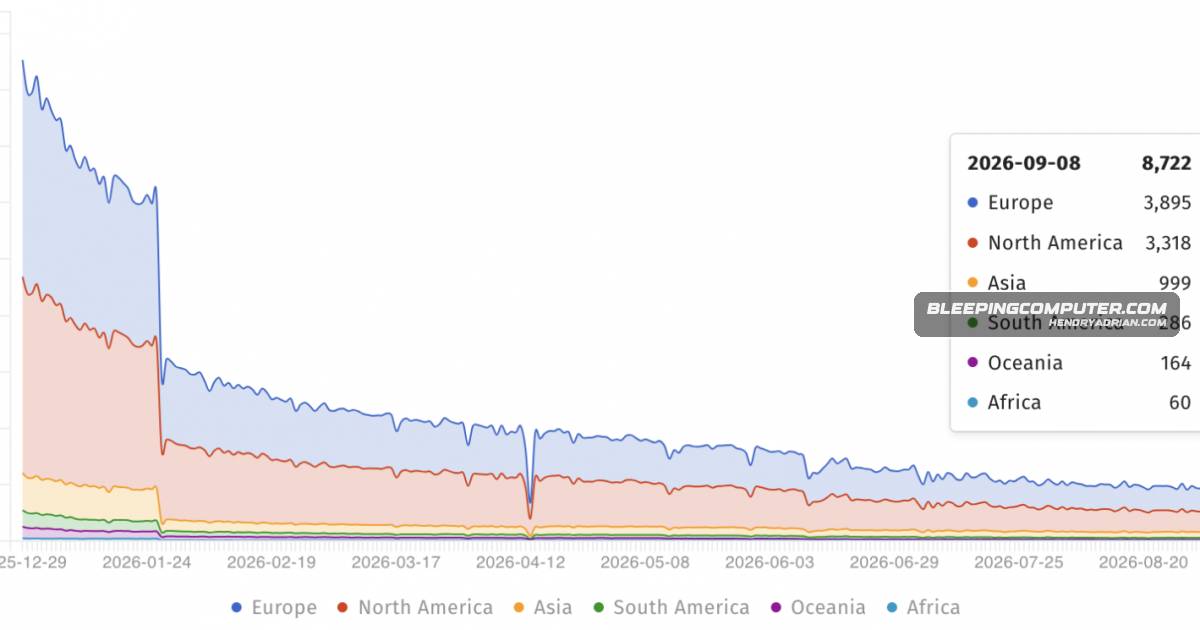
CISA Says Ransomware Gangs Are Exploiting WatchGuard Firebox RCE Flaw

CISA says ransomware gangs are exploiting CVE-2025-14733, an unauthenticated RCE flaw in WatchGuard Firebox firewalls. Multiple Fireware OS branches are affected, and nearly 9,000 unpatched devices reportedly remain exposed.

Sep 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

Skullcandy Dime 3 Earbuds Allow Unauthenticated Bluetooth Pairing

CERT/CC warns that Skullcandy Dime 3 earbuds on firmware 1.0.0.28 allow nearby devices to pair without approval, enabling audio and microphone access. Firmware 1.0.0.30 fixes the flaw, but customers cannot currently update existing units themselves.

Sep 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Confirms Active Exploitation of Critical Secure FMC Flaw

Cisco says unauthenticated attackers are exploiting CVE-2026-20079 to run commands as root on vulnerable Secure FMC systems. Cisco and CISA urge patching; hot fixes prevent future attacks but do not clean compromised devices.

Sep 10, 2026
Vulnerability & Exploit · fieldeffect.com

N-able patches actively exploited, maximum-severity N-central flaw

CISA added N-able N-central flaw CVE-2026-86218 to its Known Exploited Vulnerabilities catalog. N-able issued a hotfix for affected self-hosted deployments; hosted deployments received vendor-applied remediation.

Sep 10, 2026
Vulnerability & Exploit · securityweek.com

Google Patches 180 Vulnerabilities in September Android Update

Google’s September 2026 Android updates patch 180 vulnerabilities, including critical flaws that could enable remote code execution. Devices on patch level 2026-09-05 or newer receive the fixes.

Sep 9, 2026
PreviousPage 31 of 65 Next
© 2026 cyber.hendryadrian.com