cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · thehackernews.com

Attackers Exploit Issabel Framework Flaw for Unauthenticated Command Execution

CVE-2026-89026, a critical Issabel Framework flaw involving a hard-coded JWT key, is being exploited to run commands without authentication. A patch was released August 1, 2026; Shadowserver first observed exploitation September 9.
Sep 17, 2026
Vulnerability & Exploit · bitsight.com

Critical Cisco ISE Authentication Bypass CVE-2026-76460 Under Active Exploitation

Cisco confirms active exploitation of CVE-2026-76460, a critical unauthenticated remote authentication bypass in ISE and ISE-PIC that may enable root-level command execution. Cisco urges patching and recommends re-imaging if compromise is suspected.

Sep 17, 2026
Vulnerability & Exploit · fieldeffect.com

Attackers Test Critical WSO2 Authentication Bypass; Patches Available

Researchers observed attempts to exploit WSO2 CVE-2026-5430, an authentication bypass that can grant administrative access. Fixes were released in May 2026; exposed deployments should be patched and reviewed for unauthorized activity.

Sep 17, 2026
Vulnerability & Exploit · fieldeffect.com

Cisco patches actively exploited authentication bypass in ISE and ISE-PIC

Cisco patched an actively exploited authentication bypass in ISE and ISE-PIC that allows unauthenticated remote access to a management API and may enable root-level command execution. Upgrade to a fixed release and restrict management access.

Sep 17, 2026
Vulnerability & Exploit · abstract.security

Critical GitLab File-Read Flaw CVE-2026-85706 Exploited; Patch Self-Managed Instances

CVE-2026-85706 lets unauthenticated attackers read files from vulnerable self-managed GitLab servers. CISA confirmed exploitation; GitLab has patched affected releases, and exposed instances should be investigated and credentials rotated.

Sep 17, 2026
Vulnerability & Exploit · helpnetsecurity.com

Parallels Desktop flaw can give local users root access on Macs

JFrog disclosed CVE-2026-90894, an argument injection flaw affecting Parallels Desktop 26.4.0 on Apple silicon Macs. Alludo fixed it in version 27.0.0; exploitation requires local code execution and an active service.

Sep 16, 2026
Vulnerability & Exploit · bleepingcomputer.com

Critical ScreenConnect flaw exploited in attacks; CISA orders federal agencies to patch

CISA says attackers are exploiting ScreenConnect flaw CVE-2026-84869. ConnectWise patched it in version 26.6.5 and recommends disabling TransferFiles permissions temporarily; over 1,000 exposed instances remain unpatched.

Sep 16, 2026
Vulnerability & Exploit · securityweek.com

Two Critical WordPress Plugin Flaws Could Enable Unauthenticated Site Takeovers

Two critical unauthenticated flaws in The Events Calendar plugin can lead to remote code execution and site takeover. Patches are available, but many installations may remain vulnerable; exploitation requires comments to be enabled.

Sep 16, 2026
Vulnerability & Exploit · bleepingcomputer.com

Acronis Patches Linux Privilege-Escalation Flaw in cPanel and Plesk Backup Plugins

Acronis says CVE-2026-87886, a Linux local privilege-escalation flaw in its cPanel & WHM and Plesk backup integrations, was exploited in limited targeted attacks, based on one report from a potentially affected customer. Updates are available.

Sep 16, 2026
Vulnerability & Exploit · fieldeffect.com

Cisco Secure Email Gateway Zero-Day Exploited for Root Access

Cisco confirmed active exploitation of a critical SQL injection in Secure Email Gateway that can give attackers unauthenticated root access via crafted email. Fixed AsyncOS releases are available; Cisco also provided investigation guidance.

Sep 16, 2026
Vulnerability & Exploit · sophos.com

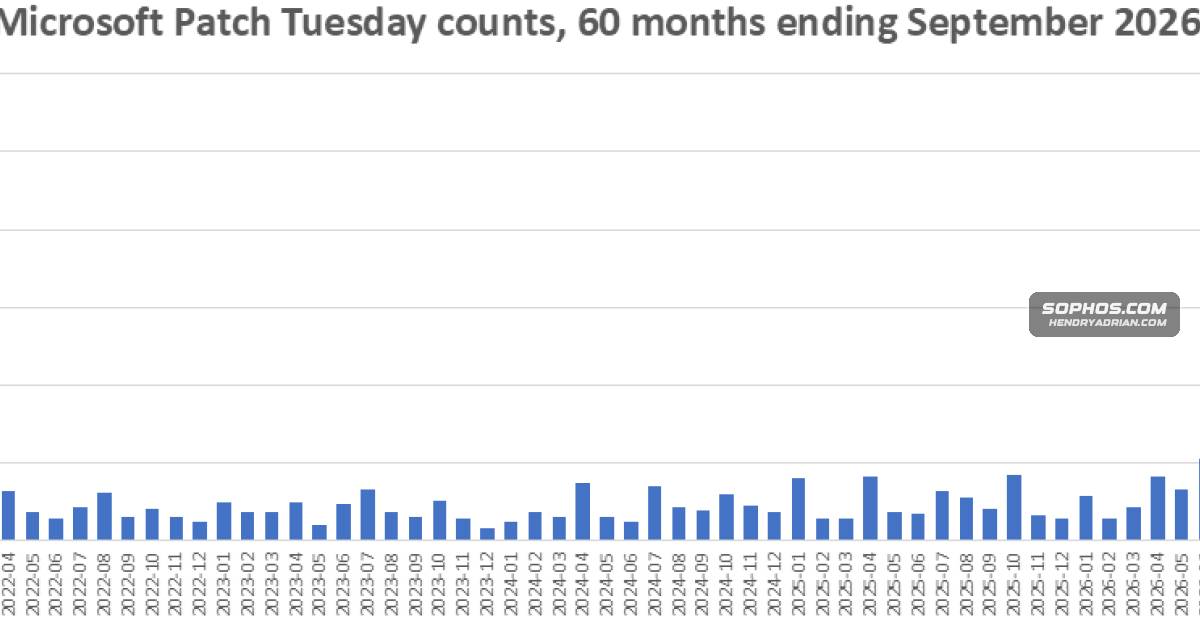
Microsoft’s September Patch Tuesday Addresses 973 CVEs Across 39 Product Families

Microsoft released 973 September patches across 39 product families. Two Windows elevation-of-privilege flaws were actively exploited, and 82 Office for Mac fixes were still pending; an Exchange flaw was patched out of band on October 2.

Sep 16, 2026
Vulnerability & Exploit · cyberscoop.com

Cisco Zero-Day in Secure Email Gateway Exploited for Root Access

Cisco says attackers actively exploited CVE-2026-76461, an unauthenticated root-level command-execution flaw in Secure Email Gateway. Cisco contacted cloud customers with possible compromise indicators and released patches and hunting guidance.

Sep 15, 2026
Vulnerability & Exploit · arcticwolf.com

Arctic Wolf Warns of Exploited Cisco Secure Email Gateway Zero-Day

Arctic Wolf reports active exploitation of a pre-authentication SQL injection in Cisco Secure Email Gateway that can enable root code execution via crafted email. Fixed AsyncOS releases are available; it says patching is the only effective remediation.

Sep 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Says Ransomware Gangs Are Exploiting Critical VMware vCenter Flaw

CISA says ransomware gangs are exploiting VMware vCenter flaw CVE-2026-59310. Broadcom patched the directory traversal flaw in July; QUIRSO reported 361 compromised IP addresses, and more than 450 vCenter servers remain exposed online.

Sep 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Exploit WooCommerce Plugin Flaw to Upload PHP Webshells

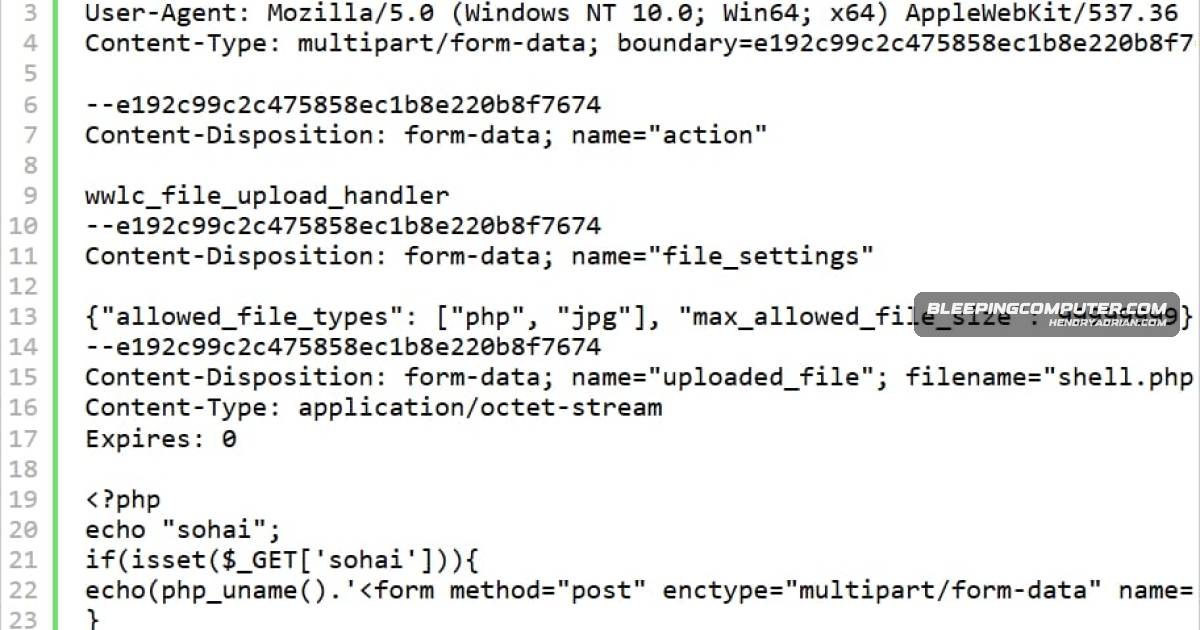
CVE-2026-27540 lets unauthenticated attackers upload PHP webshells through the WooCommerce Wholesale Lead Capture plugin. Wordfence reports over 100,000 blocked attempts; admins should update to version 2.0.3.2 or later and check for compromise.

Sep 15, 2026
Vulnerability & Exploit · rapid7.com

Critical Cisco Email Gateway Flaw Exploited in the Wild; Patch Immediately

Cisco says attackers are exploiting CVE-2026-76461, a critical SQL injection in Secure Email Gateway that can enable unauthenticated root command execution. Fixed versions are available; Cisco urges customers to upgrade urgently.

Sep 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Patches Actively Exploited Secure Email Gateway Zero-Day Allowing Root Command Execution

Cisco confirmed active exploitation of CVE-2026-76461, which can let unauthenticated attackers run commands as root on Secure Email Gateway appliances. CISA added it to KEV and ordered federal agencies to patch within three days.

Sep 15, 2026
Vulnerability & Exploit · thehackernews.com

Actively Exploited Cisco Email Gateway Flaw Enables Unauthenticated Root Command Execution

Cisco says attackers are exploiting CVE-2026-76461 in Secure Email Gateway. The flaw allows unauthenticated root command execution; updates are available, and CISA added it to KEV.

Sep 15, 2026
Vulnerability & Exploit · securityweek.com

Cisco Secure Email Gateway Zero-Day Exploited to Run Commands as Root

Cisco says attackers are exploiting CVE-2026-76461, an unauthenticated flaw in Secure Email Gateway that can allow root-level command execution. CISA added it to its KEV catalog and set a September 17 remediation deadline for federal agencies.

Sep 15, 2026
Vulnerability & Exploit · fieldeffect.com

Researchers Report Scanning of Exposed Vite Servers for Sensitive Files

Researchers recorded 807 sessions and about 32,000 events targeting exposed Vite servers in August 2026. The activity attempted to retrieve sensitive files through CVE-2026-39364, fixed in Vite 7.3.2 and 8.0.5.

Sep 15, 2026
Vulnerability & Exploit · sophos.com

Critical Cisco Secure Email Gateway flaw CVE-2026-76461 exploited in the wild

Cisco confirmed active exploitation of critical CVE-2026-76461, an unauthenticated remote SQL injection flaw in Cisco Secure Email Gateway that could enable root-level command execution.

Sep 15, 2026
Vulnerability & Exploit · thehackernews.com

Telegram Desktop Flaw Could Let Hidden JavaScript Steal Messages From HTML Exports

A Telegram Desktop export flaw let bot button text inject JavaScript into HTML chat exports, potentially exposing that file’s contents or altering its display when opened in a browser. The issue is fixed; older exports remain risky.

Sep 14, 2026
Vulnerability & Exploit · arcticwolf.com

Check Point Patches Two Critical VPN Vulnerabilities Enabling Unauthenticated RCE

Check Point released patches for two CVSS 9.8 vulnerabilities affecting Security Gateway, Management Server and Spark Firewall. Both may enable unauthenticated remote code execution; no active exploitation or public PoC was known at publication.

Sep 14, 2026
Vulnerability & Exploit · arcticwolf.com

CVE-2026-84869 Enables Unauthorized File Transfer and Execution in ScreenConnect

Arctic Wolf reports that CVE-2026-84869 affects ScreenConnect clients before 26.6.5, allowing file transfer and execution through active sessions without host confirmation. It recommends upgrading; workarounds only mitigate risk.

Sep 14, 2026
PreviousPage 30 of 65 Next
© 2026 cyber.hendryadrian.com