
CISA Adds Three Cisco, Citrix and Fortinet Flaws to KEV After Exploitation Reports
Summary
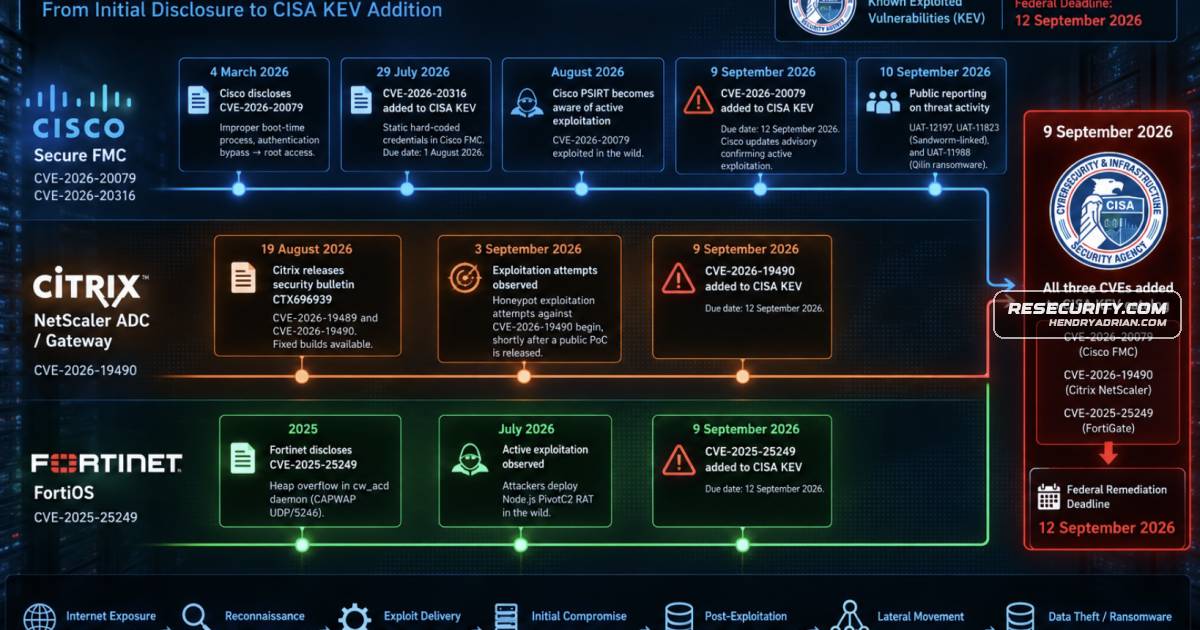
CISA added three actively exploited Cisco, Citrix and Fortinet vulnerabilities to its KEV catalog on Sept. 9, 2026, with a Sept. 12 federal remediation deadline. The article details affected builds, exploit paths and mitigations.
Key points
- CISA added CVE-2026-20079, CVE-2026-19490 and CVE-2025-25249 to its KEV catalog on Sept. 9, 2026; the federal remediation deadline was Sept. 12.
- Cisco confirmed active exploitation of CVE-2026-20079, an authentication bypass in Secure Firewall Management Center that can lead to root access. Talos linked activity to multiple intrusion clusters.
- CVE-2026-19490 is a configuration-dependent authentication bypass affecting Citrix NetScaler ADC/Gateway. Citrix says no workaround exists and recommends upgrading to fixed builds.
- CVE-2025-25249 is a pre-authentication heap overflow in Fortinet's cw_acd daemon handling CAPWAP traffic. Threat-intelligence reporting cited more than 30,000 targeted FortiGate IP addresses and 178 confirmed infections involving PivotC2.
- The article provides affected and fixed releases, explains the reported exploit paths, and recommends patching, checking for compromise, and restricting unnecessary access to management interfaces and CAPWAP ports.
Article Details
- Vulnerability Types
- Authentication bypass
- Pre-authentication heap-based buffer overflow
- Severity
- High-impact; CVE-2026-20079 is CVSS v3.1 10.0 (critical), and CVE-2026-19490 is CVSS v4.0 9.3 (critical). No score is provided for CVE-2025-25249.
- Affected Versions
- Cisco Secure Firewall Management Center (FMC) Software 7.0 (affected builds; exact builds not specified)
- Cisco Secure Firewall Management Center (FMC) Software 7.2 (affected builds; exact builds not specified)
- Cisco Secure Firewall Management Center (FMC) Software 7.4 (affected builds; exact builds not specified)
- Cisco Secure Firewall Management Center (FMC) Software 7.6 (affected builds; exact builds not specified)
- Cisco Secure Firewall Management Center (FMC) Software 7.7 (affected builds; exact builds not specified)
- Cisco Secure Firewall Management Center (FMC) Software 10.0 (affected builds; exact builds not specified)
- Citrix NetScaler ADC / NetScaler Gateway 14.1 before 14.1-73.32
- Citrix NetScaler ADC / NetScaler Gateway 13.1 before 13.1-63.21
- FortiOS 7.6 before 7.6.4
- FortiOS 7.4 before 7.4.9
- FortiOS 7.2 before 7.2.12
- FortiOS 7.0 before 7.0.18
- FortiSwitchManager 7.2 before 7.2.7
- FortiSwitchManager 7.0 before 7.0.6
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Citrix states that no workaround exists; if patching is delayed, restrict Gateway/AAA access to known source IPs and enforce MFA at a downstream identity provider.
- For Fortinet, block inbound UDP 5246–5249 from untrusted sources and disable fabric access on WAN-facing interfaces.
- For Cisco FMC, place management access behind a jump host or management VPN and restrict outbound internet access.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 146[.]103[.]99[.]177 | Reported outbound C2 IP address associated with Fortinet exploitation activity. |
| IPV4 | 46[.]151[.]29[.]58 | Reported outbound C2 IP address associated with Fortinet exploitation activity. |
MITRE ATT&CK
T1018 · Remote System DiscoveryPivotC2 is described as supporting network scanning for internal reconnaissance.T1021.001 · Remote Desktop ProtocolThe article describes attackers using compromised NetScaler access to establish RDP sessions and access RDP hosts.T1059.004 · Unix ShellOn Cisco FMC, the attacker triggers execution as root of a malicious Makeself-format shell script at /var/tmp/license.tmp.T1059.007 · JavaScriptThe Fortinet chain spawns a Node.js reverse shell and writes the PivotC2 backdoor.T1078 · Valid AccountsThe Cisco FMC exploit uses the hard-coded machine account report:snortrules to upgrade the hijacked session.T1090 · ProxyPivotC2 provides SOCKS5/HTTP proxy tunneling and port forwarding from compromised Fortinet appliances.T1105 · Ingress Tool TransferThe Fortinet exploit chain uses a stager to download and execute a Node.js payload.T1190 · Exploit Public-Facing ApplicationAttackers exploited network-reachable Cisco FMC, Citrix NetScaler, and Fortinet appliances through unauthenticated requests or CAPWAP traffic.T1486 · Data Encrypted for ImpactThe article associates Qilin ransomware activity with encryption of critical systems.T1505.003 · Web ShellUAT-12197 reportedly deploys JSP web shells on compromised Cisco FMC appliances.T1550.004 · Web Session CookieThe Cisco FMC exploit hijacks a persistent boot-time session by supplying the CGISESSID cookie value csm_processes.T1562.001 · Disable or Modify ToolsUAT-11988 is reported to conduct antivirus killing during post-compromise activity.T1573 · Encrypted ChannelCompromised Fortinet appliances maintain C2 through outbound TLS connections.
CVE
CVE-2025-25249CVE-2025-25249 — Fortinet FortiOS: A pre-authentication heap-based buffer overflow in the cw_acd daemon that can result in remote code or command execution.CVE-2026-1948919 August 2026: Citrix publishes security bulletin CTX696939 covering CVE-2026-19489 and CVE-2026-19490, with fixed NetScaler builds provided.CVE-2026-19490CVE-2026-19490 — Citrix NetScaler ADC/Gateway: An authentication-bypass vulnerability affecting Gateway and AAA virtual-server configurations under specific conditions.CVE-2026-20079CVE-2026-20079 — Cisco Secure Firewall Management Center (FMC): An unauthenticated authentication-bypass vulnerability that can result in root access to the underlying FMC appliance.CVE-2026-2031629 July 2026: Cisco discloses CVE-2026-20316, a separate FMC vulnerability involving static credentials. CISA adds the vulnerability to the KEV catalog with a federal remediation due date of 1 August 2026.
Threat Actors
QilinThe article associates Qilin ransomware operations with UAT-11988 and reports ransomware deployment following exploitation activity.SandwormThe article says UAT-11823 is linked to Sandworm, which it describes as a Russian state-sponsored APT associated with exploitation of CVE-2026-20079.UAT-11823Cisco Talos tracks this intrusion cluster as exploiting CVE-2026-20079; it is linked in the article to Sandworm and reportedly deploys Cyclops Blink and harvests managed-firewall configurations.UAT-11988Cisco Talos tracks this intrusion cluster as exploiting FMC vulnerabilities; the article identifies it as a Qilin ransomware operator and reports reconnaissance, credential theft, antivirus killing, and ransomware deployment.UAT-12197Cisco Talos tracks this intrusion cluster as exploiting CVE-2026-20079; it reportedly deploys JSP web shells and a malicious JAR to harvest credentials.
Malware
Cyclops Blinkand UAT-11988. The activity includes web shells, credential theft, reverse-shell and proxy tooling, Cyclops Blink, and Qilin-associated ransomware activity.PivotC2Threat-intelligence reporting identified more than 30,000 targeted FortiGate IP addresses and 178 confirmed infections, with attackers deploying the PivotC2 Node.js post-exploitation framework.
Vendors
CiscoCVE-2026-20079 — Cisco Secure Firewall Management Center (FMC): An unauthenticated authentication-bypass vulnerability that can result in root access to the underlying FMC appliance.CitrixCVE-2026-19490 — Citrix NetScaler ADC/Gateway: An authentication-bypass vulnerability affecting Gateway and AAA virtual-server configurations under specific conditions.FortinetCVE-2025-25249 — Fortinet FortiOS: A pre-authentication heap-based buffer overflow in the cw_acd daemon that can result in remote code or command execution.
Products
Cisco Secure Firewall Management CenterCVE-2026-20079 — Cisco Secure Firewall Management Center (FMC): An unauthenticated authentication-bypass vulnerability that can result in root access to the underlying FMC appliance.Fortinet FortiGateThreat-intelligence reporting identified more than 30,000 targeted FortiGate IP addresses and 178 confirmed infections, with attackers deploying the PivotC2 Node.js post-exploitation framework.FortiOSCVE-2025-25249 — Fortinet FortiOS: A pre-authentication heap-based buffer overflow in the cw_acd daemon that can result in remote code or command execution.FortiSASEFortinet FortiOS / FortiSwitchManager / FortiSASEFortiSwitchManagerFortinet FortiOS / FortiSwitchManager / FortiSASENetScaler ADCCVE-2026-19490 — Citrix NetScaler ADC/Gateway: An authentication-bypass vulnerability affecting Gateway and AAA virtual-server configurations under specific conditions.NetScaler GatewayNetScaler Gateway is the SSL VPN and secure remote-access module built on top of the ADC platform.