Hackers Exploit Sogou Input Method Flaw to Install GrayRabbit Backdoor
Summary
Gen Digital reports that UNC3569 exploited CVE-2026-51990 in Sogou Input Method for Windows to install GrayRabbit via a crafted link. Tencent patched the flaw in version 16.3.0.3498, though the browser remains outdated and unsandboxed.
Key points
- Gen Digital says UNC3569 exploited the flaw in the wild to deliver the GrayRabbit backdoor.
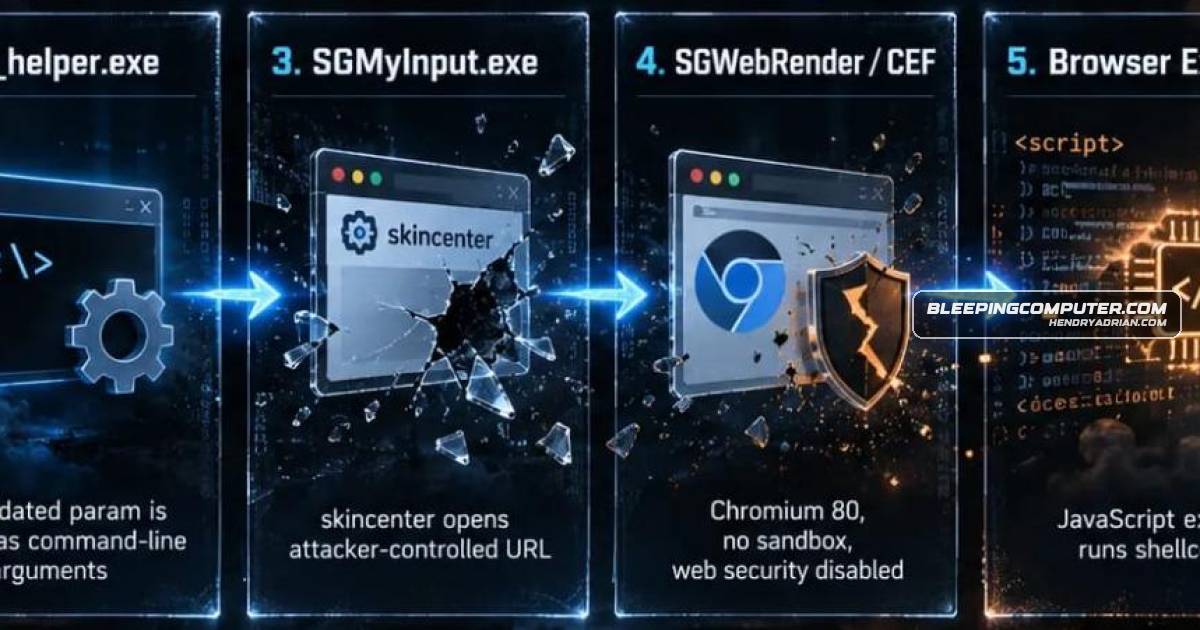
- The attack starts when a victim clicks a crafted sgbiz: URI, which passes attacker-controlled arguments to Sogou’s helper and executable.
- The chain directs Sogou’s embedded Chromium webview to an attacker-controlled page, where an exploit reportedly achieves code execution.
- The analyzed GrayRabbit variant supports process execution, reverse shells, file transfer, system and user data collection, and in-memory plugin loading.
- Tencent released a fix in Sogou Input Method version 16.3.0.3498, validating URL arguments and restricting schemes and destinations.
- Researchers warn that the browser remains outdated and unsandboxed, with web-security protections disabled.
Article Details
- Vulnerability Types
- Command-line argument injection
- Unrestricted URL navigation
- Remote code execution through exploitation of the outdated Chromium engine
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1203 · Exploitation for Client ExecutionA malicious page exploits a vulnerability in Sogou's outdated Chromium 80 engine to achieve code execution.T1204.001 · Malicious LinkThe attack begins when a victim clicks a crafted sgbiz: URI.T1620 · Reflective Code LoadingGrayRabbit can reflectively load plugins into the host's memory.
CVE
Threat Actors
Malware
Vendors
Gen DigitalGen Digital says the flaw enables one-click remote code execution, and Tencent has patched the issue in Sogou Input Method version 16.3.0.3498.TencentThreat actors linked to UNC3569 are exploiting CVE-2026-51990 in Tencent’s Sogou Input Method for Windows to deliver the GrayRabbit backdoor through a crafted link.
Products
ChromiumThe chain abuses command-line injection, unrestricted URL navigation, and an outdated Chromium engine.Tencent Sogou Input MethodThreat actors linked to UNC3569 are exploiting CVE-2026-51990 in Tencent’s Sogou Input Method for Windows to deliver the GrayRabbit backdoor through a crafted link.