
CISA Says Ransomware Gangs Are Exploiting WatchGuard Firebox RCE Flaw
Summary
CISA says ransomware gangs are exploiting CVE-2025-14733, an unauthenticated RCE flaw in WatchGuard Firebox firewalls. Multiple Fireware OS branches are affected, and nearly 9,000 unpatched devices reportedly remain exposed.
Key points
- CVE-2025-14733 is an out-of-bounds write flaw that can enable unauthenticated remote code execution.
- Affected systems include Fireware OS 11.x and later, 12.x and later, and versions 2025.1 through 2025.1.3.
- WatchGuard said exposure depends on configuration, including IKEv2 VPN, and some devices may remain at risk if a branch office VPN to a static gateway peer is configured.
- CISA says ransomware gangs are using the flaw but has not shared further details about the attacks.
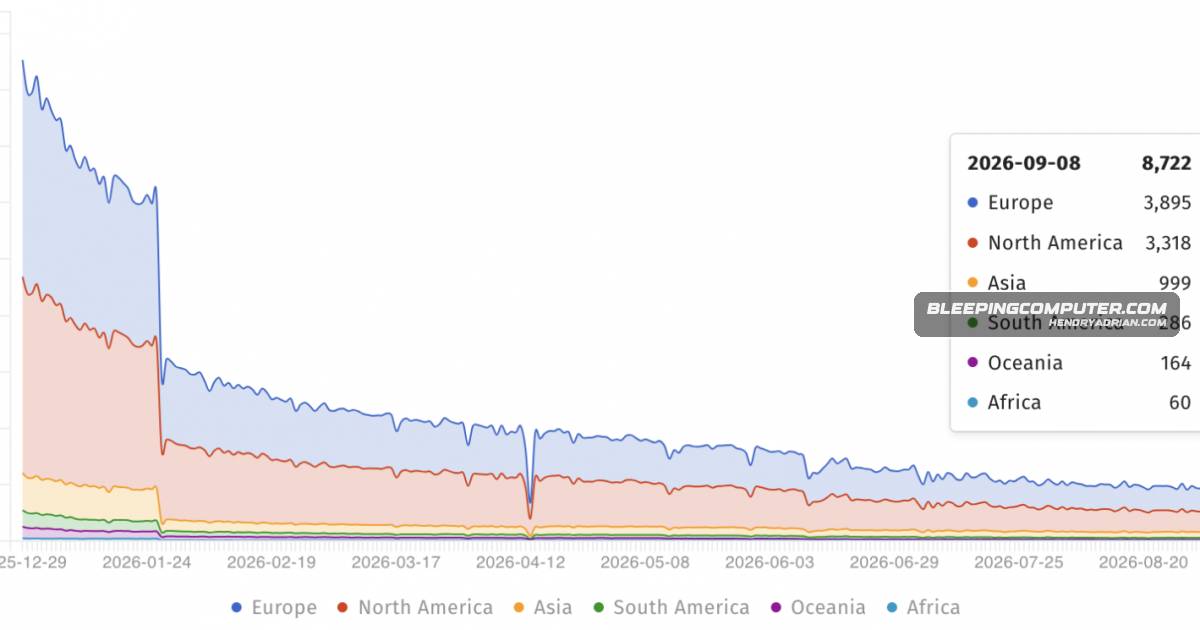
- Shadowserver reported nearly 9,000 unsecured Firebox instances remain exposed; WatchGuard previously shared indicators to help customers check for compromise.
Article Details
- Vulnerability Types
- Out-of-bounds write enabling unauthenticated remote code execution
- Severity
- Critical
- Affected Versions
- Fireware OS 11.x and later, including 11.12.4_Update1
- Fireware OS 12.x and later, including 12.11.5
- Fireware OS 2025.1 through 2025.1.3
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
CVE-2025-14733WatchGuard · Fireware OSCISA has confirmed that ransomware gangs are exploiting CVE-2025-14733, a critical WatchGuard Firebox firewall flaw that allows unauthenticated remote code execution through an out-of-bounds write.CVE-2025-9242WatchGuard · Fireware OSMore recently, in September 2025, WatchGuard patched an RCE vulnerability (CVE-2025-9242) affecting Firebox firewalls and almost identical to CVE-2025-14733.