Microsoft’s September Patch Tuesday Addresses 973 CVEs Across 39 Product Families
Summary
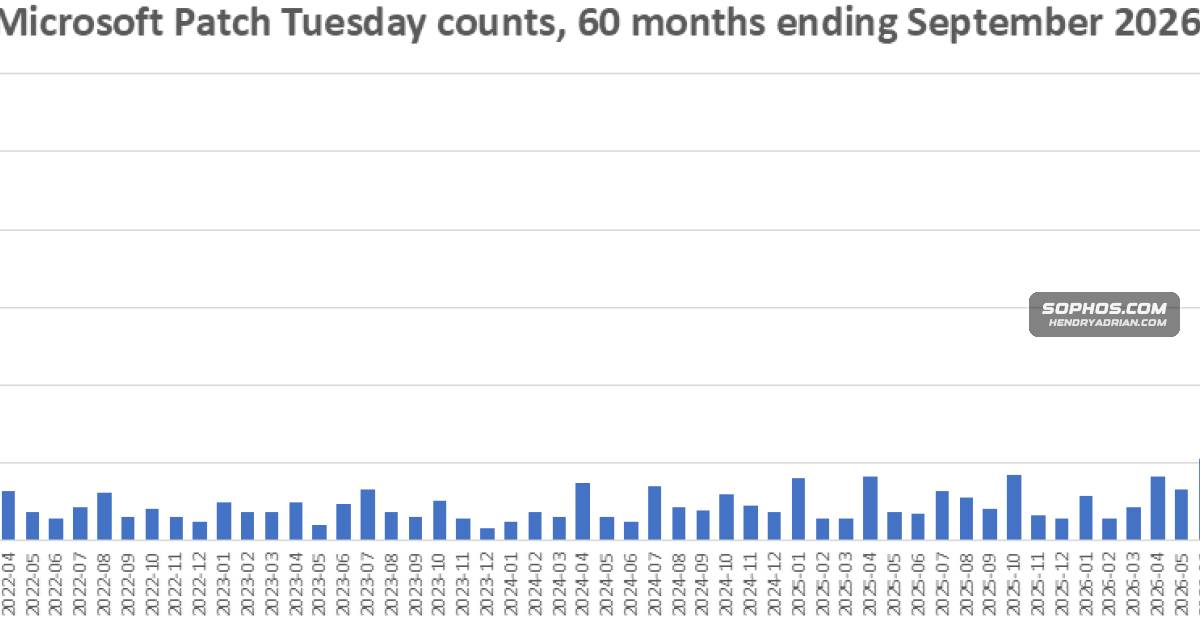
Microsoft released 973 September patches across 39 product families. Two Windows elevation-of-privilege flaws were actively exploited, and 82 Office for Mac fixes were still pending; an Exchange flaw was patched out of band on October 2.
Key points
- The September 9 release covered 973 CVEs across 39 product families, including 114 rated Critical and 284 with CVSS scores of 8.0 or higher.
- Two Windows elevation-of-privilege vulnerabilities, CVE-2026-81963 and CVE-2026-85880, had active exploits detected.
- Microsoft expected 58 vulnerabilities to be exploited within 30 days; none of the September issues had been publicly disclosed before the patches were released.
- Fixes for 82 Office for Mac vulnerabilities were not yet available at the September release, including two Critical issues rated CVSS 9.8.
- On October 2, Microsoft released an out-of-band patch for CVE-2026-96940, an Important-severity Exchange Server elevation-of-privilege flaw with a CVSS score of 8.8.
- Sophos listed protections for a number of the vulnerabilities and advised administrators that updates can also be downloaded manually from the Windows Update Catalog.
Article Details
- Vulnerability Types
- Elevation of Privilege
- Information Disclosure
- Remote Code Execution
- Denial of Service
- Security Feature Bypass
- Spoofing
- Tampering
- Weak Authentication
- Improper Validation of an Integrity Check Value
- Link Following
- Improper Access Control
- Heap-Based Buffer Overflow
- Use of an Uninitialized Resource
- Severity
- Of the 973 Microsoft CVEs in the September release, 114 were rated Critical, 857 Important, one Moderate, and one Low. The October 2 addition, CVE-2026-96940, was rated Important.
- Affected Versions
- Exchange Server Subscription Edition (SE)
- Exchange Server 2016 and Exchange Server 2019, through the Period 2 Extended Security Update program only
- SQLite v3.51.1
- Supported Windows client and server versions: either CVE-2026-81963 or CVE-2026-85880 applies to each version, but not both
- Office for Mac; specific affected versions were not stated
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- partial
CVE
CVE-2025-70873with the main release. The usual Servicing Stack update (ADV990001) was issued. MITRE sent word of CVE-2025-70873, an information disclosure issue affecting SQLite v3.51.1. The only eyebrow-raising advisory item, inCVE-2026-34182only eyebrow-raising advisory item, in fact, comes from the OpenSSL Software Foundation, warning of CVE-2026-34182 – an improper validation of an integrity-check value (CWE-354) concerning CMS (Cryptographic MessageCVE-2026-68846CVE-2026-68876CVE-2026-68884CVE-2026-69277CVE-2026-69301CVE-2026-69305CVE-2026-69310CVE-2026-69337CVE-2026-69364CVE-2026-69366CVE-2026-69385CVE-2026-69406CVE-2026-69436CVE-2026-69451CVE-2026-69460CVE-2026-69466CVE-2026-69473CVE-2026-69498CVE-2026-69541CVE-2026-69585CVE-2026-69600CVE-2026-69605CVE-2026-69623CVE-2026-69714CVE-2026-69723CVE-2026-69757CVE-2026-69779CVE-2026-69832CVE-2026-69911CVE-2026-69921CVE-2026-70289CVE-2026-70342CVE-2026-70583CVE-2026-71340CVE-2026-71343CVE-2026-77500CVE-2026-80093CVE-2026-81963CVE-2026-81963 -- Windows Update Stack Elevation of Privilege VulnerabilityCVE-2026-85880CVE-2026-85880 -- Windows Advanced Local Procedure Call (ALPC) Elevation of Privilege VulnerabilityCVE-2026-96940Update: On October 2, Microsoft released a patch for CVE-2026-96940, an Important-severity Elevation of Privilege issue affecting Exchange Server Subscription Edition (SE), Exchange Server 2016, and Exchange Server 2019
Vendors
Adobethe main event. The Chrome team released 24 Edge-related patches in the days before Patch Tuesday, while Adobe moved 21 patches affecting Acrobat with the main release. The usual Servicing Stack update (ADV990001) wasMicrosoftUpdate: On October 2, Microsoft released a patch for CVE-2026-96940, an Important-severity Elevation of Privilege issue affecting Exchange Server Subscription Edition (SE), Exchange Server 2016, and Exchange Server 2019OpenSSL Software Foundationaffecting SQLite v3.51.1. The only eyebrow-raising advisory item, in fact, comes from the OpenSSL Software Foundation, warning of CVE-2026-34182 – an improper validation of an integrity-check value (CWE-354)SophosVarious of this month’s issues are amenable to direct detection by Sophos protections, and we include information on those in the usual table below.
Products
AccessAccess: 4Acrobat24 Edge-related patches in the days before Patch Tuesday, while Adobe moved 21 patches affecting Acrobat with the main release. The usual Servicing Stack update (ADV990001) was issued. MITRE sent word ofAzureto September 9. All are Critical-severity and two carry a “perfect” 10.0 CVSS base score; these affect Azure, Copilot, Discovery Studio, Entra, Fabric, and Power Automate. We include these nine items in the usualAzure AIAzure AI: 1Azure Cosmos DBAzure Cosmos DB: 1Azure CycleCloudAzure CycleCloud: 1Copilot9. All are Critical-severity and two carry a “perfect” 10.0 CVSS base score; these affect Azure, Copilot, Discovery Studio, Entra, Fabric, and Power Automate. We include these nine items in the usual charts andCopilot StudioCopilot Studio: 1Discovery Studioare Critical-severity and two carry a “perfect” 10.0 CVSS base score; these affect Azure, Copilot, Discovery Studio, Entra, Fabric, and Power Automate. We include these nine items in the usual charts and statisticsDynamics 365Dynamics 365: 2Edgerelatively low advisory count poses an interesting contrast to the main event. The Chrome team released 24 Edge-related patches in the days before Patch Tuesday, while Adobe moved 21 patches affecting Acrobat with theEntraand two carry a “perfect” 10.0 CVSS base score; these affect Azure, Copilot, Discovery Studio, Entra, Fabric, and Power Automate. We include these nine items in the usual charts and statistics below, butExcelExcel: 30Exchange Server 2016Elevation of Privilege issue affecting Exchange Server Subscription Edition (SE), Exchange Server 2016, and Exchange Server 2019 (for the latter two, via the Period 2 Extended Security Update programExchange Server 2019of Privilege issue affecting Exchange Server Subscription Edition (SE), Exchange Server 2016, and Exchange Server 2019 (for the latter two, via the Period 2 Extended Security Update program only). This CVE was theExchange Server Subscription Edition (SE)patch for CVE-2026-96940, an Important-severity Elevation of Privilege issue affecting Exchange Server Subscription Edition (SE), Exchange Server 2016, and Exchange Server 2019 (for the latter two, via the Period 2Fabricand two carry a “perfect” 10.0 CVSS base score; these affect Azure, Copilot, Discovery Studio, Entra, Fabric, and Power Automate. We include these nine items in the usual charts and statistics below, but they’reGoogle Chromemonth in a row, the relatively low advisory count poses an interesting contrast to the main event. The Chrome team released 24 Edge-related patches in the days before Patch Tuesday, while Adobe moved 21 patchesHEVCHEVC: 2Microsoft SharePointSharePoint: 16Microsoft WindowsCritical severity; 58 CVEs are expected to be exploited within the next 30 days. (Two Important-severity Windows vulnerabilities already are; more on those below.) 284 have a CVSS Base score of 8.0 or higher. None ofOfficeIt can also happen if you are a user of a less common flavor of a product – Office for Mac, for instance. Over the years, the occasional Office patch has gone out on Patch Tuesday with a note telling the Mac crowd toOffice for MacIt can also happen if you are a user of a less common flavor of a product – Office for Mac, for instance. Over the years, the occasional Office patch has gone out on Patch Tuesday with a note telling the Mac crowd toOutlookthat Preview Pane is a vector. One more has no Mac patch yet, and also simply viewing the message in Outlook is a vector. That’s eighty-two CVEs for which, most likely, Microsoft simply ran out of runway.Power Automatea “perfect” 10.0 CVSS base score; these affect Azure, Copilot, Discovery Studio, Entra, Fabric, and Power Automate. We include these nine items in the usual charts and statistics below, but they’re fortunately notPower PlatformPower Platform: 1PowerPointPowerPoint: 6PowerShellPowerShell: 1PublisherPublisher: 2Remote DesktopRemote Desktop: 3SkypeSkype: 10Sophos Intercept XSophos XGS FirewallSQLite(ADV990001) was issued. MITRE sent word of CVE-2025-70873, an information disclosure issue affecting SQLite v3.51.1. The only eyebrow-raising advisory item, in fact, comes from the OpenSSL Software Foundation,VSVS: 21XboxXbox: 1