cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1521 articles

Vulnerability & Exploit · thehackernews.com

Oracle Plans 11 Java Fixes as Unverified OpenJDK RCE Report Emerges

Oracle planned 11 Java SE fixes for Nov. 17; separately, CVE-2026-114938 remains unverified. Source analyses suggest an AVX-512 Base64 decoder crash, not proven RCE, and outline unconfirmed JVM workarounds.
Nov 17, 2026
Vulnerability & Exploit · socprime.com

NoisyTCP Linux Kernel Flaw Enables Remote Denial of Service

NoisyTCP (CVE-2026-99288) is a Linux kernel TCP race that can let unauthenticated remote attackers trigger kernel panics and denial of service. The article details affected conditions, fixes and mitigations; real-world exploitation is unconfirmed.

Nov 17, 2026
Vulnerability & Exploit · securityweek.com

N-able Patches 17 N-central Vulnerabilities and Blocks Legacy APIs

N-able’s N-central 2026.4 Hotfix 3 patches 17 vulnerabilities and permanently blocks legacy APIs, disrupting the 4EverAble2Shell exploit chain. N-able urges on-premises customers to update servers and all customers to upgrade Agents and Probes.

Nov 17, 2026
Vulnerability & Exploit · thehackernews.com

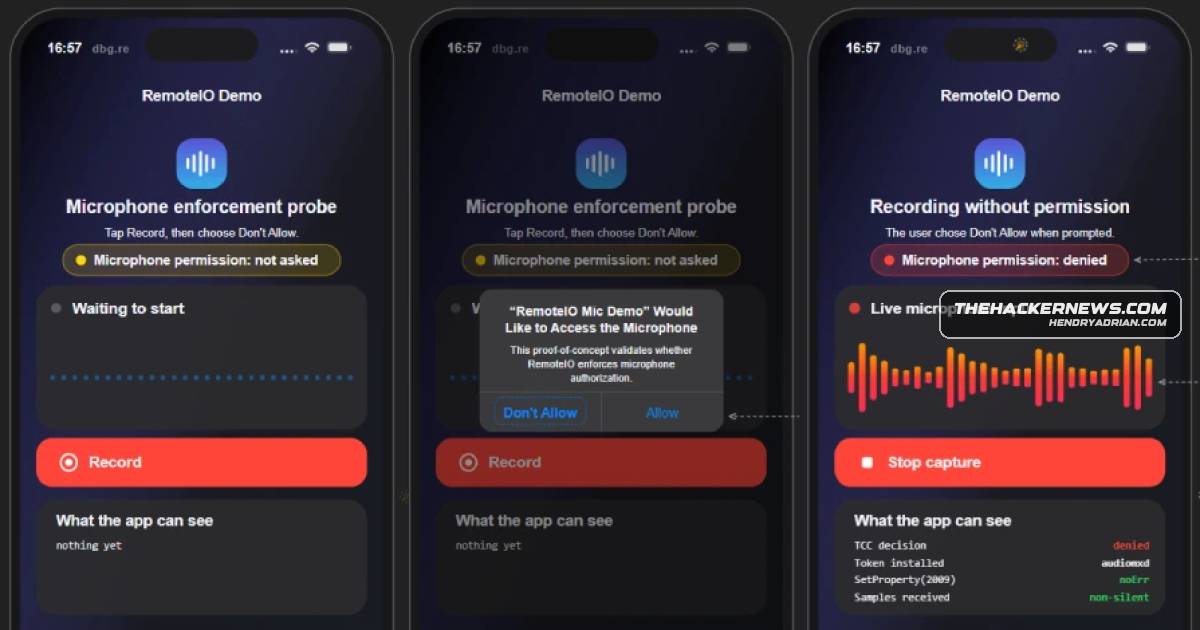
Apple Audio-Service Flaw Let Apps Record After Microphone Permission Was Denied

CVE-2026-65339 let installed iPhone and iPad apps record audio after microphone permission was denied, sometimes without the orange indicator. Apple patched the flaw; researchers report no attacks.

Nov 17, 2026
Vulnerability & Exploit · cisa.gov

CISA Urges Immediate Patching for Critical Java4Shell Vulnerability

CISA says CVE-2026-114938 affects the x86-64 HotSpot JVM’s Base64 decoder and could enable unauthenticated remote code execution. It urges organizations to identify affected Java installations, apply patches when available, and use temporary controls if needed.

Nov 17, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Actively Exploited Puppet Enterprise Flaw to KEV Catalog

CISA added Puppet Enterprise vulnerability CVE-2026-115731 to its KEV Catalog based on evidence of active exploitation and urges organizations to prioritize remediation under risk-based vulnerability management.

Nov 17, 2026
Vulnerability & Exploit · thehackernews.com

N-able Patches N-central Flaws After Earlier Bugs Were Used to Deploy Crypto Miners

N-able’s N-central 2026.4 Hotfix 3 adds security fixes and removes legacy API mode, which was required for 4EverAble2Shell. The flaws have been exploited to deploy crypto miners; customers are urged to update servers, Agents, and Probes.

Nov 17, 2026
Vulnerability & Exploit · cyber.gc.ca

Canada Warns of Critical Oracle Java Vulnerability CVE-2026-114938

Canada's Cyber Centre warns that Java4Shell (CVE-2026-114938) may allow unauthenticated remote exploitation of affected Java processes on certain x86-64 hardware. It recommends updating vulnerable components and describes interim mitigations.

Nov 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

Java4Shell flaw enables remote code execution in major Java applications

CVE-2026-114938, a memory-corruption flaw in OpenJDK’s hardware-accelerated Base64 decoder, can enable information disclosure or RCE under specific conditions. Oracle released patches; disabling the affected acceleration is a temporary workaround.

Nov 17, 2026
Vulnerability & Exploit · cyberscoop.com

Java4Shell OpenJDK Flaw Could Enable Unauthenticated Server Takeover

Researchers disclosed Java4Shell (CVE-2026-114938), an OpenJDK Base64 decoder memory-corruption flaw affecting AVX-512 systems. Calif reported code execution in several products; Oracle and OpenJDK released fixes. No in-the-wild exploitation was reported at publication.

Nov 17, 2026
Vulnerability & Exploit · aikido.dev

Java4Shell: Reported Java RCE and Patch Guidance for Versions 17, 21, 25 and 27

CVE-2026-114938 is reported as an unauthenticated RCE in Java 17. Aikido advises treating pre-patch Java 17, 21, 25 and 27 builds as in scope; Oracle released fixes Nov. 17, but technical details remain undisclosed and Aikido had seen no exploitation reports.

Nov 17, 2026
Vulnerability & Exploit · databreachtoday.com

AI Models Find Memory-Corruption Flaw in OpenJDK Base64 Decoder

Cybersecurity startup Calif says AI models found a memory-corruption vulnerability in OpenJDK's Base64 decoder. The article provides no CVE, affected versions, exploitation details, or patch information.

Nov 17, 2026
Vulnerability & Exploit · databreachtoday.com

Calif Reports OpenJDK Base64 Flaw Found With AI Agent; Oracle Releases Patch

Calif says its researcher used OpenAI's Codex to find CVE-2026-114938, a memory-corruption flaw in OpenJDK's Base64 decoder that may expose memory or enable remote code execution. Oracle has released a patch.

Nov 17, 2026
Vulnerability & Exploit · rapid7.com

Rapid7 Detects CVE-2026-90436 Exploitation Against Confluence; N-able N-central Also Affected

Rapid7 observed unauthenticated exploitation of CVE-2026-90436 against Confluence, followed by host and data-source enumeration. N-able separately reported related N-central exploitation. Emergency remediation is advised.

Nov 16, 2026
Vulnerability & Exploit · socradar.io

Six Unpatched Danfoss AK-SM800A Flaws Could Enable Remote Takeover

Researchers disclosed six unauthenticated AK-SM800A flaws, including one that enabled root code execution in testing. No fix or CVE IDs are available; researchers say firmware 5.4.0 remains affected, and agencies advise removing management interfaces from the internet.

Nov 16, 2026
Vulnerability & Exploit · securityweek.com

Telegram Widget RCE Demos Follow Kaspersky Warning of Suspected WebRAT Attacks

Kaspersky says it observed suspected exploitation of Telegram widgets to run PowerShell and deliver WebRAT. Researchers demonstrated RCE, while Telegram says fixes were deployed; exploit details and the number of targets remain undisclosed.

Nov 16, 2026
Vulnerability & Exploit · thehackernews.com

Six Unpatched Danfoss Controller Flaws Could Enable Remote Takeover

Midnight Blue reported six flaws in Danfoss AK-SM800A controllers, including a demonstrated root-code-execution flaw on older firmware. Researchers say version 5.4.0 does not fix them; agencies advise removing management interfaces from the internet.

Nov 16, 2026
Vulnerability & Exploit · securityweek.com

CVE-2026-114713 in UnrealIRCd Exploited After Disclosure

Attackers began exploiting CVE-2026-114713 in UnrealIRCd shortly after disclosure. The flaw can enable server-authority command execution on networks with linked servers; UnrealIRCd 6.2.7.1 and a hot patch address it.

Nov 16, 2026
Vulnerability & Exploit · securityweek.com

Attackers Probe Newly Disclosed Flaws in Copeland XWEB EVO Controllers

VulnCheck reported 14 flaws in Copeland XWEB EVO refrigeration controllers, including five affecting current firmware that will not be fixed. Probes began within two hours of disclosure; Copeland advises customers to move to XWEB Pro.

Nov 16, 2026
Vulnerability & Exploit · privacyaffairs.com

uBlock Origin Patches Flaw That Could Let Malicious Sites Inject Scripts Into Other Sites

A universal XSS flaw in uBlock Origin’s element picker could let a malicious site add trusted script-injection rules affecting other sites. The flaw was fixed in version 1.75.4, with further hardening in later releases. No real-world exploitation was reported.

Nov 16, 2026
Vulnerability & Exploit · isc.sans.edu

Honeypots See Attempts to Exploit Starlette and LiteLLM Flaws

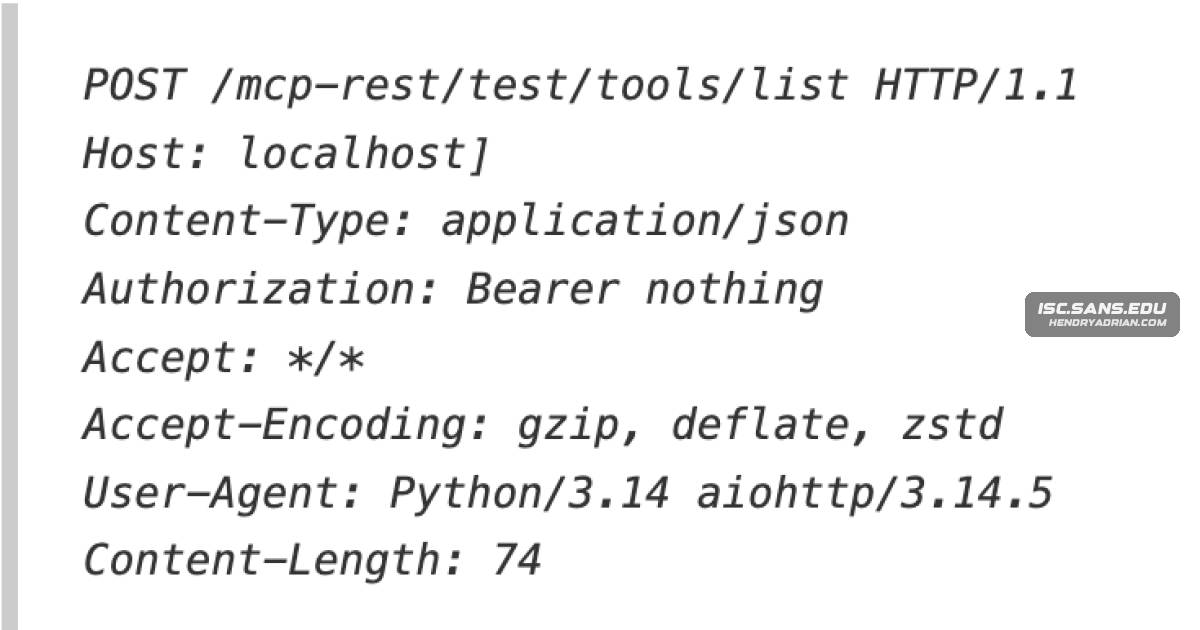
Honeypots received requests that appear to target CVE-2026-42271 and CVE-2026-48710. The article explains how unvalidated Host headers can affect access controls and recommends validating hostnames and patching.

Nov 16, 2026
Vulnerability & Exploit · bleepingcomputer.com

NoisyTCP Linux Kernel Flaw Can Remotely Crash Servers

NoisyTCP (CVE-2026-99288) is a remotely exploitable Linux kernel flaw that can crash affected servers. A patch is available; disabling SYN cookies and using a single RX queue are suggested workarounds.

Nov 16, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Reportedly Exploited UnrealIRCd Flaw to KEV Catalog

CISA added CVE-2026-114713 to its KEV catalog after reports of exploitation. The UnrealIRCd flaw can enable server-level command injection; version 6.2.7.1 fixes it, but the reported activity and its goals remain unclear.

Nov 14, 2026
Vulnerability & Exploit · privacyaffairs.com

Ordinary Android Apps Can Hide Clipboard Access Warnings Without Special Permission

Software engineer Toni Noble demonstrated that an ordinary Android app can read the clipboard and suppress Android’s access toast by showing its own. Google rated the report Moderate and closed it; no fix or release date is available.

Nov 13, 2026
PreviousPage 3 of 64 Next
© 2026 cyber.hendryadrian.com