cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1523 articles

Vulnerability & Exploit · thehackernews.com

CISA Adds Reportedly Exploited UnrealIRCd Flaw to KEV Catalog

CISA added CVE-2026-114713 to its KEV catalog after reports of exploitation. The UnrealIRCd flaw can enable server-level command injection; version 6.2.7.1 fixes it, but the reported activity and its goals remain unclear.
Nov 14, 2026
Vulnerability & Exploit · privacyaffairs.com

Ordinary Android Apps Can Hide Clipboard Access Warnings Without Special Permission

Software engineer Toni Noble demonstrated that an ordinary Android app can read the clipboard and suppress Android’s access toast by showing its own. Google rated the report Moderate and closed it; no fix or release date is available.

Nov 13, 2026
Vulnerability & Exploit · thehackernews.com

PostgreSQL Fixes 52 Flaws, Including Type-Confusion Bug That Can Enable Code Execution

PostgreSQL fixed 52 flaws, including CVE-2026-6460, a type-confusion bug that can let a user able to create objects run code as the PostgreSQL OS user. Exploitation has not been reported; affected versions require updates and extension rebuilds.

Nov 13, 2026
Vulnerability & Exploit · thehackernews.com

Mior and Skyfall Attacks Can Read Data From AMD SEV-SNP VMs

Researchers demonstrated Mior and Skyfall attacks that can expose data from AMD SEV-SNP VMs under different host-control conditions. AMD assigned CVEs and firmware fixes; neither advisory says the flaws have been used in attacks.

Nov 13, 2026
Vulnerability & Exploit · socradar.io

Apache Fixes Critical HTTP/2 Race Condition That Could Enable Remote Code Execution

Apache HTTP Server 2.4.71 fixes CVE-2026-119618, a critical mod_http2 race condition that could enable RCE. Exploit evidence remains mixed; the article reports no observed in-the-wild activity and recommends patching or disabling HTTP/2 until fixed.

Nov 13, 2026
Vulnerability & Exploit · socradar.io

4EverAble2Shell Exploited on 21 N-central Servers, Report Says

4EverAble2Shell reportedly gives unauthenticated root access to internet-exposed N-able N-central servers with the Legacy API enabled. Huntback telemetry identified 21 servers mining Monero; no fix is available, and N-able advises disabling the API.

Nov 13, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Two Actively Exploited Vulnerabilities to KEV Catalog

CISA added UnrealIRCd CVE-2026-114713 and Check Point CVE-2026-123039 to its KEV Catalog based on evidence of active exploitation. It urges organizations to prioritize remediation using risk-based vulnerability management.

Nov 13, 2026
Vulnerability & Exploit · securityweek.com

Citrix Patches 28 NetScaler Flaws, Including Critical Console Bug

Citrix patched 28 NetScaler ADC and Gateway vulnerabilities, including nine critical flaws, and a critical NetScaler Console access-control bypass. The article does not mention in-the-wild exploitation.

Nov 13, 2026
Vulnerability & Exploit · securityweek.com

SignDrop Windows Zero-Day Exploit Enables Local System Privilege Escalation

Researcher Abdelhamid Naceri says SignDrop abuses Windows CLFS logic to let a local user create a signature file with System privileges and spawn a System shell. Cyderes tested the PoC; it found no evidence of in-the-wild exploitation.

Nov 13, 2026
Vulnerability & Exploit · securityweek.com

Attackers Exploit N-able N-central Zero-Day Hours After PoC Release

Attackers reportedly exploited N-able N-central’s 4EverAble2Shell chain within hours of its PoC release, gaining root access on some servers and deploying XMRig. N-able restricted Legacy API and other features while investigating.

Nov 13, 2026
Vulnerability & Exploit · thehackernews.com

Reports Tie N-central Flaw Exploitation to XMRig on 21 Servers

N-able is restricting some N-central features amid disclosures of 4EverAble2Shell and Agent2Shell. Huntback reports XMRig was deployed on 21 N-central servers, including 19 already running Hotfix 2.

Nov 13, 2026
Vulnerability & Exploit · sysdig.com

Apache HTTP Server CVE-2026-119618: Heap Corruption Demonstrated, RCE Not Yet Publicly Shown

CVE-2026-119618 affects Apache httpd 2.4.55–2.4.70 when HTTP/2 is enabled. A public PoC demonstrates heap corruption and crashes, but not RCE; upgrade to 2.4.71 or temporarily disable HTTP/2.

Nov 13, 2026
Vulnerability & Exploit · fieldeffect.com

SAP patches four critical flaws enabling unauthenticated code execution and account access

SAP patched four CVSS 10.0 flaws affecting NetWeaver, Web Dispatcher and Gateway. The vulnerabilities can enable unauthenticated command execution or access as any SAP user; no exploitation or scanning was publicly reported as of November 11, 2026.

Nov 13, 2026
Vulnerability & Exploit · cyberscoop.com

Researchers Disclose 14 Vulnerabilities in Copeland-Dixell Refrigeration Systems

VulnCheck disclosed 14 vulnerabilities in Copeland-Dixell XWEB EVO systems; lab testing found they could enable root or administrative access, and at least two are reportedly actively exploited. Patches are available, but legacy versions remain exposed.

Nov 13, 2026
Vulnerability & Exploit · aikido.dev

Critical Apache HTTP Server Flaw Enables Unauthenticated Remote Code Execution

CVE-2026-119618 is a race condition in Apache HTTP Server’s HTTP/2 module that can enable unauthenticated remote code execution. Versions 2.4.55–2.4.70 are affected; upgrade to 2.4.71 or disable HTTP/2 temporarily.

Nov 13, 2026
Vulnerability & Exploit · cyfirma.com

CYFIRMA Exploit Radar Highlights Five Vulnerabilities and Mitigations

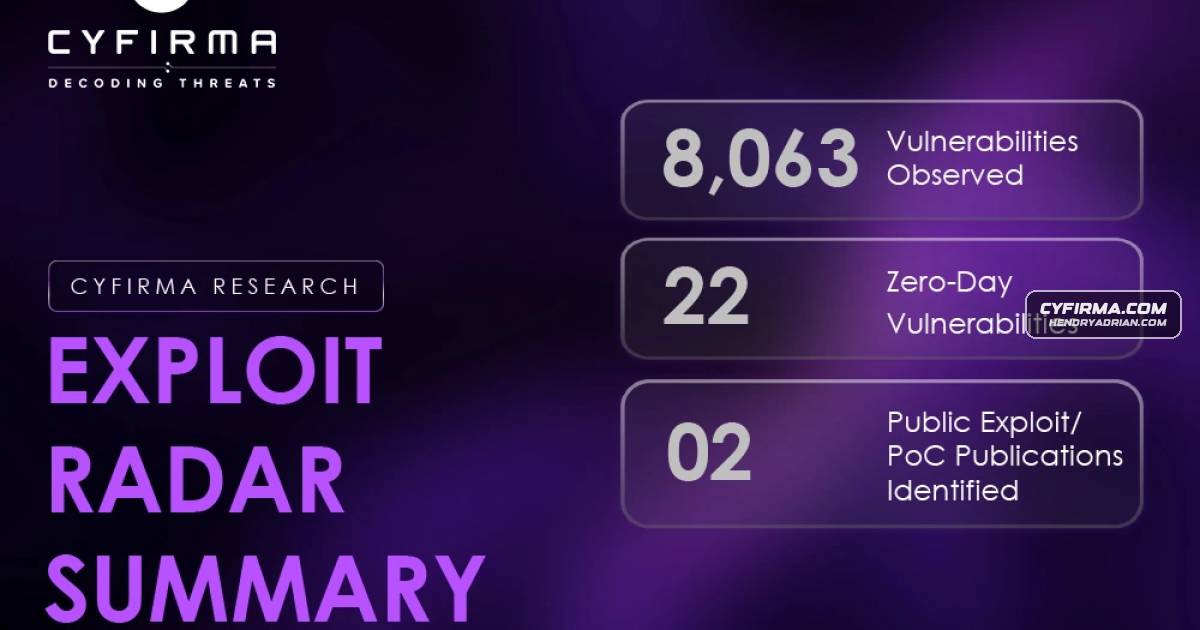
CYFIRMA’s fortnightly summary reports a 23.29% rise in observed vulnerabilities and details five CVEs affecting TOTOLINK, Portabase, blueprintUE, NextScan and Fider, with affected versions, risks and recommended fixes.

Nov 13, 2026
Vulnerability & Exploit · bleepingcomputer.com

Check Point patches zero-day reportedly exploited to gain root access

Check Point released emergency hotfixes for CVE-2026-123039, a Gaia OS privilege-escalation flaw. The company says attackers exploited it on about two dozen customers’ devices and advises stopping dynamic_server if hotfixes cannot be applied.

Nov 13, 2026
Vulnerability & Exploit · thehackernews.com

SignDrop PoC Claims Windows CLFS Flaw Can Grant SYSTEM Access

A public SignDrop proof of concept claims a local Windows user can exploit CLFS companion-file creation to gain SYSTEM access. Microsoft has not confirmed the flaw or issued a CVE or patch; a separate assessment found the exploit works but is unreliable.

Nov 12, 2026
Vulnerability & Exploit · thehackernews.com

Two Critical Red Hat Quay Flaws Could Expose Private Images and Robot Tokens

Two critical Red Hat Quay flaws can expose private images and secrets, allow image tampering, or steal other tenants’ robot tokens. Red Hat lists affected versions and fixes, with token rotation and access restrictions suggested as interim steps.

Nov 12, 2026
Vulnerability & Exploit · securityweek.com

Apache Patches Critical HTTP/2 Remote Code Execution Flaw

Apache fixed CVE-2026-119618 in HTTP Server 2.4.71. The race condition affects versions 2.4.55–2.4.70 with HTTP/2 enabled; Red Hat says reliable exploitation has been demonstrated, but no in-the-wild exploitation was reported as of November 11.

Nov 12, 2026
Vulnerability & Exploit · thehackernews.com

Citrix Patches NetScaler Flaws That Could Enable DoS and Authentication Bypass

Citrix patched vulnerabilities affecting NetScaler ADC, NetScaler Gateway, NetScaler Console, and Secure Access Client. The flaws could cause denial of service or authentication bypass; Citrix said it was unaware of exploits.

Nov 12, 2026
Vulnerability & Exploit · socprime.com

Apache Fixes Critical HTTP/2 Race Condition Enabling Unauthenticated RCE

Apache fixed CVE-2026-119618, a critical mod_http2 race condition affecting versions 2.4.55–2.4.70 when HTTP/2 is enabled. Upgrade to 2.4.71 or vendor-fixed packages; no in-the-wild exploitation was reported as of Nov. 12, 2026.

Nov 12, 2026
Vulnerability & Exploit · thehackernews.com

Google Details Three AMD Turin CPU Flaws and Required VM Updates

Google says three AMD Zen 5/Turin transient-scheduler flaws could expose data within a VM. Google Cloud customers need a guest OS fix and VM stop/start; no exploitation is reported, and bare-metal systems need firmware and OS updates.

Nov 12, 2026
Vulnerability & Exploit · thehackernews.com

Researchers Report N-central Exploits That Bypass Patch for Root and SYSTEM Access

Researcher Sean Bales says two N-central exploits work against a patched build. N-able is investigating and advises disabling the internet-exposed Legacy API. Probing has been observed, but no successful exploitation is confirmed.

Nov 12, 2026
PreviousPage 4 of 64 Next
© 2026 cyber.hendryadrian.com