cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1521 articles

Vulnerability & Exploit · malwarebytes.com

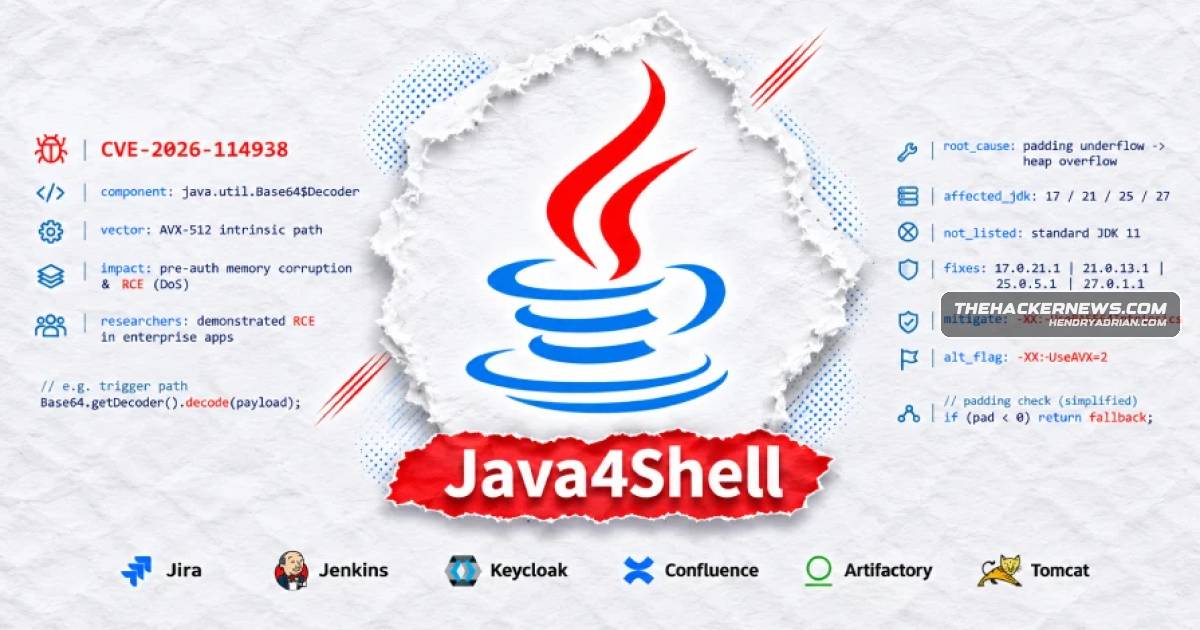
Java4Shell flaw can enable remote code execution under narrow conditions

CVE-2026-114938 affects OpenJDK’s x86-64 Base64 decoder and can enable application-specific remote code execution when several conditions align. Oracle and OpenJDK released fixes; no in-the-wild abuse was reported.
Nov 18, 2026
Vulnerability & Exploit · socprime.com

Researchers Demonstrate Pre-Authentication RCE in Major Java Applications via Java4Shell

CVE-2026-114938 (Java4Shell) is an OpenJDK Base64-decoder heap out-of-bounds write on x86-64 CPUs with AVX-512 VBMI. Researchers demonstrated application-specific RCE; patches are rolling out, and active exploitation is unconfirmed.

Nov 18, 2026
Vulnerability & Exploit · securityweek.com

Critical Perforce Puppet RCE Vulnerability Exploited in Attacks

CVE-2026-115731, a critical Puppet deserialization flaw enabling remote code execution, is being exploited. Patches are available, and administrators are advised to disable CA auto-signing and enforce strong certificate validation.

Nov 18, 2026
Vulnerability & Exploit · socradar.io

Researchers Report Java4Shell RCE in OpenJDK Base64 Decoder; Patches Available

Researchers report CVE-2026-114938, an OpenJDK Base64 decoder heap overflow affecting specified Java builds on x86-64 AVX-512 VBMI systems. Fixes are available; no in-the-wild exploitation was confirmed as of Nov. 18, 2026.

Nov 18, 2026
Vulnerability & Exploit · thehackernews.com

CISA Urges Immediate Patching of Java4Shell Flaw

CISA urged organizations to patch Java4Shell (CVE-2026-114938), an OpenJDK/Oracle Java flaw that may enable denial of service or remote code execution under specific conditions. No in-the-wild exploitation is known; temporary mitigations are available.

Nov 18, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Exploited Puppet RCE Flaw to KEV Catalog

CISA added CVE-2026-115731, a critical Puppet deserialization flaw that can enable remote code execution, to its KEV catalog, citing active-exploitation reports. Patches were released; the article gives no affected-version details.

Nov 18, 2026
Vulnerability & Exploit · securityweek.com

Java4Shell Flaw Risks Memory Disclosure and RCE in Enterprise Apps

Oracle released fixes for CVE-2026-114938, a Java Base64 memory-safety flaw affecting x86-64 systems with AVX-512 VBMI. Researchers demonstrated app-specific RCE; Talos said it had not seen in-the-wild exploitation.

Nov 18, 2026
Vulnerability & Exploit · thehackernews.com

Researchers Say Java4Shell Can Enable Unauthenticated RCE in Jira, Jenkins and More

CVE-2026-114938 affects Java’s AVX-512 Base64 decoder and may enable unauthenticated code execution in several applications, researchers say. Oracle, OpenJDK and other vendors released fixes; Red Hat updates were pending.

Nov 18, 2026
Vulnerability & Exploit · kudelskisecurity.com

nginx2root: Five Nginx RCE Flaws Can Chain With an Unpatched Kernel Bug for Host Root

Xint disclosed five configuration-dependent unauthenticated nginx RCE flaws and a separate unpatched Linux kernel SCTP privilege-escalation bug that can chain to host root and Docker escape. No in-the-wild exploitation is reported; nginx fixes are available, but the.

Nov 18, 2026
Vulnerability & Exploit · zscaler.com

Researchers Demonstrate Pre-Authentication RCE via OpenJDK Java4Shell Flaw

Calif.io disclosed Java4Shell (CVE-2026-114938), an OpenJDK AVX-512 Base64-decoder heap-corruption flaw, and reported RCE demonstrations across Java applications. The advisory recommends patching or temporarily disabling Base64 intrinsics.

Nov 18, 2026
Vulnerability & Exploit · darkreading.com

Critical RCE Flaws Found in Five Brazilian Digital-Signing Extensions

Researchers found critical RCE vulnerabilities in five Brazilian digital-signing extensions with more than 10 million installs. Attacker-controlled sites could exploit unsafe DLL loading; all five flaws were patched by mid-September.

Nov 18, 2026
Vulnerability & Exploit · darkreading.com

Java4Shell OpenJDK Flaw Enables Remote Code Execution

Researchers say Java4Shell, a memory-corruption flaw in OpenJDK’s optimized Base64 decoder, can enable memory disclosure or RCE. CVE-2026-114938 affects specified Java builds; Oracle issued a patch, and JVM flags are offered as mitigations.

Nov 18, 2026
Vulnerability & Exploit · fieldeffect.com

Java4Shell HotSpot Flaw Causes Heap Corruption; Researchers Demonstrate RCE

CVE-2026-114938 (“Java4Shell”) is an integer-underflow flaw in x86-64 HotSpot’s Base64 decoder. Researchers demonstrated RCE under specific Java, CPU and input conditions; public exploitation is unconfirmed. Fixed Java releases are available.

Nov 18, 2026
Vulnerability & Exploit · fieldeffect.com

Researchers Report Apache Axis 1.x RCE Exploitation Targeting Confluence and N-central

Researchers reported active exploitation of unauthenticated RCE CVE-2026-90436 in end-of-life Apache Axis 1.x, including Confluence and N-central deployments. The article outlines exposure, upgrades, mitigations, and compromise checks.

Nov 18, 2026
Vulnerability & Exploit · databreachtoday.com

Nginx Memory Corruption Flaws Could Enable Unauthenticated Remote Code Execution

Researchers disclosed Nginx memory corruption flaws that could enable unauthenticated remote code execution. A Rapid7 proof of concept demonstrated one flaw’s potential, with practical limits; F5 has issued fixes for two detailed CVEs.

Nov 18, 2026
Vulnerability & Exploit · aikido.dev

nginx2root: Five nginx Flaws Can Be Chained with a Linux SCTP Bug for Root Access

The nginx2root disclosure covers five nginx flaws affecting HTTP/2, HTTP/3, resolver and mail-proxy configurations. Chained with a Linux SCTP use-after-free, a flaw can enable host root access; fixes and configuration-specific mitigations are provided.

Nov 18, 2026
Vulnerability & Exploit · security.com

Java4Shell OpenJDK Flaw Enables Unauthenticated Remote Code Execution

CVE-2026-114938, dubbed Java4Shell, is a heap overflow in OpenJDK’s Base64 decoder that can enable unauthenticated RCE on affected AVX-512 VBMI systems. Patches are available; no in-the-wild exploitation was reported as of Nov. 18, 2026.

Nov 18, 2026
Vulnerability & Exploit · aikido.dev

PHP Plans Critical Security Releases for Nov. 19, Including CVE-2026-115560

PHP plans security releases for all supported versions on Nov. 19. CVE-2026-115560 affects specific session-handler configurations; PHP recommends disabling session upload progress as a mitigation until fixes are released.

Nov 18, 2026
Vulnerability & Exploit · cyberscoop.com

Researchers disclose five exploitable NGINX flaws; F5 releases fixes

Researchers disclosed five NGINX vulnerabilities with working exploits. The critical HTTP/2 flaw can enable unauthenticated remote code execution; F5 released fixes, and researchers demonstrated chaining it with a Linux kernel flaw to gain root.

Nov 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

Apache Roller RCE Flaw Actively Exploited; Users Urged to Patch

Apache says attackers are exploiting CVE-2026-129448, an unauthenticated deserialization flaw in Apache Roller 4.0.0–6.1.4. Upgrade to 6.1.6 or later; admins can apply temporary XML-RPC mitigations.

Nov 18, 2026
Vulnerability & Exploit · blog.qualys.com

Java4Shell Flaw Puts Unpatched OpenJDK Systems at Risk of Remote Code Execution

Java4Shell (CVE-2026-114938) affects unpatched OpenJDK-based runtimes on x86-64 systems with AVX-512 VBMI; researchers demonstrated pre-authentication RCE in several products. Oracle issued fixes, and Qualys outlines workarounds and remediation priorities.

Nov 17, 2026
Vulnerability & Exploit · wiz.io

OpenJDK CVE-2026-114938 Enables Remote Code Execution on AVX-512 Systems

CVE-2026-114938 affects OpenJDK’s AVX-512 Base64 decoder, where malformed padding can cause a heap out-of-bounds write. Wiz reports remote exploitability; affected systems should be patched or use recommended JVM workarounds.

Nov 17, 2026
Vulnerability & Exploit · thehackernews.com

Researchers Say Two Telegram Android Widget Exploits Bypass New Defenses

NebuSec says two Telegram Android widget bugs can bypass a new QuickJS process filter; the published 13.2.2 source uses seccomp audit mode for some calls. Exploit scope and installed-version impact are unclear; Kaspersky separately reported suspected widget exploitation

Nov 17, 2026
Vulnerability & Exploit · rapid7.com

Java Base64 Decoder Flaw Could Enable Unauthenticated Remote Code Execution

CVE-2026-114938 is a heap-based overflow in OpenJDK’s hardware-accelerated Base64 decoder. Under specific x86-64 and JVM conditions, malformed input can corrupt memory and potentially enable RCE; vendors have released patches and a temporary mitigation.

Nov 17, 2026
PreviousPage 2 of 64 Next
© 2026 cyber.hendryadrian.com