
Apple Audio-Service Flaw Let Apps Record After Microphone Permission Was Denied
Summary
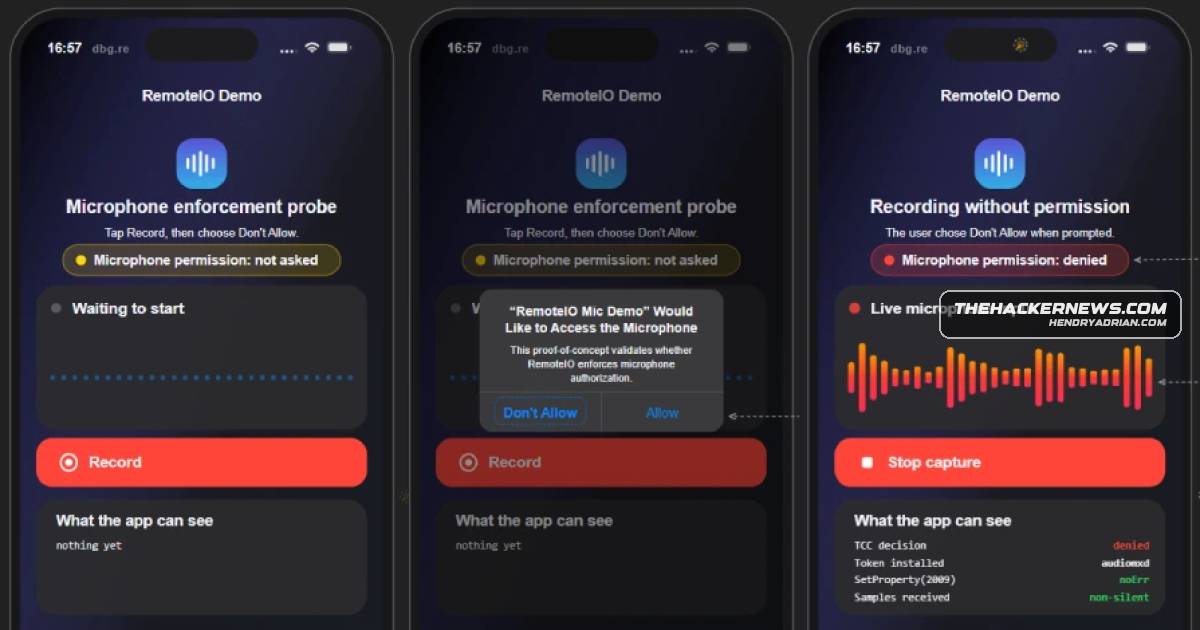
CVE-2026-65339 let installed iPhone and iPad apps record audio after microphone permission was denied, sometimes without the orange indicator. Apple patched the flaw; researchers report no attacks.
Key points
- The flaw let apps bypass microphone permission checks by supplying audiomxd with an audit token identifying the audio service itself.
- Researchers reproduced the bypass on iOS 26.6 and an iPadOS 27 beta; tests also covered iOS 27 builds.
- Recording had to start while the app was in the foreground, but could continue after the app went to the background or the device was locked.
- The orange microphone indicator was absent in some tests; one later test build appeared to restore it.
- Apple's fix makes the service verify the real caller's identity. External callers need a private entitlement to override that identity.
- The flaw was patched in Apple's August 17 security updates; Meta's timeline says the fix had shipped in iOS 27.0 beta 5 on August 10.
- Neither Apple nor the researchers reported attacks exploiting the flaw.
Article Details
- Vulnerability Types
- Microphone permission bypass
- Process identity spoofing through a forged audit token
- Severity
- CVSS 5.0 out of 10
- Affected Versions
- iOS 26.6
- iPadOS 27 beta
- iOS 27 test builds
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Install the updates that fix the flaw.
MITRE ATT&CK
CVE
People
Vendors
Products
iOSNeither researcher describes a way for users to check whether an app recorded them before the fix. Calap reproduced the bypass on iOS 26.6, released July 27, and on an iPadOS 27 beta.iPadOSNeither researcher describes a way for users to check whether an app recorded them before the fix. Calap reproduced the bypass on iOS 26.6, released July 27, and on an iPadOS 27 beta.