
Honeypots See Attempts to Exploit Starlette and LiteLLM Flaws
Summary
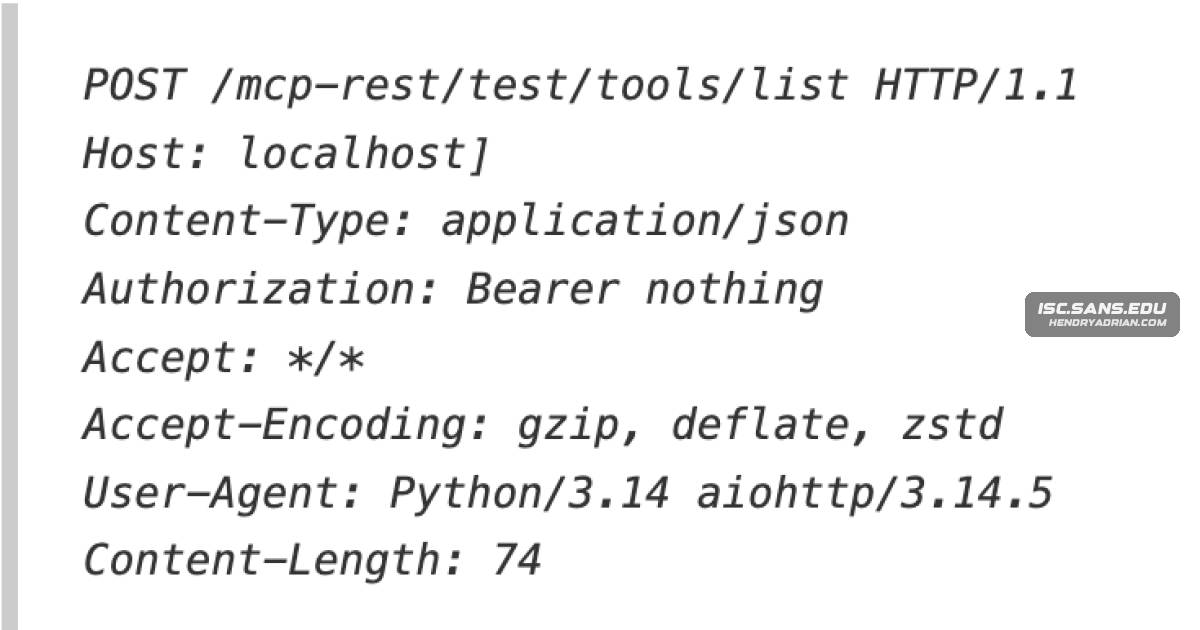
Honeypots received requests that appear to target CVE-2026-42271 and CVE-2026-48710. The article explains how unvalidated Host headers can affect access controls and recommends validating hostnames and patching.
Key points
- Honeypots observed requests to LiteLLM’s /mcp-rest/test/tools/list endpoint that appear to attempt exploitation; the article does not report successful compromise.
- Starlette versions before 1.0.1 do not validate the Host header, according to the article.
- An attacker can use unusual Host-header characters to influence URL construction and confuse access-control checks.
- The vulnerabilities can reportedly be chained for unauthenticated remote code execution, according to a linked write-up.
- Recommended defenses include patching, validating hostnames before building URLs, and allowing only specific hostnames in filters.
Article Details
- Vulnerability Types
- Unvalidated Host header enabling access-control bypass
- Unauthenticated remote code execution through a vulnerability chain
- Affected Versions
- Starlette versions prior to 1.0.1
- Exploitation Status
- reported
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Configure WAF rules or filters to allow only specific hostnames.
MITRE ATT&CK
CVE
CVE-2026-42271BerriAI · litellm; Red Hat · Red Hat OpenShift AI 2.25; +2 moreThese requests appear to attempt to exploit CVE-2026-42271 and CVE-2026-48710.CVE-2026-48710Kludex · starlette; Red Hat · Exploit Intelligence; +13 moreThese requests appear to attempt to exploit CVE-2026-42271 and CVE-2026-48710.