cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1521 articles

Vulnerability & Exploit · securityweek.com

PHP Patches Seven Critical RCE Vulnerabilities

PHP patched seven critical-severity flaws with potential RCE impact, including a PHP-FPM request-smuggling issue. PHP 8.6.0 and 8.5.13 fix all seven; most fixes are also available for earlier supported releases.
Nov 19, 2026
Vulnerability & Exploit · thehackernews.com

Critical VMware vCenter Authentication Bypass Rated CVSS 9.8

Broadcom says CVE-2026-123890, a CVSS 9.8 authentication bypass in VMware vCenter's Directory Service, affects supported releases and some unsupported versions. Patches are available; no workaround or exploitation has been reported.

Nov 19, 2026
Vulnerability & Exploit · thehackernews.com

Drupal Fixes Critical Installer Flaw That Could Enable Unauthenticated Site Takeover

Drupal patched CVE-2026-132165, a critical installer flaw that could enable site takeover or remote code execution under uncommon conditions. The advisory reports no attacks, but notes an existing proof of concept and recommends blocking the installer.

Nov 19, 2026
Vulnerability & Exploit · securityweek.com

Apache Axis and Roller Vulnerabilities Exploited in Attacks

CVE-2026-90436 in Apache Axis 1.x and CVE-2026-129448 in Apache Roller are being exploited. CISA added the Axis flaw to KEV; guidance includes migrating or patching Axis and upgrading Roller to 6.1.6 or later.

Nov 19, 2026
Vulnerability & Exploit · securityweek.com

Splunk Patches Nearly 140 Vulnerabilities in Enterprise, Enterprise Security and SOAR

Splunk patched nearly 140 vulnerabilities across Enterprise, Enterprise Security and SOAR, including critical flaws that could enable code execution or data and configuration access. The company did not say the flaws were exploited in the wild.

Nov 19, 2026
Vulnerability & Exploit · securityweek.com

F5 Patches Five Critical NGINX2Root Flaws as PoCs Go Public

F5 patched five critical NGINX2Root flaws that could enable unauthenticated RCE. PoCs are public, with exploitation constraints noted; F5 says the fixes cover specified NGINX versions. No in-the-wild exploitation was reported.

Nov 19, 2026
Vulnerability & Exploit · guardsix.com

Java4Shell OpenJDK Heap Overflow Can Enable Pre-Auth RCE in Java Products

Java4Shell (CVE-2026-114938) is an AVX-512 VBMI-dependent OpenJDK Base64 heap overflow. Fixes are available and exploitation attempts have been observed; a reported Confluence compromise remains unconfirmed. The article details mitigations and detection.

Nov 19, 2026
Vulnerability & Exploit · securityweek.com

Java4Shell Exploitation Attempts Emerge as Vendors Issue Advisories

CVE-2026-114938 affects certain OpenJDK builds on x86-64 CPUs with AVX-512 VBMI. Vendors report varying product impacts and are issuing fixes; observed probing has not established successful compromises.

Nov 19, 2026
Vulnerability & Exploit · thehackernews.com

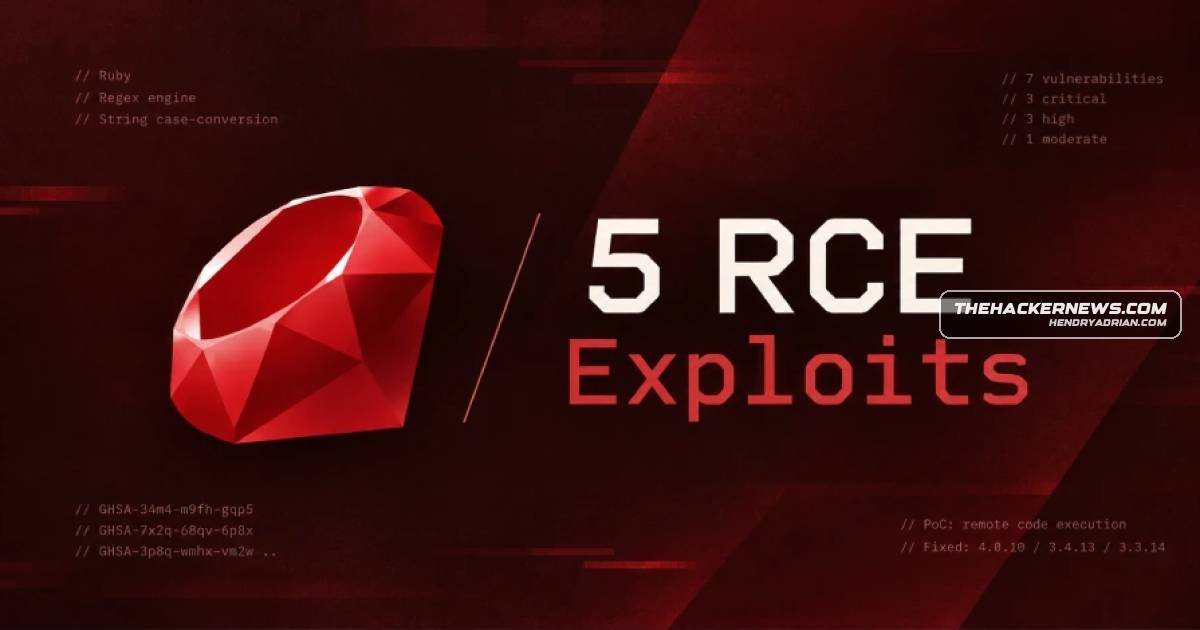
Ruby Fixes Seven Regex and String Flaws; Five Have PoC RCE

Ruby fixed seven memory-safety flaws in its regex engine and string case-conversion code. Maintainers say PoCs demonstrate remote code execution for five; no attacks have been reported. Fixed releases are Ruby 4.0.10, 3.4.13 and 3.3.14.

Nov 19, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Four Actively Exploited Vulnerabilities to KEV Catalog

CISA added four flaws affecting REDCap, Apache Axis, LiteLLM and Synology DSM to its KEV catalog. Reports link them to cryptomining, LLMjacking and C3RB3R ransomware; federal agencies face remediation deadlines in November and December 2026.

Nov 19, 2026
Vulnerability & Exploit · securityweek.com

PHP Readies Critical Updates for File-Upload Progress RCE Flaw

PHP plans critical security updates for November 19, including a fix for CVE-2026-115560, an RCE flaw in file-upload progress tracking that requires an unusual configuration. PHP recommends disabling session upload as a mitigation.

Nov 19, 2026
Vulnerability & Exploit · varonis.com

Java4Shell OpenJDK Base64 Overflow Reproduced on AVX-512 VBMI Systems

Varonis reproduced Java4Shell, a 64-byte heap overflow in OpenJDK Base64 decoding on affected JDKs with AVX-512 VBMI. The article identifies fixed builds and the JVM flag mitigation, but says it did not test the reported RCE chain.

Nov 19, 2026
Vulnerability & Exploit · aikido.dev

Ruby2Shell Flaw Enables Unauthenticated Code Execution in Vulnerable Ruby Apps

CVE-2026-132825 is a critical Ruby heap overflow in case conversion that can enable unauthenticated code execution when apps process untrusted strings in certain legacy encodings. Fixed releases are 3.3.14, 3.4.13 and 4.0.10; Ruby 3.2 and older have no fix.

Nov 19, 2026
Vulnerability & Exploit · bleepingcomputer.com

Critical NGINX HTTP/2 Flaws Enable Remote Code Execution; Linux Bug Chain Can Yield Root Access

Researchers demonstrated remote code execution through two NGINX HTTP/2 flaws; one can be chained with a Linux kernel bug for root access. F5 fixed the flaws and three others in NGINX releases, and recommends upgrading.

Nov 19, 2026
Vulnerability & Exploit · blog.qualys.com

NGINX2Root: Five nginx Flaws Disclosed, Led by CVE-2026-123007

Five nginx flaws affect specified unpatched builds. Researchers demonstrated remote code execution for CVE-2026-123007; no public in-the-wild exploitation was confirmed as of November 18, 2026. Patching is the complete fix; disabling HTTP/2 is temporary mitigation for 2

Nov 18, 2026
Vulnerability & Exploit · censys.com

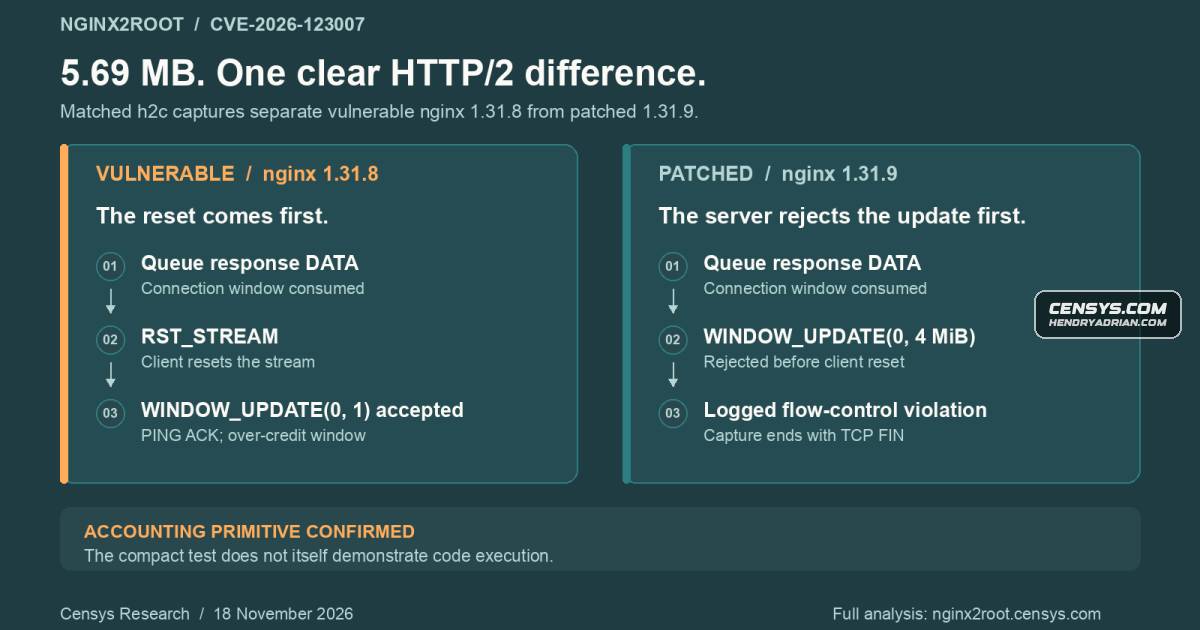
Censys Tests Five nginx2root Flaws, Reproduces Three Use-After-Free Conditions

Censys tested five nginx2root CVEs, confirming an h2c flow-control error and three use-after-free conditions; it did not reproduce the HTTP/3 proxy issue. The article details detection limits, patch versions and mitigations.

Nov 18, 2026
Vulnerability & Exploit · levelblue.com

Java4Shell (CVE-2026-114938) Corrupts Memory; Calif Reports RCE in Products

A hardware-specific OpenJDK Base64 decoder flaw can overwrite 62 bytes beyond a buffer. Calif reports product-specific RCE, but no in-the-wild exploitation was reported as of Nov. 18. The article details affected versions, fixes, workarounds and detection.

Nov 18, 2026
Vulnerability & Exploit · thehackernews.com

Decade-Old NGINX HTTP/2 Flaw Can Enable Unauthenticated Code Execution

Researchers demonstrated unauthenticated code execution through a decade-old NGINX HTTP/2 flaw. NGINX fixed it and four related flaws in versions 1.31.9 and 1.30.7; no exploitation in the wild has been reported.

Nov 18, 2026
Vulnerability & Exploit · thehackernews.com

F5 Warns Six Critical BIG-IP Flaws Can Crash Traffic and May Allow RCE

F5 disclosed six critical BIG-IP flaws that can crash TMM in specific configurations and may allow remote code execution. Engineering hotfixes are available, but no workaround is listed; the advisories report no exploitation.

Nov 18, 2026
Vulnerability & Exploit · thehackernews.com

Actively Exploited Apache Roller Flaw Enables Unauthenticated Remote Code Execution

Apache says CVE-2026-129448 affects Roller 4.0.0–6.1.4 and is actively exploited. The unauthenticated XML-RPC deserialization flaw can enable remote code execution; upgrade to 6.1.6 or later or apply the stated workarounds.

Nov 18, 2026
Vulnerability & Exploit · blog.cloudflare.com

Java4Shell OpenJDK Flaw Enables Remote Code Execution; Cloudflare Adds WAF Rules

Java4Shell (CVE-2026-114938) is a critical OpenJDK Base64-decoder heap-corruption flaw that can enable remote code execution on specific x86-64/AVX-512 systems. Cloudflare added paid-plan WAF rules; patching remains the complete fix.

Nov 18, 2026
Vulnerability & Exploit · cyble.com

Java4Shell Flaw Can Enable Code Execution on Some AVX-512 Java Servers

Java4Shell (CVE-2026-114938) is a Java Base64 decoder heap overflow affecting certain runtimes on x86-64 CPUs with AVX-512 VBMI. Researchers demonstrated code execution on some apps; no in-the-wild exploitation was reported as of Nov. 18, 2026.

Nov 18, 2026
Vulnerability & Exploit · thehackernews.com

Researchers Bypass TPM Lockouts on Some PCs to Guess Windows Hello and BitLocker PINs

Researchers reset TPM lockouts on tested AMD and Intel laptops using flash-state attacks, guessing configured PINs in 236 tries. AMD confirmed a firmware flaw and plans fixes; Intel said no Intel-component vulnerability was demonstrated.

Nov 18, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Four Actively Exploited Vulnerabilities to KEV Catalog

CISA added four vulnerabilities affecting Synology DSM, LiteLLM, Apache Axis, and REDCap to its KEV Catalog based on evidence of active exploitation, urging organizations to prioritize remediation.

Nov 18, 2026
Page 1 of 64 Next
© 2026 cyber.hendryadrian.com