
Censys Tests Five nginx2root Flaws, Reproduces Three Use-After-Free Conditions
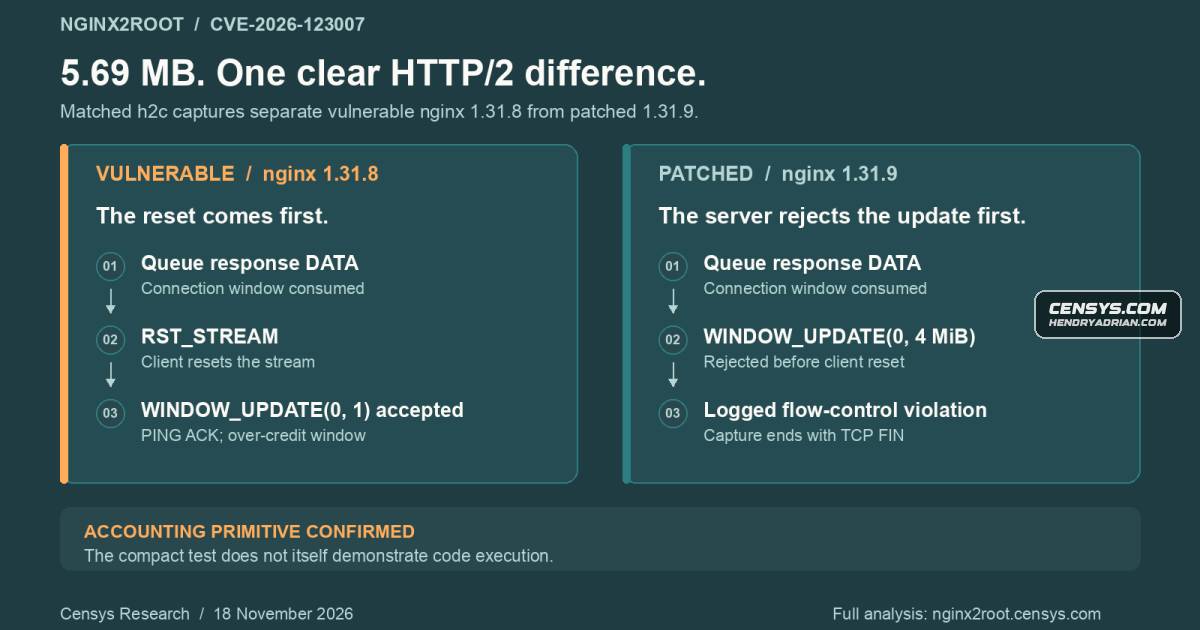
Summary
Censys tested five nginx2root CVEs, confirming an h2c flow-control error and three use-after-free conditions; it did not reproduce the HTTP/3 proxy issue. The article details detection limits, patch versions and mitigations.
Key points
- Censys confirmed the CVE-2026-123007 flow-control accounting error over cleartext HTTP/2 on nginx 1.31.8; patched 1.31.9 rejected the test sequence, which caused no crash.
- Researchers reproduced use-after-free conditions for CVE-2026-123633, CVE-2026-123634 and CVE-2026-113425; results included worker crashes, with some findings limited to AddressSanitizer or custom debug builds.
- CVE-2026-121810, involving HTTP/3 with upstream proxying, was not reproduced. The tested conditions did not result in remote code execution; Censys also said it had not verified the reported kernel flaw or exploit chain.
- Censys recommends nginx Open Source 1.30.7 or later on stable, 1.31.9 or later on mainline, and specified NGINX Plus updates, followed by a full service restart.
- Disabling HTTP/2 addresses only two of the five CVEs. Reachability depends on configuration, including HTTP/3 proxying, runtime DNS resolution with subrequests, and mail proxy authentication.
- A candidate Suricata rule fired on the tested vulnerable h2c capture and not on its patched control, but this validates only that traffic pair. Other rules remain experimental, and testing found a TCP-segmentation gap.
- As of 18 November 2026, Censys was not aware of reported in-the-wild exploitation; the article describes this as a point-in-time absence of evidence.
Article Details
- Vulnerability Types
- Use-after-free
- HTTP/2 flow-control accounting error
- Affected Versions
- nginx 1.31.8
- Exploitation Status
- not_reported
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Disable HTTP/2 or HTTP/3 to mitigate protocol-specific attack paths; disabling HTTP/2 addresses only two of the five CVEs.
- Restrict mail proxy traffic to trusted sources.
CVE
CVE-2026-113425F5 · NGINX Open Source; F5 · NGINX PlusCVE-2026-113425 Mail proxy with auth_http Stale-session crash on pristine 1.31.8, confirmed as a use-after-free under ASAN; 1.31.9 stayed runningCVE-2026-121810F5 · NGINX Open Source; F5 · NGINX PlusCVE-2026-121810 HTTP/3 with upstream proxying Not reproducedCVE-2026-123007F5 · NGINX Open Source; F5 · NGINX PlusWe reached the CVE-2026-123007 corrupted flow-control state with a compact cleartext HTTP/2 test and vulnerable and patched packet captures: github.com/Censys-Research/nginx2rootCVE-2026-123633F5 · NGINX Open Source; F5 · NGINX PlusCVE-2026-123633 HTTP/2 with upstream proxying Use-after-free and worker crash on the unmodified official 1.31.8 image; 1.31.9 did not crashCVE-2026-123634F5 · NGINX Open Source; F5 · NGINX PlusCVE-2026-123634 Runtime DNS resolution with subrequests Use-after-free confirmed under AddressSanitizer (ASAN), plus crashes on a custom debug build. No stock-image crash