Astaroth, Mekotio and Ousaban Campaigns Abuse Google Cloud Run to Deliver Banking Trojans
Summary
Talos details high-volume campaigns using Google Cloud Run links and malicious MSIs to distribute Astaroth, Mekotio and Ousaban, primarily to victims in Latin America. The report describes their infection chains, malware behavior and indicators.
Key points
- Campaign email volume rose significantly from September 2023; messages mainly targeted Latin American victims, with some activity in Europe and North America.
- Emails often impersonated invoice, financial or tax-document senders and linked to attacker-controlled Google Cloud Run services.
- The services delivered malicious MSI files directly or redirected victims to ZIP archives hosted in Google Cloud Storage.
- Talos observed Astaroth and Mekotio payloads distributed from the same Google Cloud project and storage bucket, and Ousaban delivered during an Astaroth infection; it assessed the campaigns were linked with moderate confidence.
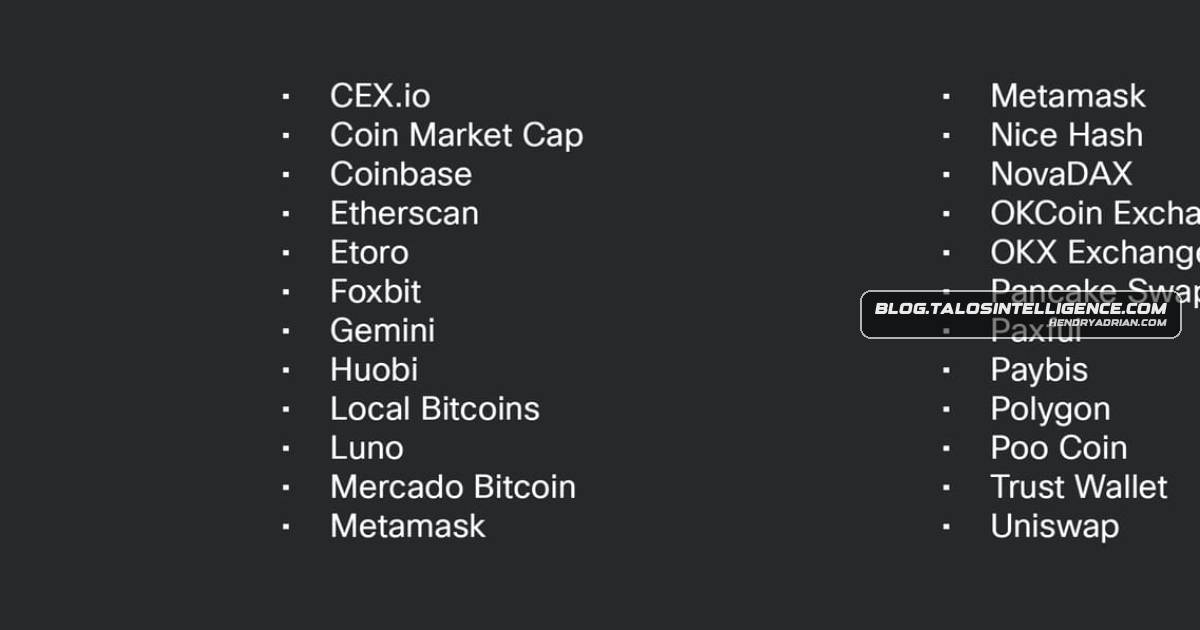
- Astaroth uses JavaScript, Bitsadmin and an AutoIt loader, and can steal banking and cryptocurrency credentials, capture keystrokes and screenshots, and persist through a Startup-folder shortcut.
- Mekotio uses malicious DLLs embedded in MSI installers and applies geolocation filtering; its command-and-control communications were not responding during analysis.
- Talos published hashes, URLs, domains and IPs, and noted available Cisco product coverage, Snort rules and ClamAV signatures.
Article Details
- Attack Vectors
- Malicious emails, often themed around invoices, financial or tax documents, deliver links to attacker-deployed Google Cloud Run services.
- Cloud Run services deliver malicious MSI installers directly or redirect victims to ZIP archives in Google Cloud Storage.
- Astaroth MSI files execute embedded JavaScript that retrieves next-stage components; Bitsadmin downloads AutoIt components and payload data.
- Mekotio MSI files contain malicious DLLs and a CAB archive with dependencies.
- Astaroth uses a loader DLL to inject its payload into regsvcs.exe, logs keystrokes, and captures screenshots of targeted banking pages.
- Astaroth establishes persistence through a Startup-menu LNK file that launches an AutoIt script using PowerShell.
- Defensive Notes
- Cisco Talos recommends blocking malicious emails, websites, domains, IPs, and URLs, and detecting or blocking the associated malware and activity using its listed Cisco security products.
- The article lists Snort SIDs 63014–63017 and 300827 and ClamAV signatures for Astaroth, Ousaban, and Mekotio.
- The attackers use cloaking, including checks for proxies and crawlers and redirects to legitimate websites; the researchers downloaded payloads by visiting URLs with Brazilian IP addresses.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 0tuiwp[.]mariomanagement[.]biz[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | 2joafm[.]marioanalytics[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | 4hawb[.]produtoeletro[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | caiiaf[.]businesswise[.]biz[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | cua3e[.]mariosolutions[.]biz[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | e0aonr[.]creativeplus[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | eeiul[.]marioadvisory[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | h4aowa[.]mariostrategy[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | kka5c[.]marioanalytics[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | lwafa[.]actiongroup[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | nqaa8e[.]businesswise[.]biz[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | nweow8[.]mariostrategy[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | w8oaa0[.]mariosolutions[.]biz[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | wba0s[.]produtoeletro[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | wiae5[.]marioadvisory[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | xwago[.]creativeplus[.]my[.]id | Domain listed as associated with the malware campaigns. |
| DOMAIN | yaiinr[.]actiongroup[.]my[.]id | Domain listed as associated with the malware campaigns. |
| HOSTNAME | 1[.]tcp[.]sa[.]ngrok[.]io | Astaroth command-and-control endpoint accessed over TCP port 26885. |
| IPV4 | 34[.]135[.]1[.]100 | Google Cloud-hosted IP address used to host Astaroth distribution URLs. |
| SHA256 | 05ef393f6e6d3f8e1ba15eec63a1c2121744400d322a03c9c8e26c1ed58cb6a7 | Hash of the encoded Astaroth payload stored as sdk.log. |
| SHA256 | 094e722972e6e4d2858dd2447d30c7025e7446f4ca60a7dc5a711f906ab5b1a0 | Hash of an Astaroth MSI associated with the campaign. |
| SHA256 | 1a9113491deb9f21c590de4f7e9e370594e47431be482b32f8a5234ad7545a0b | Hash of an AutoIt binary that drops the Astaroth payload. |
| SHA256 | 237d1bca6e056df5bb16a1216a434634109478f882d3b1d58344c801d184f95d | Hash of a legitimate AutoIt3.exe binary identified as abused by the malware. |
| SHA256 | 4fa9e718fca1fa299beab1b5fea500a0e63385b5fe6d4eb1b1001f2abd97a828 | Hash of a Mekotio MSI ZIP associated with the campaign. |
| SHA256 | 5c4a89c81be51e9e048cf3624d4a44fd4355cf6bf56a3c10217d3d3037410b55 | Hash of the Astaroth loader embedded in the AutoIt script. |
| SHA256 | 6d7148b180367e84763690fc57cbd526433026f50dc0c029b00a714ba1660cd3 | Hash of dump.log, listed as an Astaroth component. |
| SHA256 | 6e1434e0f8cd402f8acb0aade942c86d6b62cd6aa3927053f25fdf57ed384b47 | Hash of the Mekotio Binary.sknwvly.dll component. |
| SHA256 | 7c7dc2065e295eb7ec60d1f8f552e455468e19e731ad20005833d71fa1371f50 | Hash of an Ousaban component. |
| SHA256 | 8d912a99076f0bdc4fcd6e76c51a1d598339c1502086a4381f5ef67520a0ddf2 | Hash of an Astaroth MSI ZIP associated with the campaign. |
| SHA256 | b45d8630d54c8d39e3554e0c5a71003d818617e07953520a8638f0935f04dc85 | Hash of the Mekotio Binary.tnqqhgm.dll component. |
| SHA256 | b712286d4d36c74fa32127f848b79cfb857fdc2b1c84bbbee285cf34752443a2 | Hash of a legitimate SQLite3 library identified as abused by the malware. |
| SHA256 | b8afd6640de8feed1774e8db3d428c0f1bca023324bb7de9a5eb99db2ea84e26 | Hash of a Mekotio MSI associated with the campaign. |
| SHA256 | d972675774f28e7f5ad206f420470925c4fdbca681816a19aa91a6d054b8f55a | Hash of the Astaroth MSI CustomAction.idt component. |
| SHA256 | ed9f268ba7acdcbaeedd40a5c538c6a2637fd41a546363ed7587a6c2e5cdf02b | Hash of a Mekotio MSI associated with the campaign. |
| URL | hxxp[:]//avfa-wd3463btrq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxp[:]//factalia-ofh2cutija-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxp[:]//gasgas-wd3463btrq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxp[:]//haergsd-wd3463btrq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxp[:]//jx-krrdbo6imq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxp[:]//ptb-wd3463btrq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxp[:]//ptm-wd3463btrq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxp[:]//pto-wd3463btrq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxp[:]//w3iuwl[.]nextmax[.]my[.]id/?5/ | Astaroth next-stage distribution URL used to retrieve an obfuscated JScript file. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?39829895502632947 | Astaroth campaign distribution URL listed among the observed indicators. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?41991463280678058 | Astaroth campaign distribution URL listed among the observed indicators. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?50838302893639041 | Astaroth distribution URL used by Bitsadmin to retrieve a data blob containing an Ousaban payload. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?51999170290693658 | Astaroth campaign distribution URL listed among the observed indicators. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?54489451972678036 | Astaroth distribution URL used by Bitsadmin to download sqlite3.dll. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?61694995802639066 | Astaroth campaign distribution URL listed among the observed indicators. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?66559587320632971 | Astaroth distribution URL used by Bitsadmin to download a compiled AutoIt script. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?74709605275628771 | Astaroth distribution URL used by Bitsadmin to download an executable component. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?75129547751613994 | Astaroth campaign distribution URL listed among the observed indicators. |
| URL | hxxp[:]//wae4w[.]mariomanagement[.]biz[.]id/?76849368130628733 | Astaroth campaign distribution URL listed among the observed indicators. |
| URL | hxxps[:]//arr-wd3463btrq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxps[:]//portu-wd3463btrq-uc[.]a[.]run[.]app | Attacker-deployed Google Cloud Run URL associated with malware distribution. |
| URL | hxxps[:]//storage[.]googleapis[.]com/alele/FAT[.]1705617082[.]zip | Specific Google Cloud Storage URL identified as a Mekotio MSI ZIP payload. |
| URL | hxxps[:]//storage[.]googleapis[.]com/alele/FAT[.]1705617082[.]zip?Expires=1705677865&GoogleAccessId=smart-ratio-400902%40appspot[.]gserviceaccount[.]com&Signature=K7npJ4T3kyH0aMrcErYkgwQ9xBdJgVCfEeTXrGd73OJ02bpTtk1e5jIiOUofmiT6bVIzsyERH9%2FhkeBaY1qtsRmafNxGE0VBAuoNrKwnrYIEYAdVjkqyoqwTN%2BEWrfCSdojylzx0iSHn1rFVqyDZJC0yETT%2BJDMa5wi%2BN3m7DGxyPVc112cXVSlwzfzW5b12I165NFUEimZ1ukLF2BzEDMLxyW5Iz%2FFUNzzt6L%2BZrsID1slWVAu%2BDaXBrhyR9zYCokUR9ig1CWLo8qBvJlMsoPqro%2F1DZpZqH36Qx%2BMTbOifj%2BAPoDCYQfqKxedXcgz4mn2VM1hxkeKRQvwFXnIsRQ%3D%3D | Specific Google Cloud Storage URL delivering a Mekotio MSI ZIP. |
| URL | hxxps[:]//storage[.]googleapis[.]com/alele/Fat[.]184949849[.]zip | Specific Google Cloud Storage URL identified as an Astaroth MSI ZIP payload. |
| URL | hxxps[:]//storage[.]googleapis[.]com/alele/Fat[.]184949849[.]zip?Expires=1705678087&GoogleAccessId=smart-ratio-400902%40appspot[.]gserviceaccount[.]com&Signature=a0JYCUEIUqgtwYBtulJu8NKBZU3VIXUAG2GRKcvBZbny5CA7rGeCP8Ys8FGNoishpJAgSIJuqo6QBkzNv167IVEBcUz49BZjD4cUFLhfjPaCWgqOE1iduQGyuqQkwPJIN8Y6THlvMzM8I6nlT3lpi%2BYJv56kBv6%2Boy6GariSspImcZxBJBv9unPrWSm5qRSA3icLnWvZ3PyIfEmtp4IiCQ4LItV%2Frt50p9mN4x1%2Blnq0PT5tgO%2BNkw%2FOeb0IXVZYdpTGwVSvDqGw6IHvOZP5us7u%2F%2BGEeOy%2F2kRKJMdE%2B1U%2F0UCVEp6gIbUcDQZj%2B16JwzbAGnVd4B8JJNtRrN87kg%3D%3D | Specific Google Cloud Storage URL delivering an Astaroth MSI ZIP. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article describes obfuscated embedded JavaScript and XOR-encoded Astaroth and Ousaban payloads.T1055 · Process InjectionThe Astaroth loader injects the decoded payload into regsvcs.exe in memory.T1056.001 · KeyloggingAstaroth can log keystrokes when a targeted bank is open.T1059.001 · PowerShellA Startup-menu LNK uses PowerShell to launch the AutoIt binary with the compiled script.T1059.003 · Windows Command ShellAstaroth uses cmd.exe commands to create files and write component names to disk.T1059.007 · JavaScriptAstaroth MSI files contain embedded JavaScript that retrieves and runs the next infection stage.T1105 · Ingress Tool TransferMalware stages and components are downloaded from attacker distribution servers and Google Cloud Storage.T1113 · Screen CaptureAstaroth captures screenshots around the mouse pointer on clicks at targeted bank pages.T1140 · Deobfuscate/Decode Files or InformationThe loader decodes XOR-encoded payload files before loading them.T1197 · BITS JobsAstaroth uses bitsadmin.exe to retrieve executables, a DLL, a compiled script, and a data blob.T1547.001 · Registry Run Keys / Startup FolderAstaroth persists with an LNK file placed in the Startup menu.T1566.002 · Spearphishing LinkCampaign emails contain links to attacker-deployed Cloud Run services that deliver malware.T1614 · System Location DiscoveryMekotio queries an IP geolocation service and filters infections based on the system's location.
People
Malware
AstarothAstaroth, Mekotio & Ousaban abusing Google Cloud Run in LATAM-focused malware campaignsGuildmaGoogle Cloud Run is currently being abused in high-volume malware distribution campaigns, spreading several banking trojans such as Astaroth (aka Guildma), Mekotio and Ousaban to targets across Latin America and Europe.MekotioAstaroth, Mekotio & Ousaban abusing Google Cloud Run in LATAM-focused malware campaignsOusabanAstaroth, Mekotio & Ousaban abusing Google Cloud Run in LATAM-focused malware campaigns
Vendors
Products
Tools
AutoItretrieves the legitimate executable associated with AutoIt3.exe which will be used to execute a compiled AutoIt script later in the infection process.bitsadminThe malware then uses the Bitsadmin living-off-the-land binary (LoLBin) to retrieve the next-stage components from the aforementioned distribution server. First, it retrieves the legitimate executable associated withClamAVThe following ClamAV signatures have been released to detect malware artifacts related to this threat:NgrokThe payload communicates with C2 using Ngrok (1[.]tcp[.]sa[.]ngrok[.]io) over TCP/26885. At the time of our analysis, this server accepted connections but did not respond in return.SnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org.