CoralRaider Uses RotBot and XClient to Steal Credentials and Social Media Data
Summary
Cisco Talos details CoralRaider, a financially motivated group assessed to be based in Vietnam, using malicious Windows shortcuts, RotBot and XClient to steal credentials, financial information and social media data across several Asian countries.
Key points
- Talos says CoralRaider has operated since at least 2023 and targets victims in multiple Asian and Southeast Asian countries.
- The campaign starts with a malicious Windows shortcut that downloads an HTA file and runs obfuscated scripts to deploy RotBot.
- RotBot, a customized QuasarRAT variant, performs reconnaissance and uses Telegram bots for command and control and data exfiltration.
- XClient steals browser credentials, cookies, financial information, and data from Facebook, Instagram, TikTok, YouTube, Telegram and Discord.
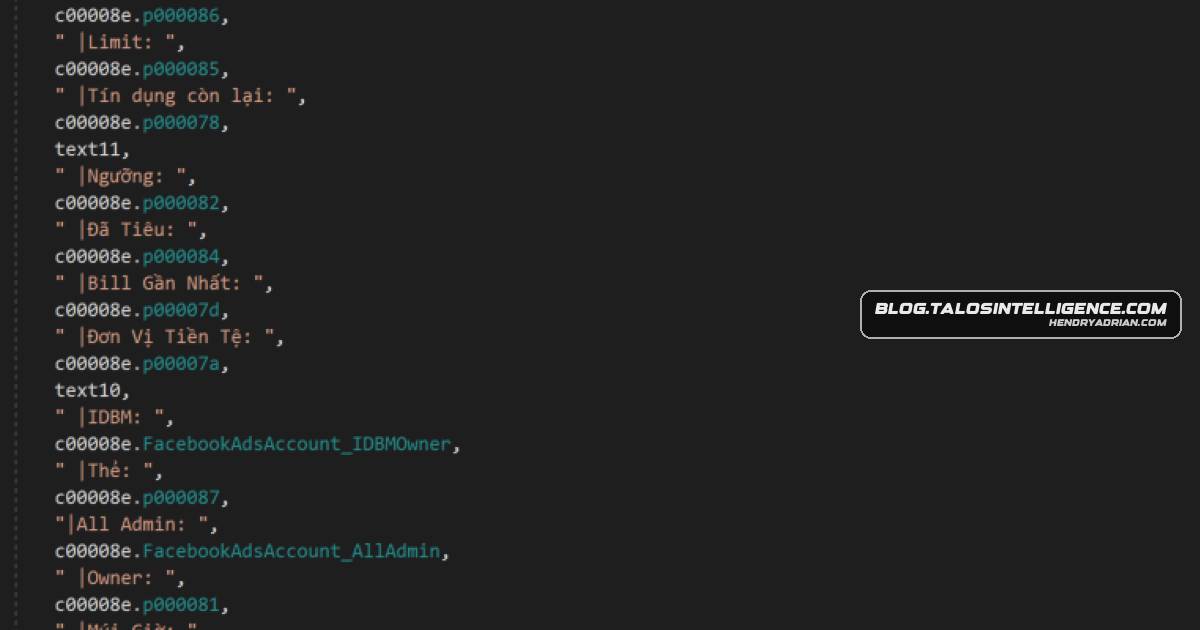
- The malware targets Facebook business and advertising accounts, including account details and payment information.
- The operators use anti-VM and anti-analysis checks, evade security tools, and abuse legitimate services and Windows binaries.
- Talos published indicators of compromise and lists Snort and ClamAV detections for the campaign.
Article Details
- Attack Vectors
- A malicious Windows shortcut file downloads and executes an HTA from an attacker-controlled download server. The article does not identify the server.
- The HTA runs an embedded obfuscated Visual Basic script, which executes PowerShell scripts that perform evasion and UAC-bypass activity before downloading RotBot.
- RotBot downloads its configuration from a host on a legitimate domain that Talos says is likely controlled by the threat actor; the domain is not disclosed.
- RotBot communicates with a Telegram bot used as the C2 channel. XClient steals browser, financial, and social-media data, then exfiltrates collected files through the bot.
- Defensive Notes
- Cisco states that Secure Endpoint can help prevent execution of the described malware, and Secure Web Appliance can block access to malicious websites and detect malware.
- Cisco recommends Secure Email, Secure Firewall, Secure Malware Analytics, Umbrella, and Cisco Duo as additional protections.
- The article reports Snort SID 63192 for this threat and lists ClamAV detections: Lnk.Downloader.CoralRaider-10024620-0, Html.Downloader.CoralRaider-10025101-0, Win.Trojan.RotBot-10024631-0, and Win.Infostealer.XClient-10025106-2.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 118[.]71[.]64[.]18 | Talos says this Hanoi IP address, observed in an image from the actor's debug bot, is likely CoralRaider's IP address. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelRotBot and XClient exfiltrate victim data and collected files through the Telegram bot C2.T1057 · Process DiscoveryRotBot checks running processes on the victim machine.T1059.001 · PowerShellThe Visual Basic script executes embedded PowerShell scripts, which decrypt and run additional scripts.T1059.005 · Visual BasicThe HTA runs an embedded Visual Basic script.T1082 · System Information DiscoveryRotBot performs reconnaissance of system data on the victim machine.T1113 · Screen CaptureXClient captures screenshots of the victim's desktop and saves them as PNG files.T1204.002 · Malicious FileThe infection begins when a victim opens a malicious Windows shortcut file.T1218.005 · MshtaThe downloaded HTA file executes the embedded script.T1497.001 · System ChecksRotBot and XClient perform virtual-environment checks, including checks for VMware, VirtualBox, and Sandboxie.T1518.001 · Security Software DiscoveryXClient checks whether antivirus software, including AVG, Avast, and Kaspersky, is running.T1539 · Steal Web Session CookieXClient collects browser cookies, including Facebook cookies used to access the victim's account.T1548.002 · Bypass User Account ControlThe PowerShell scripts are reported to bypass User Access Controls.T1555.003 · Credentials from Web BrowsersXClient collects stored credentials and other data from browser files.T1560.001 · Archive via UtilityXClient packages collected victim data into a ZIP archive.
People
Threat Actors
Malware
QuasarRATThey use RotBot, a customized variant of QuasarRAT, and XClient stealer as payloads in the campaign we analyzed.RotBotThey use RotBot, a customized variant of QuasarRAT, and XClient stealer as payloads in the campaign we analyzed.XClientThey use RotBot, a customized variant of QuasarRAT, and XClient stealer as payloads in the campaign we analyzed.
Vendors
CiscoCisco Talos discovered a new threat actor we’re calling “CoralRaider” that we believe is of Vietnamese origin and financially motivated. CoralRaider has been operating since at least 2023, targeting victims in severalQiAnXinthe attack chain components of this campaign can be found in the report published by the researchers at QiAnXin Threat Intelligence Center.
Products
Avastit runs in the Sandboxie environment. XClient stealer also checks if anti-virus software, including AVG, Avast, and Kaspersky, is running on the victim’s machine. AVGif it runs in the Sandboxie environment. XClient stealer also checks if anti-virus software, including AVG, Avast, and Kaspersky, is running on the victim’s machine. DiscordTikTok business ads, and YouTube. It also collects the application data from the Telegram desktop and Discord application on the victim's machine. The stealer plugin can capture screenshots of the victim’s desktopFacebookactor’s Desktop on the Telegram bot, we found a few Telegram groups in Vietnamese named “Kiém tien tá» Facebook,” “Mua Bán Scan MINI,” and “Mua Bán Scan Meta.” Monitoring these groups revealed that they wereInstagramcredit card details. It also collects the victim’s data from social media accounts, including Facebook, Instagram, TikTok business ads, and YouTube. It also collects the application data from the Telegram desktop andKasperskySandboxie environment. XClient stealer also checks if anti-virus software, including AVG, Avast, and Kaspersky, is running on the victim’s machine. Microsoft Office 365versions — the first was created on May 10, 2023. We also spotted that they have logged into their Microsoft Office 365 account with the display name “daloia krag” while accessing the spreadsheet, and CoralRaiderMicrosoft WindowsThe actor uses the dead drop technique, abusing a legitimate service to host the C2 configuration file and uncommon living-off-the-land binaries (LoLBins), including Windows Forfiles.exe and FoDHelper.exe Sandboxiechecks if a DLL called sbieDll.dll exists in the victim machine file system to detect if it runs in the Sandboxie environment. XClient stealer also checks if anti-virus software, including AVG, Avast, and Kaspersky, isTelegramconfidence that the CoralRaider operators are based in Vietnam, based on the actor messages in their Telegram C2 bot channels and language preference in naming their bots, PDB strings, and other Vietnamese wordsTikTokdetails. It also collects the victim’s data from social media accounts, including Facebook, Instagram, TikTok business ads, and YouTube. It also collects the application data from the Telegram desktop and DiscordVirtualBoxthe radar. First, it will do virtual environment evasion if the victim’s machine runs in VMware or VirtualBox. It also checks if a DLL called sbieDll.dll exists in the victim machine file system to detect if itVMwarehelp it to avoid the radar. First, it will do virtual environment evasion if the victim’s machine runs in VMware or VirtualBox. It also checks if a DLL called sbieDll.dll exists in the victim machine file system toYouTubethe victim’s data from social media accounts, including Facebook, Instagram, TikTok business ads, and YouTube. It also collects the application data from the Telegram desktop and Discord application on the victim's
Countries
BangladeshTalos observed that CoralRaider is conducting a malicious campaign targeting victims in multiple countries in Asia and Southeast Asia, including India, China, South Korea, Bangladesh, Pakistan, Indonesia and Vietnam. ChinaTalos observed that CoralRaider is conducting a malicious campaign targeting victims in multiple countries in Asia and Southeast Asia, including India, China, South Korea, Bangladesh, Pakistan, Indonesia and Vietnam. IndiaTalos observed that CoralRaider is conducting a malicious campaign targeting victims in multiple countries in Asia and Southeast Asia, including India, China, South Korea, Bangladesh, Pakistan, Indonesia and Vietnam. IndonesiaTalos observed that CoralRaider is conducting a malicious campaign targeting victims in multiple countries in Asia and Southeast Asia, including India, China, South Korea, Bangladesh, Pakistan, Indonesia and Vietnam. PakistanTalos observed that CoralRaider is conducting a malicious campaign targeting victims in multiple countries in Asia and Southeast Asia, including India, China, South Korea, Bangladesh, Pakistan, Indonesia and Vietnam. South KoreaTalos observed that CoralRaider is conducting a malicious campaign targeting victims in multiple countries in Asia and Southeast Asia, including India, China, South Korea, Bangladesh, Pakistan, Indonesia and Vietnam. VietnamCoralRaider operators likely based in Vietnam