
FriendlyDealer Uses Fake App Stores to Funnel Users to Gambling Sites
Summary
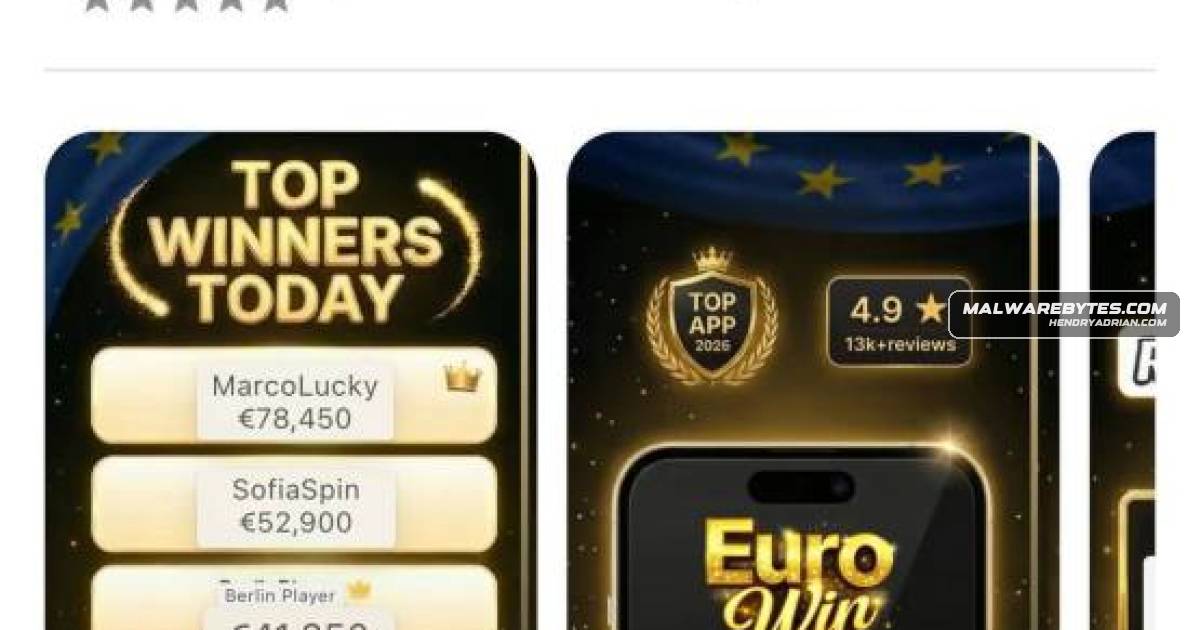
Malwarebytes describes FriendlyDealer, a campaign using fake app-store pages across 1,500+ domains to install PWAs that redirect users to gambling offers. The kit collects telemetry but, according to the report, does not install traditional malware or steal passwords.
Key points
- A reusable kit generates fake Google Play and Apple App Store pages across at least 1,500 domains and more than 20 casino-brand skins.
- The pages prompt users to install Progressive Web Apps that appear on the home screen, then route them to gambling offers through affiliate links.
- The kit uses device detection, browser-specific handlers, and Chrome’s mobile install prompt to make the installation flow appear legitimate.
- Campaign code sends browser and advertising identifiers, telemetry, and JavaScript error reports to ihavefriendseverywhere[.]xyz; it can also register push notifications if permission is granted.
- The report says the operation earns affiliate commissions and does not install traditional malware or steal passwords; the reported harm is deceptive routing to gambling sites.
- The researchers could not attribute the campaign to a specific group; Russian-language code artifacts suggest a Russian-speaking development context but may have been inherited or reused.
- The article provides removal and site-data-clearing steps for Android and iPhone users who installed one of the PWAs.
Article Details
- Attack Vectors
- Paid ads lead users to fake Google Play or Apple App Store pages hosted across more than 1,500 domains.
- The pages prompt users to install Progressive Web Apps that imitate gambling apps and redirect users to casino offers through affiliate links.
- The kit detects the device and uses browser-specific links to reopen pages in Chrome or Safari so it can trigger the install flow.
- The installed web apps can request notification permission and collect browser, device, advertising, and error telemetry.
- Defensive Notes
- Remove any unrecognized app or PWA from the home screen.
- Clear site data for the relevant site in Chrome or Safari, and check other Chromium-based browsers if used.
- Review browser or website notification permissions and revoke access for unrecognized sites.
- If money was deposited after being redirected from one of these pages, contact the bank or payment provider promptly.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ihavefriendseverywhere[.]xyz | Campaign data-collection server receiving telemetry and JavaScript error reports from FriendlyDealer deployments. |
| DOMAIN | valor[.]bet | Domain identified as a FriendlyDealer gate or checkpoint. |
MITRE ATT&CK
T1071.001 · Web ProtocolsThe app and background script send telemetry and error reports to the campaign server using web requests.T1119 · Automated CollectionThe kit automatically gathers browser and advertising data and records JavaScript errors from users' devices.T1204.001 · Malicious LinkUsers are induced to follow ad-driven pages and tap an install prompt to add a FriendlyDealer PWA.T1656 · ImpersonationThe campaign uses fake pages impersonating Google Play and the Apple App Store to persuade users to install gambling PWAs.
Products
App Storelarge-scale social-engineering campaign that uses a reusable web kit to create fake Google Play and Apple App Store pages (deployed across 1,500+ domains) which trick users into installing Progressive Web Apps thatGoogle Chromeincrease authenticity include device detection, correct platform fonts, browser-specific handlers to open Chrome/Safari, suppression of zooming, and use of Chrome’s install prompt to bypass unknown-source warnings.Google PlayFriendlyDealer is a large-scale social-engineering campaign that uses a reusable web kit to create fake Google Play and Apple App Store pages (deployed across 1,500+ domains) which trick users into installingSafariauthenticity include device detection, correct platform fonts, browser-specific handlers to open Chrome/Safari, suppression of zooming, and use of Chrome’s install prompt to bypass unknown-source warnings.