
Sekoia Details EvilTokens PhaaS That Automates BEC Reconnaissance with AI
Summary
Sekoia analyzes EvilTokens, a Microsoft device-code phishing service that uses harvested tokens for mailbox access and Graph reconnaissance, then applies chained LLMs to identify financial threads and draft tailored BEC scenarios.
Key points
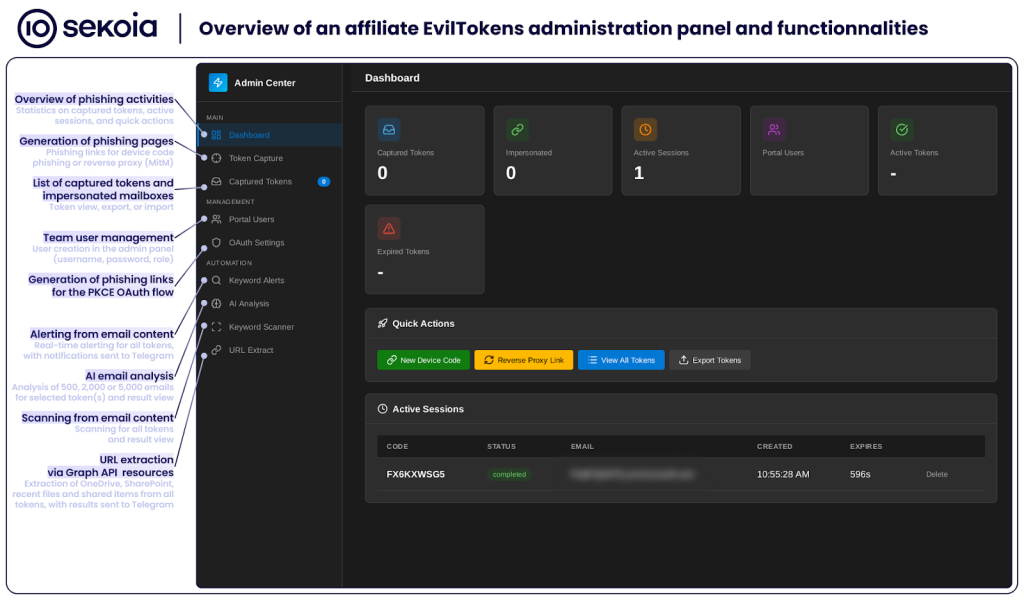
- Sekoia reports that EvilTokens is marketed through Telegram as a phishing-as-a-service offering with device-code phishing kits and an affiliate administration panel.
- The service captures Microsoft access and refresh tokens through the device-code flow; its custom browser and webmail interface are designed for access to compromised Microsoft 365 accounts.
- The backend uses Microsoft Graph to gather mailbox, contact, calendar, and organization information; Sekoia says tokens can also be exchanged for a Primary Refresh Token to establish persistence.
- Its two-stage LLM pipeline analyzes up to 5,000 emails in batches, identifies potential financial exposure, and generates tailored BEC scenarios and draft emails.
- Sekoia analyzed public affiliate repositories containing PHP phishing-page code that relays device-code requests to a centralized backend; analysts assess with high confidence that the repositories belong to an affiliate.
- Sekoia assesses that EvilTokens is the first PhaaS to offer AI-augmented post-compromise tooling, potentially reducing the effort and time needed to prepare targeted BEC fraud.
Article Details
- Attack Vectors
- Device-code phishing pages impersonating Microsoft, Outlook, Adobe Acrobat, or DocuSign trick victims into completing an authentication flow that yields access and refresh tokens.
- Stolen tokens are used to access compromised Microsoft 365 mailboxes and other services; the service also converts tokens into cookies for live browser sessions.
- Microsoft Graph API requests collect mailbox contents and organizational information for reconnaissance and tailored business email compromise (BEC) fraud.
- An AI-driven pipeline analyzes stolen emails and reconnaissance data to identify financial opportunities and draft victim-tailored BEC messages.
- Defensive Notes
- Sekoia assesses that the automated workflow can reduce the time available for defenders to detect and respond to post-compromise activity to a few minutes.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | machinemind-market[.]com | Domain for the dedicated website selling the EvilTokens Portal Browser, an attacker-associated tool for accessing accounts with stolen tokens. |
MITRE ATT&CK
T1078 · Valid AccountsAffiliates use harvested tokens to access compromised Microsoft accounts and mailboxes.T1087.004 · Cloud AccountThe backend queries Microsoft Graph manager and directReports data to identify organizational relationships and potential targets.T1114 · Email CollectionThe backend collects victims’ emails and mailbox contents for analysis and BEC targeting.T1528 · Steal Application Access TokenThe backend captures Microsoft access and refresh tokens after victims complete the device-code authorization flow.T1550.001 · Application Access TokenEvilTokens uses harvested application access tokens to access Microsoft services and mailbox data.T1550.004 · Web Session CookieThe pipeline converts tokens into cookies for access to live browser sessions on Microsoft domains.T1566 · PhishingEvilTokens phishing pages impersonate services such as Microsoft and DocuSign to induce victims to submit device codes.T1567 · Exfiltration Over Web ServiceThe article describes Microsoft Graph API requests used to retrieve victim data for the service’s post-compromise workflow.
Vendors
Groqingests up to 5,000 emails in batches, uses LLM models (llama-3.1-8b-instant, llama-3.3-70b-versatile, Groq API, and gpt-4o-mini) to identify financial exposure, synthesize risk reports, and automatically draftMicrosoftEvilTokens is a Phishing-as-a-Service (PhaaS) that provides turnkey Microsoft device code phishing pages, a centralised affiliate administration panel, and a custom browser to weaponise harvested access and refreshOpenAIAdditionally, EvilTokens leverages gpt-4o-mini directly via the OpenAI API to automatically translate stolen emails into English for attackers working with non-English victim mailboxes.
Products
Microsoft 365 Apps for EnterpriseThe platform includes a custom “Portal Browser” (ET Browser) to simultaneously access multiple Microsoft 365 accounts using stolen tokens, and a built-in webmail interface that impersonates Outlook for direct mailboxMicrosoft GraphIts backend integrates an AI-driven pipeline that uses Microsoft Graph API and chained LLM prompts to automatically identify exploitable payment threads and draft tailored BEC emails, dramatically accelerating
Tools
ET BrowserThe platform includes a custom “Portal Browser” (ET Browser) to simultaneously access multiple Microsoft 365 accounts using stolen tokens, and a built-in webmail interface that impersonates Outlook for direct mailboxEvilTokensEvilTokens is a Phishing-as-a-Service (PhaaS) that provides turnkey Microsoft device code phishing pages, a centralised affiliate administration panel, and a custom browser to weaponise harvested access and refreshPortal BrowserThe platform includes a custom “Portal Browser” (ET Browser) to simultaneously access multiple Microsoft 365 accounts using stolen tokens, and a built-in webmail interface that impersonates Outlook for direct mailbox