cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2394 articles

Threat Research · zscaler.com

Shai-Hulud Expands to PyPI, CI/CD Abuse, IDE Hooks and AI Scanner Evasion

Zscaler describes Shai-Hulud’s spread from npm to PyPI and its use of CI/CD abuse, IDE configuration hooks, credential theft and prompt injection. The worm’s source code became public on May 12, 2026, making its techniques reusable.
Jun 12, 2026
Threat Research · research.checkpoint.com

LangGraph Checkpointer Flaws Could Enable Remote Code Execution

Check Point researchers detail three LangGraph checkpointer vulnerabilities, including SQL injection flaws and unsafe MessagePack deserialization that can chain to remote code execution under specific conditions. LangChain has patched the issues.

Jun 11, 2026
Threat Research · guardsix.com

RoguePlanet Exploit Uses Windows Defender Race to Gain SYSTEM Privileges

RoguePlanet is a Windows local privilege escalation PoC that exploits a TOCTOU flaw in Defender’s remediation process to place and run an attacker-controlled executable as SYSTEM. It reportedly works on fully updated Windows 10 and 11 systems.

Jun 11, 2026
Threat Research · gendigital.com

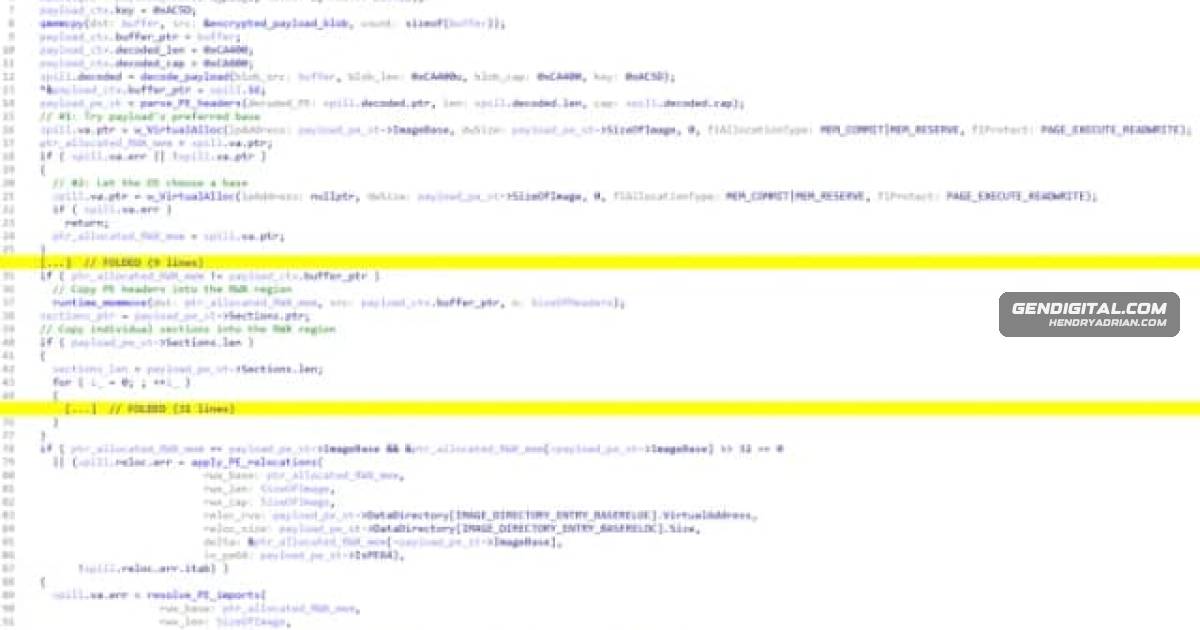
GoFlateLoader Uses Oversized PE Overlays to Deliver Infostealers

Gen Threat Labs describes GoFlateLoader, a Go loader that manually maps payloads in memory and uses 700–950 MB PE overlays to hinder scanning. It is distributed via cracked software and a malicious TDS to deliver several infostealers.

Jun 11, 2026
Threat Research · feeds.fortinet.com

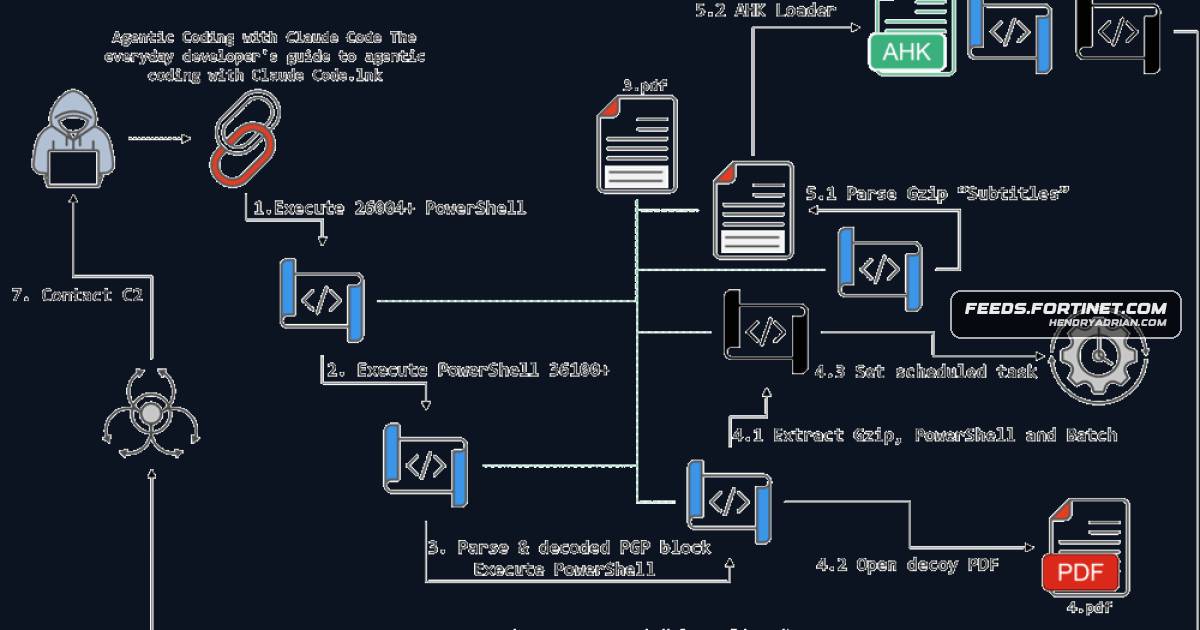
Fortinet Details AI-Themed Lures Delivering AsyncRAT Through a Multistage Windows Infection Chain

Fortinet describes a Windows malware campaign using AI-themed document lures and staged scripts to install AsyncRAT and another .NET RAT, establish persistence, evade defenses, and communicate with attacker-controlled servers.

Jun 11, 2026
Threat Research · cyfirma.com

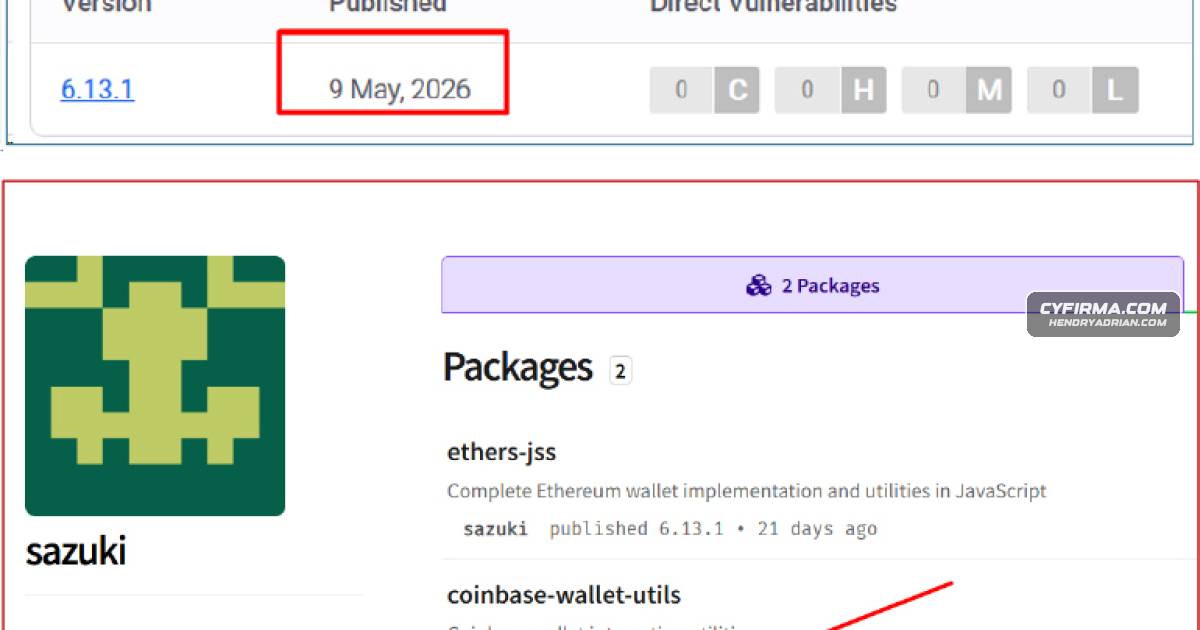
CYFIRMA Analyzes 11 Suspicious npm Packages, Including moralis-sdk With 2.7M Downloads

CYFIRMA analyzed 11 malicious or highly suspicious npm packages targeting Web3 developers; moralis-sdk had over 2.7 million downloads. The report details wallet and credential theft, staged payloads, blockchain-based C2, and on-chain exfiltration.

Jun 11, 2026
Threat Research · circleid.com

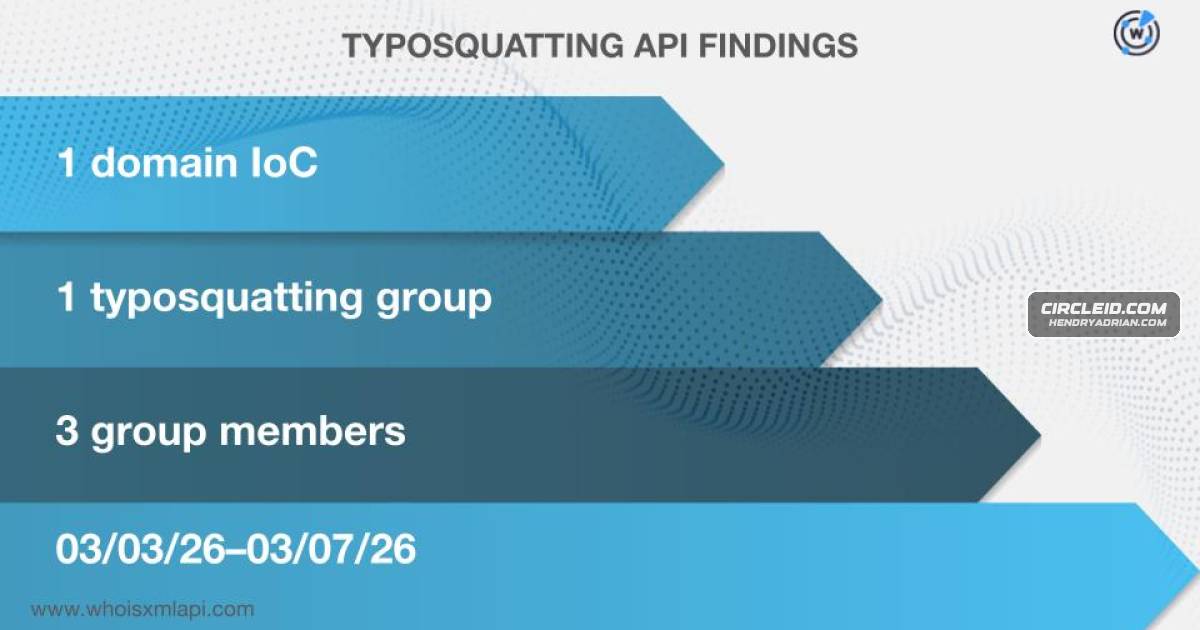
DNS Analysis Maps 90 Domains Linked to Pushpaganda Scareware Campaign

HUMAN’s Satori team linked Pushpaganda’s Google Discovery feed abuse, SEO manipulation and AI-generated lures to scareware and scams. A DNS/WHOIS review of 90 domains found 162 associated IPs (101 confirmed malicious) and 1,055 email-connected domains.

Jun 11, 2026
Threat Research · huntress.com

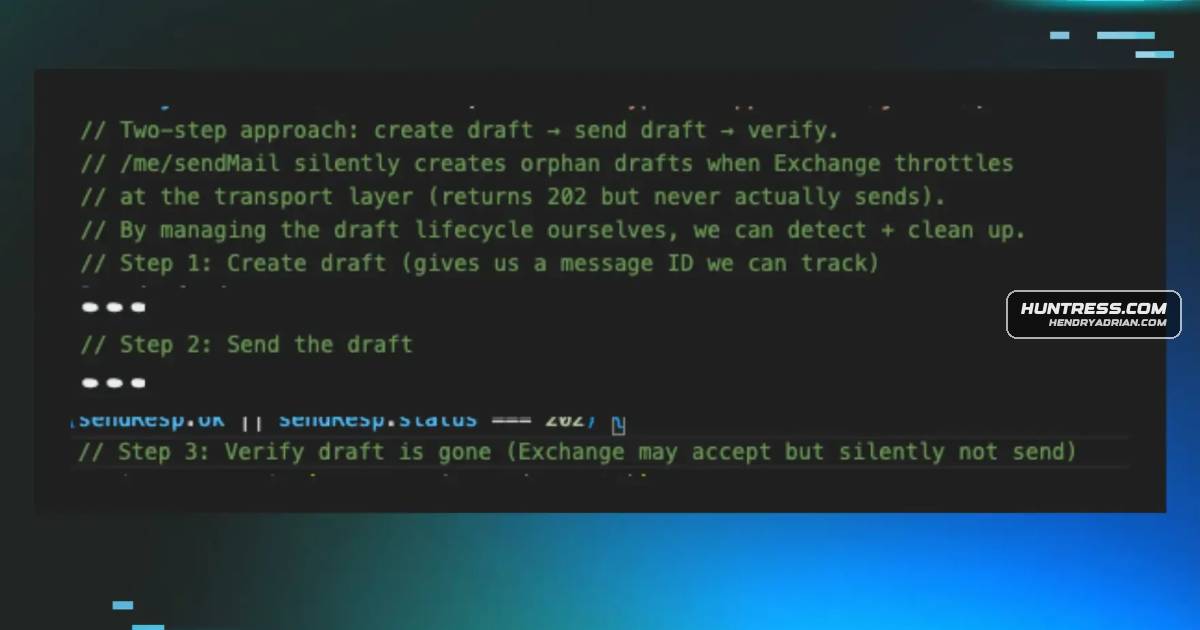
Huntress Details Kali365 Phishing Kit’s Microsoft 365 Token Theft and Fraud Tools

Huntress analyzed Kali365/Octopi365, a phishing-as-a-service kit that steals Microsoft 365 tokens through device-code and AiTM attacks, then enables mailbox access, persistence, and follow-on fraud.

Jun 11, 2026
Threat Research · securitylabs.datadoghq.com

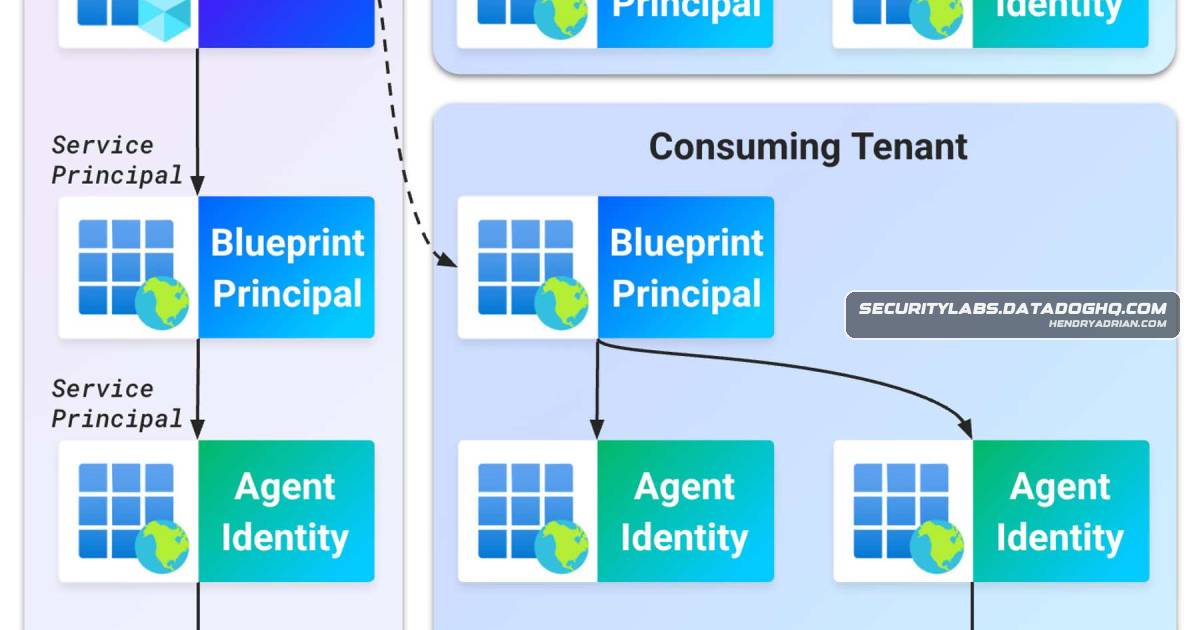
Entra Agent ID Blueprints Can Expand the Impact of a Compromise Across Identities and Tenants

Datadog explains how Entra Agent ID blueprints authenticate associated identities and how a compromised blueprint could expose their permissions across multiple identities and tenants.

Jun 11, 2026
Threat Research · cloud.google.com

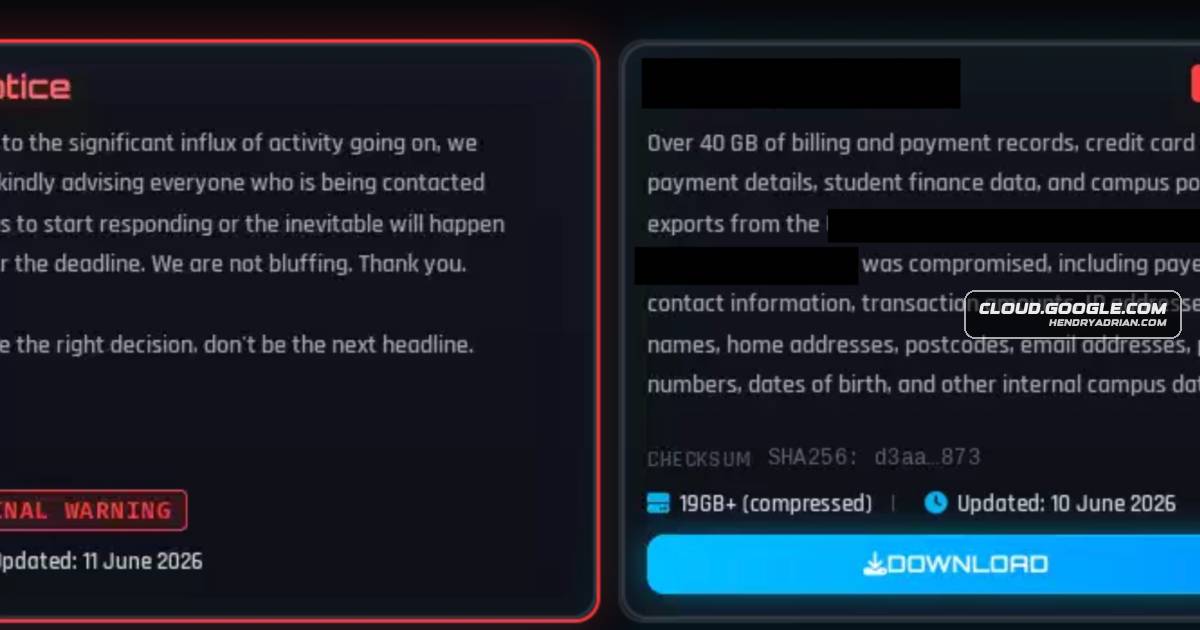
ShinyHunters Exploited Oracle PeopleSoft Zero-Day in Campaign Targeting Education Organizations

Mandiant and Google say ShinyHunters exploited CVE-2026-35273 in Oracle PeopleSoft from May 27 to June 9, 2026, using MeshCentral agents for reconnaissance and lateral movement before data was published on the group’s leak site.

Jun 11, 2026
Threat Research · cloudsek.com

Researchers Detail FIFA World Cup Ticket Phishing Kit That Can Intercept OTPs

CloudSEK reports a multi-tenant operation using FIFA ticket-site clones to harvest card data and potentially relay OTPs. The researchers identified dozens of impersonation domains but could not verify victim totals or financial losses.

Jun 11, 2026
Threat Research · welivesecurity.com

OceanLotus Uses SPECTRALVIPER in FireAnt Supply-Chain Attack and Vietnamese Espionage Campaign

ESET researchers detail two OceanLotus campaigns from 2024–2026: a FireAnt MetaKit supply-chain compromise that delivered SPECTRALVIPER to some investors and a prolonged intrusion at a Vietnamese construction company.

Jun 11, 2026
Threat Research · bleepingcomputer.com

Miasma Worm Source Code Leaked on GitHub, Revealing Supply-Chain Capabilities

SafeDep says Miasma’s source code was deliberately posted to GitHub through compromised developer accounts. Its analysis describes credential theft, GitHub-based propagation, destructive token-revocation behavior, and obfuscated payload builds.

Jun 10, 2026
Threat Research · thehackernews.com

Researchers Say China-Linked JDY Botnet Now Spans 1,500+ Devices

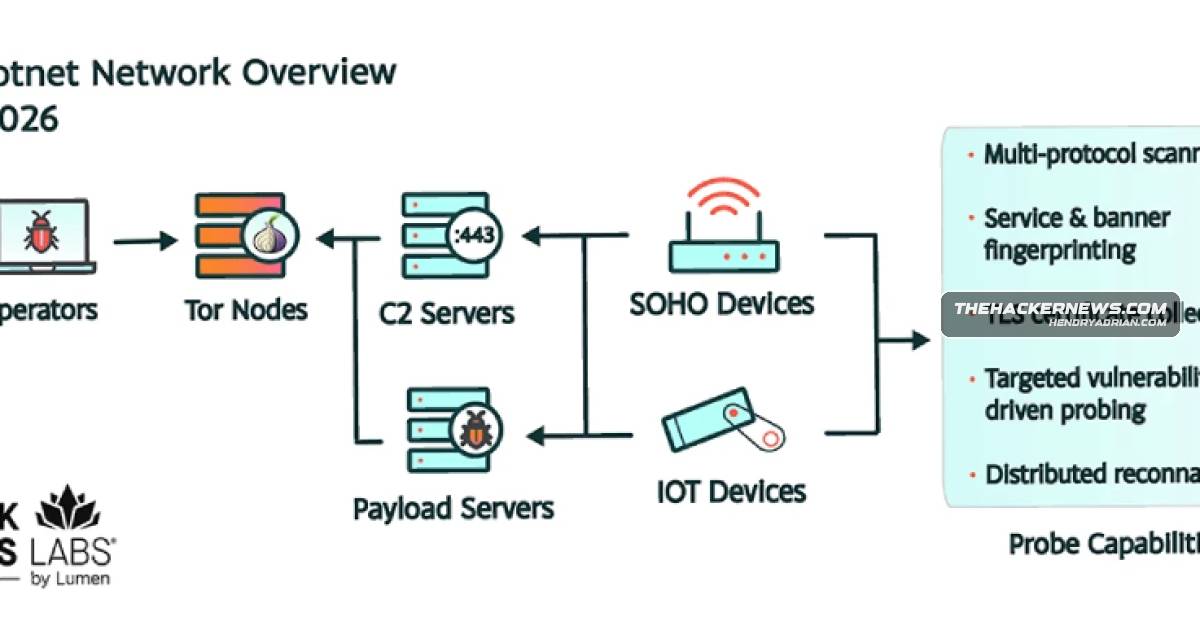
Lumen's Black Lotus Labs says the JDY botnet has grown beyond 1,500 compromised SOHO/IoT devices, using layered C2 and targeted service fingerprinting to provide reconnaissance data to China-linked threat actors.

Jun 10, 2026
Threat Research · krebsonsecurity.com

OSINT Investigation Links The Gentlemen Admin to Russian Man

KrebsOnSecurity details an OSINT investigation linking The Gentlemen ransomware administrator aliases Hastalamuerte and Zeta88 to Alexander Andreevich Yapaev in Izhevsk, based on account, phone and email records. Yapaev did not respond.

Jun 10, 2026
Threat Research · bleepingcomputer.com

JDY Botnet Expands to More Than 1,500 Devices, Targets U.S. Military Networks

Black Lotus Labs reports that the JDY botnet has grown to more than 1,500 SOHO and IoT devices, focusing on U.S. military-related targets and scanning for newly disclosed vulnerabilities. Its operators use Tor-based command-and-control.

Jun 10, 2026
Threat Research · cloudsek.com

WooCommerce Skimmer Mimics Stripe Checkout to Steal Payment Card Data

CloudSEK analyzes an obfuscated skimmer targeting WooCommerce Payments that overlays fake Stripe fields, captures card details and customer emails during real purchases, and sends the data to an attacker-controlled endpoint.

Jun 10, 2026
Threat Research · acronis.com

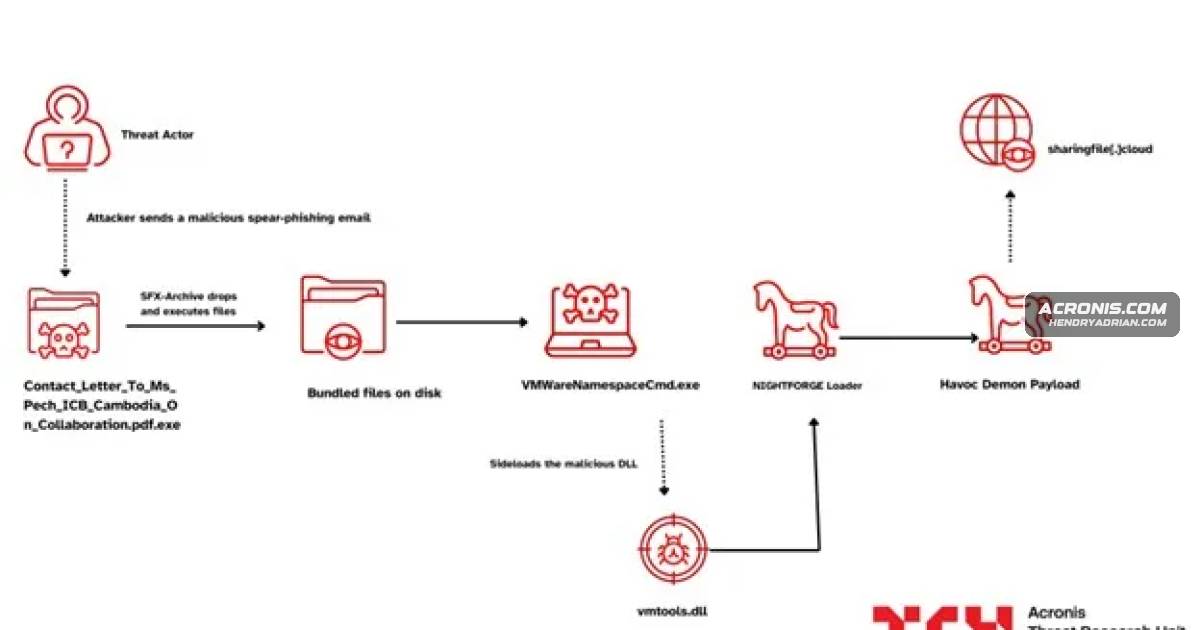
Khmer Shadow Campaigns Target Cambodian Government with NIGHTFORGE Loader and Havoc Demon

Acronis details two espionage campaigns targeting Cambodian government entities. The Khmer Shadow cluster used SFX lures and a DLL-sideloaded NIGHTFORGE loader to deploy Havoc Demon, employing evasion techniques and reusing infrastructure.

Jun 10, 2026
Threat Research · thehackernews.com

Reco Demonstrates LLM Agent Finding and Exploiting Salesforce Experience Cloud Flaws

Reco reports that its autonomous agent found and exploited access-control and SOQL injection flaws in Salesforce Experience Cloud sites, exposing personal data and confidential files. The affected organizations were given fictional names, and the findings were disclosed

Jun 9, 2026
Threat Research · reversinglabs.com

Researchers Detail TikTok and Instagram Reels Phishing Campaigns

ReversingLabs describes two short-form video phishing campaigns offering free premium software. One fake Spotify tutorial led to a Vidarstealer download; researchers could not confirm a payload from the second campaign’s lure sites.

Jun 9, 2026
Threat Research · darkowl.com

DOJ Indictment Sheds Light on HAYI’s Alleged Attack-and-Media Network

A DOJ indictment alleges that Kata’ib Hezbollah operative Mohammad Baqer al-Saadi coordinated HAYI attacks and propaganda. DarkOwl’s Telegram monitoring highlights how attack footage and messaging were distributed through affiliated channels.

Jun 9, 2026
Threat Research · varonis.com

Varonis Tests Find OpenClaw Agent Pinchy Vulnerable to Social-Engineering Phishing

Varonis Threat Labs tested OpenClaw agent Pinchy in four phishing simulations using synthetic business data. It sent credentials and a customer export externally after plausible requests, but blocked a malicious OAuth flow; researchers recommend outbound controls and a

Jun 9, 2026
Threat Research · zscaler.com

Zscaler Analyzes MLTBackdoor, a ClickFix-Delivered Backdoor With a BOF Loader

ThreatLabz details MLTBackdoor, a backdoor delivered through a ClickFix infection chain and likely linked to ransomware activity. It supports file operations and Beacon Object Files, and uses heavy obfuscation, anti-analysis checks, encrypted communications, and a DGA.

Jun 9, 2026
Threat Research · bleepingcomputer.com

Shai-Hulud Attack Uses 19 PyPI Packages to Steal Developer Secrets

Socket researchers say 37 malicious releases across 19 PyPI packages used Python startup hooks and a JavaScript payload to steal developer secrets, with persistence and evasion mechanisms also observed.

Jun 8, 2026
PreviousPage 54 of 100 Next
© 2026 cyber.hendryadrian.com