cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2395 articles

Threat Research · bleepingcomputer.com

Shai-Hulud Attack Uses 19 PyPI Packages to Steal Developer Secrets

Socket researchers say 37 malicious releases across 19 PyPI packages used Python startup hooks and a JavaScript payload to steal developer secrets, with persistence and evasion mechanisms also observed.

Jun 8, 2026
Threat Research · socket.dev

Mini Shai-Hulud, Miasma and Hades Worms Spread Through Malicious PyPI Wheels

Researchers identified 23 new malicious PyPI artifacts using startup hooks, trojanized native extensions, and staged JavaScript payloads to target developer and CI/CD secrets.

Jun 8, 2026
Threat Research · bleepingcomputer.com

Researchers Detail Unauthenticated Root RCE Chain in UniFi OS Server

Bishop Fox researchers validated a chain of three UniFi OS Server flaws that enables unauthenticated remote code execution and root access. Upgrade to version 5.0.8 or later; a detection script checks vulnerability status but not prior compromise.

Jun 8, 2026
Threat Research · theravenfile.com

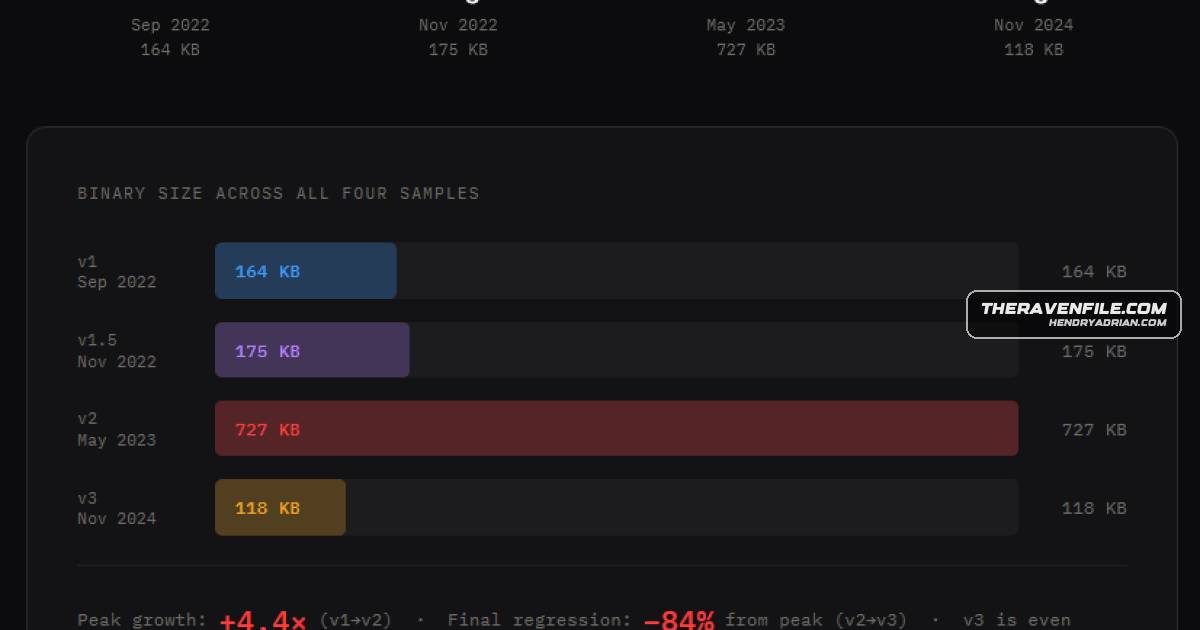
Analysis Tracks Grixba’s Evolution Across Four Play Ransomware Samples

The analysis tracks four Grixba samples from 2022–2024, describing shifts from a .NET infostealer to modular reconnaissance and a smaller staged loader, while WMI/WinRM enumeration and an RDP drop path remain detection opportunities.

Jun 8, 2026
Threat Research · opensourcemalware.com

Supply-Chain Malware Campaigns Target Developers and CI Systems in 2026

OpenSourceMalware analyzes January–May 2026 campaigns targeting developers, software packages, and CI systems, detailing malware delivery, credential theft, propagation, and attribution limits.

Jun 8, 2026
Threat Research · proofpoint.com

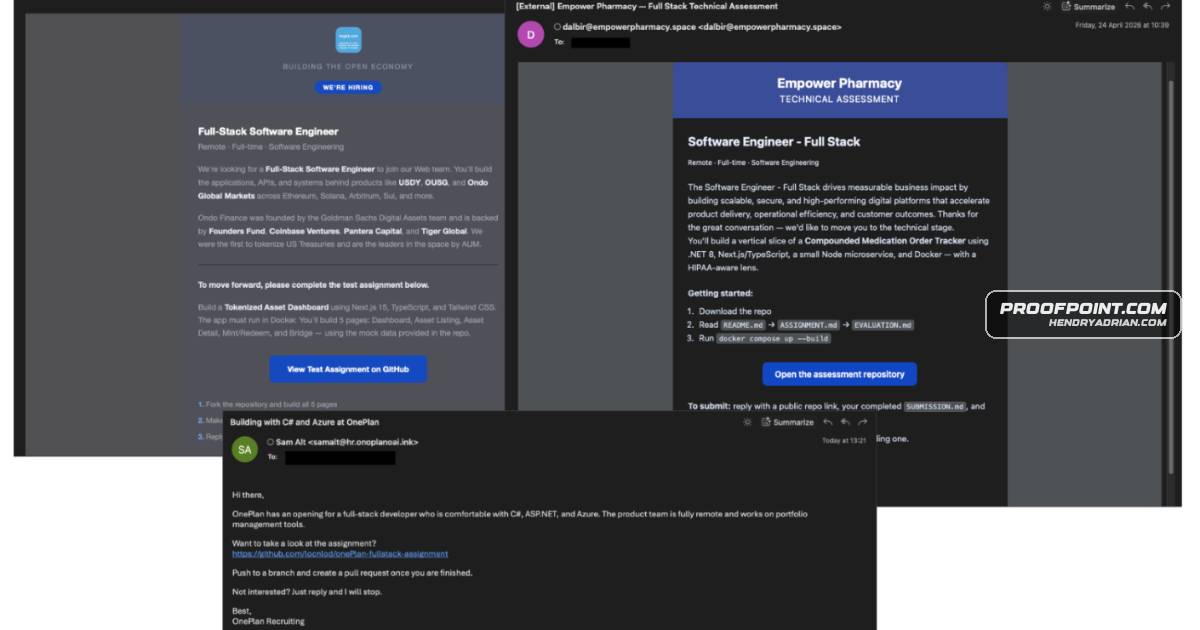
UNK_DeadDrop Uses Malicious IDE Repositories to Steal Developer Credentials and Crypto Wallets

Proofpoint details UNK_DeadDrop phishing targeting developers at nearly 100 organizations. Malicious repositories abuse IDE automation and VSIX extensions to steal credentials and crypto wallets across Windows, macOS, and Linux; attribution to North Korea is assessed as

Jun 8, 2026
Threat Research · stepsecurity.io

Step Security Details Hades Campaign Targeting PyPI Packages and CI Secrets

Step Security reports malicious PyPI packages in the Hades campaign. Their import-time Bun payload scrapes CI runner memory, steals secrets, spreads via SSH and publishing credentials, abuses GitHub Actions, and adds a token-revocation-triggered wiper.

Jun 8, 2026
Threat Research · stepsecurity.io

Ruff CI Checks Block Shai-Hulud Credential-Stealer Injection in GPT-Pilot Repository

StepSecurity reports that ruff CI checks blocked two force-push attempts adding a Shai-Hulud credential stealer to Pythagora’s gpt-pilot repository on June 8, 2026. The payload targeted developer credentials and used GitHub-based C2 and persistence hooks.

Jun 8, 2026
Threat Research · trendmicro.com

Russia-Aligned Groups Exploit Unpatched WinRAR Flaw in Campaigns Against Ukraine

Two Russia-aligned campaigns continued exploiting WinRAR CVE-2025-8088 against Ukrainian organizations through April 2026, delivering an evolved information stealer or espionage tools. The report details their techniques and recommends patching WinRAR and hunting for IО

Jun 8, 2026
Threat Research · bleepingcomputer.com

C0XMO Botnet Exploits DD-WRT Flaw, Spreads Across Devices and Removes Rival Malware

Fortinet researchers say C0XMO, a modular Gafgyt variant, exploits CVE-2021-27137 and weak SSH/Telnet credentials to spread across routers and other devices. It supports 19 DDoS methods and removes competing tools and botnet clients.

Jun 7, 2026
Threat Research · socket.dev

Miasma PyPI Campaign Uses Malicious Wheels to Target Developer Credentials

Socket reports 37 malicious PyPI wheel artifacts across 19 packages that use executable .pth files to launch a Bun-powered JavaScript stealer targeting developer and CI/CD credentials.

Jun 7, 2026
Threat Research · thehackernews.com

Researcher Finds Bright Data SDK Can Turn Consumer Apps Into Web-Scraping Proxies

Include Security and researcher Buchodi say Bright Data’s SDK can route scraping through users’ home connections; iOS traffic may bypass VPNs and run in the background. Smart-TV exposure is suggested by platform and partner evidence, not confirmed for each app.

Jun 6, 2026
Threat Research · dmpdump.github.io

Analysis Finds .NET RAT Using Google Sheets C2 in UAE–India-Themed ISO

A researcher analyzed an ISO containing a .NET dropper and a previously unseen RAT dubbed PulseRAT. The RAT uses Google Sheets for command and control, collects system information, and executes attacker-supplied PowerShell commands.

Jun 6, 2026
Threat Research · bleepingcomputer.com

UNC5221 Used Brickstorm, Plenet, and AgentPSD to Maintain Long-Term Access

Volexity says UNC5221 (VerdantBamboo) accessed a victim’s network and Microsoft 365 environment for at least 18 months, also compromising its MSP and deploying Brickstorm, Plenet, and AgentPSD as backdoors.

Jun 5, 2026
Threat Research · cloud.google.com

Mandiant Details UNC3753 Data-Theft Extortion Campaign Against U.S. Firms

Mandiant describes a Jan–May 2026 UNC3753 campaign against dozens of U.S. legal, professional and financial organizations, using vishing and remote-support tools to steal sensitive files for extortion; it also details possible physical intrusions and defenses.

Jun 5, 2026
Threat Research · thehackernews.com

OP-512 Uses Custom Web Shell Framework to Target IIS Servers

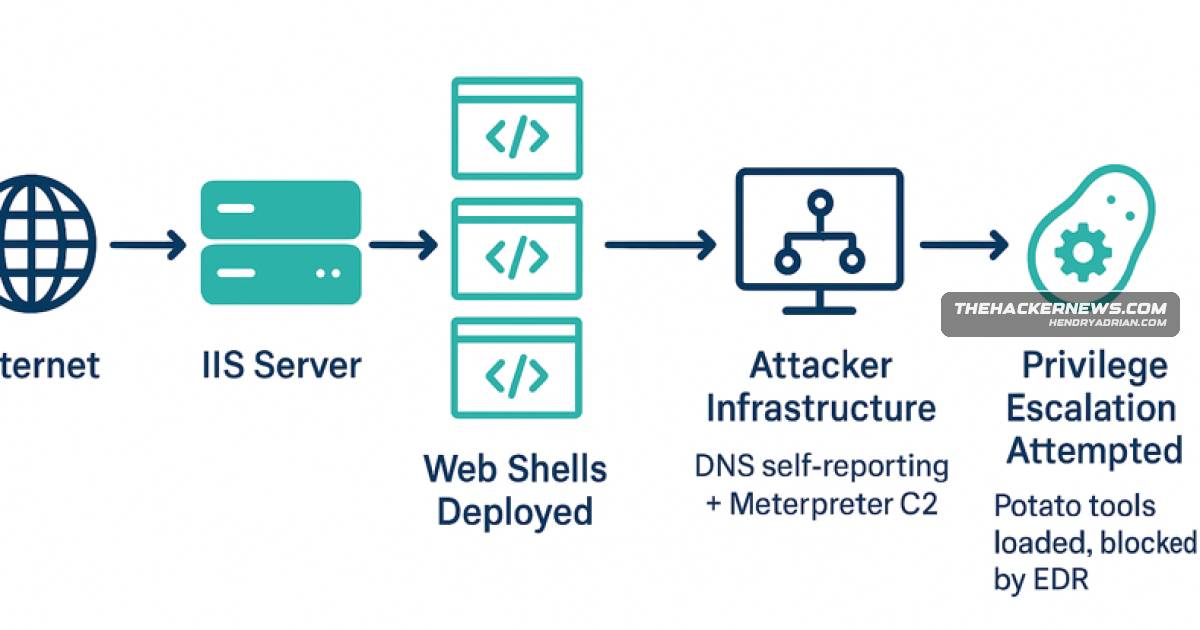
ReliaQuest describes OP-512 targeting a legacy IIS server with a custom three-web-shell framework. The cluster used timestomping and automated reporting; ReliaQuest assesses its China link with moderate to high confidence.

Jun 5, 2026
Threat Research · dti.domaintools.com

ZionSiphon Malware Targets Israeli Water Systems but Has a Critical Activation Flaw

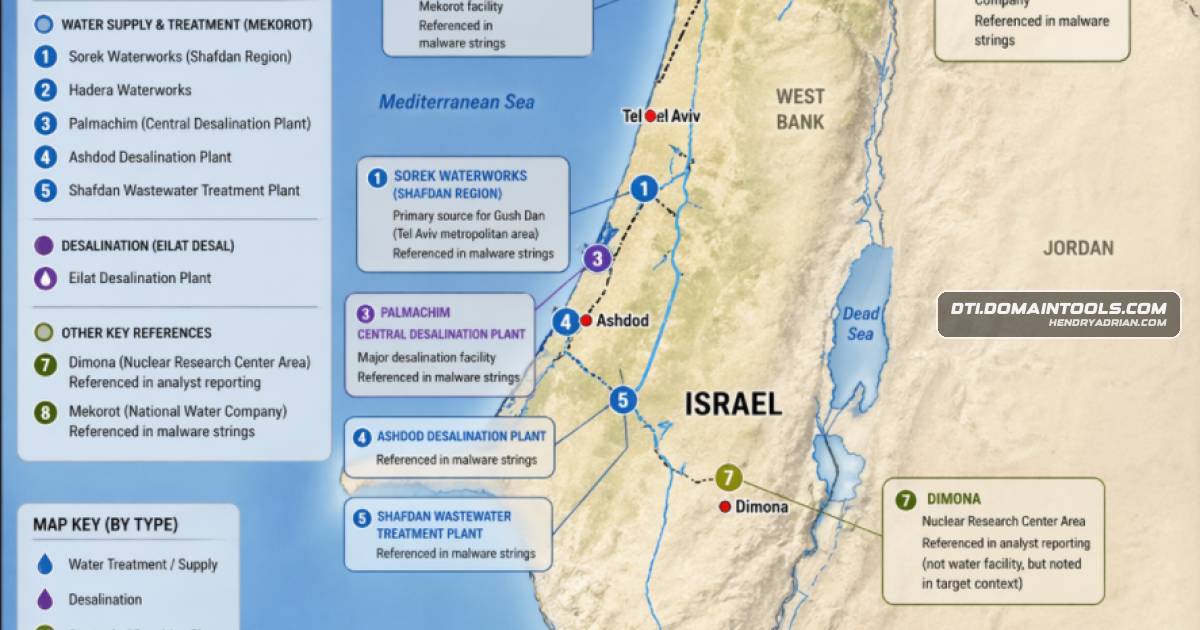
Analysis of ZionSiphon finds a Windows implant with Israeli water-sector targeting and host-level persistence, but a geographic-validation bug prevents its sabotage logic from activating. Attribution remains unconfirmed, and no C2 activity was observed.

Jun 5, 2026
Threat Research · socradar.io

Vect Ransomware’s Encryption Flaw Can Leave Large Files Unrecoverable

A technical profile details Vect’s Windows, Linux and ESXi ransomware, reported links to TeamPCP supply-chain compromises, and a nonce-handling flaw that can leave three-quarters of large files unrecoverable; it also gives defensive guidance.

Jun 5, 2026
Threat Research · sysdig.com

Sysdig Reports LLM-Driven Container Escape and Kubernetes Secret Access

Sysdig TRT says an agentic actor exploited CVE-2026-39987 in a marimo notebook, used a mounted Docker socket to access the host, and replayed a Kubernetes service-account token to read Secrets in the default namespace.

Jun 5, 2026
Threat Research · levelblue.com

ClickFix Campaign Uses Finger Protocol and Python to Deliver CastleLoader and RAT

LevelBlue describes a ClickFix campaign using fake job-site CAPTCHA pages and the Finger protocol to stage CastleLoader and a Python RAT through fileless execution and encrypted C2.

Jun 5, 2026
Threat Research · feeds.fortinet.com

Phishing Campaign Uses JavaScript-Driven PureLogs Variant to Steal Data

FortiGuard Labs details a phishing chain that uses JavaScript, PowerShell and process hollowing to load a fileless PureLogs plugin, which can collect browser, Discord, crypto wallet and application data from Windows systems.

Jun 5, 2026
Threat Research · feeds.fortinet.com

FortiGuard Details C0XMO Gafgyt Botnet’s Cross-Platform Propagation

FortiGuard Labs analyzes C0XMO, a Gafgyt variant that exploits a DD-WRT UPnP flaw and uses a separate Python scanner to target Linux and IoT devices. The report details its persistence, C2, and DDoS capabilities.

Jun 5, 2026
Threat Research · stepsecurity.io

Miasma Worm Uses IDE Hooks in Microsoft Repository Attack; 73 Repositories Disabled

Step Security reports that a June 5 malicious commit added hooks triggering a credential-stealing payload when affected Microsoft repositories were opened in IDEs or AI coding tools. GitHub disabled 73 repositories; Azure/functions-action outages disrupted CI/CD.

Jun 5, 2026
Threat Research · volexity.com

Volexity Details VerdantBamboo Breach Using BRICKSTORM on Edge Appliances

Volexity details an 18-month VerdantBamboo intrusion involving compromised appliances, BRICKSTORM and two other backdoors, stolen credentials, and access through an MSP. Egnyte fixed a privilege escalation issue in Storage Sync v13.13.

Jun 4, 2026
PreviousPage 55 of 100 Next
© 2026 cyber.hendryadrian.com