Entra Agent ID Blueprints Can Expand the Impact of a Compromise Across Identities and Tenants
Summary
Datadog explains how Entra Agent ID blueprints authenticate associated identities and how a compromised blueprint could expose their permissions across multiple identities and tenants.
Key points
- An Entra blueprint can create up to 250 agent identities per tenant, each with its own permissions and optional agent user.
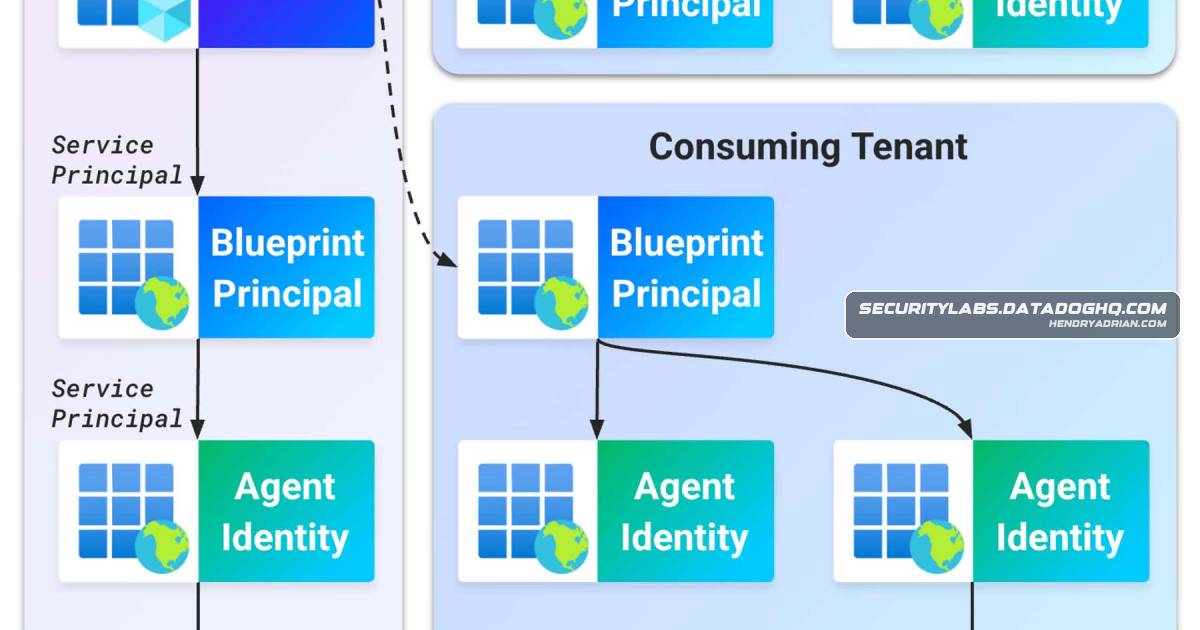
- Blueprint credentials authenticate associated blueprint principals, agent identities, and agent users; credentials cannot be added directly to those child identities.
- A blueprint compromise could enable access to all associated identities and their assigned or inherited permissions.
- Blueprints used across tenants create a cross-tenant risk because the publishing tenant's blueprint credential can authenticate identities in consuming tenants.
- The article describes a two-step token exchange that uses the blueprint credential to obtain a blueprint principal token, then an agent identity token.
- Some privileged roles and permissions remain assignable to agent identities, including roles outside Entra such as Exchange Administrator and Azure DevOps Administrator.
Article Details
- Attack Vectors
- Compromising a blueprint credential can allow an attacker to authenticate as all associated blueprint principals, agent identities, and agent users, including identities in other tenants.
- A blueprint credential can be used in token exchanges to obtain tokens as an agent identity and exercise that identity's assigned or inherited permissions.
- The article describes cross-tenant risk when a third-party blueprint is used to create agent identities in consuming tenants.
- Defensive Notes
- Secure blueprint credentials because the blueprint is the trusted authentication source for all identities associated with it.
- Review permissions assigned to blueprint principals, agent identities, and agent users, including inherited delegated permissions and roles that remain assignable.
- Assess third-party blueprints and the permissions of their associated identities across every tenant where they are used.
Threat Actors
Vendors
Products
Azure AI StudioAgent identities are already in use in Microsoft's own products as the backbone of services like Copilot Studio and Microsoft Foundry (formerly Azure AI Studio).Azure DevOpsfrom assignment, many roles with permissions in applications outside of Entra (Exchange Administrator, Azure DevOps Administrator) and roles with heightened visibility (Global Reader) can still be assigned.Copilot StudioAgent identities are already in use in Microsoft's own products as the backbone of services like Copilot Studio and Microsoft Foundry (formerly Azure AI Studio).Microsoft EntraThis post provides technical background about agent identities in Microsoft Entra.Microsoft Exchange ServerTeams and Exchange access for agent usersMicrosoft FoundryAgent identities are already in use in Microsoft's own products as the backbone of services like Copilot Studio and Microsoft Foundry (formerly Azure AI Studio).Microsoft GraphAgents can also be created using the Microsoft Graph API.TeamsThis account can have a mailbox, join Teams channels, and accomplish other tasks an SP cannot.