
Genians Details APT37 NarwhalRAT Campaign and Infrastructure
Summary
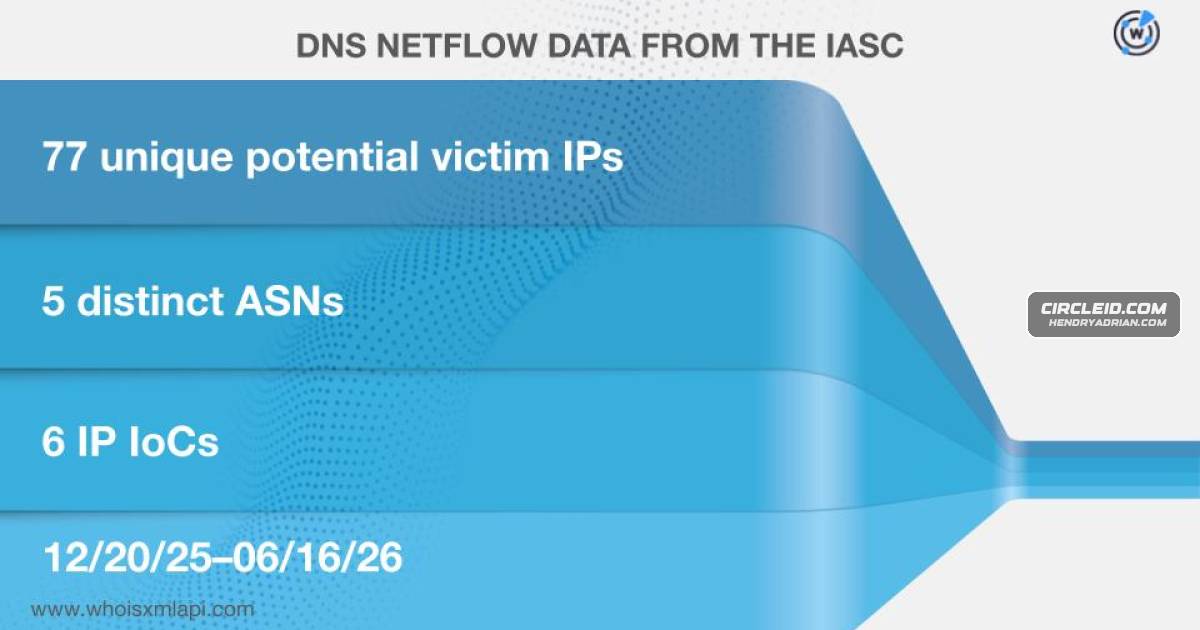
Genians researchers describe an APT37 campaign using NarwhalRAT, likely delivered through spearphishing and malicious LNK files. Their infrastructure analysis identified network indicators and 77 IP addresses potentially associated with victims.
Key points
- Researchers say NarwhalRAT can keylog, capture screens, collect USB data, and execute commands remotely.
- Initial access was believed to involve spearphishing emails impersonating the Microsoft account team or cybersecurity advisories, followed by malicious LNK files and a compiled Python payload.
- The campaign appeared to use a Korean relay server and the pCloud API in a dual command-and-control setup.
- Genians identified 11 network indicators: five domains and six IP addresses. Traffic data showed 77 distinct IP addresses potentially associated with victims communicating with the IP indicators.
- One client IP made 24 DNS queries for novel21[.]co[.]kr between May 21 and 25, 2026.
- The researchers' DNS and WHOIS analysis identified 79 email-connected domains, 792 IP-connected domains, and 17 string-connected domains.
Article Details
- Attack Vectors
- Initial access was believed to involve spearphishing emails impersonating the Microsoft account team and cybersecurity advisories.
- Malicious LNK files induced users to install NarwhalRAT, which was delivered as a compiled Python script.
- The campaign appeared to use a Korean relay server and the pCloud API as a dead-drop resolver for command-and-control operations.
- Defensive Notes
- The article recommends supplementary investigation to corroborate indicators, noting that some entities identified as threats may later prove harmless.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | daehoat[.]com | Identified as a domain IoC associated with the APT37 NarwhalRAT campaign. |
| DOMAIN | novel21[.]co[.]kr | Identified as a domain IoC associated with the APT37 NarwhalRAT campaign; sample traffic showed a client querying it. |
| DOMAIN | webhostingkorea[.]com | Identified as a domain IoC associated with the APT37 NarwhalRAT campaign. |
| IPV4 | 218[.]150[.]78[.]198 | One of the six IP IoCs associated with the campaign; the article links the IP IoCs to Korean relay command-and-control infrastructure. |
| IPV4 | 218[.]150[.]78[.]231 | One of the six IP IoCs associated with the campaign; the article links the IP IoCs to Korean relay command-and-control infrastructure. |
| IPV4 | 61[.]100[.]9[.]206 | One of the six IP IoCs associated with the campaign; the article links the IP IoCs to Korean relay command-and-control infrastructure. |
MITRE ATT&CK
T1025 · Data from Removable MediaNarwhalRAT collected data from USB devices.T1056.001 · KeyloggingNarwhalRAT was used for keylogging to collect input data.T1059.006 · PythonNarwhalRAT was installed as a compiled Python script.T1090 · ProxyThe campaign appeared to route command-and-control traffic through a Korean relay server.T1113 · Screen CaptureNarwhalRAT was used to capture victim screens.T1204.002 · Malicious FileMalicious LNK files induced installation after users opened them.T1566.001 · Spearphishing AttachmentInitial access was believed to use spearphishing emails impersonating the Microsoft account team and cybersecurity advisories.
Threat Actors
Malware
Countries
Chinahas been active since at least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.Indiabeen active since at least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.Japancyber espionage group APT37 has been active since at least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.Kuwaitat least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.NepalAPT37 has been active since at least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.Romaniasince at least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.Russiagroup APT37 has been active since at least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.South Koreastate-sponsored cyber espionage group APT37 has been active since at least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.Vietnamespionage group APT37 has been active since at least 2012 and primarily targeted South Korea, Japan, Vietnam, Russia, Nepal, China, India, Romania, Kuwait, and other Middle East countries.