
Research Uncovers CNCMachineRMS RAT at End of BabaDeda Loader Chain
Summary
An investigation traces a ClickFix infection through signed WinWrapIDE.exe, four decoy DLLs and BabaDeda to CNCMachineRMS, a RAT with shell, file, screenshot, persistence and account-backdoor capabilities.
Key points
- The reported infection chain begins with a ClickFix lure and abuses the legitimately signed IBM SPSS IDE binary WinWrapIDE.exe, followed by four decoy DLLs.
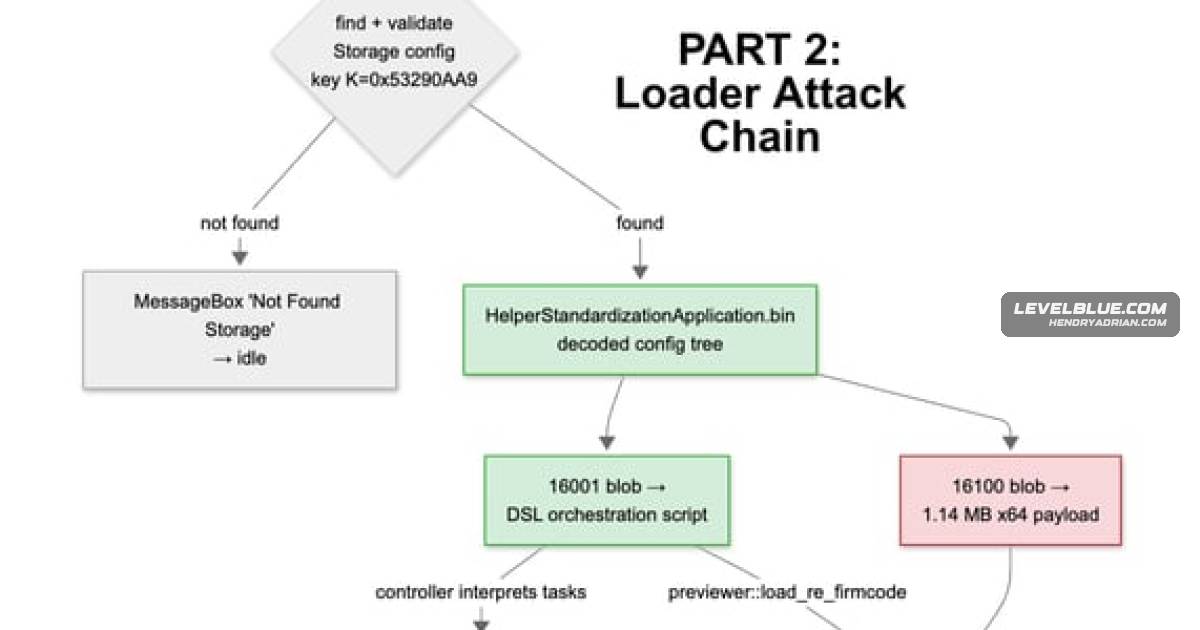
- The final decoy uses EnumTimeFormatsEx to execute shellcode indirectly; the BabaDeda stage depends on an obfuscated configuration file that carries the embedded implant.
- CNCMachineRMS provides interactive shell and file-management functions, screen capture, local-account backdoor creation, seven persistence mechanisms and 20 operator commands.
- The implant uses a custom scripting language and a shared serialized property-tree format for configuration, local state and command-and-control traffic.
- The investigation reports a screenshot on first contact and beaconing every 600 seconds. DNS-over-HTTPS resolution uses dns[.]google, cloudflare-dns[.]com and dns[.]quad9[.]net.
- Reported investigation artifacts include Notepadreleased[.]com over TCP/443, a persistence name of “IBM SPSS WinWrap Basic IDE,” and Windows event IDs 4720 and 4732 associated with local-account activity.
Article Details
- Attack Vectors
- A ClickFix lure initiates the infection chain.
- The chain launches the legitimately signed IBM SPSS IDE binary WinWrapIDE.exe and uses its COM-activated scripting engine to load a dropped DLL.
- Four decoy DLLs load through ordinary import resolution before the final decoy writes shellcode into an executable buffer.
- The final decoy passes the shellcode pointer to EnumTimeFormatsEx, which acts as a callback trampoline for the BabaDeda stage.
- BabaDeda reads the obfuscated HelperStandardizationApplication.bin configuration file, which contains a script and the embedded CNCMachineRMS payload.
- CNCMachineRMS beacons over TCP/443 and can provide interactive shell access, file management, screen capture, local account creation, persistence, and further payload staging.
- Defensive Notes
- The article advises treating an infected host as having had hands-on-keyboard access and investigating follow-on payloads as part of the incident.
- Look for the listed SHA-256 hashes, the Run key or scheduled task named IBM SPSS WinWrap Basic IDE, the specified task and state-file paths, and Windows event IDs 4720 and 4732.
- The implant beacons every 600 seconds and resolves domains through DNS over HTTPS providers, so internal resolver logs may not show its DNS lookups.
- For sandbox detonation, creating C:\Intel disables the malware's VM check in this build.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | notepadreleased[.]com | C2 domain used by CNCMachineRMS for network beaconing over TCP/443. |
| IPV4 | 85[.]158[.]110[.]78 | C2 IP address used by CNCMachineRMS for network beaconing over TCP/443. |
| SHA256 | 0562c588997fa9961d55c6ab1db2656344324bca8db9ea7b64fe309132b2399f | Hash of the legitimately signed WinWrapIDE.exe binary abused in the loader chain. |
| SHA256 | 2922837a8d049bf0b51f0f9b27340a377b27dd1912675e2cd82056db83ec7a19 | Hash of HelperStandardizationApplication.bin, the obfuscated configuration file carrying the script and embedded payload. |
| SHA256 | 3466c3524f13cb3b7c87819e619bdb482ec9034a57bcdbe0240af6a9a530b02a | Hash of ComPDFKit.Viewer.dll, identified as a component in the malicious loader chain. |
| SHA256 | 3b9b86feb3b789dda9cdfe5425ccb7e1feae9fde2cc158ff962991218a98f53f | Hash of model.dat, a file containing the BabaDeda stage. |
| SHA256 | 3d4e7187f74de912f9d52f5ba6a95bd41868348b16583d72957d732c0ed8f0e7 | Hash of ClLoca.dll, identified as a component in the malicious loader chain. |
| SHA256 | 5b71b49bad415643ff3e291ee3ba550e5edfd584eb913859dadb81634450e7e7 | Hash of wwide9.dll, identified as a component in the malicious loader chain. |
| SHA256 | 744b8165b6161cbd1d5ecc423ecfdb8306485afdc80262000ab3c6908881ef9e | Hash of the BabaDeda stage, identified as a memory-only artifact. |
| SHA256 | b804b9dd2726e69fb4f496a6872f90edf9146ad8044c6d3a592040ce1074a5d0 | Hash of Xceed.Wpf.DataGrid.dll, identified as a component in the malicious loader chain. |
| SHA256 | bb81786286be437b3ec6d562055767097c9277054e1d09172caa96376451481c | Hash of the CNCMachineRMS payload, identified as a memory-only artifact. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe configuration and payload are concealed through layers of obfuscation; the implant also builds strings at runtime.T1053.005 · Scheduled TaskThe implant establishes persistence with scheduled tasks, including tasks configured to run at logon as SYSTEM.T1059 · Command and Scripting InterpreterCNCMachineRMS executes behavior through its own custom scripting language stored in the configuration.T1105 · Ingress Tool TransferThe implant has typed commands for pulling down and running additional payloads.T1113 · Screen CaptureCNCMachineRMS takes a screenshot on first contact and provides screen capture functionality.T1136.001 · Local AccountCNCMachineRMS creates local accounts and adds them to privileged groups as a backdoor capability.T1202 · Indirect Command ExecutionThe final decoy uses EnumTimeFormatsEx as a benign callback trampoline to execute the shellcode indirectly.T1547.001 · Registry Run Keys / Startup FolderThe article identifies a Run key named IBM SPSS WinWrap Basic IDE as a persistence artifact.
Malware
BabaDedaA loader chain starting from a ClickFix lure abuses signed IBM SPSS IDE, decoy DLLs, and EnumTimeFormatsEx to deliver the BabaDeda stage and the CNCMachineRMS remote administration implant.CNCMachineRMSA loader chain starting from a ClickFix lure abuses signed IBM SPSS IDE, decoy DLLs, and EnumTimeFormatsEx to deliver the BabaDeda stage and the CNCMachineRMS remote administration implant.