Stealer-Exposed Workstation Reveals Blind Eagle’s Malware and Phishing Operation
Summary
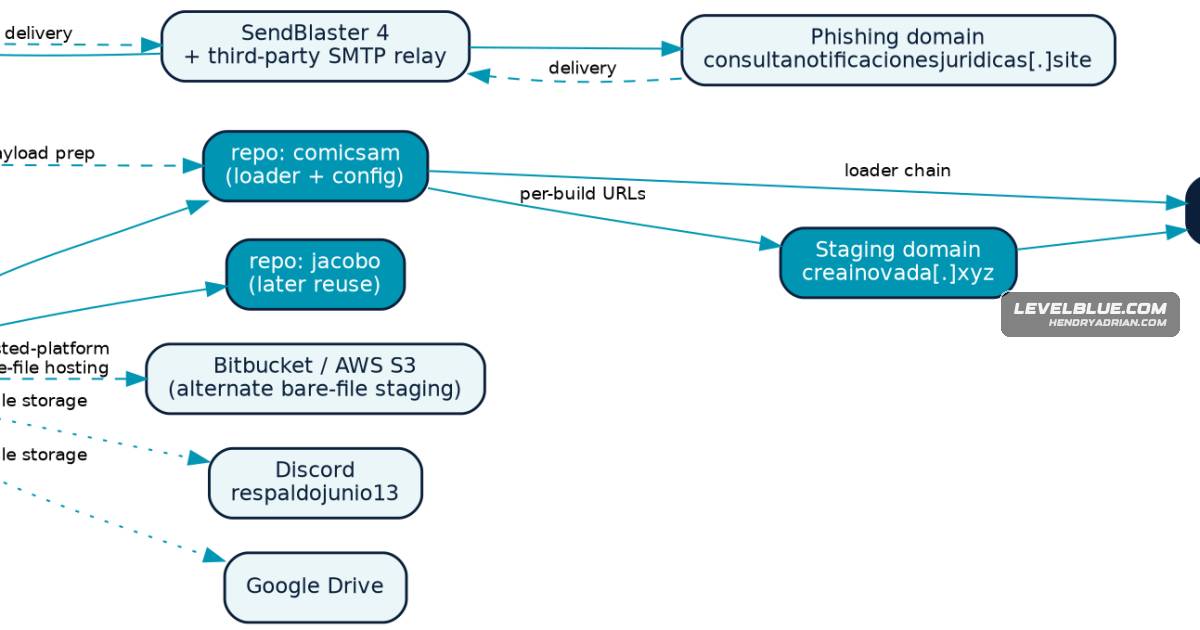
Researchers linked a GitHub loader account to a workstation exposed in an infostealer log, uncovering Blind Eagle RAT builds, phishing materials, delivery infrastructure, and a multi-stage malware execution chain.
Key points
- A plaintext email in GitHub commit metadata led researchers to a stealer-log record; separate compromise intelligence associated the address with an infected device.
- Recovered workstation artifacts included multiple RAT build folders, Colombian government-themed phishing templates, bulk-email software, and records of domains and hosting services.
- The investigation linked GitHub, Bitbucket, AWS S3, and other services to payload staging, alongside DuckDNS command-and-control infrastructure.
- Researchers reconstructed a delivery chain using VBScript, obfuscated PowerShell, and InstallUtil.exe, with an AsyncRAT-associated certificate and C2 domain.
- The operator’s browser history and files showed research into and use of crypters and protectors intended to reduce malware detection.
- The article recommends monitoring password-protected archive lures, suspicious WScript/PowerShell activity, InstallUtil execution, and payloads hosted on trusted platforms.
Article Details
- Attack Vectors
- Phishing emails impersonated Colombian judicial and traffic authorities and delivered password-protected archives.
- A GitHub-hosted loader separated a legitimate AutoIt interpreter from the script logic; other staging locations included Bitbucket, AWS S3, and creainovada[.]xyz.
- Validated samples used an SFX RAR/VBScript and multi-stage PowerShell chain that ultimately executed through InstallUtil.exe.
- The reconstructed chain used DuckDNS infrastructure for RAT command and control.
- Defensive Notes
- Flag password-protected archives when the extraction password is supplied in the email body, and inspect file signatures rather than relying on extensions.
- Monitor for wscript.exe or cscript.exe launching hidden or policy-bypassing PowerShell, and for InstallUtil.exe running outside software deployment.
- Monitor script files written to %ProgramData% and AutoIt3.exe running with an unrelated data file.
- Inspect content hosted on trusted platforms and alert on unusual processes connecting to raw.githubusercontent.com; do not rely on hosting reputation alone.
- For Colombia-based organizations, prioritize detection for judicial-notification, traffic-violation, and DIAN-themed lures.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | consultanotificacionesjuridicas[.]site | Domain associated with the judicial-notification phishing lure. |
| DOMAIN | creainovada[.]xyz | Malware staging domain that the article says hosted per-build payloads and was live during detonation. |
| DOMAIN | simpmit[.]co | Phishing domain used by the traffic-violation lure. |
| HOSTNAME | dccomicrat81[.]duckdns[.]org | AsyncRAT command-and-control hostname. |
| IPV4 | 64[.]89[.]160[.]17 | Prior staging IP identified in the article's indicator table. |
| URL | hxxps[:]//simpmit[.]co/ | Destination linked from the traffic-violation phishing template. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe execution chain used Base64-encoded PowerShell stages; the operator also researched and purchased crypters or protectors.T1036 · MasqueradingPayloads were disguised as PDFs, archives, and legitimate-looking documents.T1059.001 · PowerShellThe samples used multi-stage PowerShell execution.T1059.005 · Visual BasicVBScript stages were delivered through SFX archives and launched with wscript.exe.T1071 · Application Layer ProtocolThe article's ATT&CK alignment reports RAT communications over common web protocols.T1105 · Ingress Tool TransferThe loader chain retrieved payloads and configuration files from GitHub and other staging services.T1218.004 · InstallUtilThe reconstructed chain used InstallUtil.exe as a trusted Windows utility.T1566.001 · Spearphishing AttachmentJudicial-notification and traffic-violation lures delivered password-protected archives.T1566.002 · Spearphishing LinkVictims were directed to actor-controlled phishing domains hosting payloads.T1568.003 · DNS CalculationThe article identifies DuckDNS infrastructure for RAT command and control.T1583.001 · DomainsThe investigation describes operation of phishing and staging domains.T1583.006 · Web ServicesThe article reports use of GitHub, Bitbucket, AWS S3, Discord, Paste.ee, and cloud-hosting platforms for staging or storage.
People
Emmanuel C.Security researcher not affiliated with LevelBlue who contributed additional infrastructure and tooling findings.RodaAlias publicly associated in prior reporting with a crypter developer; the article treats the reference as a supporting clue, not attribution.Roda-ModderPresented alongside Roda as an alias associated with a crypter developer; the article treats the reference as a supporting clue, not attribution.
Threat Actors
Malware
AsyncRATdropper structure, the PowerShell obfuscation pattern, the abuse of InstallUtil.exe, and the AsyncRAT SSL-certificate fingerprint) — the reconstructed execution chain looks like this:DCRatIts name combines “comic,” echoing the comicsam GitHub repository, with “rat,” echoing DcRat, one of the RAT families found in the recovered Rats directory.Remcos RATThe Remcos folder provided another clue.XWorm
Vendors
Amazon Web Services200 OK) at scan time, alongside a Bitbucket-hosted path and a pre-signed AWS S3 URL following the identical “img_test.jpg” naming pattern — the same bare-file-on-a-trusted-CDNBitbucketand serving a payload (creainovada[.]xyz/instructions/Wscript.txt, 200 OK) at scan time, alongside a Bitbucket-hosted path and a pre-signed AWS S3 URL following the identical “img_test.jpg” naming pattern — the sameGitHubwho contributed additional infrastructure and tooling findings based on an analysis of the same GitHub staging account.
Products
Tools
Cassandra ProtectorThe history included research into several such services, including FUD Crypter, MI6 Crypter, PolyCrypt, and Cassandra Protector.FUD CrypterThe history included research into several such services, including FUD Crypter, MI6 Crypter, PolyCrypt, and Cassandra Protector.MI6 CrypterThe history included research into several such services, including FUD Crypter, MI6 Crypter, PolyCrypt, and Cassandra Protector.PolyCryptThe history included research into several such services, including FUD Crypter, MI6 Crypter, PolyCrypt, and Cassandra Protector.