Mirage Kitten Deploys Node.js and JavaScript RATs Through Fake Job Challenges
Summary
Kaspersky details Mirage Kitten’s use of NodeRabbit and PollCat, cross-platform RATs delivered in trojanized coding challenges to targets in the Middle East and Africa.
Key points
- Fake recruiter accounts lure developers with coding assessments hosted in ZIP archives, including projects hosted on Amazon S3.
- NodeRabbit is a Node.js RAT targeting Windows, Linux, and macOS; PollCat is a separate RAT written in obfuscated JavaScript.
- Both malware families establish persistence across operating systems and support remote commands, including file access and process execution.
- A newer NodeRabbit variant can install a fake VS Code extension and inject launchers into Git hooks to persist through developer workflows.
- PollCat can start C2 communications before the user completes the lure’s OTP login; successful authentication can trigger another instance and persistence.
- The operators use Azure-hosted and other domains for C2, with some traffic designed to blend into legitimate network activity.
- Kaspersky attributes the activity to Mirage Kitten and reports telemetry identifying victims in fintech, aviation, and aerospace sectors in Afghanistan, Egypt, and Ethiopia.
Article Details
- Attack Vectors
- Fake recruiter accounts contact targets on job-search platforms and direct them to trojanized coding-challenge archives hosted on Amazon S3.
- Running the challenge project imports a bundled trojanized npm package that launches NodeRabbit.
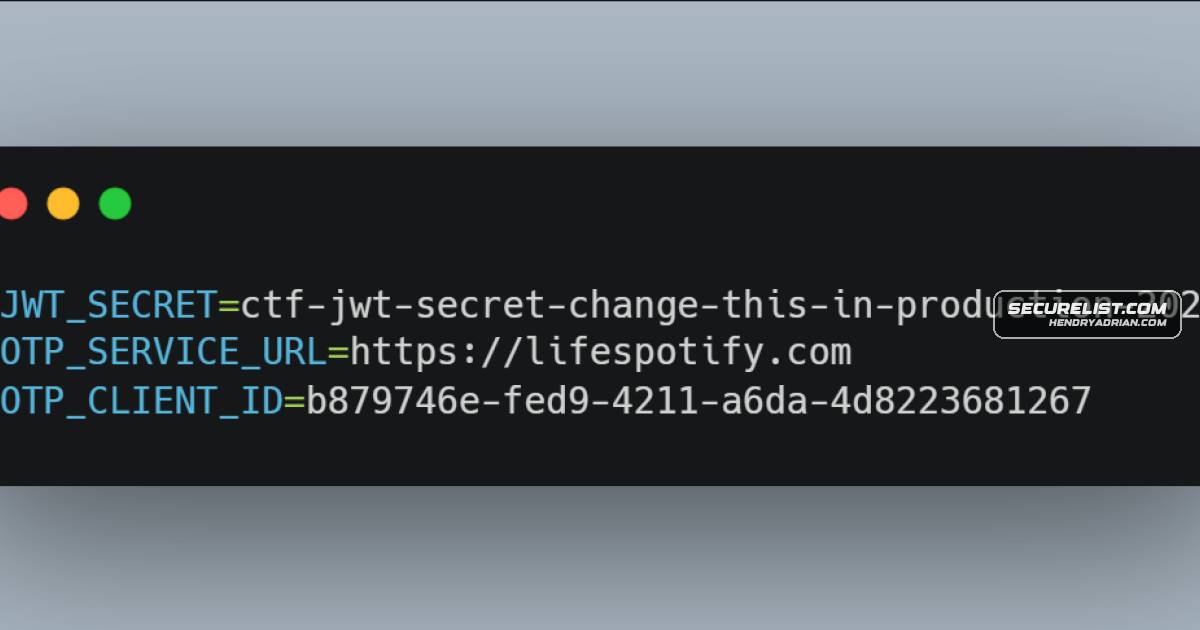
- PollCat is delivered in a trojanized React coding challenge; loading the application starts the malware before OTP authentication.
- PollCat forwards submitted OTP codes to an attacker-managed URL.
- Defensive Notes
- The article says reviewing the challenge source and investigating unfamiliar npm imports could reveal a trojanized project.
- Kaspersky products detect the threat as Trojan.JS.MirageKitten.*.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | aceofspadesmanagement[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | crossdwm[.]azurewebsites[.]net | Domain listed as NodeRabbit campaign infrastructure. |
| DOMAIN | digimediaskill[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | dnshnsdev[.]azurewebsites[.]net | Domain listed as NodeRabbit campaign infrastructure. |
| DOMAIN | gamebarapp[.]azurewebsites[.]net | PollCat C2 domain. |
| DOMAIN | gamebarappinformation[.]azurewebsites[.]net | PollCat C2 domain. |
| DOMAIN | glmediaagency[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | greenyjsgfd[.]azurewebsites[.]net | Domain listed as NodeRabbit campaign infrastructure. |
| DOMAIN | healthcomfsdpower[.]com | NodeRabbit C2 domain. |
| DOMAIN | healthful-hub[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | healthfullyrecipes[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | healthvitalitycare[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | healthyweightplan[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | hecowime-aqdphyd4bbdef6es[.]westeurope-01[.]azurewebsites[.]net | Domain listed as NodeRabbit campaign infrastructure. |
| DOMAIN | helptellerbls[.]azurewebsites[.]net | Domain listed as NodeRabbit campaign infrastructure. |
| DOMAIN | hpjumpsrv[.]azurewebsites[.]net | Domain listed as NodeRabbit campaign infrastructure. |
| DOMAIN | kyrasey-f8hfexa5cqamh7fk[.]westeurope-01[.]azurewebsites[.]net | NodeRabbit C2 domain. |
| DOMAIN | lifespotify[.]com | PollCat C2 domain, also used to receive OTP submissions. |
| DOMAIN | mens-health-online[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | msmanagementgrp[.]com | Domain identified as Mirage Kitten operational infrastructure. |
| DOMAIN | msmanagementgrpmedia[.]com | NodeRabbit infrastructure domain listed in the article. |
| DOMAIN | naturalapplication[.]azurewebsites[.]net | Domain listed as Mirage Kitten campaign infrastructure. |
| DOMAIN | neumedicahealthcare[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | optimumhealthcredit[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | plugplay[.]azurewebsites[.]net | NodeRabbit C2 domain. |
| DOMAIN | refreshhealthandwellness[.]com | Additional infrastructure attributed to Mirage Kitten. |
| DOMAIN | retaildemo[.]azurewebsites[.]net | Domain listed as Mirage Kitten campaign infrastructure. |
| DOMAIN | rgbteller[.]azurewebsites[.]net | NodeRabbit C2 domain listed in the infrastructure table. |
| DOMAIN | sahi-finance[.]com | PollCat C2 domain. |
| DOMAIN | storview[.]azurewebsites[.]net | NodeRabbit infrastructure domain listed in the article. |
| DOMAIN | timedrv[.]azurewebsites[.]net | Domain listed as NodeRabbit campaign infrastructure. |
| DOMAIN | tubitak[.]azurewebsites[.]net | NodeRabbit infrastructure domain listed in the article. |
| DOMAIN | userwellgtfs[.]azurewebsites[.]net | NodeRabbit infrastructure domain listed in the article. |
| DOMAIN | visitfinancedentists[.]com | NodeRabbit C2 domain. |
| DOMAIN | wdisystem[.]azurewebsites[.]net | Domain listed as NodeRabbit campaign infrastructure. |
| DOMAIN | wslmenus[.]azurewebsites[.]net | NodeRabbit infrastructure domain listed in the article. |
| DOMAIN | wslwebui[.]azurewebsites[.]net | NodeRabbit C2 domain. |
| MD5 | 0962f56d7ec69f4f2a0162dcbe22116b | Hash of the trojanized Case-34234.zip archive. |
| MD5 | 1ea83e4e4592b01e4acab63eb867bee5 | Hash of the trojanized Front-Technical-Challenge.zip archive. |
| MD5 | 291ac3abe73c5158e59a437b75d5f0aa | Hash of the trojanized Project-1802.zip archive. |
| MD5 | 366515822d5ac1cc500711ef57a2e32e | Hash of Task-FullStack.zip, listed as a trojanized project archive. |
| MD5 | 795e053a990a1569ffdcb57f48f6d085 | Hash of the trojanized RankChallenge-react-6uJSX3-main.zip archive. |
| MD5 | 810f8e3b88eb05f710c09552941d6f56 | Hash of the Retrograde/MiniFast native DLL backdoor cited in the malware comparison. |
| MD5 | be086789568441d0d7e4679aee51f566 | Hash of the trojanized challenges-17831.zip archive. |
| MD5 | cbaaf0900a13f28e380f49adecec932c | Hash of FrontEnd-Task.zip, listed as a trojanized project archive. |
| MD5 | cf449f1992c2819e62ac44a0b06ac2e7 | Hash of the trojanized fullstack-1536.zip archive. |
| MD5 | de5af16a3757ef700b01dc34d67079ae | Hash of the trojanized webapp76531.zip archive. |
| MD5 | e259c5edf158aac4cfe14f77ddd0b196 | Hash of the trojanized challenges-17832.zip archive. |
| MD5 | e95a4366686e3f786ea3c056fab5b0da | Hash of the trojanized webapp76592.zip archive. |
| URL | hxxps[:]//lifespotify[.]com/api/users/b879746e-fed9-4211-a6da-4d8223681267/otp/validate | Attacker-managed URL that receives OTP codes submitted through the trojanized challenge. |
| URL | hxxps[:]//oracle-challenge[.]s3[.]us-east-1[.]amazonaws[.]com/Front-Technical-Challenge[.]zip | Specific trojanized coding-challenge archive URL identified as payload delivery infrastructure. |
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryNodeRabbit enumerates network adapters, MAC and IP addresses, and DNS settings.T1027 · Obfuscated Files or InformationPollCat is described as obfuscated JavaScript.T1033 · System Owner/User DiscoveryNodeRabbit and PollCat collect usernames and other user or domain information.T1036.005 · Match Legitimate Resource Name or LocationNodeRabbit variant 2 masquerades as Intel Driver & Support Assistant.T1041 · Exfiltration Over C2 ChannelPollCat uploads local files or file chunks to its C2.T1053.003 · CronNodeRabbit and PollCat add Linux cron entries, including @reboot entries, for persistence.T1053.005 · Scheduled TaskNodeRabbit and PollCat create Windows scheduled tasks to relaunch their payloads.T1057 · Process DiscoveryThe malware lists running processes and PollCat collects process names.T1059.005 · Visual BasicNodeRabbit's WSL persistence writes a launcher.vbs file and invokes it through wscript.exe.T1059.007 · JavaScriptNodeRabbit and PollCat execute JavaScript malware using Node.js.T1071.001 · Web ProtocolsThe malware uses HTTP(S) requests to register with C2, poll for commands, and submit results.T1082 · System Information DiscoveryNodeRabbit and PollCat collect host and operating-system information for C2 registration.T1083 · File and Directory DiscoveryNodeRabbit lists and reads files, while PollCat inventories directories and searches development locations.T1105 · Ingress Tool TransferPollCat retrieves files from its C2 through the /vault/<uuid> endpoint and writes them to the victim machine.T1114.001 · Local Email CollectionNodeRabbit variant 3 harvests account addresses from Outlook OST and PST artifacts.T1176 · Software ExtensionsNodeRabbit variant 3 installs a fake VS Code extension that starts the payload.T1204.002 · Malicious FileTargets are pressured to download and run trojanized coding-challenge projects.T1497.001 · System ChecksNodeRabbit variant 2 checks system resources, uptime, usernames, hostnames, and running analysis tools before deciding whether to exit.T1518.001 · Security Software DiscoveryPollCat inventories selected software directories and searches for folders associated with named security-software vendors.T1543.001 · Launch AgentNodeRabbit and PollCat create macOS LaunchAgent configuration files to relaunch their payloads.T1547.001 · Registry Run Keys / Startup FolderNodeRabbit creates Windows Run registry values for persistence.T1566.002 · Spearphishing LinkFake recruiter outreach directs targets to coding challenges through links on job-search platforms.T1573.001 · Symmetric CryptographyNodeRabbit encrypts C2 request data with AES-256-GCM.
Threat Actors
Malware
NodeRabbitWhile monitoring Mirage Kitten activity, we uncovered a previously undocumented malware family that we dubbed NodeRabbit.PollCatDuring the same investigation, we discovered another previously undocumented malware family that we dubbed PollCat.Retrograde/MiniFastStructural similarities with the Retrograde/MiniFast native DLL backdoor (MD5:810F8E3B88EB05F710C09552941D6F56)
Vendors
Products
GitHub CopilotIf a compatible extension directory exists, it creates a fake extension displayed as GitHub Copilot Helper, with the description AI coding assistant helper service and the activation event on StartupFinished.Intel Driver & Support AssistantFor persistence, Variant 2 masquerades as Intel Driver & Support Assistant.Node.jsNodeRabbit is a cross-platform remote access trojan (RAT) built with Node.js.VS CodeCheck selected VS Code, scheduled-task, and Run-key persistence indicators
Countries
AfghanistanWe identified the first sample on a system in Afghanistan.EgyptFurther threat hunting revealed two additional, more advanced, variants: one on a system in Egypt and another on a system in Ethiopia.EthiopiaFurther threat hunting revealed two additional, more advanced, variants: one on a system in Egypt and another on a system in Ethiopia.
Industries
aviation and aerospaceBased on our telemetry, we identified victims in fintech, aviation and aerospace sectors across the Middle East and Africa – specifically, in Egypt, Ethiopia and Afghanistan.fintechBased on our telemetry, we identified victims in fintech, aviation and aerospace sectors across the Middle East and Africa – specifically, in Egypt, Ethiopia and Afghanistan.