
Fake GTA 6 Leak Site Uses Code to Drain Cryptocurrency Wallets
Summary
Malwarebytes analyzed a fake GTA 6 leaked-copy site that profiles connected wallets and can seek transfers or token and NFT approvals across seven blockchains. The article explains the code and advises users to reject suspicious wallet requests.
Key points
- The site disguises a leaked-copy offer with convincing GTA 6 details and loads wallet-draining code; assets can be taken only if a user approves a transaction or permission request.
- An inline Solana script prepares to transfer the wallet balance minus a small amount for transaction fees, rather than charging the advertised price.
- A separate script targets wallets across Ethereum, Polygon, BNB Smart Chain, Avalanche, Arbitrum, Base, and Fantom, and can request immediate transfers or later access to tokens and NFTs.
- The script inventories wallet assets and estimated value, along with the visitor’s IP address and country, and reports the information to the operator.
- A configurable setting named CIS_Protection blocks visitors from ten listed countries; the script can also hinder security analysis by detecting automated browsers and interfering with developer tools.
- The findings suggest the larger drainer may be a hosted or rented service, but the article says it could not identify the product.
- Users should reject transactions moving most of a balance or granting token or NFT permissions; anyone who granted permissions should revoke them, since disconnecting the site alone does not cancel them.
Article Details
- Attack Vectors
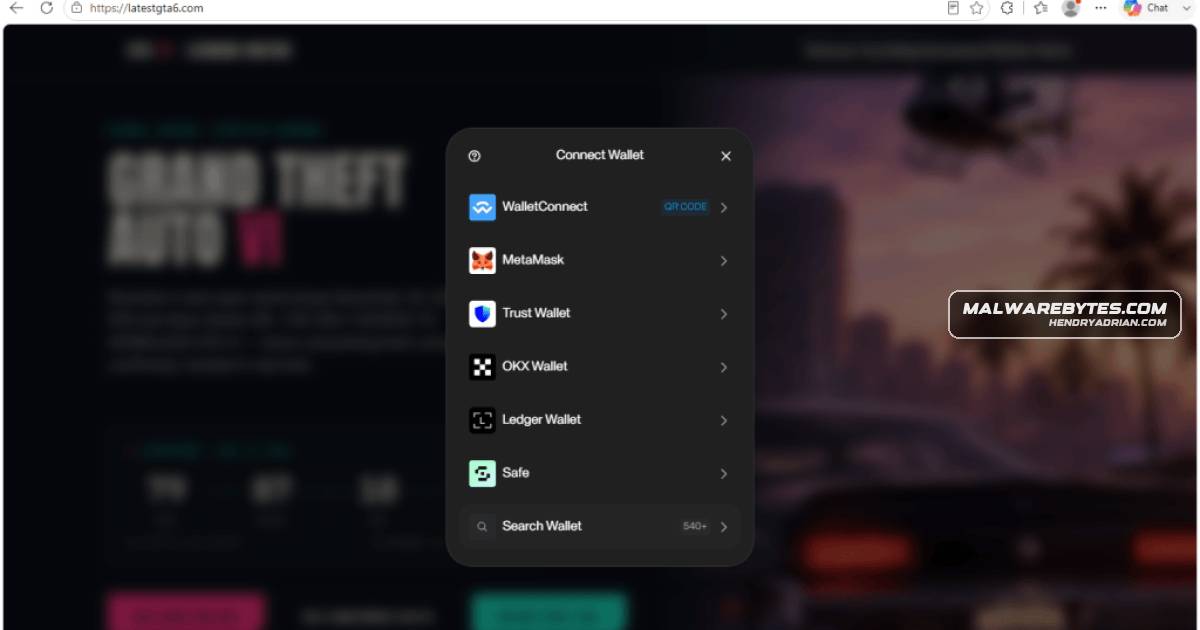
- A fake GTA 6 countdown and leaked-copy page loads wallet-draining code when visitors arrive.
- The page advertises a $50 or 1 SOL purchase, then prompts visitors to connect a cryptocurrency wallet.
- Inline Solana code checks the connected wallet balance and prepares a transfer of nearly all funds, leaving a small amount for transaction fees.
- A separate script inventories wallet assets and can prepare immediate transfers or requests for ongoing access to tokens and NFTs across seven blockchain networks.
- The script sends wallet and visitor details to the operator and uses visitor IP addresses to block access from listed countries.
- The script can detect automated browsers used by security scanners, interfere with developer tools, suppress console messages, and conceal server addresses.
- Defensive Notes
- Review wallet transaction previews carefully; reject transfers of all or nearly all funds and requests for ongoing token or NFT permissions.
- A wallet connection alone does not grant permission to take assets, but any permissions granted through the site should be reviewed and revoked; disconnecting the site does not revoke them.
- Treat offers of leaked, early, or playable GTA 6 copies as unauthorized, and do not connect a cryptocurrency wallet or send cryptocurrency to such sites.
- Check wallet contents across all chains. If funds were taken or a recovery phrase was entered, move remaining assets to a newly created wallet.
- Keep large balances out of wallets used for browsing, and beware of paid recovery offers after theft.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | centrodigestionedellarapina[.]life | Identified as a drainer infrastructure domain used by the scam pages. |
| DOMAIN | dasunerforschtelandamendederwelt[.]sbs | Identified as a drainer infrastructure domain used by the scam pages. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe script conceals server addresses in its code and suppresses browser-console messages to make analysis harder.T1041 · Exfiltration Over C2 ChannelThe script reports wallet holdings, estimated value, visitor IP address, country, and connection count to the operator.T1071.001 · Web ProtocolsThe drainer downloads settings from the operator's server and uses web-based infrastructure for its activity.T1497.001 · System ChecksThe script can detect automated browsers used by security scanners and interfere with analysis.
Products
Countries
Armenia[Countries] Geo-blocked regions associated with CIS_Protection – Armenia, Russia, and 8 more countriesAzerbaijanit uses the visitor’s IP address to identify their country and checks it against a fixed list: Armenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan.Belarusvisitor’s IP address to identify their country and checks it against a fixed list: Armenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan.KazakhstanIP address to identify their country and checks it against a fixed list: Armenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan.Kyrgyzstanto identify their country and checks it against a fixed list: Armenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan.Moldovatheir country and checks it against a fixed list: Armenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan.Russia[Countries] Geo-blocked regions associated with CIS_Protection – Armenia, Russia, and 8 more countriesTajikistanchecks it against a fixed list: Armenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan.Turkmenistana fixed list: Armenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan.UzbekistanArmenia, Azerbaijan, Belarus, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Turkmenistan, and Uzbekistan.