TraderTraitor Backdoors Found on an IT Services Provider’s Mac
Summary
SentinelOne found TraderTraitor’s FLATROOF and ROOFDECK backdoors on an Indian IT services provider’s Mac and identified fake job-interview projects using malicious Terraform provider lock files. The infection route for this victim remains unproven.
Key points
- The victim was an Indian IT services provider with no cryptocurrency ties; telemetry identified one affected Apple Silicon Mac belonging to a DevOps engineer.
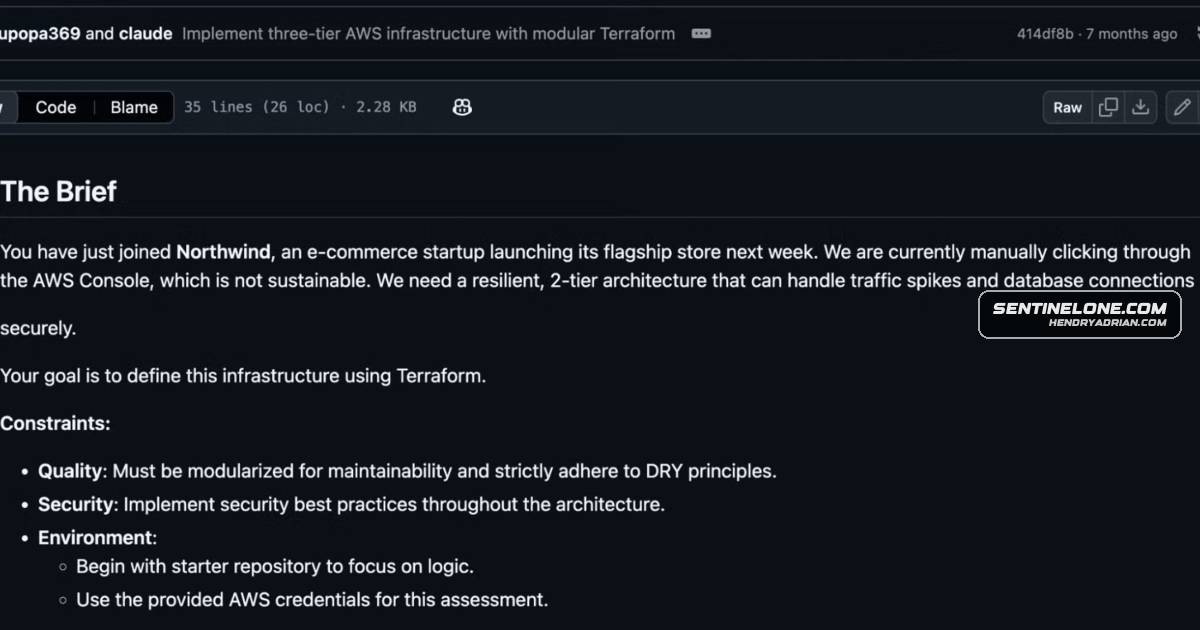
- Researchers found weaponized Terraform lock files in fake coding-project repositories used in job-interview lures. Running `terraform init` with a malicious provider could download and execute attacker-controlled code.
- SentinelOne could not confirm how the backdoors reached this victim’s Mac; both were present by March 18, 2026, and began running on March 29.
- The Rust-based macOS backdoors, FLATROOF and ROOFDECK, can collect system and browser data, command histories, and the login keychain; ROOFDECK also supports remote commands, file transfer, reconnaissance, and persistence.
- A later ROOFDECK version beaconed to a new command-and-control server until June 1; the binary was moved to Trash on June 17.
- SentinelOne recommends monitoring developer endpoints for unsigned binaries and suspicious IDE child processes, and checking Terraform provider sources before running unfamiliar projects.
Article Details
- Attack Vectors
- TraderTraitor used fake job interviews to direct developers to coding projects containing weaponized Terraform lock files.
- The lock files specified custom providers hosted on attacker-controlled, typosquatted registry domains. Running terraform init downloaded and executed the malicious provider modules.
- In the additional victim's case, telemetry established that both backdoors were present by 2026-03-18, but did not establish how they were delivered. Cursor launched them when a development workspace was opened on 2026-03-29.
- According to the LayerZero Labs report, the attackers installed the backdoors after an employee installed a weaponized interview project on a company workstation.
- Defensive Notes
- Prioritize endpoint monitoring for engineers with cloud permissions and source-control access. Investigate unsigned binaries running from home directories, unexpected IDE child processes, and outbound TLS from either.
- Follow up on unsolicited coding repositories and interview assignments; consider restricting external job interviews on corporate workstations.
- Before running a Terraform project with an included .terraform.lock.hcl file, verify its provider registries and investigate package sources, including packages on the official registry.
- Train developers with sensitive access to recognize typosquatted provider domains and the risks of running projects of unknown origin.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | anesthesiaschool[.]com | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| DOMAIN | galaxy-royal[.]online | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| DOMAIN | grenight[.]com | ROOFDECK command-and-control domain used by the later loginwindow binary. |
| DOMAIN | heyhay[.]online | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| DOMAIN | mactroubleshoots[.]pro | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| DOMAIN | registry[.]hashicorp-aws[.]com | Attacker-controlled Terraform provider registry specified by weaponized lock files. |
| DOMAIN | registry[.]hashicorp-aws[.]io | Attacker-controlled Terraform provider registry specified by weaponized lock files. |
| DOMAIN | registry[.]hashicorp-terraform[.]io | Attacker-controlled Terraform provider registry specified by weaponized lock files. |
| DOMAIN | storage[.]hubpage[.]cloud | ROOFDECK command-and-control domain. |
| DOMAIN | technicais[.]sytes[.]net | FLATROOF command-and-control domain. |
| DOMAIN | tinklify[.]com | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| DOMAIN | vaimage[.]com | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | 185-66-91-112[.]cprapid[.]com | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | 213-111-146-132[.]cprapid[.]com | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | app[.]heyhay[.]online | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | dela[.]servehttp[.]com | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | game[.]galaxy-royal[.]online | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | mx01[.]galaxy-royal[.]online | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | ns4[.]galaxy-royal[.]online | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | update[.]heyhay[.]online | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | wss[.]sytes[.]net | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | www[.]anesthesiaschool[.]com | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | www[.]freehealth[.]lat | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | www[.]heyhay[.]online | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | www[.]mactroubleshoots[.]pro | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| HOSTNAME | www[.]tinklify[.]com | Listed among domains associated with the custom certificate's 'ub' user metadata; C2 use was not established. |
| IPV4 | 176[.]97[.]114[.]232 | FLATROOF command-and-control IP associated with technicais.sytes[.]net. |
| IPV4 | 45[.]11[.]59[.]140 | ROOFDECK command-and-control IP associated with storage.hubpage[.]cloud. |
| IPV4 | 85[.]137[.]56[.]10 | Server from which ROOFDECK staged the later loginwindow payload. |
| IPV4 | 85[.]137[.]56[.]245 | ROOFDECK command-and-control IP associated with grenight[.]com. |
| SHA1 | 02df07a173ab03b82a4fb6a08973fff8b1467f28 | FLATROOF backdoor binary identified as SystemUpdate. |
| SHA1 | 4ad92bf92ee614b05c340ce17bef7b6ef5a25e82 | SHA-1 fingerprint of the custom certificate identified for ROOFDECK TLS communication. |
| SHA1 | 5728b11d30586bbfc1d8bd12df1c722a06e767a2 | Stripped ROOFDECK backdoor binary identified as loginwindow. |
| SHA1 | c491d477dbe0ae04e9aed9dbe237144c03f73ec4 | ROOFDECK backdoor binary identified as iSync. |
| SHA256 | 4b2d3e8ccce8920a6d01e7d02b84236545a20e5f754b3eec253f8b416b731daa | SHA-256 fingerprint of the custom certificate identified for ROOFDECK TLS communication. |
| URL | hxxps[:]//github[.]com/chainstacker/Northwind-IAC/blob/930e5be6d34511bedbfb0d762bd08fffe64e9630/aws/us-east-1/prod/northwind/global/vpc/[.]terraform[.]lock[.]hcl | Specific GitHub file identified as a weaponized Terraform lock file. |
| URL | hxxps[:]//github[.]com/exubient0/terraform-candidate-repo/blob/main/[.]terraform[.]lock[.]hcl | Specific GitHub file identified as a weaponized Terraform lock file. |
| URL | hxxps[:]//github[.]com/radupopa369/gtn-candidate-repo/blob/feat/three-tier-infrastructure/live/[.]terraform[.]lock[.]hcl | Specific GitHub file identified as a weaponized Terraform lock file. |
| URL | hxxps[:]//github[.]com/RyanLRay/Technical-Assessments/blob/19af09ebe8b7ad03419677dda515507dd099bc39/README[.]md?plain=1#L175 | Specific coding-challenge README reference to a weaponized Terraform provider domain. |
| URL | hxxps[:]//github[.]com/Steed-LHV/assessment | Coding-challenge repository listed as containing README references to a weaponized Terraform provider domain. |
MITRE ATT&CK
T1036.005 · Match Legitimate Resource Name or LocationBackdoor binaries used names resembling macOS components, including SystemUpdate, iSync, and loginwindow.T1057 · Process DiscoveryFLATROOF's harvesting module collected a running-process snapshot using ps aux; ROOFDECK also supports process listing.T1070.004 · File DeletionAfter the later ROOFDECK version began beaconing, the attackers used it to delete the original FLATROOF and ROOFDECK binaries.T1071.001 · Web ProtocolsROOFDECK polled an HTTPS /app_version endpoint for signed, encrypted commands.T1082 · System Information DiscoveryFLATROOF collected a system hardware and software profile using system_profiler.T1102.001 · Dead Drop ResolverROOFDECK searched Nostr profiles for an operator-controlled website field containing its C2 URL.T1105 · Ingress Tool TransferROOFDECK retrieved a later loginwindow payload from a staging server and supports downloading additional files.T1115 · Clipboard DataROOFDECK supports reading and writing the macOS clipboard, including potentially copied secrets.T1204.002 · Malicious FileFake interview projects induced developers to run Terraform with a weaponized lock file, causing malicious provider modules to execute.T1543.001 · Launch AgentROOFDECK installed a plist in ~/Library/LaunchAgents with RunAtLoad enabled for persistence.T1553.001 · Gatekeeper BypassFLATROOF removed the com.apple.quarantine attribute from ROOFDECK and set its executable bit so it could run without a Gatekeeper prompt.T1567 · Exfiltration Over Web ServiceFLATROOF's harvesting module exfiltrated collected data using a Telegram bot token and file-attachment mechanism.
Threat Actors
Jade SleetExplicitly identified as an alternate name for TraderTraitor.LazarusThe article describes TraderTraitor as a Lazarus subgroup.PUKCHONGExplicitly identified as an alternate name for TraderTraitor.TraderTraitorDescribed as a financially motivated DPRK state-sponsored Lazarus subgroup; the article explicitly gives UNC4899, PUKCHONG, and Jade Sleet as alternate names.UNC4899Explicitly identified as an alternate name for TraderTraitor.
Malware
FLATROOFof this breach, SentinelOne identified an additional victim infected with the macOS backdoors, FLATROOF (aka macOS.Gaslight) and ROOFDECK, which were first observed in the LayerZero Labs attack.LightlessCananother tactic often used in more sophisticated North Korea-aligned toolsets, including Lazarus’ LightlessCan.macOS.Gaslightbreach, SentinelOne identified an additional victim infected with the macOS backdoors, FLATROOF (aka macOS.Gaslight) and ROOFDECK, which were first observed in the LayerZero Labs attack.ROOFDECKidentified an additional victim infected with the macOS backdoors, FLATROOF (aka macOS.Gaslight) and ROOFDECK, which were first observed in the LayerZero Labs attack.
Products
Amazon Web Servicesto collect API keys from the organization and to escalate privileges to expand into the victim’s Amazon Web Services and Google Cloud Platform environments.CursorCursor in active daily use. No malicious activity seen.GitHubWe also identified more weaponized GitHub repositories from the social engineering schemes used to target job seekers in these campaigns.Google Cloud Platformthe organization and to escalate privileges to expand into the victim’s Amazon Web Services and Google Cloud Platform environments.MacBookbased in India and unaffiliated with cryptocurrency. One endpoint was involved: an Apple Silicon MacBook belonging to a DevOps engineer. The engineer ran Terraform and Ansible against AWS, OVH and OpenStack onmacOSFollowing disclosure of the TraderTraitor attack against LayerZero Labs in April 2026, SentinelOne identified an additional victim with the same macOS backdoors.TerraformThis report expands on how Terraform lock files enable the delivery of malware from custom Terraform provider registries controlled by the attackers.
Countries
DPRKThroughout 2026, the financially motivated DPRK state-sponsored Lazarus subgroup TraderTraitor (aka UNC4899, PUKCHONG, Jade Sleet) has engaged in campaigns targeting entities involved in cryptocurrency trading,IndiaThe affected organization is an IT services provider based in India and unaffiliated with cryptocurrency. One endpoint was involved: an Apple Silicon MacBook belonging to a DevOps engineer. The engineer ran Terraform
Industries
cryptocurrency tradingOur analysis explores the mechanics of these backdoors and the expanded targeting against a victim in the IT services sector with no relationship to cryptocurrency trading.IT servicesOur analysis explores the mechanics of these backdoors and the expanded targeting against a victim in the IT services sector with no relationship to cryptocurrency trading.