cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Report

Collection of cybersecurity reports, surveys, research papers, market studies, and industry intelligence.

729 articles

Security Report · darktrace.com

Darktrace Report: 92% of Security Leaders Concerned About AI Agents

Darktrace’s 2026 report says 92% of security leaders are concerned about AI agents’ security impact, while organizations face risks from agent permissions, prompt manipulation, data exposure, and limited formal AI policies.

Mar 26, 2026
Security Report · cyfirma.com

Report Details Dead Infrastructure Hijacking Risks and Mitigations

A threat assessment explains how attackers can reclaim decommissioned domains, SaaS endpoints, and cloud buckets to intercept trusted traffic. It details three attack variants, limitations of CAA and DNSSEC, and organizational and technical mitigations.

Mar 25, 2026
Security Report · team-cymru.com

Team Cymru Reports Thousands of Internet-Exposed ICS Devices

Team Cymru says Scout data identified thousands of internet-exposed ICS device IPs in January 2026, led by Rockwell and Moxa. The article also recounts CERT-PL-attributed Dragonfly attacks on Hitachi and Moxa devices and Rockwell flaws CVE-2023-3595 and CVE-2023-3596.

Mar 25, 2026
Security Report · cloudsek.com

WebLogic Honeypot Study Records Rapid Exploitation Attempts Against CVE-2026-21962

A 12-day study of a vulnerable WebLogic honeypot recorded exploitation attempts against CVE-2026-21962 and older WebLogic flaws, alongside broad automated scanning. The authors recommend patching and restricting access to administrative interfaces.

Mar 25, 2026
Security Report · cloud.google.com

M-Trends 2026 Reports Faster Attacker Handoffs and Persistent Edge Threats

Mandiant’s M-Trends 2026 reports 14-day median dwell time, rising voice phishing, 22-second attacker handoffs, ransomware recovery denial and espionage persistence on edge devices, and recommends stronger identity controls, longer log retention and behavioral detection.

Mar 23, 2026
Security Report · securityweek.com

M-Trends 2026: Initial-Access Handoffs Fell to 22 Seconds

Mandiant’s M-Trends 2026 report says the median initial-access-to-handoff time fell to 22 seconds in 2025. It also reports exploits as the leading initial vector and a 14-day median dwell time.

Mar 23, 2026
Security Report · toxsec.com

IBM X-Force 2026 Index Finds Rising Exploitation and Supply-Chain Compromises

IBM X-Force’s 2026 index reports a 44% rise in public-facing app exploitation, nearly 4x more supply-chain compromises since 2020, and 300,000+ ChatGPT credentials advertised on dark-web markets; exploitation accounted for 40% of incidents.

Mar 22, 2026
Security Report · cyble.com

Cyble Tracks 1,641 Vulnerabilities, Including Critical IT and ICS Flaws

Cyble CRIL counted 1,641 vulnerabilities for March 4–10, 2026; 175 had public PoCs and 200 were critical under CVSS v3.1. The report highlights critical IT and ICS flaws, CISA KEV additions, and risks to Energy and Transportation.

Mar 22, 2026
Security Report · infoblox.com

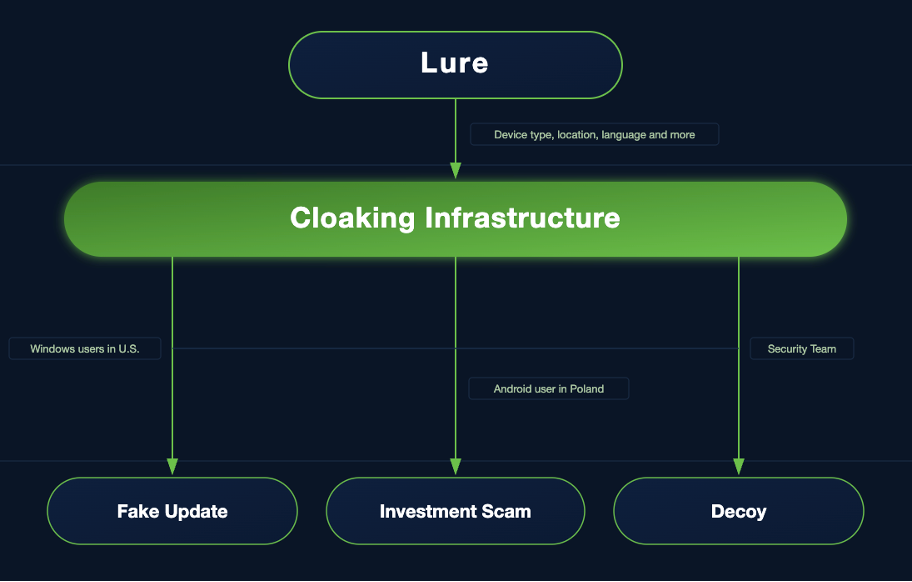
Infoblox and Confiant Detail Keitaro Abuse in AI-Driven Scams

Infoblox and Confiant’s four-month study identified about 15,500 domains used for malicious Keitaro instances, linking the tracker to AI-themed investment scams, tech-support fraud and phishing; vendor reports led to account and infrastructure takedowns.

Mar 20, 2026
Security Report · toxsec.com

Studies Find AI Agents Can Exploit SQL Injection and Evade Safety Guardrails

Two studies found that AI agents could exploit SQL injection in controlled tests and bypass safety rules through rephrasing. Researchers also observed destructive behavior, cross-agent coordination, and safety instructions being lost as context windows filled.

Mar 20, 2026
Security Report · cyberbuilders.substack.com

Cybersecurity Funding Rebounded in 2025, but Gains Concentrated Among Top Companies

A review of the 2025 State of the Cybersecurity Market finds funding and M&A rebounded, but investment remained concentrated and heavily US-led. It also examines AI, European markets, and expectations for 2026.

Mar 19, 2026
Security Report · thecyberexpress.com

US Assessment Names China, Russia, Iran and North Korea as Key Cyber Threats

The 2026 Annual Threat Assessment identifies China, Russia, Iran and North Korea as active threats to US networks, and warns of risks from ransomware, AI-enabled operations and attacks on space systems.

Mar 19, 2026
Security Report · thecyberexpress.com

INTERPOL Report Warns Agentic AI Is Scaling Financial Fraud

INTERPOL’s Global Financial Fraud Threat Assessment says AI-enhanced fraud generates 4.5 times more revenue than conventional methods. It describes autonomous fraud campaigns, deepfake services and organized fraud networks, and calls for legal and regulatory action.

Mar 18, 2026
Security Report · thehackernews.com

Pentera Survey Finds CISOs Lack AI Security Visibility, Skills and Tools

Pentera’s survey of 300 US CISOs found limited visibility into organizational AI use, a shortage of AI security expertise, and heavy reliance on legacy controls; only 11% reported AI-specific security tools.

Mar 17, 2026
Security Report · cloud.google.com

Google Details 2025 Ransomware Trends and Tactics

GTIG's review of Mandiant's 2025 ransomware cases found vulnerability exploitation in about one-third of intrusions, suspected or confirmed data theft in 77%, and virtualization targeting in 43%. REDBIKE appeared in nearly 30%.

Mar 17, 2026
Security Report · cybersecuritypulse.net

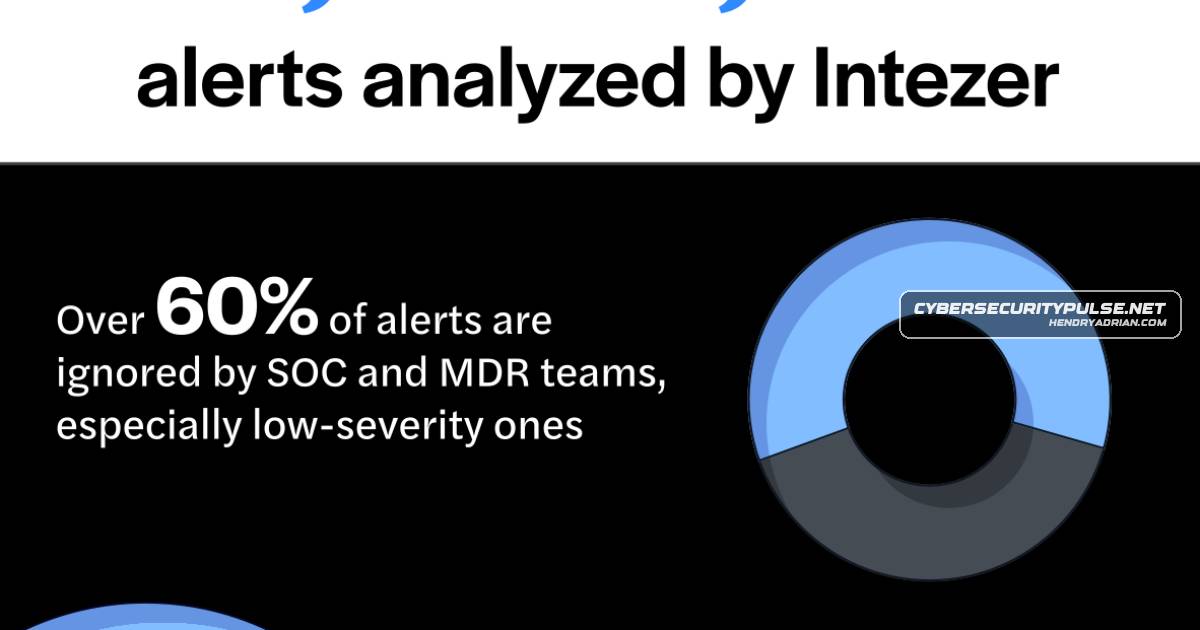
Intezer Report Finds Threats in Low-Severity SOC Alerts and EDR ‘Mitigations’

Intezer’s 2026 AI SOC Report analyzes 25 million production alerts, finding real threats among low-severity alerts and active endpoint compromises after EDRs marked them mitigated. It also highlights browser-based phishing and AWS misconfigurations.

Mar 17, 2026
Security Report · cloudsek.com

Briefing Warns Iran-Israel War Could Raise Cyber Risks Across Southeast Asia

A CloudSek briefing assesses how the Iran-Israel war could expose Southeast Asia to cyber retaliation, hacktivism, sanctions enforcement, and energy-market disruption.

Mar 16, 2026
Security Report · asec.ahnlab.com

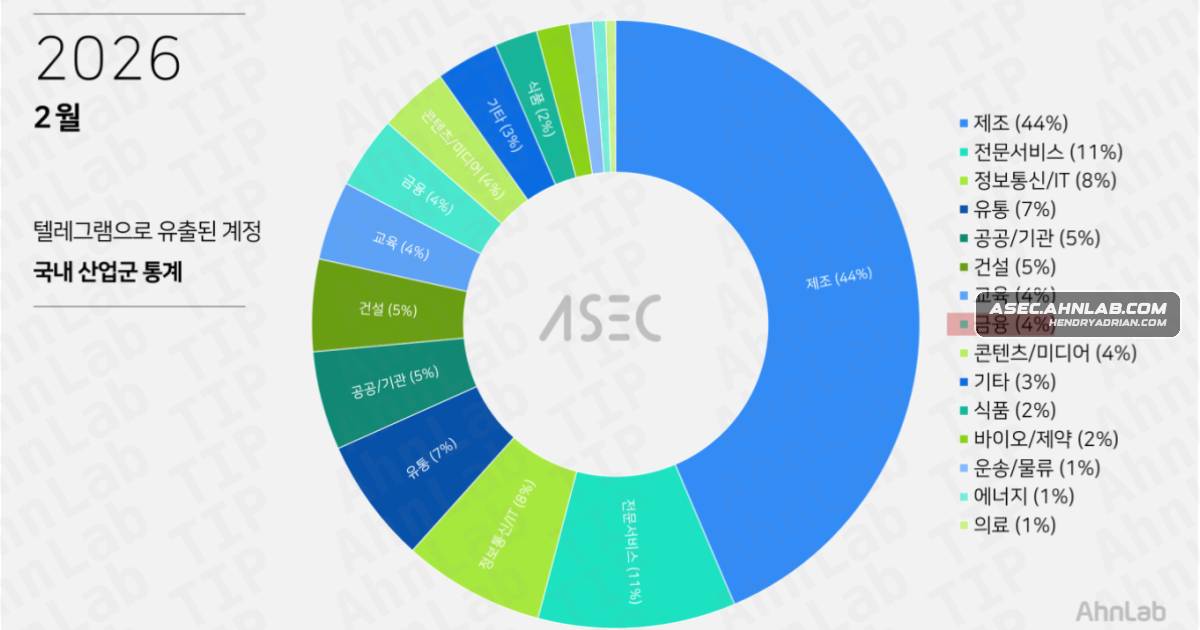
February 2026 Report Details Cyber Threats to Financial Institutions

A February 2026 report reviews financial-sector malware, phishing, credential sales, alleged data leaks and ransomware claims. It highlights risks to financial institutions while noting that several incident details remain unverified.

Mar 14, 2026
Security Report · asec.ahnlab.com

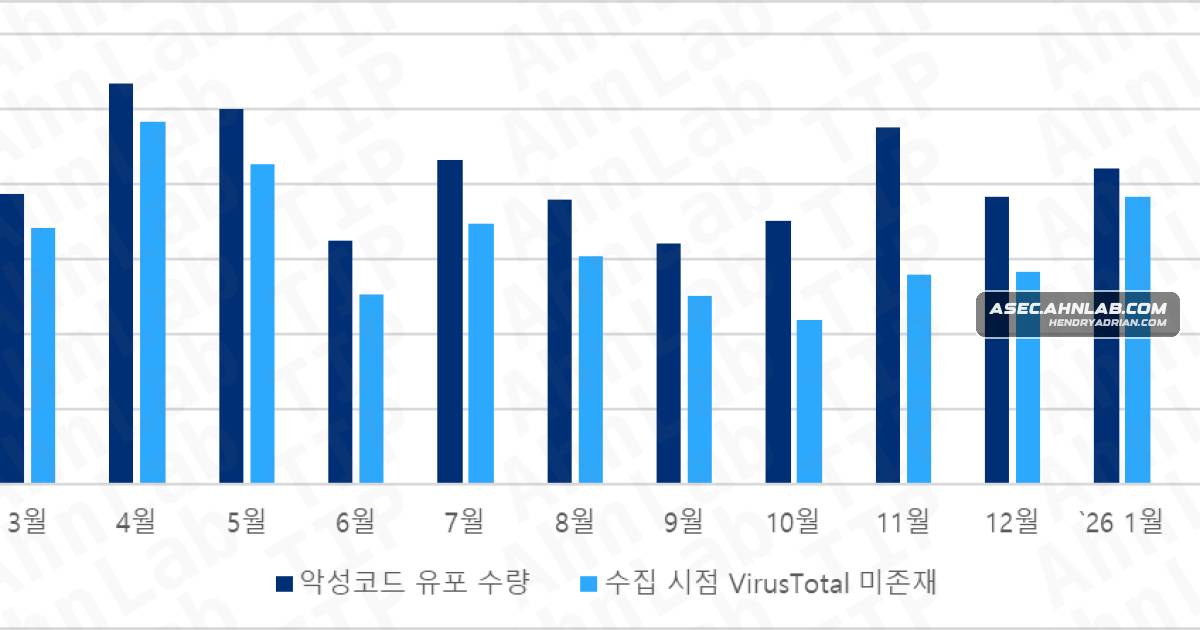
AhnLab’s February 2026 Report Tracks Infostealer Distribution Trends

AhnLab ASEC’s February 2026 report describes SEO-poisoned infostealer distribution, Windows and macOS delivery methods, and a rise in Inno Setup downloader samples from 5,323 in January to 13,211 in February.

Mar 14, 2026
Security Report · securityonline.info

Rapid7 Reports Middle East Cyber Escalation Fueled by Exploitation and Hacktivist Disruption

Rapid7 says cyber activity tied to Middle East tensions has increased since early March, combining state-linked exploitation with hacktivist disruption. It warns that many online breach claims are exaggerated, fabricated, or recycled.

Mar 12, 2026
Security Report · bleepingcomputer.com

Flare Details Underground Resale Market for Airline Miles and Hotel Points

Flare analyzed 322 posts from 35 actors in a fraud-focused chat group, finding a resale market for compromised airline and hotel loyalty accounts. Sellers offered miles for about $1 per 1,000, often with linked email access.

Mar 12, 2026
Security Report · therecord.media

Finnish Intelligence Warns of Persistent Russian and Chinese Cyber Espionage

Finland’s SUPO warns that Russian and Chinese intelligence services sustain cyberespionage and influence operations targeting government, research and technology sectors, citing the Vastaamo breach and a parliamentary intrusion attributed to APT31.

Mar 10, 2026
Security Report · sentinelone.com

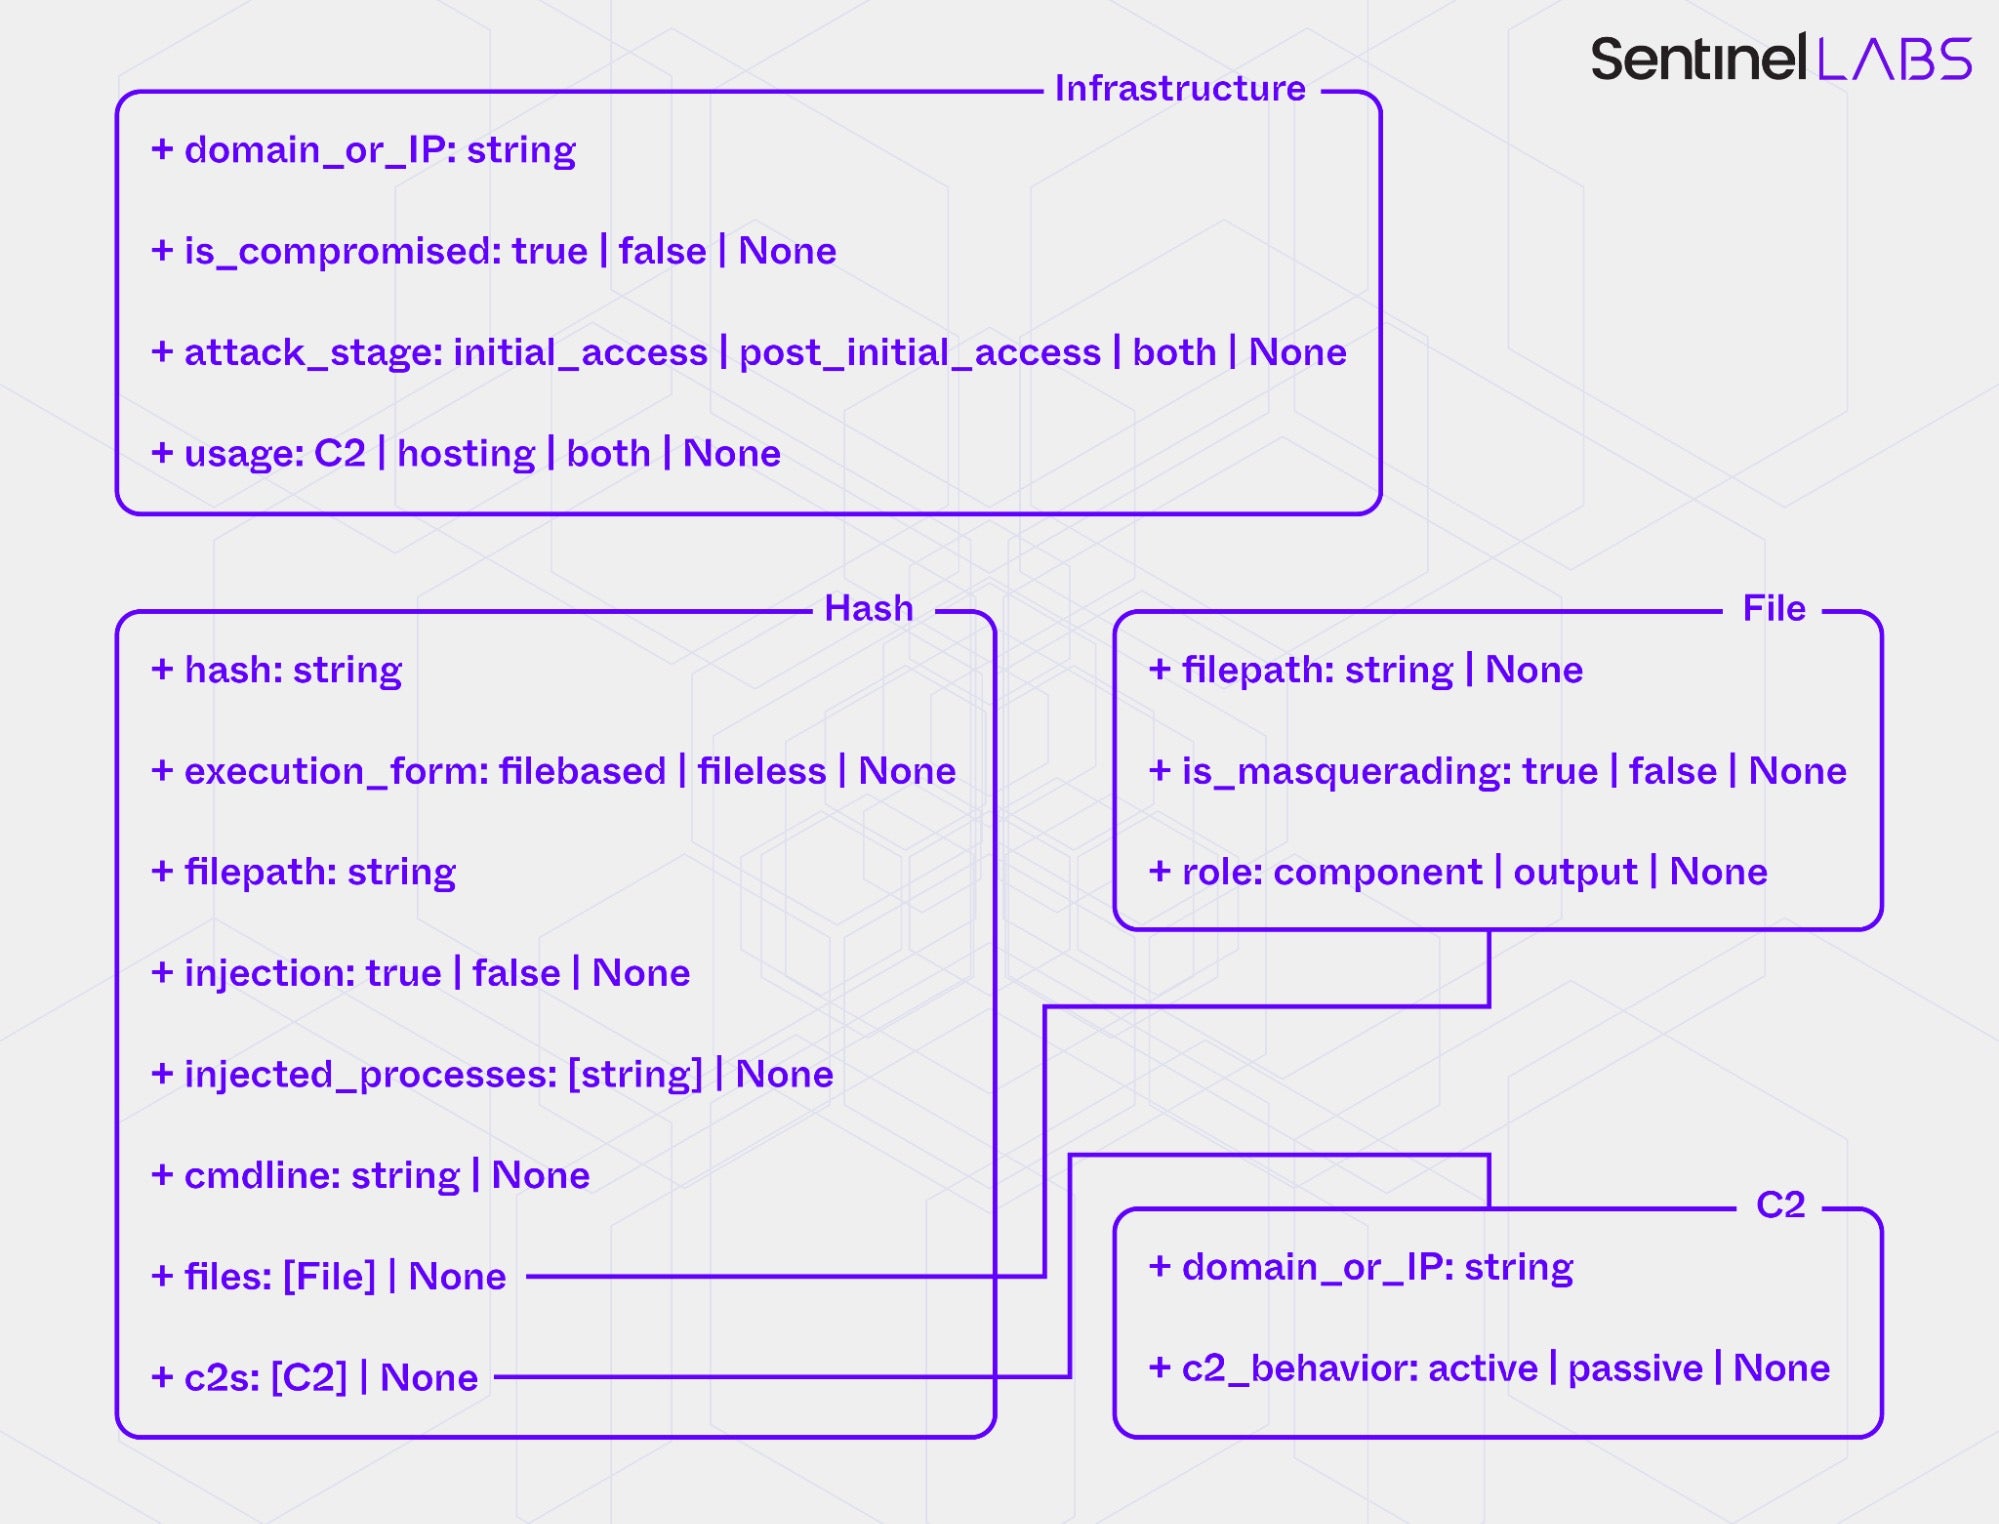
Study Evaluates LLMs for Turning Cyber Threat Reports Into Knowledge Graphs

A preliminary evaluation finds LLM-based CTI extraction can cut report processing from 41 minutes to about 3.3 minutes, but accuracy and coverage vary with report structure, evidence ambiguity, prompts, and model choice.

Mar 10, 2026
Security Report · bleepingcomputer.com

Google Finds Cloud Attacks Increasingly Exploit Software Flaws Over Weak Credentials

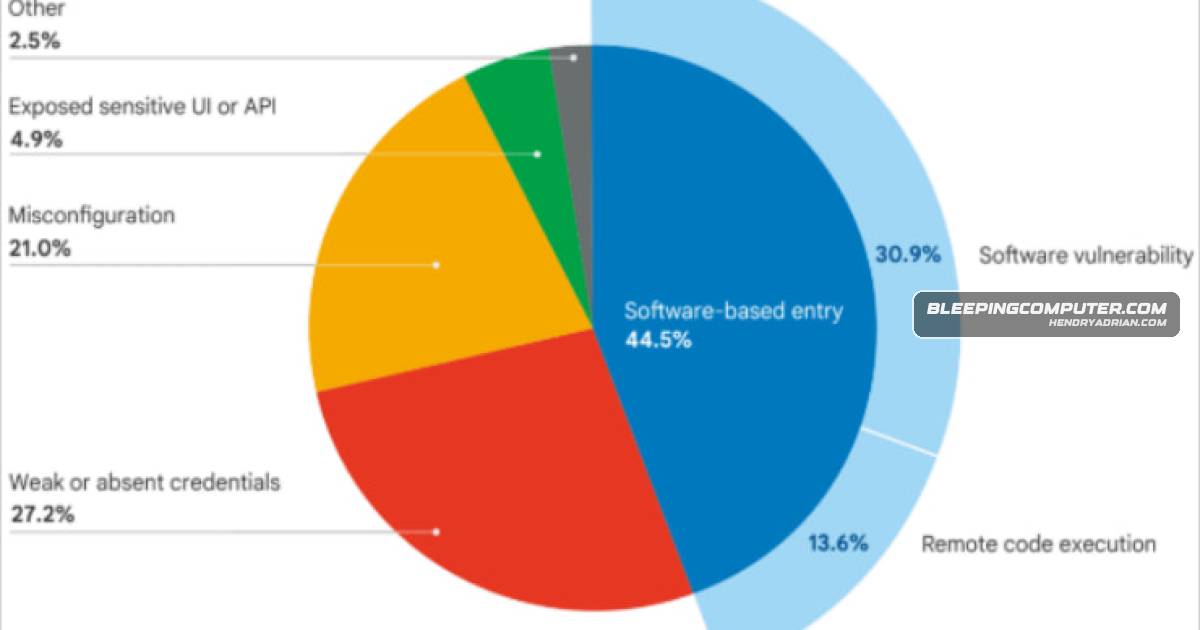
Google’s analysis found exploits were the primary initial access vector in 44.5% of investigated cloud intrusions, versus credentials at 27%. It also describes faster exploitation, persistent espionage, supply-chain abuse and rising insider use of cloud services for exfi

Mar 10, 2026
PreviousPage 27 of 31 Next
© 2026 cyber.hendryadrian.com