
February 2026 Report Details Cyber Threats to Financial Institutions
Summary
A February 2026 report reviews financial-sector malware, phishing, credential sales, alleged data leaks and ransomware claims. It highlights risks to financial institutions while noting that several incident details remain unverified.
Key points
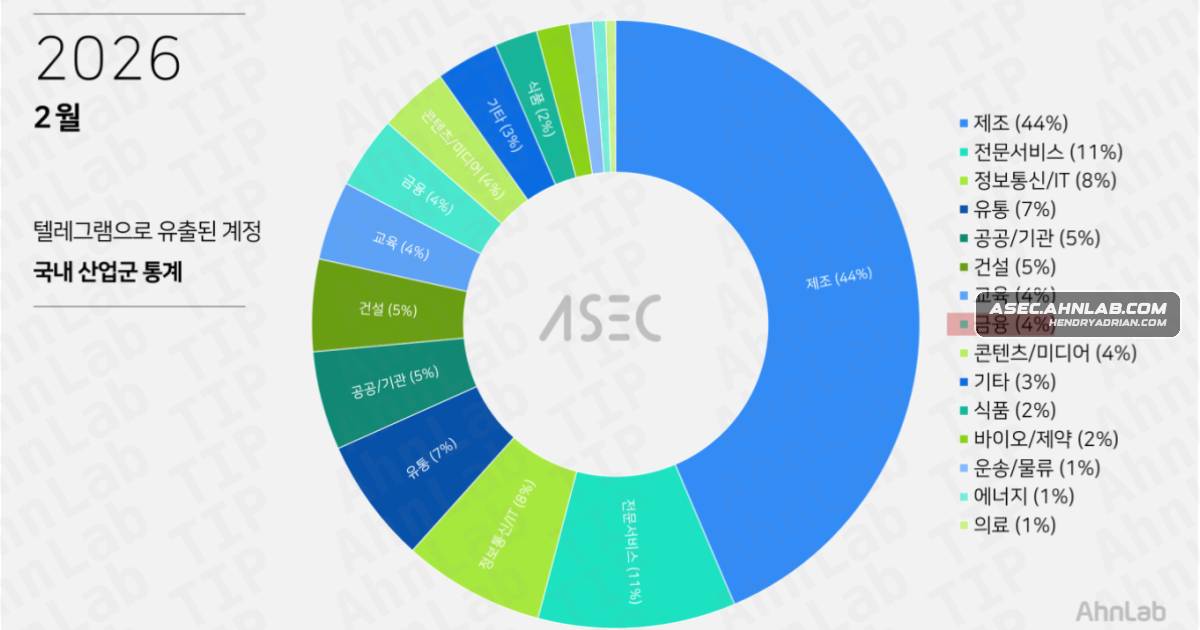
- The report covers malware and phishing targeting financial institutions, includes a Top 10 list of financial-sector malware, and summarizes malware-distribution and Telegram account-leak statistics.
- An actor identified as miyako is reportedly selling firewall and network administrator credentials for Chinese financial institutions on BreachForums; claims of administrator access and potential RCE are not independently established in the article.
- FulcrumSec claims to have stolen more than 19,000 mortgage application documents from the masked company w***s[.]com, including sensitive personal and financial information; the report says the scope and data integrity require further verification.
- The report says ransomware groups CL0P, DragonForce, and Qilin listed financial-sector victims on their leak sites.
- Qilin reportedly listed the masked victim t***e[.]com, but the page later became inaccessible; whether data was released or a ransom was paid remains unclear.
Article Details
- Publisher
- AhnLab ASEC
- Report Period
- February 2026
- Scope
- Cyber threats affecting the South Korean and global financial sectors, including malware, phishing, credential sales, data leaks, and ransomware.
- Key Statistics
- FulcrumSec claimed to have stolen over 19,000 mortgage application documents; the claim and the data's integrity require further verification.
- miyako offered firewall and network administrator access for $300.
- The Qilin victim post became inaccessible approximately 12 hours after it appeared.
- Recommendations
- Verify the actual scope and integrity of the data claimed stolen from W***s.
- Continuously monitor for secondary financial fraud and identity theft related to the claimed mortgage-data exposure.
- Monitor the Qilin post for reactivation and for potential secondary distribution of data.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| MD5 | 02e33ac182acde8ce5c04fb2da933181 | MD5 hash listed among ransomware/victim data samples; the article does not identify the specific file. |
| MD5 | 1f8715d769b879769fa4c65a2c9a9467 | MD5 hash listed among ransomware/victim data samples; the article does not identify the specific file. |
| MD5 | 1ff8f539b8743cf828e9cdcfe279f5c9 | MD5 hash listed among ransomware/victim data samples; the article does not identify the specific file. |
| MD5 | 315558591aa1bc116c75979c1eadae29 | MD5 hash listed among ransomware/victim data samples; the article does not identify the specific file. |
| MD5 | 55f0b29b65d2c29bdaf88c0305a80fc1 | MD5 hash listed among ransomware/victim data samples; the article does not identify the specific file. |
MITRE ATT&CK
T1078 · Valid AccountsThe report associates the sale of firewall and network administrator credentials with the use of valid accounts for access; the credentials and access were described by miyako.T1190 · Exploit Public-Facing ApplicationThe report associates claimed root-level remote code execution and shell access on Linux-based firewall devices with exploitation of a public-facing application.T1486 · Data Encrypted for ImpactThe report lists this technique for ransomware activity involving financial-sector companies, but does not describe encryption of specific victim data.
Threat Actors
Cl0pNamed as a ransomware group that reportedly compromised financial-related companies and publicly listed victims on its leak site.DragonForceNamed as a ransomware group that reportedly compromised financial-related companies and publicly listed victims on its leak site.fulcrumsecClaimed to have stolen over 19,000 mortgage application documents and related materials from W***s. The report says the claim has some credibility based on past activity, but the breach scope and data integrity remain unverified.miyakoIdentified as an Initial Access Broker selling firewall and network administrator credentials for Chinese financial institutions; miyako claimed the access provided administrator privileges and possible RCE and shell access.QilinNamed as a ransomware group that posted T***s as a victim. The post later became inaccessible; the report says a ransom payment is only a possibility and is not supported by clear evidence.