
Infoblox and Confiant Detail Keitaro Abuse in AI-Driven Scams
Summary
Infoblox and Confiant’s four-month study identified about 15,500 domains used for malicious Keitaro instances, linking the tracker to AI-themed investment scams, tech-support fraud and phishing; vendor reports led to account and infrastructure takedowns.
Key points
- The researchers identified about 15,500 domains used for malicious Keitaro instances during the study period; about 9,000 were registered before use.
- Investment scams, especially AI-themed schemes using generated content and deepfakes, were the most common threat category observed.
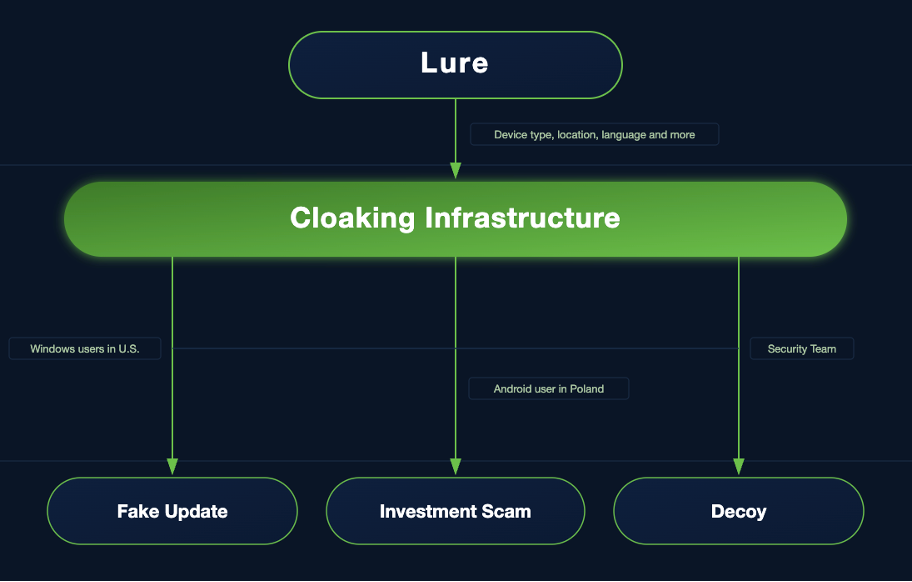
- Operators use Keitaro’s conditional routing and fingerprinting—such as by location, user agent, ASN and referrer—to show lures to selected visitors and benign content to others.
- Campaign traffic came through compromised websites, spam, social media and advertising networks.
- FaiKast used AI-generated deepfake videos impersonating news figures to promote fraudulent investment schemes; researchers observed it entering the ad ecosystem primarily through Bigo Ads.
- FishSteaks campaigns used multi-stage giveaway pages to funnel visitors to phishing sites designed to collect personal and credit card information.
- The researchers say their abuse reports led to more than a dozen threat-actor accounts being canceled and infrastructure being removed; they also verified that TA2726 and other actors used illicit Keitaro copies.
Article Details
- Publisher
- Infoblox
- Report Period
- Four months beginning 2025-10-01; abuse reporting since 2025-08.
- Scope
- Malicious use of Keitaro Tracker, including AI-themed investment scams, tech-support scams, and other fraud campaigns.
- Sample Size
- Thousands of malicious Keitaro instances; approximately 15,500 domains were actively used.
- Key Statistics
- About 9,000 of the approximately 15,500 domains were registered before use.
- Researchers reported more than 100 domains to Keitaro since 2025-08.
- More than a dozen threat-actor accounts were canceled following abuse reports.
- Confiant reports visibility into close to 90 billion ad impressions per month across publisher sites.
- Recommendations
- Continue coordinated abuse reporting and collaboration with Keitaro/Apliteni; the report says this led to account cancellations and infrastructure removals.
- Use observed Keitaro Tracker activity as a signal for identifying related campaign delivery chains.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 5000-giftcardswb[.]ru | FishSteaks giveaway-scam domain observed active throughout October and sporadically in November. |
| DOMAIN | bitget-passive-income[.]com | Domain listed as an additional example used by the same unnamed investment-scam actor as the related domains in its indicator group. |
| DOMAIN | cryptopassive-swiss-switzerland[.]org | Domain identified as used by an unnamed actor running investment scams. |
| DOMAIN | empowerementplan[.]com | WickedWally debt-relief scam domain used with deceptive advertising and a fake chatbot lure. |
| DOMAIN | fin-zen-ai[.]com | Domain identified as used by an unnamed actor's investment scam featuring AI-powered trading platforms. |
| DOMAIN | financialmatcher[.]com | Domain listed among WickedWally debt-relief scam indicators. |
| DOMAIN | funds-treasure[.]com | Domain listed among FaiKast gen-AI broadcast-persona impersonator campaign indicators. |
| DOMAIN | fzclbsmartcbeaa[.]com | Domain listed among FaiKast gen-AI broadcast-persona impersonator campaign indicators. |
| DOMAIN | lumitexaihub[.]com | Domain listed among infrastructure used by the same unnamed actor's AI-themed fake-news investment campaigns. |
| DOMAIN | lumitexchainai[.]com | Domain identified as used in an unnamed actor's AI-themed fake-news investment campaigns. |
| DOMAIN | lumitexsyncai[.]com | Domain listed among infrastructure used by the same unnamed actor's AI-themed fake-news investment campaigns. |
| DOMAIN | northernavenue[.]info | Domain listed among FaiKast gen-AI broadcast-persona impersonator campaign indicators. |
| DOMAIN | star-boostmedia[.]com | Domain used in an unnamed actor's campaign infrastructure, including locale-controlled subdomains for scam landing pages. |
| DOMAIN | synatra-nexus[.]com | Domain listed among infrastructure used by an unnamed actor's AI-powered investment scam. |
| DOMAIN | tmgmaiwwta[.]com | Domain listed among FaiKast gen-AI broadcast-persona impersonator campaign indicators. |
| DOMAIN | tradingideasai[.]com | Domain used by an unnamed investment-scam actor; its subdomains were used to select landing-page languages. |
| DOMAIN | tryhappycards[.]ru | FishSteaks giveaway-scam domain; the campaign used Keitaro and a phishing page to collect personal and credit-card information. |
| DOMAIN | wealthlift[.]click | Domain listed among FaiKast gen-AI broadcast-persona impersonator campaign indicators. |
| DOMAIN | yieldup[.]ch | Domain listed among infrastructure used by an unnamed actor running investment scams. |
| DOMAIN | yourluckycard[.]ru | Domain listed among FishSteaks giveaway-scam indicators. |
| HOSTNAME | au[.]lpa1[.]star-boostmedia[.]com | Campaign hostname listed among domains used for AI-themed fake-news scams. |
| HOSTNAME | pl1[.]tradingideasai[.]com | Locale-controlled hostname used to serve a Polish-language investment-scam landing page. |
MITRE ATT&CK
T1078 · Valid AccountsThe report describes threat actors using valid or illicit Keitaro licenses and accounts; researchers say they verified illicit tracker copies were used.T1102 · Web ServiceThe report describes short-lived tech-support scam payloads hosted on Azure Blob Storage subdomains.T1204 · User ExecutionLures and ad creatives prompt users to click through and engage with scam pages or forms.T1566.002 · Spearphishing LinkThe report maps spam and advertising links that lead victims to fraudulent landing pages to this technique.T1583.001 · DomainsThe report describes registering large numbers of domains algorithmically over time for campaigns.
People
Threat Actors
FaiKastConfiant has tracked FaiKast since May 2025; it uses AI-generated deepfake videos impersonating news anchors and public figures to promote fraudulent investment schemes.FishSteaksA cluster active since at least March 2024 that has recently used Keitaro in giveaway scams and phishing pages designed to collect personal and credit-card information.TA2726The report says TA2726 used Keitaro to deliver traffic to SocGholish for fake-browser-update campaigns and that researchers verified TA2726 used illicit copies of the tracker.WickedWallyA deceptive affiliate-marketing cluster tracked by Confiant since at least 2024; it uses AI-generated deepfake ads and debt-relief lures targeting U.S.-based audiences.
Malware
Vendors
Products
Bigo AdsActors leveraged ad ecosystems (native ads, Facebook Ads, Bigo Ads), spam, social media, and compromised sites to drive traffic into Keitaro cloaking flows and campaigns.Keitaro TrackerKeitaro Tracker is being widely abused by threat actors to perform domain cloaking, conditional traffic routing, and large-scale investment and tech-support scams, often leveraging AI-generated content and deepfakes to
Countries
CanadaEnglish (Canada)FranceGeos targeted include several European countries such as France and the U.K., as well as Canada, Japan, and Kazakhstan.JapanGeos targeted include several European countries such as France and the U.K., as well as Canada, Japan, and Kazakhstan.KazakhstanGeos targeted include several European countries such as France and the U.K., as well as Canada, Japan, and Kazakhstan.United KingdomGeos targeted include several European countries such as France and the U.K., as well as Canada, Japan, and Kazakhstan.United StatesWhile many of the campaigns are global, there are notable threat actors, particularly ones observed by Confiant in the advertising ecosystem that specifically target the United States.