cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Report

Collection of cybersecurity reports, surveys, research papers, market studies, and industry intelligence.

725 articles

Security Report · sysdig.com

Report Finds Gaps in Enterprise AI Agent Oversight and Visibility

A month-long review of AI-agent use at one software company found widespread non-engineer use, many tool calls without human approval, gaps in agent logs versus kernel telemetry, and extensive use of third-party MCP servers.
Nov 4, 2026
Security Report · opensourcemalware.com

Study Finds Reputation Feeds Miss Most Software Supply Chain Threat Indicators

An evaluation of 624 indicators found reputation services often missed software supply chain threats: 62.2% had no VirusTotal detections at ingestion, and 71.3% remained undetected months later.

Nov 3, 2026
Security Report · ncsc.gov.uk

NCSC Assessment Projects AI-Enabled Cyber Threats to the UK Through 2028

An NCSC assessment outlines three possible AI-cyber threat scenarios through 2028, forecasting increased attacks on the UK and its critical infrastructure while emphasizing that the scenarios are plausible possibilities, not predictions.

Nov 3, 2026
Security Report · reliaquest.com

ReliaQuest: New Ransomware Leak-Site Names Drove 93% of Q3 2026 Growth

ReliaQuest found ransomware leak-site listings rose 30% in Q3 2026, with 43 newly observed groups driving 93% of growth. Listings may include rebrands, recycled data, or unsupported claims; defenders should verify claims using internal evidence.

Nov 3, 2026
Security Report · bleepingcomputer.com

Gartner Predicts SOCs Will Have 50% More Engineers Than Analysts by 2028

A sponsored summary of Gartner's 2026 report says AI agents are reducing routine alert work, shifting SOC roles toward case ownership, SOC engineering and exposure management; it outlines related staffing, training and measurement changes.

Nov 3, 2026
Security Report · cyfirma.com

CYFIRMA Says Black October Was a Disclosure Wave, Warns of Faster Supply-Chain Risk

CYFIRMA analyzed 42 incidents from Nov. 2025–Oct. 2026; 34 involved supplier pathways. It assesses October’s cluster as an uncoordinated disclosure wave and says AI speeds flaw discovery and puts AI tooling at risk, recommending stronger supplier controls and resilience

Nov 3, 2026
Security Report · microsoft.com

Microsoft Analysis Finds Exploitation Concentrated in High-Impact Vulnerabilities

Microsoft analyzes 2,056 CVEs exploited in the wild through September 2026, finding exploitation concentrated in takeover vulnerabilities and outpacing patching. It recommends prioritizing high-impact flaws on exposed, critical assets.

Nov 2, 2026
Security Report · security.com

Forrester Survey Finds Midmarket Teams Turning to XDR Amid Tool Sprawl

A Broadcom-commissioned Q3 2026 Forrester Consulting survey of 253 cybersecurity decision-makers found midmarket teams face resource constraints and tool sprawl; 64% had implemented XDR, and most adopters reported or anticipated faster response and better root-cause فهم

Nov 2, 2026
Security Report · thehackernews.com

Cloudflare Reports 18.2 Million Network-Layer DDoS Attacks in Q3 2026

Cloudflare reported 18.2 million network-layer DDoS attacks in Q3 2026, up from 13.2 million in Q2. Short-burst attacks surged 208%, while attacks exceeding 1 Tbps fell 69%.

Oct 31, 2026
Security Report · wiz.io

Survey Finds AI Adoption Outpacing Enterprise Security Visibility

Wiz’s survey of 100 senior IT and security decision-makers found widespread AI deployment but limited inventory and governance: 55% use agentic systems, while only 17% have a comprehensive AI asset inventory. The report recommends stronger visibility and controls.

Oct 30, 2026
Security Report · securityonline.info

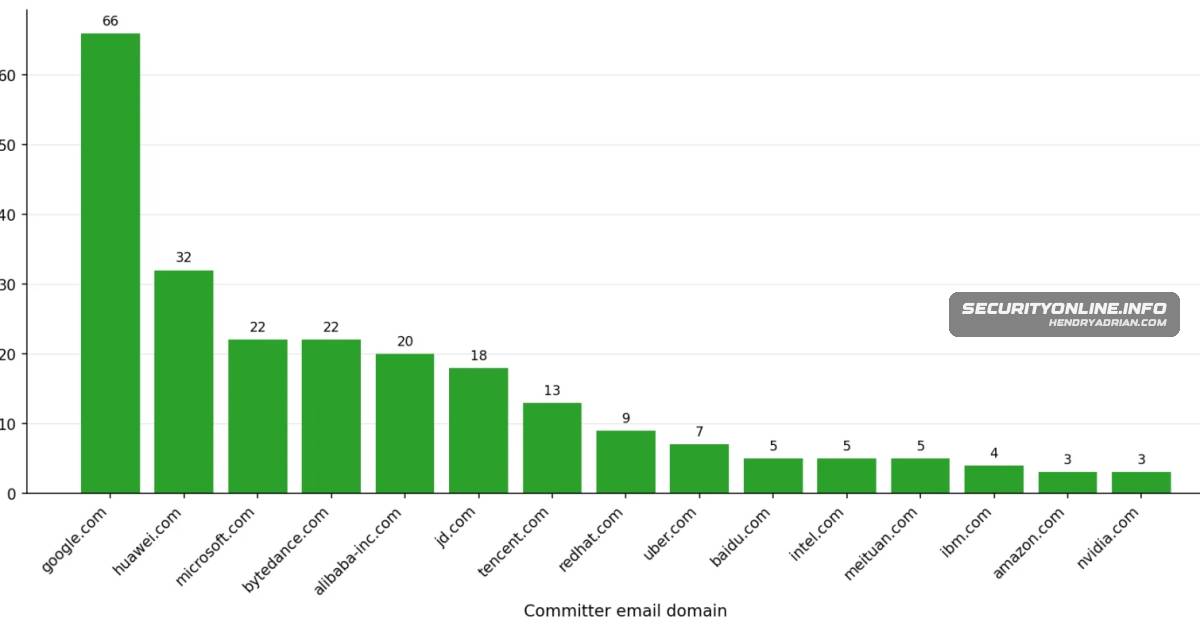
Audit Finds 26,000 Live Credentials in 7.25 Million Gitee Repositories

A researcher reported finding 26,000 unique, valid credentials in 7.25 million public Gitee repositories, validating candidates against provider endpoints. About half dated to commits pushed in 2025; affected providers were notified.

Oct 30, 2026
Security Report · cert-agid.gov.it

CERT-AGID Reports 121 Malicious Campaigns Affecting Italy in One Week

CERT-AGID identified 121 malicious campaigns affecting Italy and shared 965 indicators with accredited organizations. The weekly report also details phishing themes, malware families, and a scan of potentially vulnerable public-administration URLs.

Oct 30, 2026
Security Report · darkreading.com

Intel471 Data Show Italy’s Cyber Threat Patterns Differ Sharply From Global Trends

Intel471 data show Italy disproportionately represented in initial-access listings and ransomware targeting, with vulnerability exploitation and web infrastructure prominent. Researchers suggest patching, technology reuse and SME prevalence may contribute, but no cause

Oct 30, 2026
Security Report · blog.cloudflare.com

Cloudflare’s Q3 2026 DDoS Report Finds More Short Attacks, Fewer Hyper-Volumetric Ones

Cloudflare’s Q3 2026 report records 18.2 million mitigated network-layer DDoS attacks. Short attacks surged, attacks over 1 Tbps fell, and attackers shifted from CLDAP toward DNS amplification and other UDP floods.

Oct 29, 2026
Security Report · thehackernews.com

26,400 Working Cloud and AI Credentials Found in Public Gitee Repositories

A researcher found 26,400 working cloud and AI credentials in 7.25 million public Gitee repositories. Revocation and possible misuse were unconfirmed; the scan also found that two secret scanners detected largely different credentials.

Oct 29, 2026
Security Report · bitsight.com

PHP2Shell Exploitation Remains Unreliable as EOL Hosts Stay Exposed

BitSight says PHP2Shell scanning is widespread but reliable exploitation remains rare. Its analysis found 33.5% of scanned vulnerable hosts patched within a week, versus 6.4% on end-of-life branches, leaving about 11 million hosts without an upstream fix.

Oct 29, 2026
Security Report · acronis.com

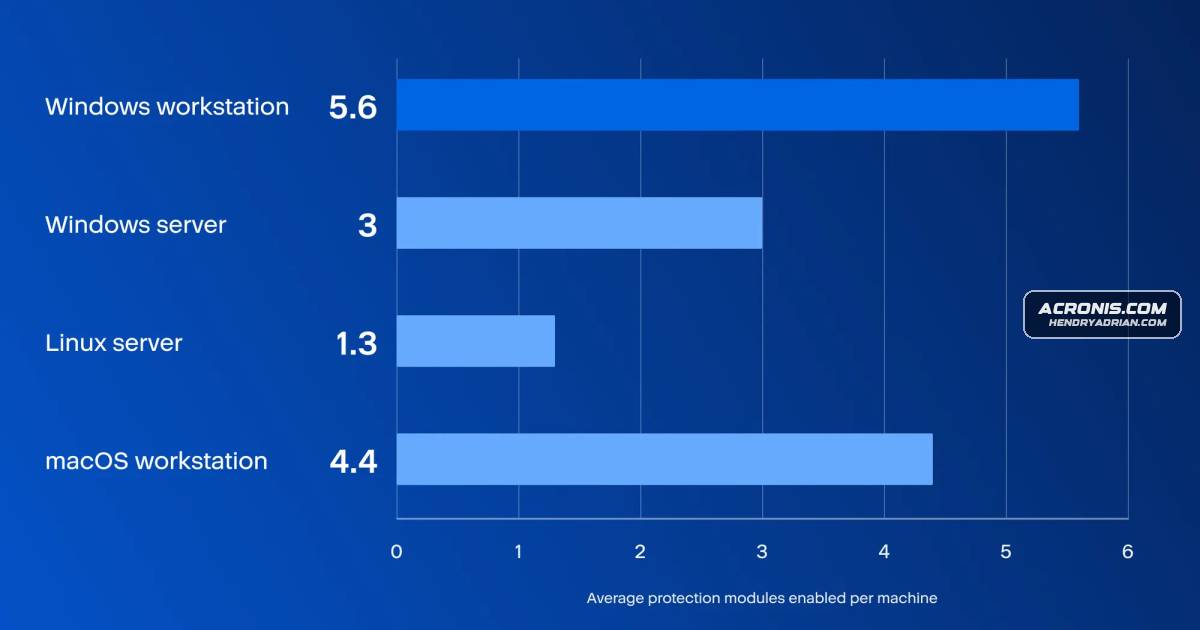
Acronis Report Examines Security Policy Configurations Across 1.6 Million Endpoints

Acronis analyzed configuration records for over 1.6 million endpoints, finding that protection plans vary by provider, region and industry. The report recommends reviewing accumulated plans, documenting settings and tailoring templates to customer needs.

Oct 29, 2026
Security Report · darkreading.com

Intel471 Data Finds Italy an Outlier in Cybercriminal Access Listings

Intel471 data says Italian organizations account for about 7% of initial-access listings and face unusually high vulnerability-based access; the article explores delayed patching, reusable attacks and Italy’s SME-heavy economy as possible explanations.

Oct 29, 2026
Security Report · levelblue.com

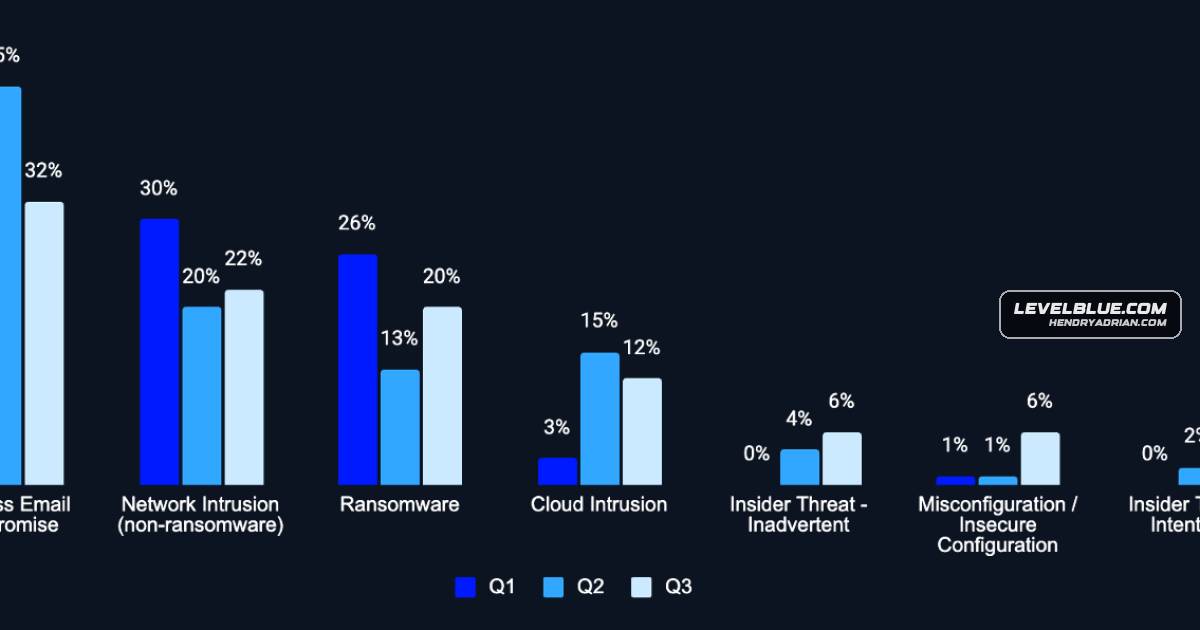
LevelBlue Q3 Briefing: Trusted Access Fueled Data Theft

LevelBlue’s Q3 2026 incident-response briefing reports data exfiltration in 83% of intrusion cases, phishing as the leading initial-access vector (42%), and MFA bypass in 79% of BEC incidents where MFA was enabled.

Oct 28, 2026
Security Report · databreachtoday.com

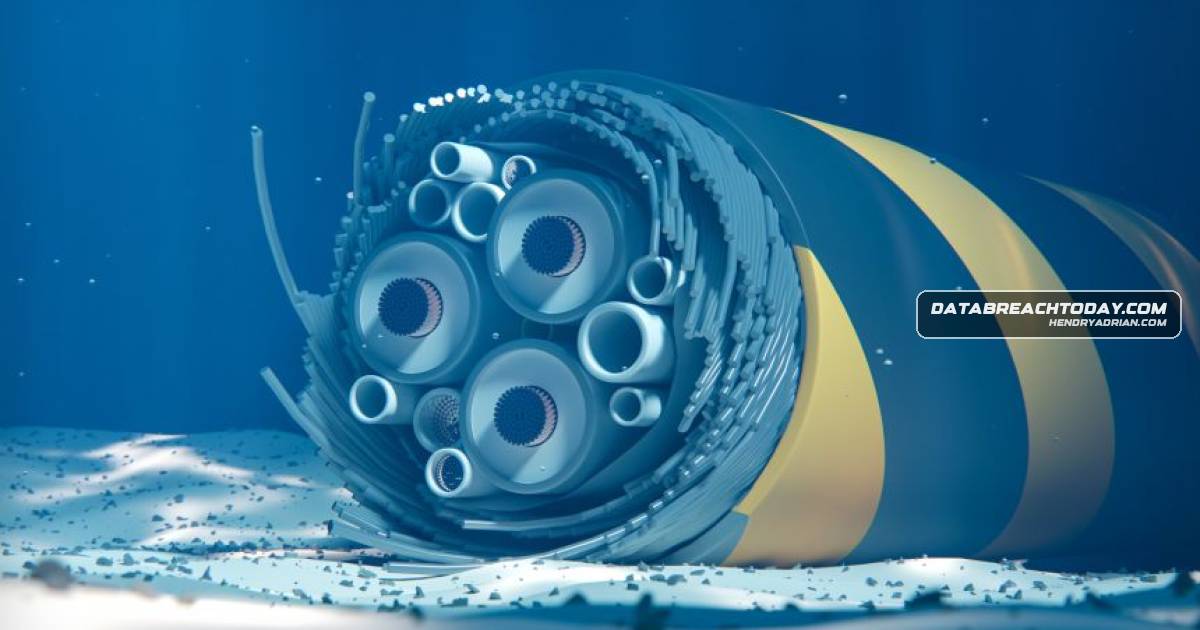
Report Warns of Chinese Threats to Trans-Pacific Subsea Cables

A U.S.-China Economic and Security Review Commission report warns that cable sabotage could strain trans-Pacific capacity and urges acoustic sensors, a lead security agency, more repair ships and outage plans.

Oct 28, 2026
Security Report · welivesecurity.com

ESET Report Tracks APT Activity and AI Use From April to September 2026

ESET’s Q2–Q3 2026 report summarizes selected APT activity from April to September, including regional targeting shifts, a destructive Belarus-aligned operation in Ukraine, supply-chain compromises, and AI use that has not substantially changed APT operations.

Oct 28, 2026
Security Report · crowdstrike.com

CrowdStrike Report Details Rising eCrime and China-Linked Threats to Legal Sector

CrowdStrike’s report on activity observed from Sept. 1, 2025, to Aug. 31, 2026, says eCrime accounted for 82% of threats to legal entities and details rising China-linked espionage, including reported zero-day exploitation.

Oct 28, 2026
Security Report · bleepingcomputer.com

InfraTrust Report Warns of Exploited Flaws in Critical Network Infrastructure

Eclypsium’s October InfraTrust Pulse tracked 2,813 vulnerabilities across 133 advisories. It highlights actively exploited network-appliance flaws and warns that PHP2Shell vulnerabilities may affect embedded management interfaces awaiting vendor firmware updates.

Oct 28, 2026
Security Report · asec.ahnlab.com

AhnLab’s September 2026 Infostealer Report Details Distribution and Lzveil Behavior

AhnLab ASEC’s September 2026 report draws on detection logs and collected samples to describe infostealer distribution, disguises, and targets. It details Lzveil’s data collection and command-and-control behavior, plus email delivery of DarkCloud and AgentTesla.

Oct 27, 2026
PreviousPage 2 of 31 Next
© 2026 cyber.hendryadrian.com