cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Report

Collection of cybersecurity reports, surveys, research papers, market studies, and industry intelligence.

725 articles

Security Report · arcticwolf.com

Arctic Wolf Report Says Agentic AI Resolves 60% of Security Investigations

Arctic Wolf’s 2026 report, based on data from more than 11,000 organizations in over 100 countries, says agentic AI autonomously resolves 60% of investigations; AI-human collaboration handles 38%, while human-only investigations fell to 2%.
Oct 27, 2026
Security Report · socradar.io

Australia’s 2025-26 Cyber Threat Report Records a 20% Rise in Incidents

Australia’s 2025-26 report says ASD’s ACSC handled 1,524 incidents, up 20%. Extensive compromises rose despite broadly stable ransomware volume; phishing, compromised accounts and unpatched systems remained major pressures.

Oct 27, 2026
Security Report · malwarebytes.com

Survey Finds Widespread Concern About AI-Generated Intimate Abuse and Online Deception

A March 2026 survey of 1,500 people across five countries found widespread concern about AI-generated intimate images, impersonation and online deception, alongside use of chatbots for emotional support and relationship advice.

Oct 27, 2026
Security Report · hornetsecurity.com

Hornetsecurity Survey Finds Ransomware Incidence Fell, but Confidence in Defenses Remains Low

Hornetsecurity’s 2027 survey of 400 IT and cybersecurity experts found 18% of organizations reported ransomware, down from 24%; 45% lacked confidence in their defenses. Phishing was the leading reported vector, while just 9% felt staff could reliably spot AI-generated l

Oct 27, 2026
Security Report · databreachtoday.com

NIST Recommends Phased, Hybrid Approach to Post-Quantum Migration

NIST’s guidance outlines a phased move to post-quantum cryptography, including priority use cases, transition timelines and hybrid approaches. It says hybrid measures can reduce single-algorithm risk but add implementation complexity and should generally be temporary.

Oct 27, 2026
Security Report · cyfirma.com

CYFIRMA Says Identity and Infrastructure Telemetry Are Reshaping Incident Investigations

CYFIRMA’s Threat Horizon update says investigations increasingly rely on identity, cloud and infrastructure telemetry. It reports rising malware-free detections and telemetry gaps, and urges defenders to retain logs beyond default windows.

Oct 27, 2026
Security Report · securityonline.info

Study Finds Smart TV ACR Opt-Out Failures and 57 Million Viewing Records Exposed

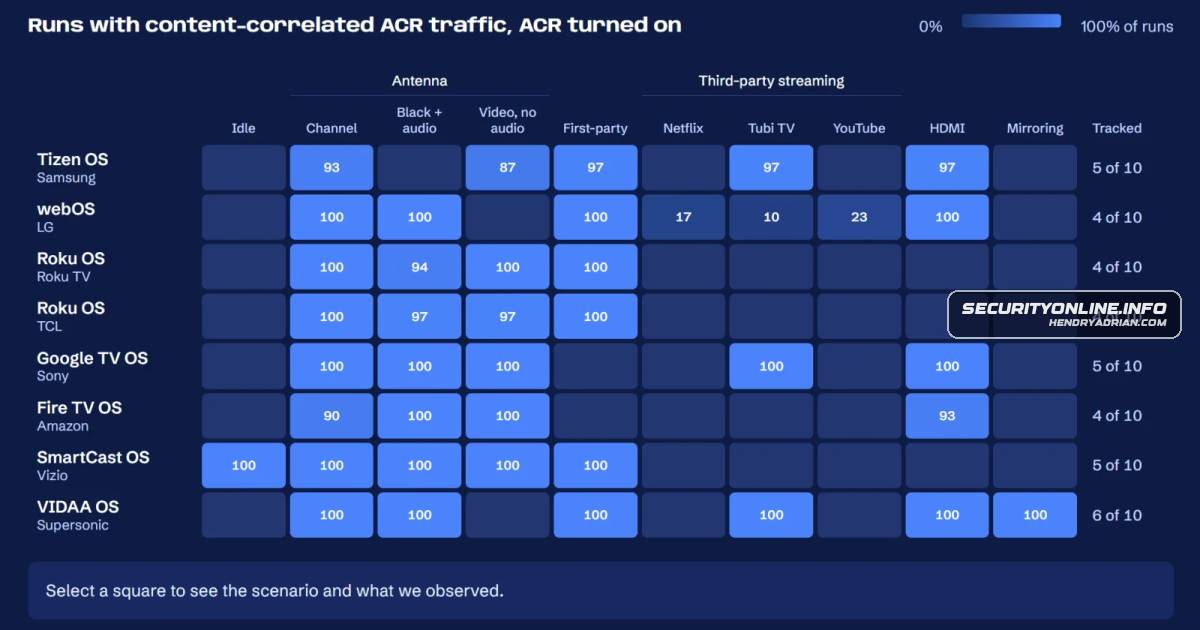
A study of 12 smart TVs found ACR-like traffic continued after opt-outs on Samsung and Vizio. Researchers collected 57 million VIDAA/Unruly viewing results from an unauthenticated MQTT broker in three hours; VIDAA added authentication, but traffic remains plaintext.

Oct 26, 2026
Security Report · cert-agid.gov.it

CERT-AGID Finds 467 Potentially Vulnerable URLs in Follow-Up PHP2Shell Scan

CERT-AGID’s Oct. 26 passive scan found 467 potentially vulnerable URLs among 20,117 reachable IPA-listed URLs, down from 650. It cautions that version disclosures do not confirm patch status and urges administrations to verify systems.

Oct 26, 2026
Security Report · cyfirma.com

CYFIRMA Report Tracks India Healthcare Threat Activity, With Pharma Claims Unconfirmed

CYFIRMA’s 2026 report logs 20 India healthcare ransomware entries for Jan–Aug, including three pharma/biotech entries, and frequent data-exposure observations. Claims remain unverified; the report finds no evidence of a coordinated campaign targeting Indian pharma.

Oct 26, 2026
Security Report · hornetsecurity.com

CISOs Identify AI Security Risks and Adoption Challenges

Hornetsecurity’s interviews with three CISOs and a broader poll describe cautious AI adoption, uneven governance and awareness, and concerns including synthetic identity fraud, data poisoning, and sensitive-data exposure.

Oct 23, 2026
Security Report · cert-agid.gov.it

CERT-AGID Reports 202 Malicious Campaigns Affecting Italy in Weekly Review

CERT-AGID analyzed 202 malicious campaigns affecting Italy, including 162 targeting Italian entities, and shared 1,460 IoCs. Phishing centered on fines, renewals, banking and refunds; 14 malware families were observed.

Oct 23, 2026
Security Report · github.com/jacobdjwilson

New Zealand’s 2026–2027 Cyber Security Action Plan Sets Out 15 Government Initiatives

New Zealand’s two-year cyber security action plan outlines 15 government initiatives, including centralized incident reporting, critical infrastructure resilience, stronger government security standards, quantum-resistant cryptography, and international partnerships.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

2026 Guide Breaks Down the Costs of a Ransomware Attack

A 2026 guide combines industry benchmarks to estimate ransomware costs, citing a $5.08 million average for mid-to-large organizations. It details ransom, response, legal, downtime, fines and insurance costs, and recommends tested backups and incident-response readiness.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

FinCEN Details How Digital Asset Investment Scam Centers Launder Proceeds

FinCEN’s September 2026 alert details how digital asset investment scam centers use guarantee marketplaces, professional money launderers, and DeFi to move proceeds, and provides detection red flags for financial institutions.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

NACD and ISA’s 2026 Handbook Guides Boards on Cyber-Risk Oversight

NACD and ISA’s 2026 cyber-risk oversight handbook outlines six governance principles, urging boards to quantify financial exposure, standardize reporting, test incident readiness, and oversee AI, quantum and third-party risks.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

Paper Proposes Time-Decay Model for Insider Risk Indicators

The paper reviews research on how insider-risk indicators lose relevance over time and proposes exponential decay levels for risk models, while calling for further validation.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

HardenStance Says Deutsche Telekom Led Telco Peers on AI Security at MWC 2026

HardenStance’s MWC 2026 briefing praises Deutsche Telekom’s AI security vision, finds Telefónica’s efforts less prominent, and says Orange showed little evidence of AI risk mitigation at its booth.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

Australia Issues Cybersecurity Guidance for LEO Satellite Communications

An Australian-led 2026 guide details cybersecurity risks and mitigations for low Earth orbit satellite communications, covering space, ground, user, link and supply-chain security, data management, sovereignty and provider assessments.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

Astra’s 2026 Cybersecurity Statistics Report Highlights Ransomware, Phishing and Sector Risks

Astra’s compilation of 160 cybersecurity statistics covers ransomware, phishing, DDoS, IoT, API and cloud security, and industry risks, with basic mitigation advice.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

Enterprise Agent Security Guide Emphasizes Task-Scoped Access and Independent Controls

An August 2026 enterprise agent security guide recommends task-scoped authority, independent action controls, runtime containment and auditable telemetry to limit prompt injection, data disclosure and unauthorized effects.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

Zscaler’s 2026 Report Outlines Zero Trust Defenses for India’s AI and Cyber Risks

Zscaler’s February 2026 report examines AI, ransomware, and IoT/OT risks to India’s digital infrastructure, recommending least-privilege access, continuous verification, data protection, and tighter third-party controls.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

Cerbos 2026 Benchmark Sets Agent Authorization and Auditability Standards

Cerbos’s 2026 guide outlines an authorization maturity model, arguing that agent access should preserve human-user permissions and delegation records. It recommends a 90-day program to assess authorization, pilot a central policy layer, and measure progress.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

Searchlight Cyber Report Estimates Ransomware Attacks Cost $5.08 Million on Average

Searchlight Cyber’s 2026 article cites estimates of $74 billion in global ransomware losses and $5.08 million per affected organization, highlighting downtime, recovery, and other costs while recommending preemptive defenses.

Oct 22, 2026
Security Report · github.com/jacobdjwilson

GSMA Outlines Post-Quantum Cryptography Migration for Satellite Networks

GSMA's PQ.07 report outlines post-quantum migration for non-terrestrial networks, recommending cryptographic inventories, phased hybrid deployments and coordinated upgrades to address satellite hardware, latency and interoperability constraints.

Oct 22, 2026
PreviousPage 3 of 31 Next
© 2026 cyber.hendryadrian.com