
ReliaQuest: New Ransomware Leak-Site Names Drove 93% of Q3 2026 Growth
Summary
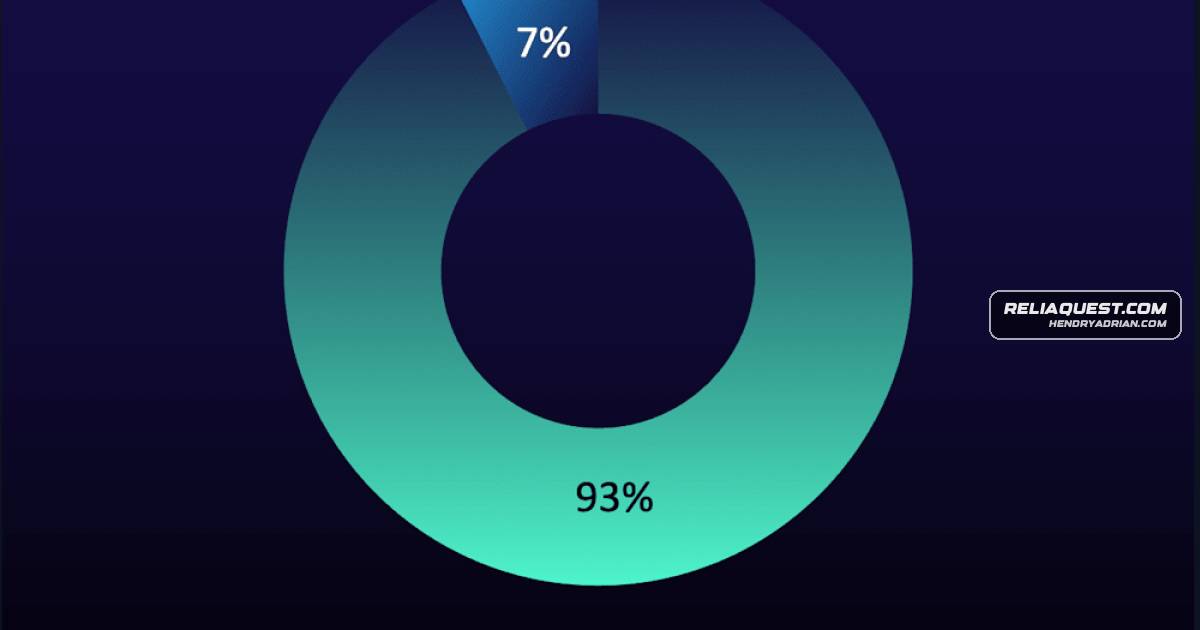
ReliaQuest found ransomware leak-site listings rose 30% in Q3 2026, with 43 newly observed groups driving 93% of growth. Listings may include rebrands, recycled data, or unsupported claims; defenders should verify claims using internal evidence.
Key points
- Organizations named on ransomware leak sites rose 30% in Q3; 43 groups appearing for the first time drove 93% of the increase, while listings by groups active in both Q2 and Q3 rose 1%.
- ReliaQuest says ExfilSquad’s released data did not substantiate a broader network breach; the report assesses the actor likely obtained limited data through exposed credentials.
- Manufacturing listings increased 70%, with Qilin and The Gentlemen accounting for much of the change; professional, scientific, and technical services remained the most-listed sector overall.
- About 85% of the increase in Q3 listings occurred outside the US; the US share of listed victims fell from 49% in Q2 to 41% in Q3.
- The report recommends verifying leak-site claims against internal telemetry, access logs, and data samples before responding, and auditing code repositories for exposed credentials and secrets.
- Recommended defenses include monitoring internet-facing systems, detecting identity compromise and lateral movement, blocking vulnerable drivers, and alerting on unexpected Group Policy changes.
Article Details
- Publisher
- ReliaQuest
- Report Period
- Q3 2026
- Scope
- Ransomware and cyber-extortion data-leak-site activity, including reported group, sector, and geographic trends.
- Sample Size
- Not disclosed
- Key Statistics
- Organizations named on data-leak sites rose 30% in Q3; the report cautions that listings do not reliably measure confirmed attacks.
- 43 groups that had not posted before Q3 accounted for 93% of the increase in named organizations.
- Organizations named by groups active in both Q2 and Q3 rose 1%.
- Manufacturing victim listings grew 70% in Q3; the report attributes much of the change to Qilin and The Gentlemen.
- Approximately 85% of Q3's increase in victim listings occurred outside the US; the US share of all listings fell to 41%. These are leak-site listing figures, not confirmed incident counts.
- Recommendations
- Build detections around shared ransomware behaviors, including abuse of remote services, identity compromise, lateral movement, defense evasion, and data exfiltration.
- Patch and monitor internet-facing edge devices, enforce Microsoft's vulnerable driver block list, and alert on unexpected Group Policy changes.
- Verify leak-site claims against internal telemetry, access logs, and posted samples before responding; keep unsupported claims unverified while investigating.
- Audit code repositories for exposed credentials, API keys, and secrets; revoke and rotate exposed credentials, and review CRM and portal logs for unusual bulk access or exports.
- Apply consistent security standards across US and non-US environments and assess regional threats against actual presence and exposure.
MITRE ATT&CK
T1078 · Valid AccountsThe report describes identity compromise and compromised accounts as ransomware footholds.T1133 · External Remote ServicesThe report recommends detecting abuse of external remote services as a shared ransomware behavior.T1484.001 · Group Policy ModificationOperators for Qilin and The Gentlemen reportedly changed Group Policy settings to push ransomware across a network.T1562.001 · Disable or Modify ToolsOperators for Qilin and The Gentlemen reportedly used vulnerable drivers to disable EDR tools.
Threat Actors
ExfilSquadReliaQuest assesses that ExfilSquad is likely an opportunistic credential-scraping actor that uses exposed credentials to access limited data and presents the access as a major breach; the available data did not substantiate the implied broader breach.QilinThe report identifies Qilin as a ransomware-as-a-service operation and says its operators exploited internet-facing systems, used vulnerable drivers to disable EDR tools, and changed Group Policy settings to deploy ransomware.The GentlemenThe report describes The Gentlemen as an affiliate-driven operation and says its operators exploited internet-facing systems, used vulnerable drivers to disable EDR tools, and changed Group Policy settings to deploy ransomware.
Countries
Industries
Manufacturinga few groups narrowed the professional, scientific, and technical services (PSTS) sector’s lead over manufacturing, why most growth occurred outside the US, and why organizations in other sectors and countriesProfessional, scientific, and technical servicesHow a few groups narrowed the professional, scientific, and technical services (PSTS) sector’s lead over manufacturing, why most growth occurred outside the US, and why organizations in other sectors and countries