
CERT-AGID Warns of SEND-Themed Phishing Targeting PagoPA Users
Summary
CERT-AGID reports email and SMS phishing impersonating SEND and PagoPA, directing users to fake traffic-fine payment pages to steal credit card details. It is coordinating takedowns and sharing related indicators.
Key points
- CERT-AGID identified multiple campaigns fraudulently using the SEND – Servizio Notifiche Digitali name and impersonating PagoPA notifications.
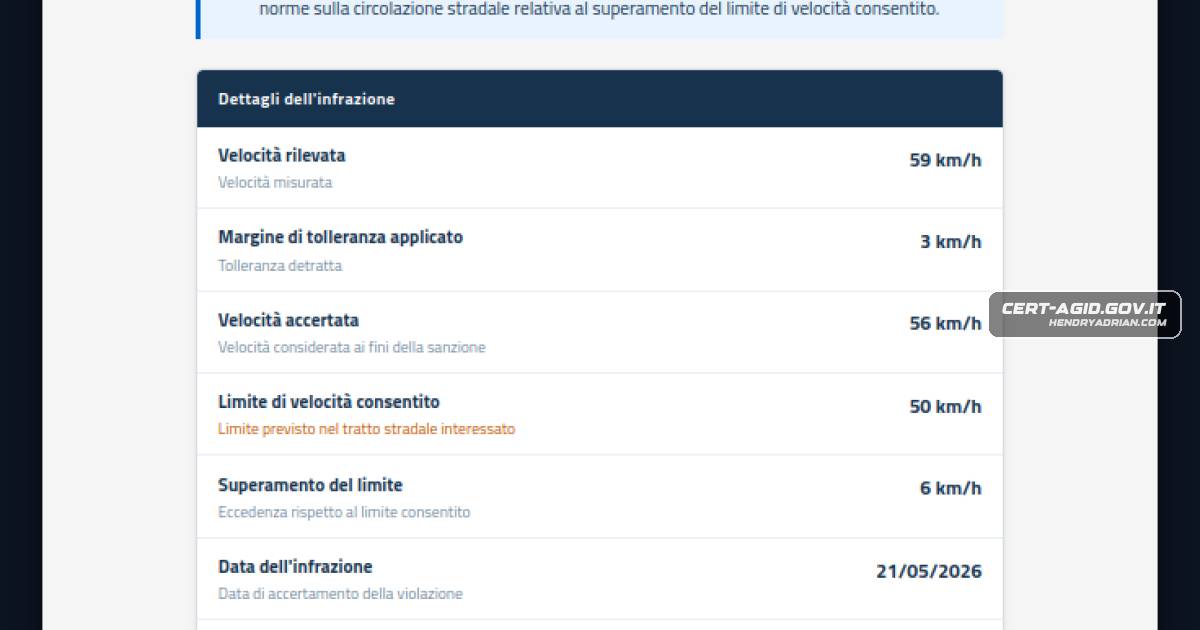
- Emails and SMS messages claim users have unpaid traffic fines and use formal language, case numbers, amounts, and urgent deadlines to appear credible.
- The fraudulent payment pages are designed to collect victims’ credit card details.
- CERT-AGID is working with PagoPA’s security team to disable malicious domains and catalog associated indicators of compromise.
- Indicators for domains identified in April have been shared with organizations accredited to CERT-AGID’s IoC feed.
- Users are advised to check destination URLs, avoid sharing banking details in messages, and report suspicious messages to the addresses provided in the article.
Article Details
- Event Type
- Phishing campaigns impersonating SEND and PagoPA through email and SMS, directing users to fraudulent payment pages.
- Impact
- The campaigns seek to trick victims into paying bogus traffic fines and entering credit card details on malicious websites. CERT-AGID and PagoPA are working to disable the malicious domains and catalog related indicators.
MITRE ATT&CK
T1204.001 · Malicious LinkThe phishing flow relies on users following message links or redirects to fraudulent sites.T1566.003 · Spearphishing via ServiceThe article identifies fake SEND/PagoPA alerts delivered through email and SMS as spearphishing via service.T1583.001 · DomainsThe article describes attackers using malicious domains to host fake payment pages.T1598 · Phishing for InformationThe fake payment pages are intended to obtain sensitive financial information, especially credit card details.