
Grandoreiro and BTMOB Campaigns Target Windows and Android Users
Summary
WatchGuard and ESET report active Grandoreiro and BTMOB campaigns targeting organizations and users in Europe and Latin America, using phishing, DLL side-loading, WebRTC-related communications and Android accessibility services to steal financial data and enable remote.
Key points
- WatchGuard reports Grandoreiro campaigns using DLL side-loading to target banks and financial institutions in Portugal.
- Grandoreiro’s reported techniques include WebRTC-related components using STUN or ICE for peer-to-peer communications, plus anti-analysis checks.
- A separate Grandoreiro phishing campaign delivers a ZIP archive containing a script that prompts users to install a fake Adobe Reader update.
- ESET reports that BTMOB, an Android RAT, spreads through fake app sites and uses accessibility services to gain additional system access.
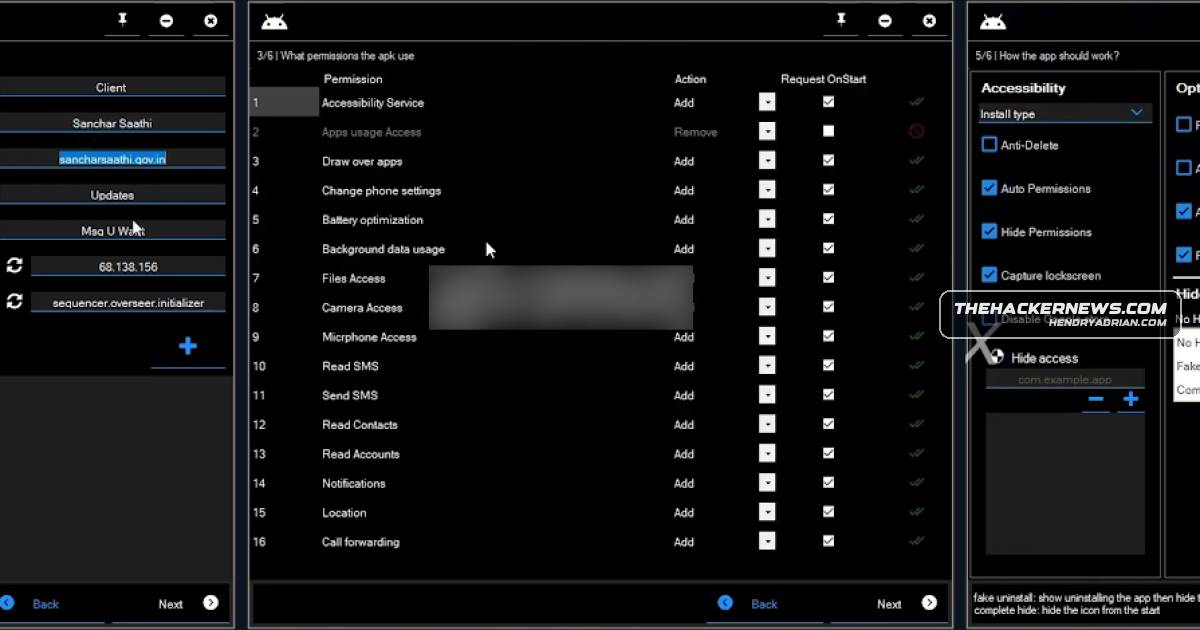
- BTMOB capabilities include remote control, screenshots, keylogging and credential theft; a builder interface lets customers generate customized payloads.
- BTMOB is sold as malware-as-a-service by an actor identified as EVLF; ESET warns that leaked versions and resale could broaden access to the tool.
Article Details
- Event Type
- Active banking-trojan campaigns targeting Windows and Android users in Latin America and Europe, reported by WatchGuard and ESET.
- Impact
- Grandoreiro campaigns target financial institutions in Portugal and can steal banking credentials and sensitive data. BTMOB can enable remote control of Android devices, capture screenshots and keystrokes, and automate credential theft. The article reports targeting of companies in Spain, Portugal, and Mexico, and mobile users in Brazil.
MITRE ATT&CK
People
Threat Actors
Malware
BTMOBusers across Latin America and Europe, including Grandoreiro attacks against banks in Portugal and BTMOB infections spread through fake app sites.CraxsRAT#GrandoreiroCypherRATBTMOB is believed to be the successor to CraxsRAT, CypherRAT, and SpySolr families.Grandoreirotrojan campaigns targeting Windows and Android users across Latin America and Europe, including Grandoreiro attacks against banks in Portugal and BTMOB infections spread through fake app sites.SpySolrBTMOB is believed to be the successor to CraxsRAT, CypherRAT, and SpySolr families.
Vendors
D3LabItalian cybersecurity company D3Lab, in an analysis of the leaked BTMOB RAT development toolkit published in December 2025, said it included the Android payload source code, its dropper, a builder environment, theESETWatchGuard and ESET found two active banking trojan campaigns targeting Windows and Android users across Latin America and Europe, including Grandoreiro attacks against banks in Portugal and BTMOB infections spreadWatchGuardWatchGuard and ESET found two active banking trojan campaigns targeting Windows and Android users across Latin America and Europe, including Grandoreiro attacks against banks in Portugal and BTMOB infections spread
Products
Adobe Acrobat ReaderPhishing emails deliver Grandoreiro via ZIP files and fake Adobe Reader updates.AndroidWatchGuard and ESET found two active banking trojan campaigns targeting Windows and Android users across Latin America and Europe, including Grandoreiro attacks against banks in Portugal and BTMOB infections spreadGoogle Play StoreFrom those sites, victims are directed to fake Google Play Store app listings that trick them into installing an Android package (APK) file containing the malware.
Countries
BrazilThat’s according to new findings from WatchGuard and ESET, which have observed the two malware families being used to single out companies in Spain, Portugal, and Mexico, as well as mobile users in Brazil.MexicoThat’s according to new findings from WatchGuard and ESET, which have observed the two malware families being used to single out companies in Spain, Portugal, and Mexico, as well as mobile users in Brazil.Portugaland Android users across Latin America and Europe, including Grandoreiro attacks against banks in Portugal and BTMOB infections spread through fake app sites.SpainThat’s according to new findings from WatchGuard and ESET, which have observed the two malware families being used to single out companies in Spain, Portugal, and Mexico, as well as mobile users in Brazil.