
CrowdStrike, Google and Shadowserver Disrupt Glassworm Botnet
Summary
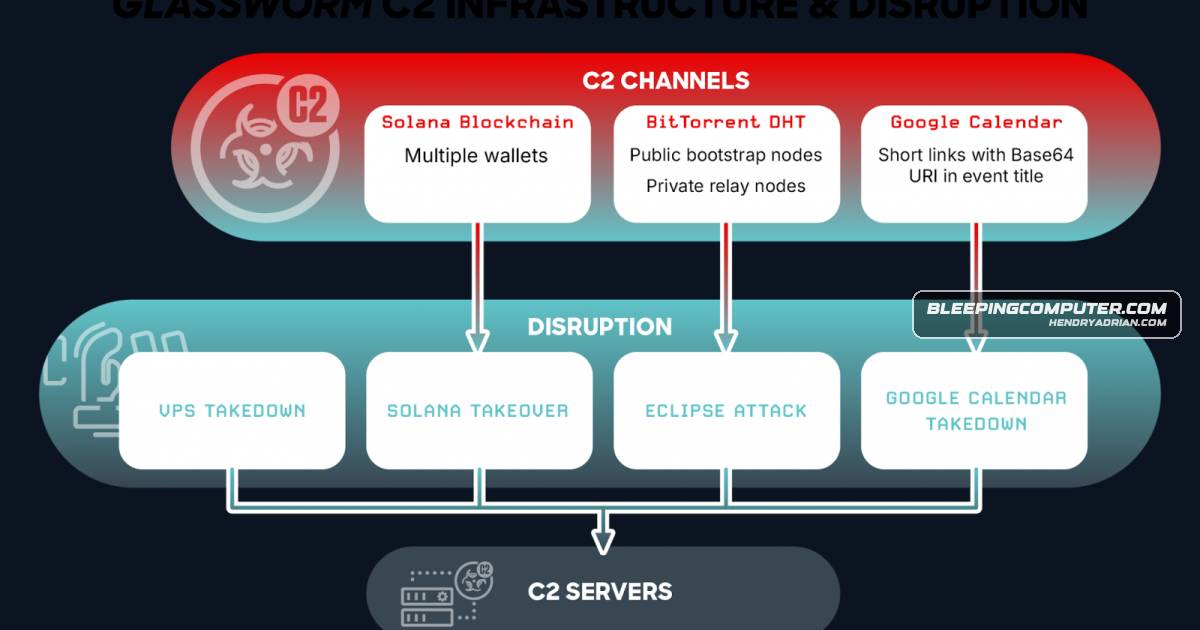
CrowdStrike, Google and The Shadowserver Foundation disrupted Glassworm by cutting off four C2 channels. The botnet targeted developers through malicious extensions and packages; infected hosts now beacon to 164.92.88[.]210.
Key points
- CrowdStrike, Google, and The Shadowserver Foundation coordinated to disrupt four Glassworm command-and-control channels.
- The channels used Solana blockchain transactions, BitTorrent DHT, Google Calendar, and direct VPS connections.
- Since October 2025, Glassworm campaigns have targeted developers with malicious OpenVSX and VS Code extensions, GitHub repositories, and npm packages.
- The campaigns stole cryptocurrency wallets and developer credentials; one March campaign affected more than 400 software artifacts.
- CrowdStrike says infected machines can no longer receive new instructions or payloads after the disruption.
- Compromised hosts are now beaconing to 164.92.88[.]210, and researchers published YARA rules to help detect infections.
Article Details
- Event Type
- Coordinated disruption of the Glassworm botnet’s command-and-control infrastructure.
- Impact
- CrowdStrike, Google, and The Shadowserver Foundation disrupted four C2 channels. According to CrowdStrike, infected machines can no longer receive new instructions or payloads. The campaigns stole cryptocurrency wallets and developer credentials; one March campaign affected more than 400 software artifacts.
MITRE ATT&CK
Malware
GlassWormCrowdStrike, Google, and The Shadowserver Foundation disrupted the Glassworm botnet by cutting off four coordinated command-and-control channels tied to Solana blockchain transactions, BitTorrent DHT, Google Calendar,GlasswormRATBitTorrent Distributed Hash Table (DHT): The GlasswormRAT queries the BitTorrent peer-to-peer network for configuration data stored against hardcoded public keys, leveraging a global decentralized network with no single
Vendors
CrowdStrikeCrowdStrike, Google, and The Shadowserver Foundation disrupted the Glassworm botnet by cutting off four coordinated command-and-control channels tied to Solana blockchain transactions, BitTorrent DHT, Google Calendar,GoogleCrowdStrike, Google, and The Shadowserver Foundation disrupted the Glassworm botnet by cutting off four coordinated command-and-control channels tied to Solana blockchain transactions, BitTorrent DHT, Google Calendar,
Products
GitHubThe botnet had been used since October 2025 in supply-chain attacks against developers through malicious OpenVSX, VS Code, GitHub, and npm artifacts that stole wallets and credentials.Google Calendarcoordinated command-and-control channels tied to Solana blockchain transactions, BitTorrent DHT, Google Calendar, and direct VPS connections.Microsoft VS CodeGlassworm campaigns have been ongoing since October 2025 and initially targeted developers with malicious OpenVSX and Microsoft VS Code extensions that stole cryptocurrency wallets and developer credentials.npmThe botnet had been used since October 2025 in supply-chain attacks against developers through malicious OpenVSX, VS Code, GitHub, and npm artifacts that stole wallets and credentials.OpenVSXThe botnet had been used since October 2025 in supply-chain attacks against developers through malicious OpenVSX, VS Code, GitHub, and npm artifacts that stole wallets and credentials.Solanadisrupted the Glassworm botnet by cutting off four coordinated command-and-control channels tied to Solana blockchain transactions, BitTorrent DHT, Google Calendar, and direct VPS connections.