
Google Attributes Axios npm Supply-Chain Attack to UNC1069
Summary
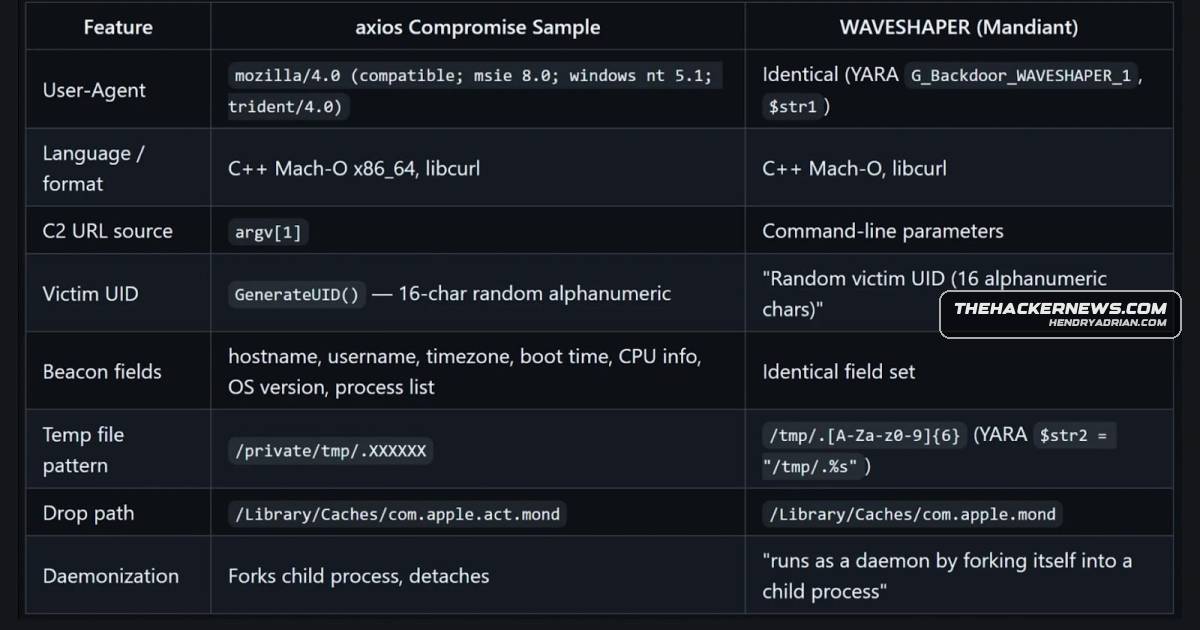
Google GTIG attributes the Axios npm supply-chain compromise to suspected North Korean cluster UNC1069. Trojanized releases added plain-crypto-js, which ran SILKBELL and delivered the WAVESHAPER.V2 backdoor to Windows, macOS, and Linux; Google says the impact remains [1
Key points
- Google's Threat Intelligence Group attributes the Axios npm supply-chain compromise to suspected North Korean cluster UNC1069; the full impact remains unclear.
- Attackers reportedly took over a maintainer's npm account and published trojanized Axios versions 1.14.1 and 0.30.4, adding the plain-crypto-js dependency.
- A package postinstall hook launched the SILKBELL dropper, which fetched operating-system-specific payloads for Windows, macOS, and Linux.
- The WAVESHAPER.V2 backdoor supports process termination, directory listing, script execution, and binary execution; it beacons to its C2 server every 60 seconds.
- Recommended actions include checking dependency trees for affected versions and plain-crypto-js, pinning Axios to a known safe version, isolating affected systems, and rotating credentials.
- The article identifies the C2 domain as sfrclak[.]com.
Article Details
- Event Type
- npm software supply-chain compromise involving trojanized Axios releases
- Impact
- Attackers reportedly seized a maintainer account and released Axios versions 1.14.1 and 0.30.4 with the malicious plain-crypto-js dependency. Its postinstall hook deployed the SILKBELL dropper, which fetched OS-specific payloads for Windows, macOS, and Linux, including the WAVESHAPER.V2 backdoor. The backdoor beacons to a C2 every 60 seconds and supports commands to terminate itself, enumerate files, run scripts, and execute binaries. Google said the full breadth of the incident was unclear and expected potentially far-reaching impacts.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | sfrclak[.]com | Domain identified in the article as a C2 domain to block. |
| IPV4 | 142[.]11[.]206[.]73 | IP address identified in the article as associated with the C2 infrastructure to block. |
MITRE ATT&CK
T1059.001 · PowerShellThe backdoor can run PowerShell commands, and the Windows execution branch delivered PowerShell malware.T1059.002 · AppleScriptThe backdoor can run AppleScript commands.T1059.004 · Unix ShellThe backdoor can run shell commands.T1105 · Ingress Tool TransferThe SILKBELL dropper fetched OS-specific next-stage payloads from a remote server.T1195.002 · Compromise Software Supply ChainAttackers compromised a package maintainer account and distributed trojanized Axios releases through the software supply chain.
People
John HultquistChief analyst at Google Threat Intelligence Group; he told The Hacker News that Google attributed the attack to a suspected North Korean threat actor tracked as UNC1069.Tomislav PeriÄinChief Software Architect at ReversingLabs; he commented on the attack's operational sophistication and advised organizations to audit package managers and treat exposed secrets as compromised.
Threat Actors
Malware
SILKBELLThe attackers pushed trojanized Axios releases that installed a malicious dependency “plain-crypto-js” which deployed the SILKBELL dropper and the cross-platform WAVESHAPER.V2 backdoor.WAVESHAPERThe attackers pushed trojanized Axios releases that installed a malicious dependency “plain-crypto-js” which deployed the SILKBELL dropper and the cross-platform WAVESHAPER.V2 backdoor.WAVESHAPER.V2The attackers pushed trojanized Axios releases that installed a malicious dependency “plain-crypto-js” which deployed the SILKBELL dropper and the cross-platform WAVESHAPER.V2 backdoor.
Vendors
GoogleGoogle has attributed the supply chain compromise of the popular Axios npm package to a financially motivated North Korean cluster tracked as UNC1069.Mandiant“WAVESHAPER.V2 is a direct evolution of WAVESHAPER, a macOS and Linux backdoor previously attributed to UNC1069,” Mandiant and GTIG said.
Products
AxiosGoogle has attributed the supply chain compromise of the popular Axios npm package to a financially motivated North Korean cluster tracked as UNC1069.npmGoogle has attributed the supply chain compromise of the popular Axios npm package to a financially motivated North Korean cluster tracked as UNC1069.